
voidsec-proxy
 voidsecsoftwares/voidsec-proxy
Multi-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
data-exfiltrationdigital-forensicsdns-subdomain-enumeration+8
4
voidsecsoftwares/voidsec-proxyMulti-module offensive security toolkit for SOCKS5 proxy chaining, port scanning, DNS enumeration, hash cracking, reverse shell generation,…
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 samybaiwir/dnslivery
Easy files and payloads delivery over DNS
 kaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…
 adityabhatt3010/cve-2026-27579-cors-misconfiguration-leading-to-authenticated-data-exposure
CVE-2026-27579 - CORS Misconfiguration – Arbitrary Origin with Credentials → Authenticated Cross-Origin Account Data Exposure
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
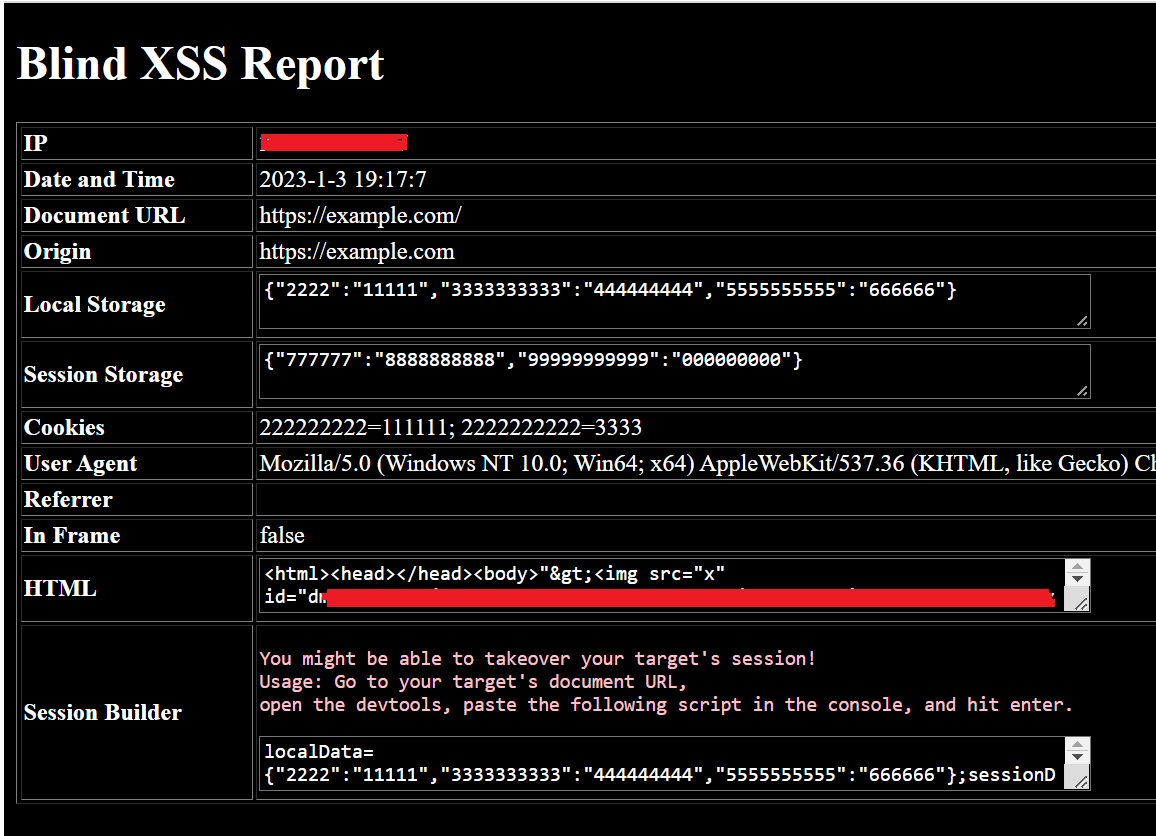 seifelsallamy/xssfire
A standalone Blind XSS Script.
 fin3ss3g0d/secretsdump.py
Enhanced version of secretsdump.py from Impacket. Adds multi-threading and accepts an input file with a list of target hosts for simultaneous secrets…
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 george0papasotiriou/cve-2026-3333-dns-rebinding-to-steal-cloud-metadata
Python exploit for CVE-2026-3333 demonstrating DNS rebinding to access cloud metadata and steal IAM credentials through an SSRF-vulnerable web app.
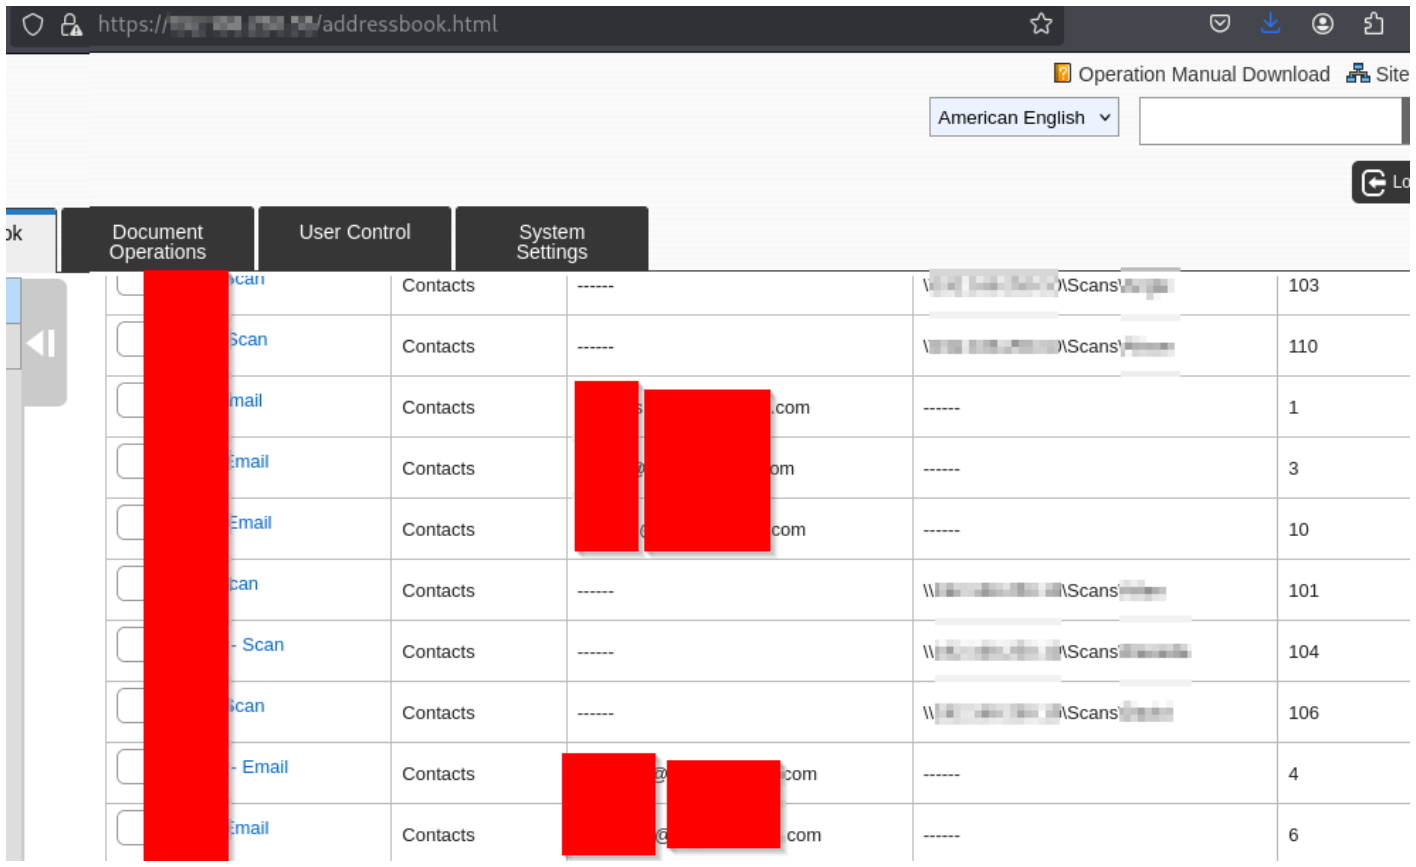 redr0nin/cve-2026-63563
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers
 gursev/flash-xdomain-xploit
ActionScript Proof of Concept to perform cross-domain reads
 nccgroup/onelogicalmyth_shell
A HTA shell to assist with breakout assessments.
 integration-it/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 nxploited/cve-2025-7401
Premium Age Verification / Restriction for WordPress <= 3.0.2 - Unauthenticated Arbitrary File Read and Write
 jgalego/hiddensteps
HiddenSteps — a local-first personal workflow intelligence platform
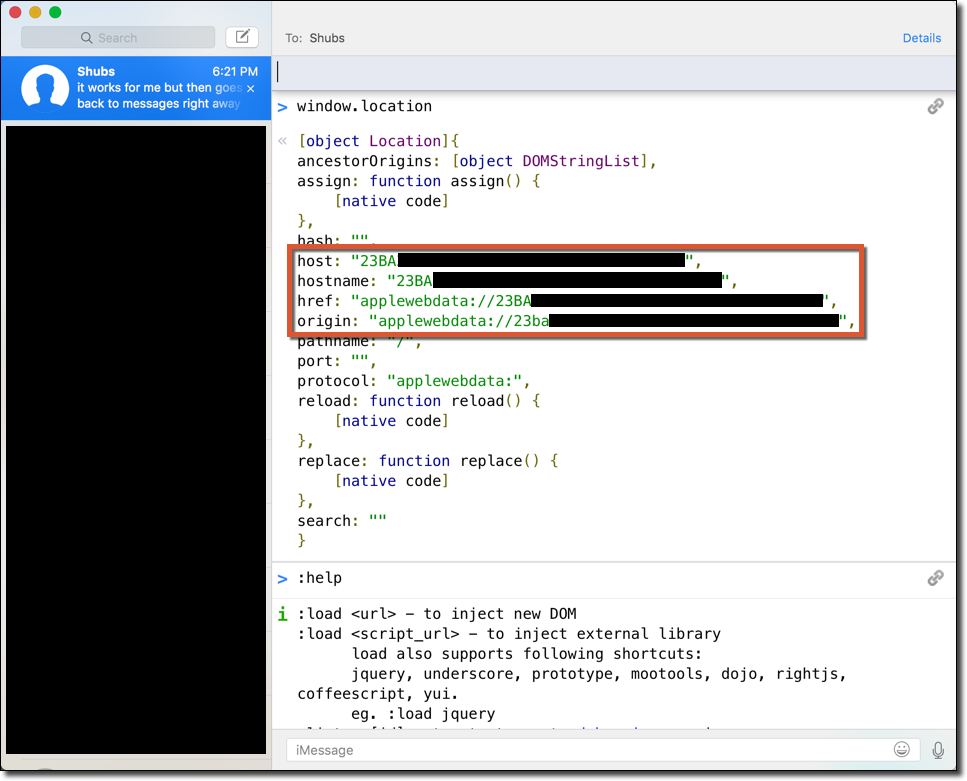 moloch--/cve-2016-1764
Extraction of iMessage Data via XSS
 inertfluid/cve-2026-54316-lab
Reproduction lab for CVE-2026-54316 (Claude Code WebFetch huggingface.co bare-hostname permission bypass / exfiltration)