

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
712
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 sensepost/det
(extensible) Data Exfiltration Toolkit (DET)
 olivsec/loboguara
Cyber threat intelligence platform for SSL certificate discovery, domain/URL scanning, data leak monitoring, tracking link generation, and threat…
 dagowda/confluencec2
This is a project aimed to make every other Saas product a C2, confluence is just the beginning.
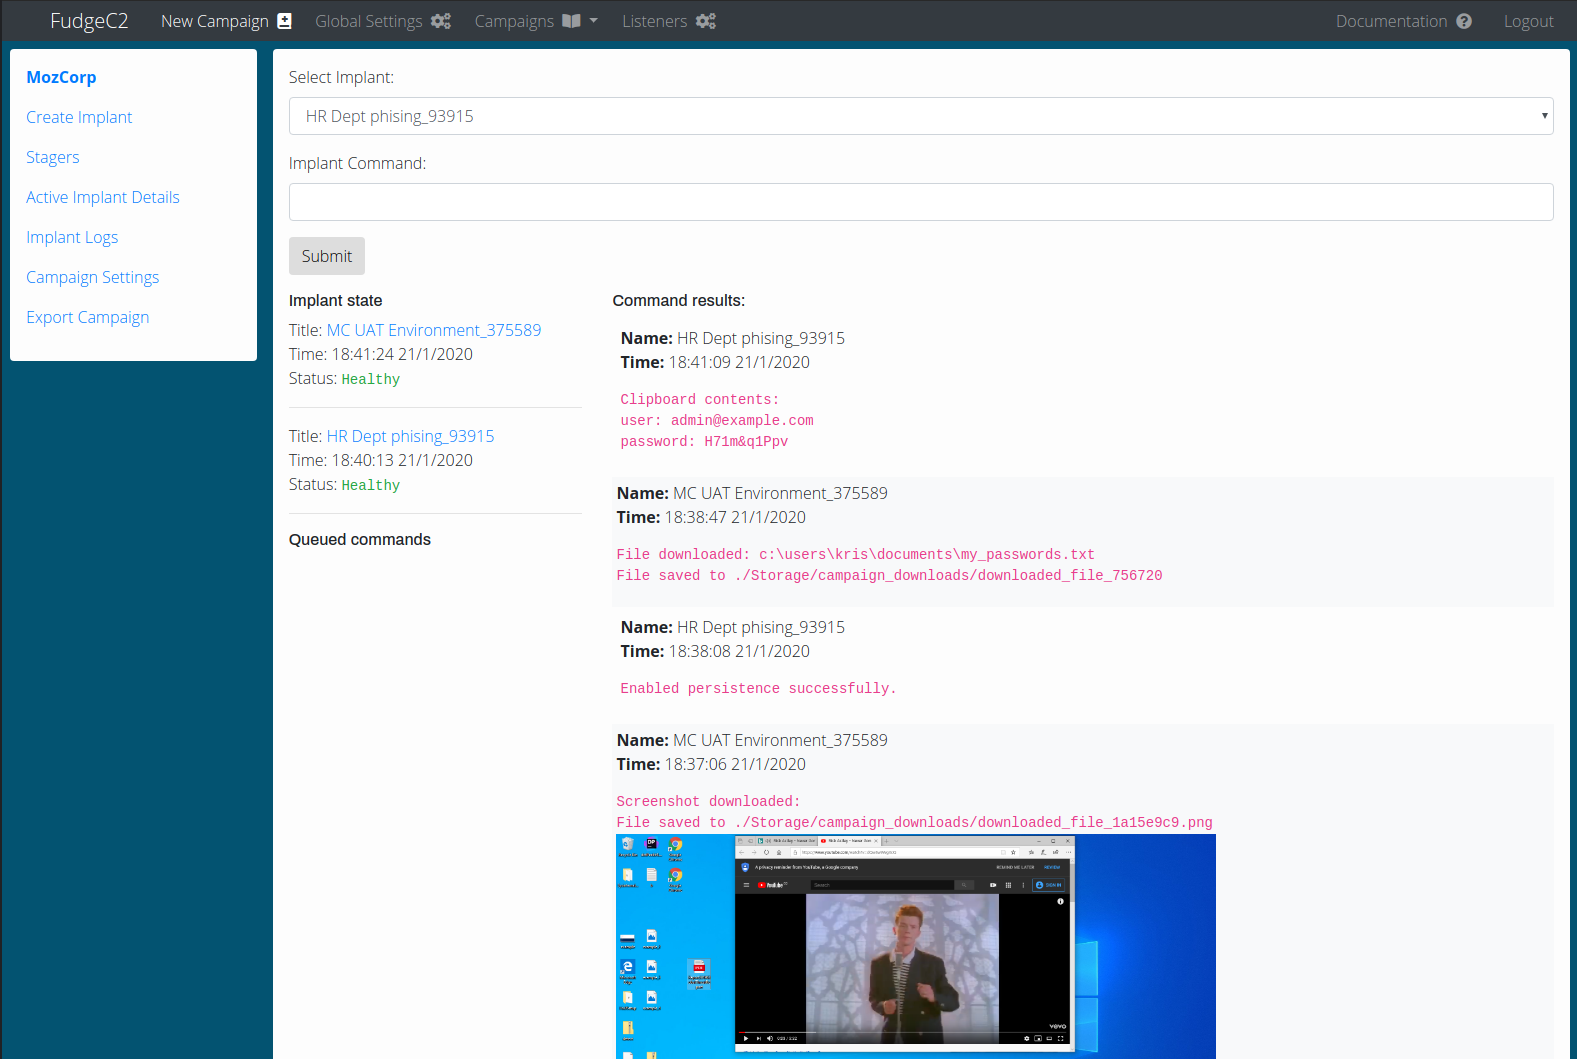 ziconius/fudgec2
FudgeC2 - a command and control framework designed for team collaboration and post-exploitation activities.
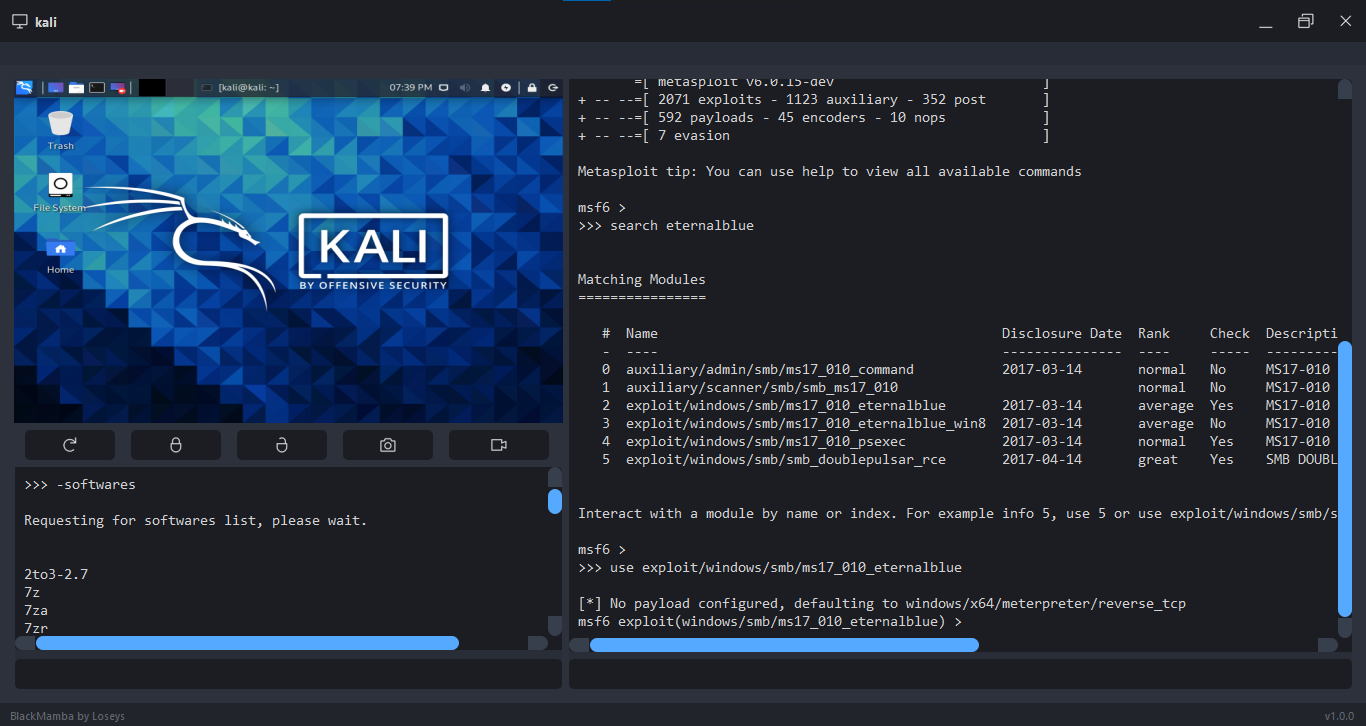 loseys/blackmamba
C2/post-exploitation framework
 pentestpartners/ptp-rat
Exfiltrate data over screen interfaces
 chasingimpact/cve-2025-66516-writeup-poc
CVE-2025-66516 working exploit, scanner, explanation.
 antisnatchor/phishlulz
Automated phishing campaign toolset that spawns dedicated AWS EC2 instances with integrated PhishingFrenzy and BeEF, plus subdomain discovery and…
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 e4zyy/project-cve-2026-45833
Exploit tool for CVE-2026-45833 in ChromaDB, enabling malicious model generation, reconnaissance, and data exfiltration from target collections via…
 nccgroup/sleipnir
Tiny payload for transfer via LOKI - Provides high speed Virtual Channel two way file transfer capabilities
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 incidedigital/mistica
An open source swiss army knife for arbitrary communication over application protocols
 offlinemark/poet
[unmaintained] Post-exploitation tool
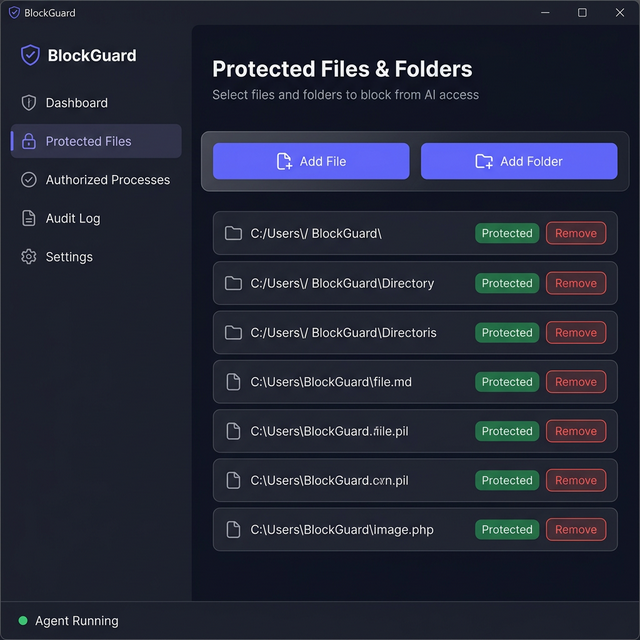 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 mbadanoiu/cve-2022-41678
CVE-2022-41678: Dangerous MBeans Accessible via Jolokia API in Apache ActiveMQ
 abraxas/cve-2026-15583
Proof-of-concept client and Docker lab reproducing CVE-2026-15583, an unauthenticated confused-deputy SSRF in Grafana MCP Server that leaks…