
Yara-detection-rules
 embee-research/yara-detection-rules
Yara Rules for Modern Malware
curated-resourcesdefensive-toolsintrusion-detection+2
embee-research/yara-detection-rulesYara Rules for Modern Malware
 luemmelsec/pentest-tools-collection
Curated collection of offensive security tools and commands for Active Directory attacks, C2, privilege escalation, obfuscation, and web pentesting.
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
 jorgeorchilles/presentations
Slides and materials for conference presentations
 s1ckb0y1337/cobalt-strike-cheatsheet
Some notes and examples for cobalt strike's functionality
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
 hackerschoice/team-teso
Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…
 threekiii/awesome-redteam
一个攻防知识库。A knowledge base for red teaming and offensive security.
 d4t4s3c/offensivereverseshellcheatsheet
Curated cheat sheet of reverse shell payloads in Bash, Netcat, PHP, PowerShell, Python, Perl, Ruby, and msfvenom, plus webshells, log poisoning, and…
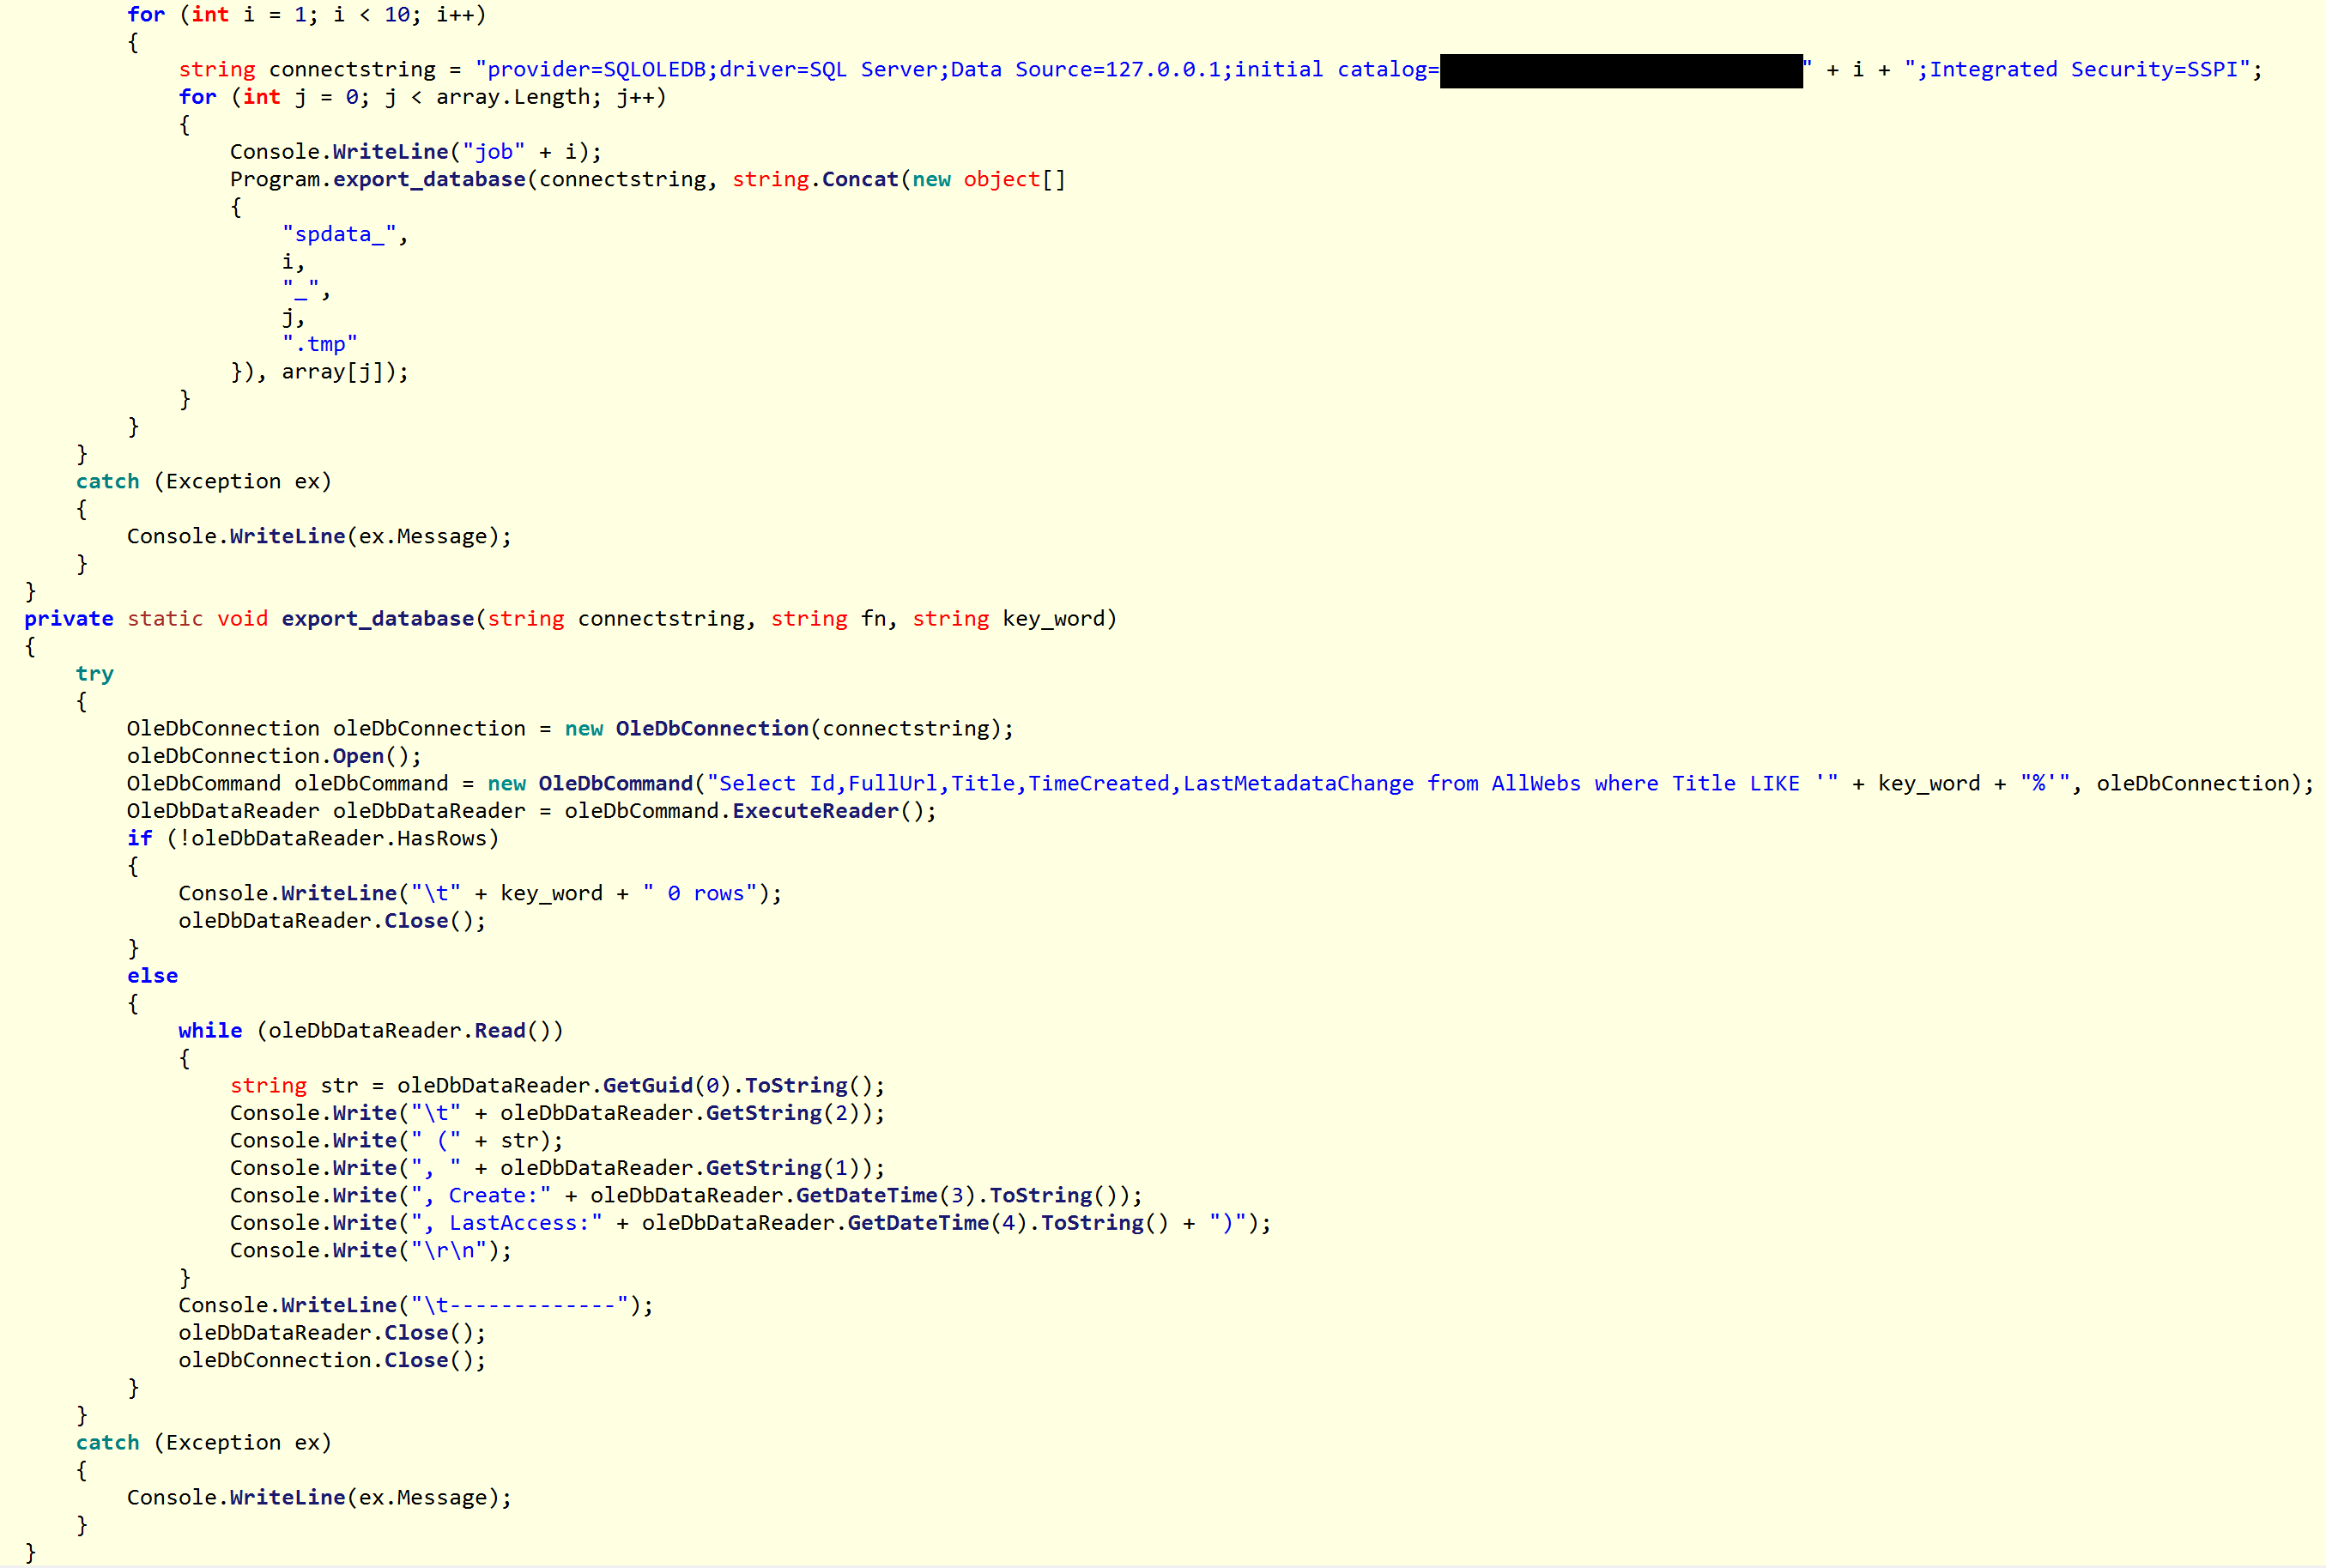 nccgroup/royal_apt
Royal APT - APT15 - Related Information from NCC Group Cyber Defense Operations Research
 edu0x01/hack-tools
Project that brings together several pentest tools
 threatexpress/malleable-c2
Cobalt Strike Malleable C2 Design and Reference Guide
 darksp33d/hyperhives-macos-infostealer-analysis
Full static analysis of HyperHives macOS Rust infostealer — 571 decrypted config values, C2 infrastructure, DPRK/Contagious Interview attribution,…
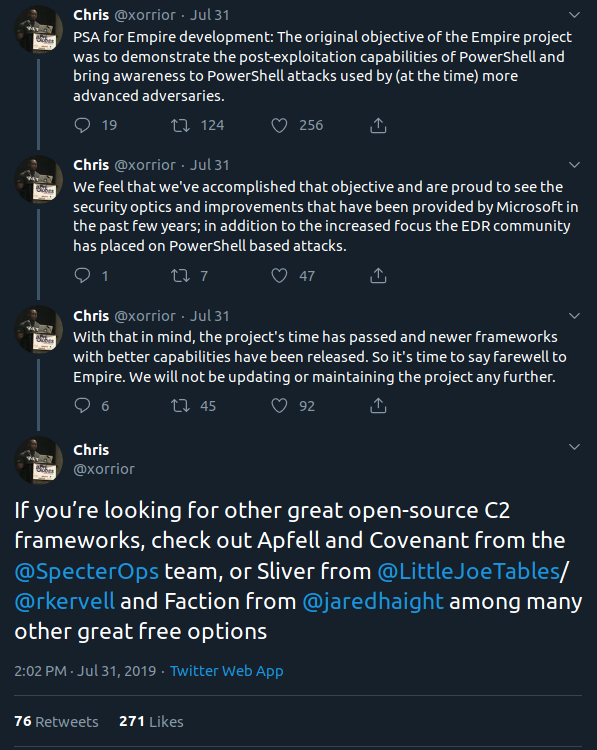 professionallyevil/c4
Cyberdelia, a Collection of Command and Control frameworks
 alphaseclab/awesome-rat
RAT And C&C Resources. 250+ Open Source Projects, 1200+ RAT/C&C blog/video.
 zer0yu/awesome-cobaltstrike
List of Awesome CobaltStrike Resources
 i-am-jakoby/powershell-for-hackers
This repository is a collection of powershell functions every hacker should know
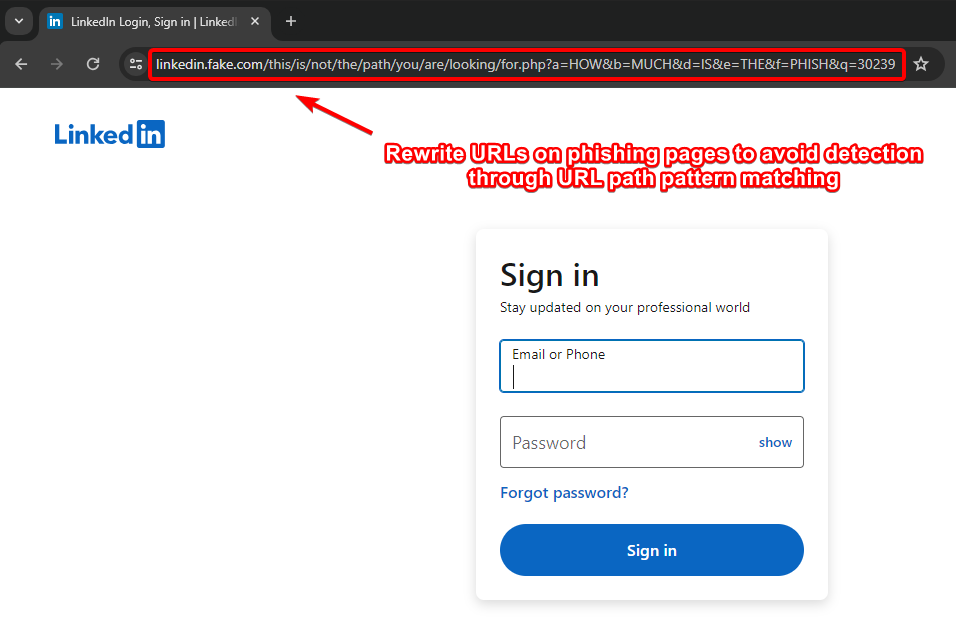 an0nud4y/evilginx-phishing-infra-setup
Evilginx Phishing Infrastructure Setup Guide - Securing Evilginx and Gophish Infrastructure, Removing IOCs, Phishing TTPs