

Red-Teaming-Toolkit
 infosecn1nja/red-teaming-toolkit
This repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
command-and-controlcurated-resourceslateral-movement+6
10.8k
infosecn1nja/red-teaming-toolkitThis repository contains cutting-edge open-source security tools (OST) for a red teamer and threat hunter.
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
 reddelexc/hackerone-reports
Curated collection of top HackerOne bug bounty reports organized by vulnerability type and program, with scripts to fetch, deduplicate, and rank…
 opencti-platform/opencti
Open Cyber Threat Intelligence Platform
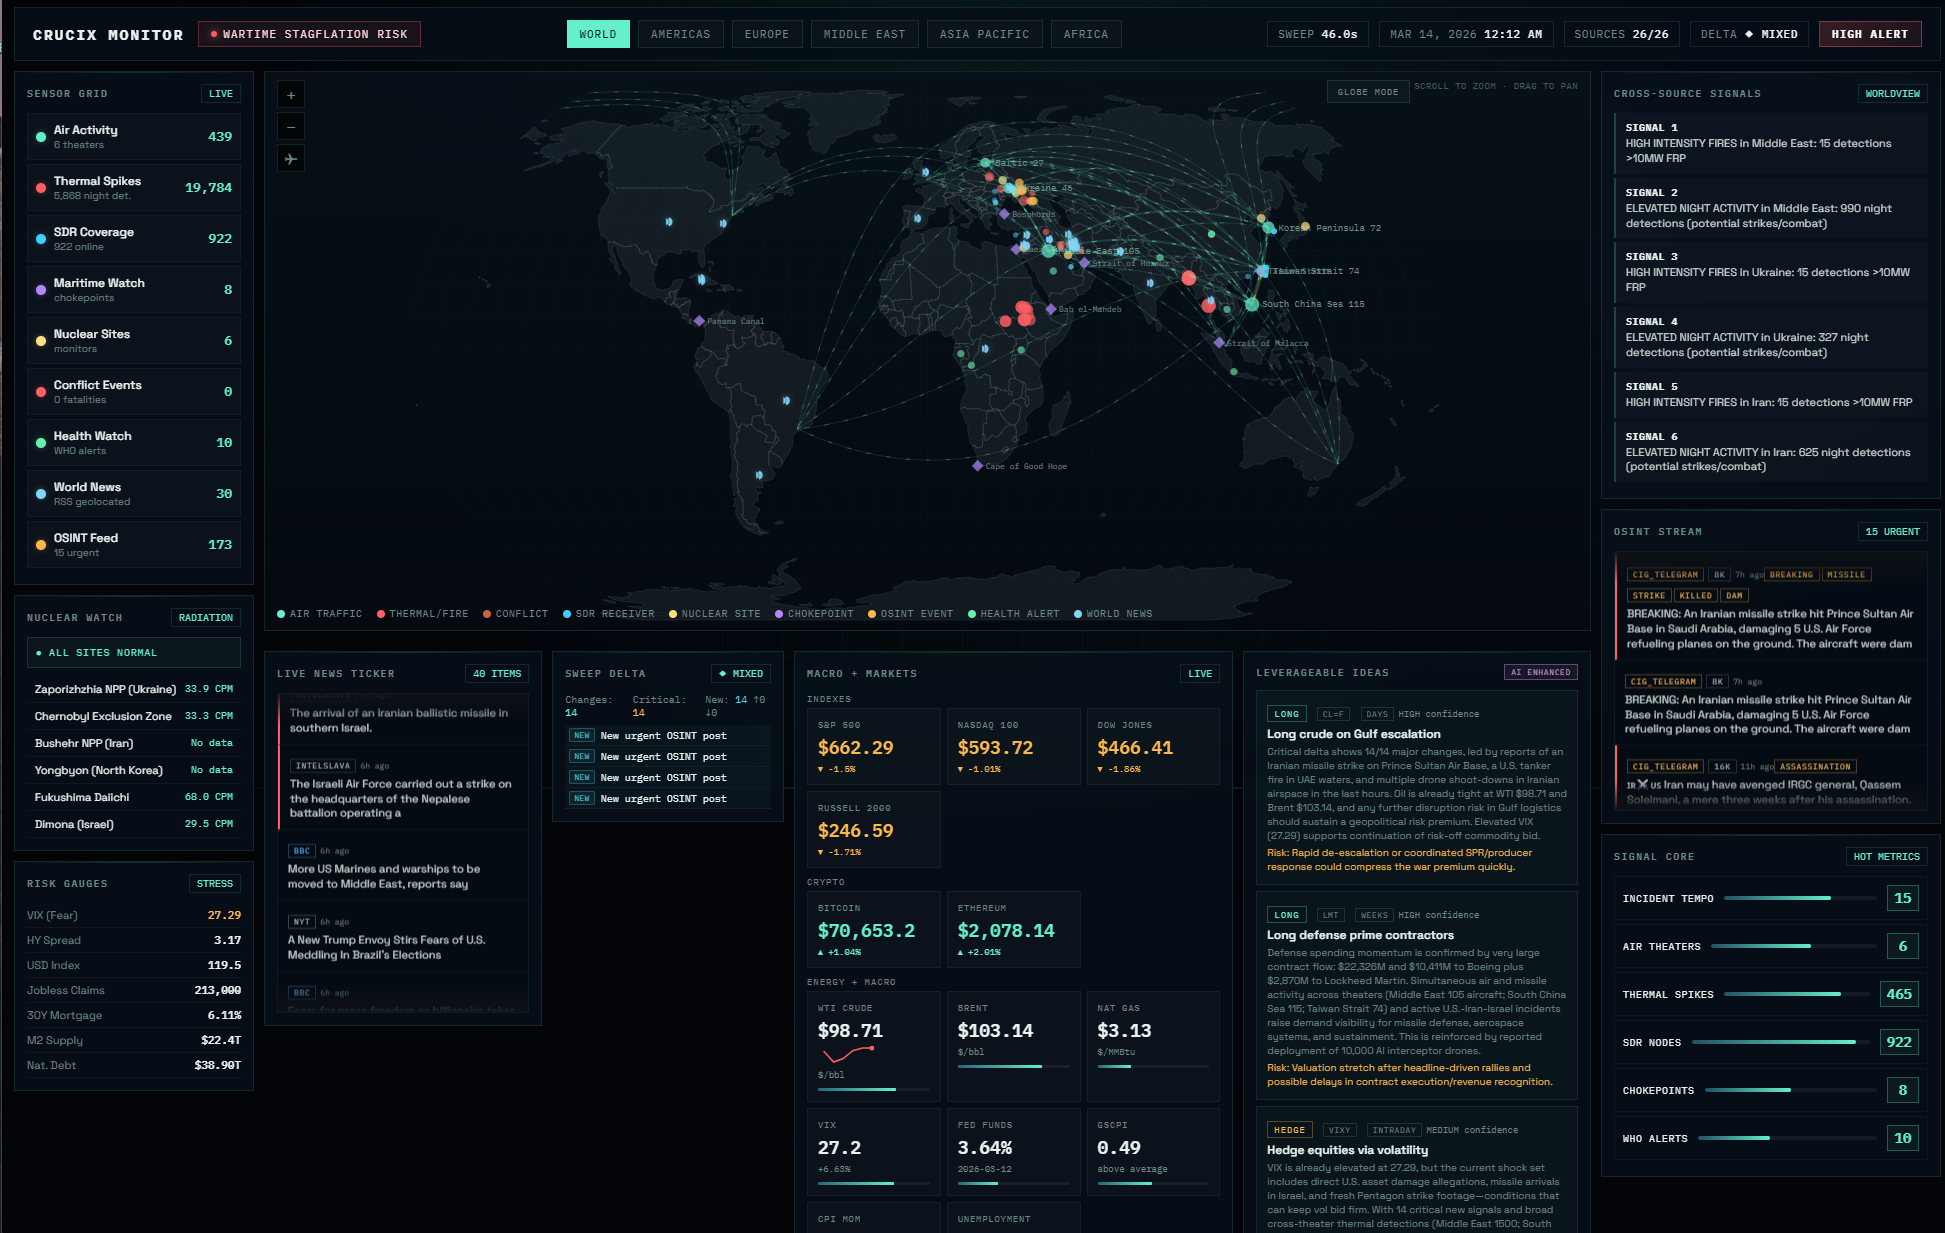 calesthio/crucix
Your personal intelligence agent. Watches the world from multiple data sources and pings you when something changes.
 juliocesarfort/public-pentesting-reports
A list of public penetration test reports published by several consulting firms and academic security groups.
 vavkamil/awesome-bugbounty-tools
Curated directory of bug bounty tools organized by category: reconnaissance, subdomain enumeration, port scanning, content discovery, exploitation,…
 hahwul/webhackersweapons
⚔️ Web Hacker's Weapons / A collection of cool tools used by Web hackers. Happy hacking , Happy bug-hunting
 fuzzdb-project/fuzzdb
Dictionary of attack patterns and primitives for black-box application fault injection and resource discovery.
 yaelwrites/big-ass-data-broker-opt-out-list
Curated, community-maintained directory of data broker opt-out instructions to help individuals remove personal information from people-search sites…
 arkadiyt/bounty-targets-data
This repo contains hourly-updated data dumps of bug bounty platform scopes (like Hackerone/Bugcrowd/Intigriti/etc) that are eligible for reports
 astrosp/awesome-osint-list
📡 Comprehensive collection of OSINT tools for cybersecurity professionals, researchers, and bug bounty hunters. Topics: information gathering,…
 s1ckb0y1337/active-directory-exploitation-cheat-sheet
A cheat sheet that contains common enumeration and attack methods for Windows Active Directory.
 edoverflow/bugbounty-cheatsheet
A list of interesting payloads, tips and tricks for bug bounty hunters.
 jakejarvis/awesome-shodan-queries
🔍 A collection of interesting, funny, and depressing search queries to plug into shodan.io 👩💻
 a-poc/blueteam-tools
Tools and Techniques for Blue Team / Incident Response
 daffainfo/allaboutbugbounty
All about bug bounty (bypasses, payloads, and etc)
 kingofbugbounty/kingofbugbountytips
Our main goal is to share tips from some well-known bughunters. Using recon methodology, we are able to find subdomains, apis, and tokens that are…