

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
43 results
atomicvulns preview

atomicvulns

GitHubdoretox/atomicvulns

Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.


ctfeducationlabs-practice+5
22
5 days ago
Juiceshopgl preview

Juiceshopgl

GitLabmbrandner-group/juiceshopgl

Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…

ctfeducationlabs-practice+5
2 years ago
awesome-web-hacking preview

awesome-web-hacking

GitHubinfoslack/awesome-web-hacking

Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…

cryptographyctfcurated-resources+6
7.3k10 days ago
WebGoat preview

WebGoat

GitHubwebgoat/webgoat

Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…

ctfeducationlabs-practice+4
9.4k4 days ago
JavaSecLab preview

JavaSecLab

GitHubwhgojp/javaseclab

Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
8813 months ago
Pegasus-Pentest-Arsenal preview

Pegasus-Pentest-Arsenal

GitHubsobri3195/pegasus-pentest-arsenal

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
575 months ago
bug-reaper preview

bug-reaper

GitHubshaniidev/bug-reaper

Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
api-security-testingctfeducation+8
727 months ago
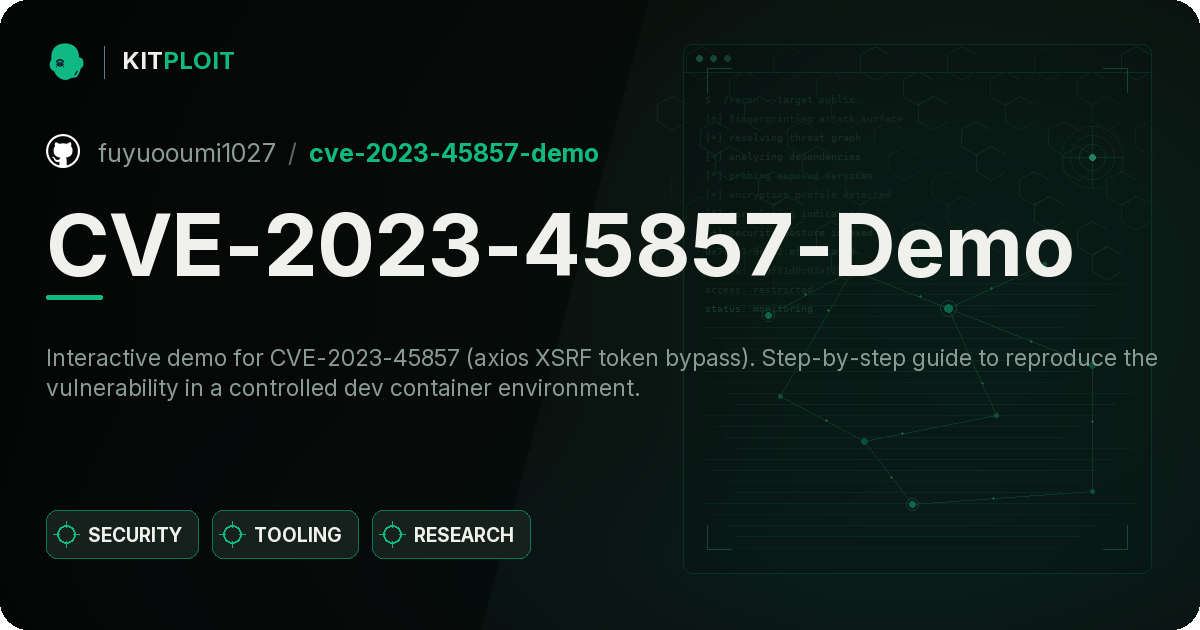
HTB-TwoMillion-machine preview

HTB-TwoMillion-machine

GitHubabedallarawashdeh/htb-twomillion-machine

Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
api-security-testingctfeducation+4
1 month ago
CVE-2023-45857-Demo preview

CVE-2023-45857-Demo

GitHubfuyuooumi1027/cve-2023-45857-demo

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
api-security-testingctfeducation+3
12 years ago
Owasp-top-10-k8s-2025 preview

Owasp-top-10-k8s-2025

GitHubhac01/owasp-top-10-k8s-2025

Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…

cloud-securitycontainer-securityctf+8
492 months ago
railsgoat preview

railsgoat

GitHubowasp/railsgoat

A vulnerable version of Rails that follows the OWASP Top 10

code-analysisctfeducation+5
92519 days ago
iGoat-Swift preview

iGoat-Swift

GitHubowasp/igoat-swift

OWASP iGoat (Swift) - A Damn Vulnerable Swift Application for iOS
ctfeducationios-security+6
4559 months ago
mas-crackmes preview

mas-crackmes

GitHubowasp/mas-crackmes

The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.

android-securitybinary-analysisctf+6
373 years ago
juice-shop preview

juice-shop

GitHubjuice-shop/juice-shop

Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…

ctfeducationlabs-practice+3
14.0k1 month ago
mutillidae preview

mutillidae

GitHubwebpwnized/mutillidae

OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…

ctfeducationlabs-practice+3
1.5k3 days ago
OWASPWebGoatPHP preview

OWASPWebGoatPHP

GitHubowasp/owaspwebgoatphp

A deliberately vulnerable web application for learning web application security.
ctfeducationlabs-practice+3
1611 year ago
CICD-Goat-Vapt-Writeup preview

CICD-Goat-Vapt-Writeup

GitHubdheeraj-jayaswal/cicd-goat-vapt-writeup

Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
ctfdevsecopseducation+5
125 days ago
AI-Vulnerabilities-Playground preview

AI-Vulnerabilities-Playground

GitHubowasp/ai-vulnerabilities-playground

Hands-on AI security lab platform with 50+ scenarios across prompt injection, agentic system exploitation, model manipulation, and MCP trust boundary…

adversarial-attackai-securityctf+4
235 months ago
Previous123Next