

DFIR-LABS
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
ctfdigital-forensicsdisk-forensics+6
660
azr43lkn1ght/dfir-labsHands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 ztrxwzy/joomla.3.7.0exploit
Proof of Concept exploit for the Joomla 3.7.0 com_fields SQL injection vulnerability (CVE-2017-8917), demonstrating detection, enumeration, and data…
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 sparshbiswas-ai/cve-2025-11844-smolagents
Educational sandbox and dynamic proof-of-concept scanner for CVE-2025-11844 XPath injection in Hugging Face smolagents library, enabling local data…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 behindsecurity/htb-wifinetictwo-exploit
A simple python script to exploit CVE-2021-31630 on HTB WifineticTwo CTF
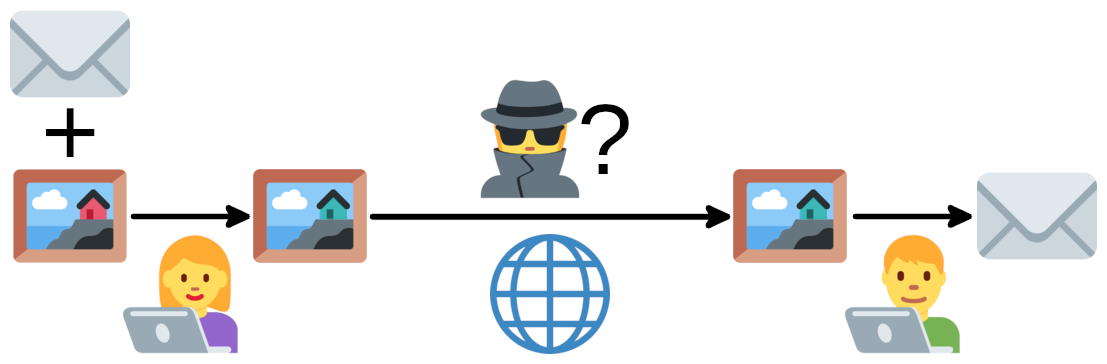 ragibson/steganography
Least Significant Bit Steganography for bitmap images (.bmp and .png), WAV sound files, and byte sequences. Simple LSB Steganalysis (LSB extraction)…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 lr-m/icseeu
This is a suite of tools/PoCs/exploits for cameras using the iCSee application. And yes - it can run NES games!
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…