

awesome-hacking
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
cryptographyctfcurated-resources+6
17.3k2 years ago
carpedm20/awesome-hackingA curated list of awesome Hacking tutorials, tools and resources
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 0xricksanchez/like-dbg
Fully dockerized Linux kernel debugging environment for Linux and MacOS
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
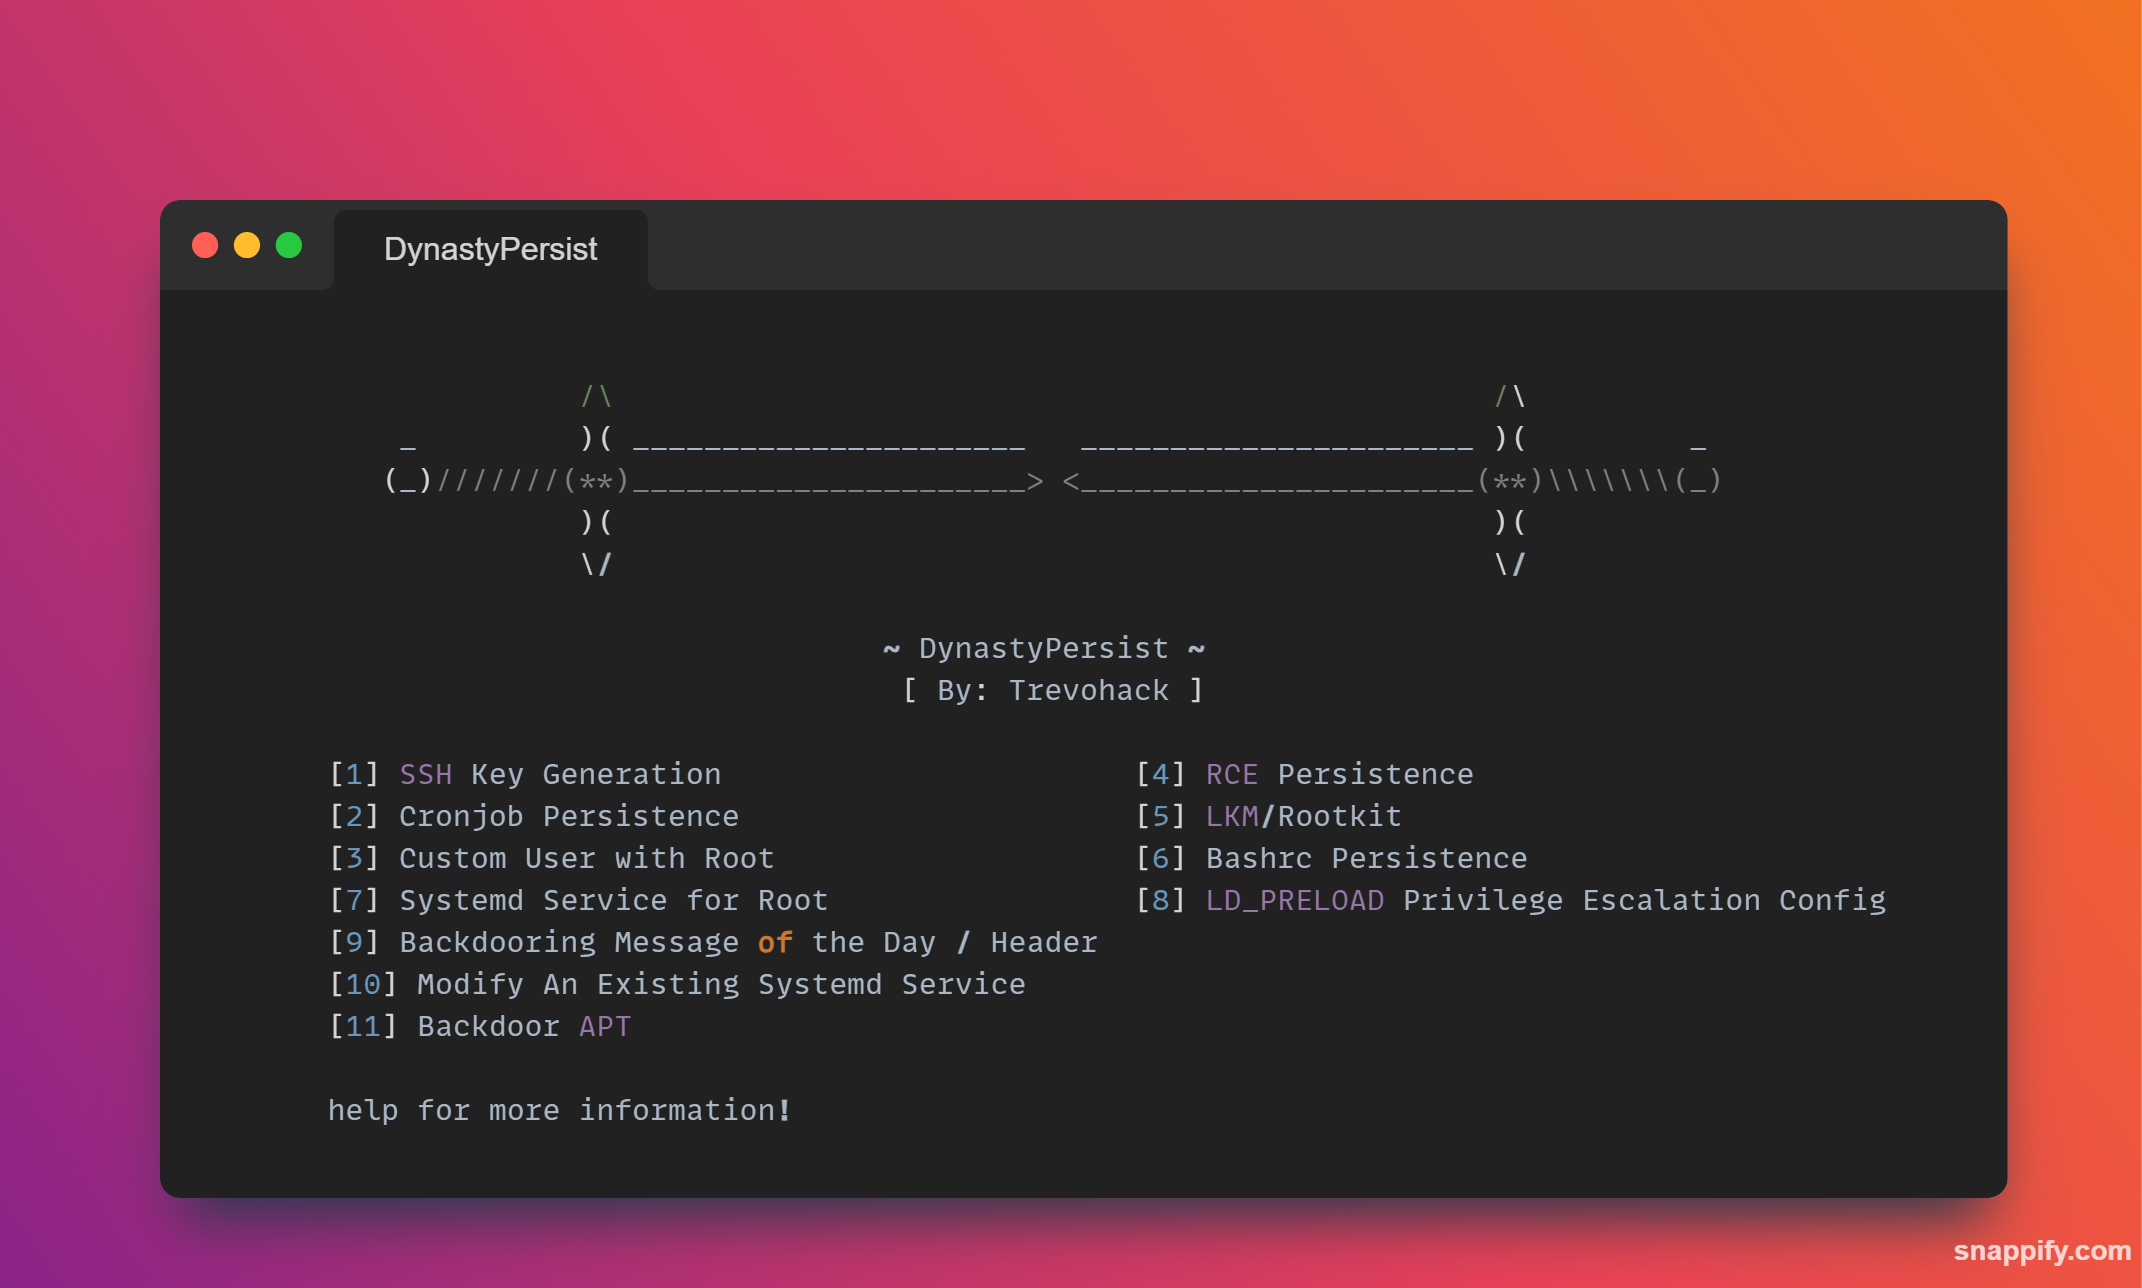 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
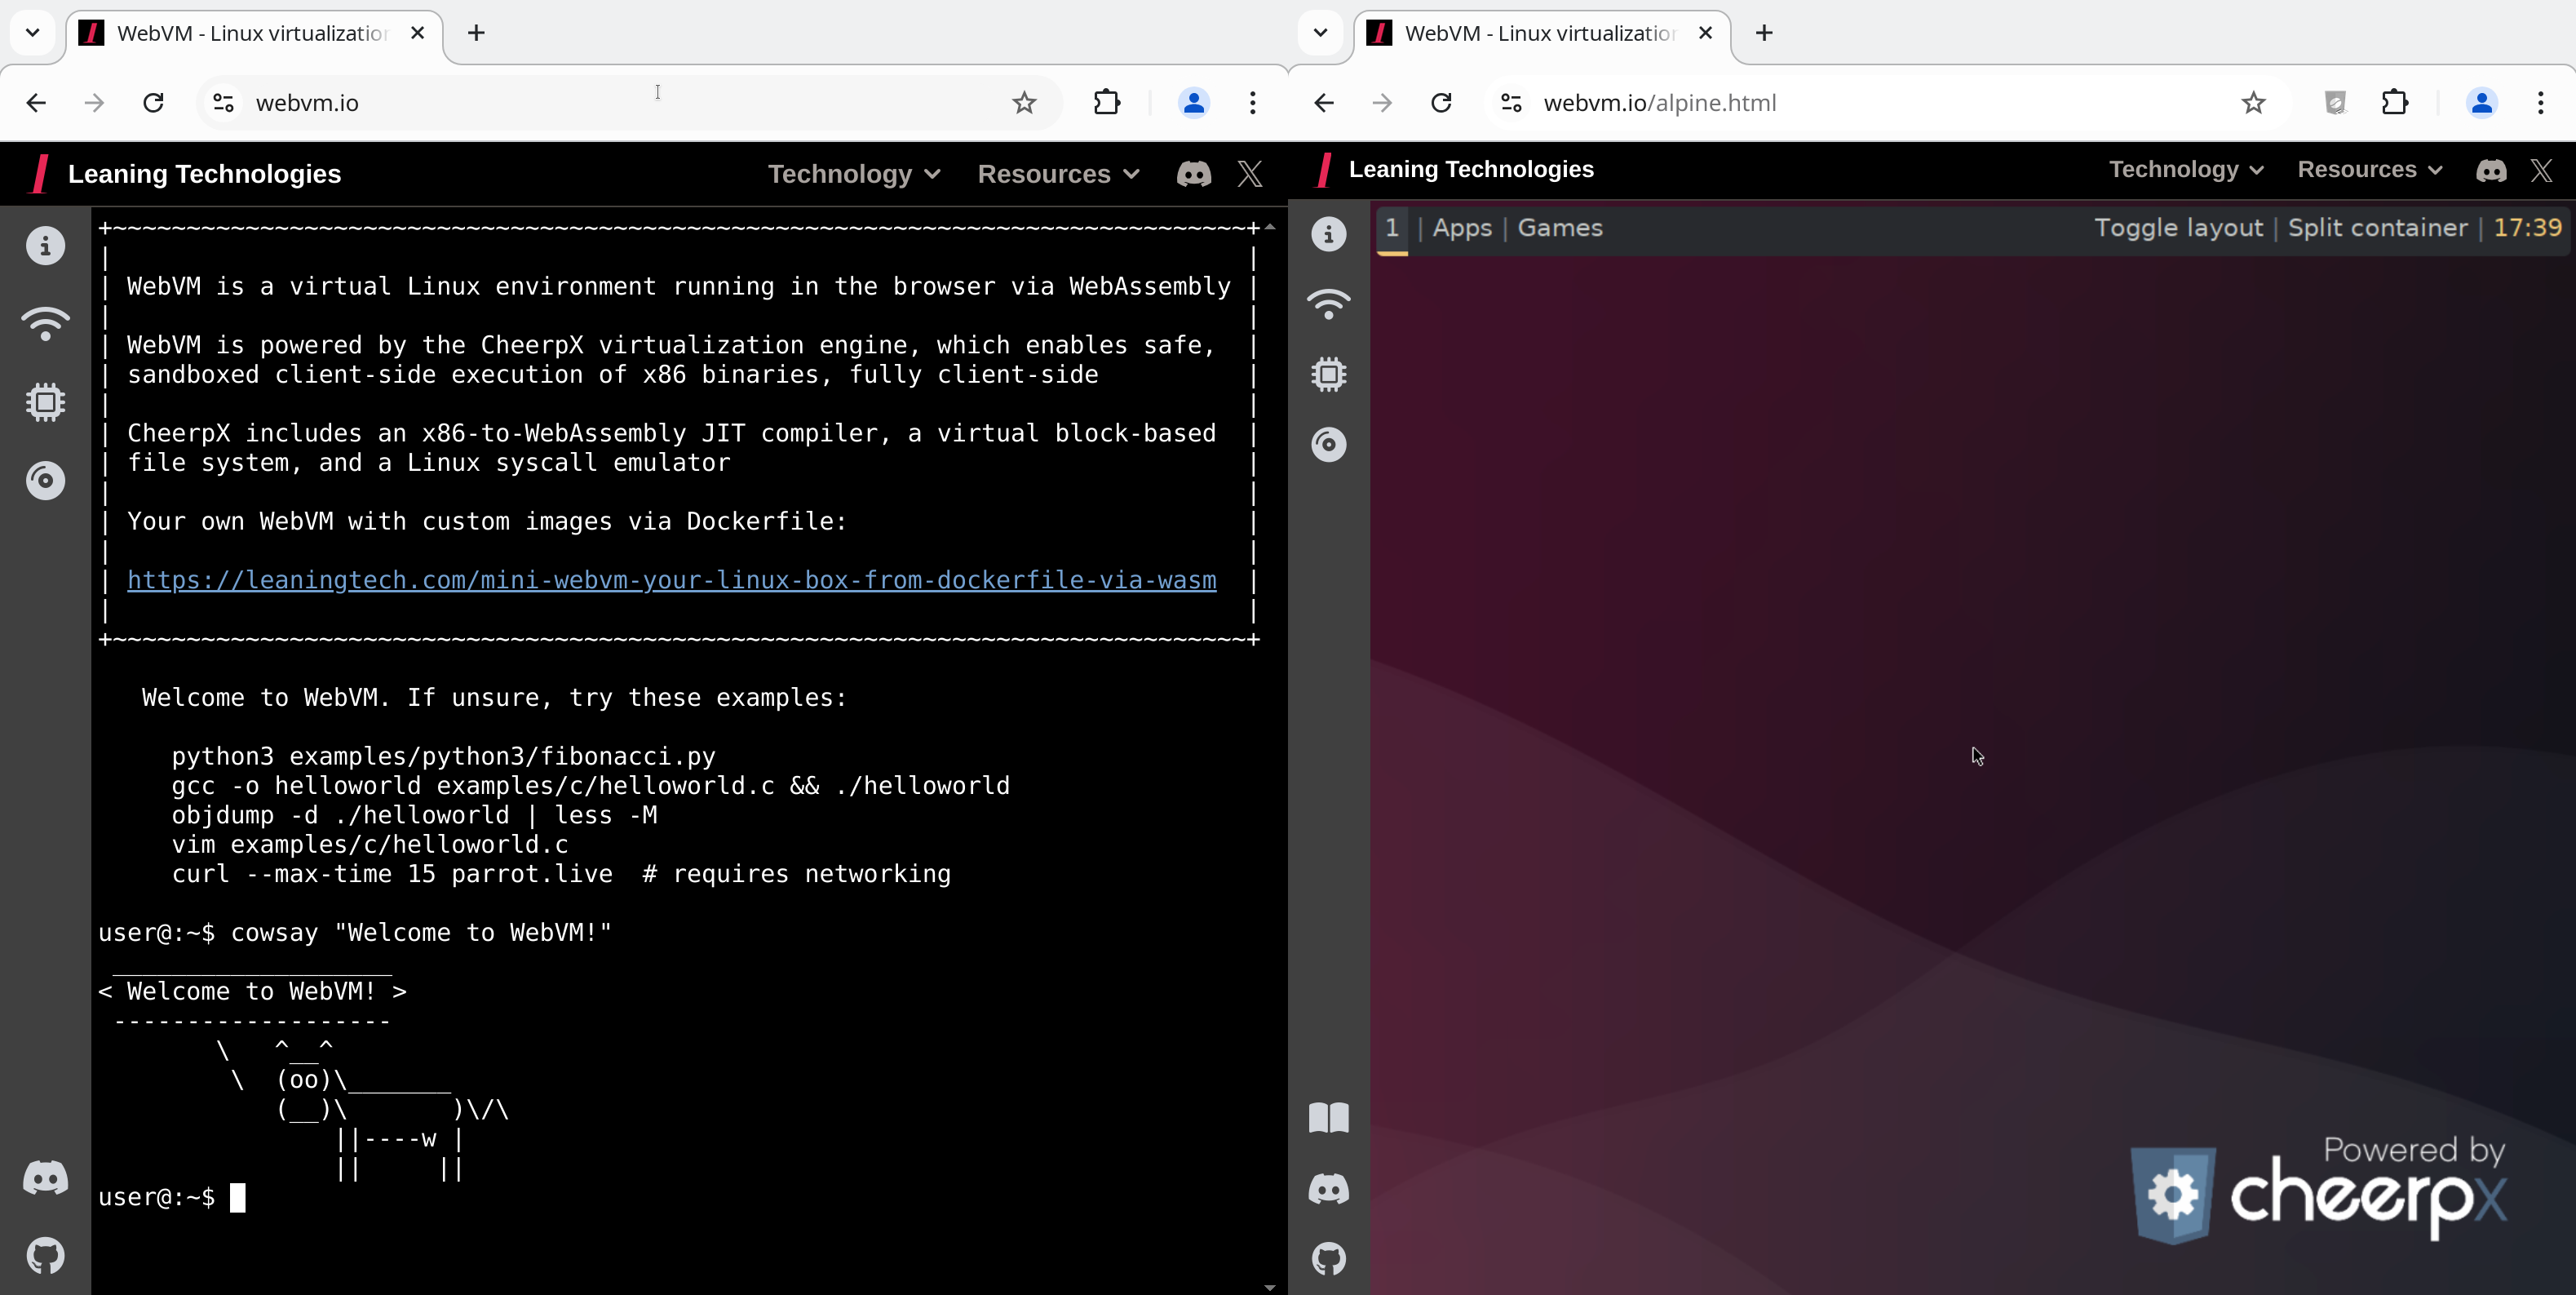 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 xairy/linux-kernel-exploitation
A collection of links related to Linux kernel security and exploitation
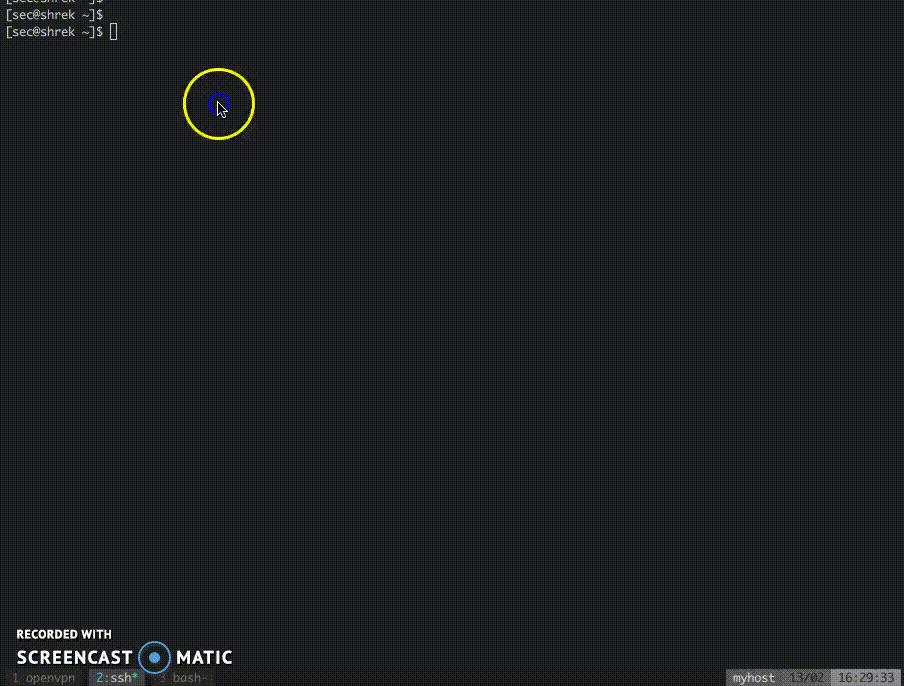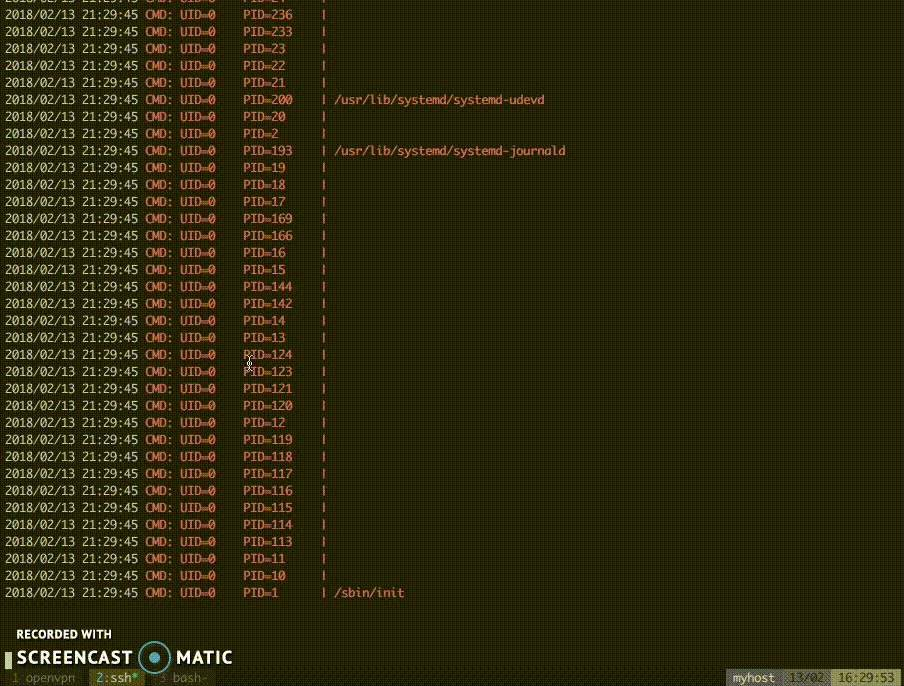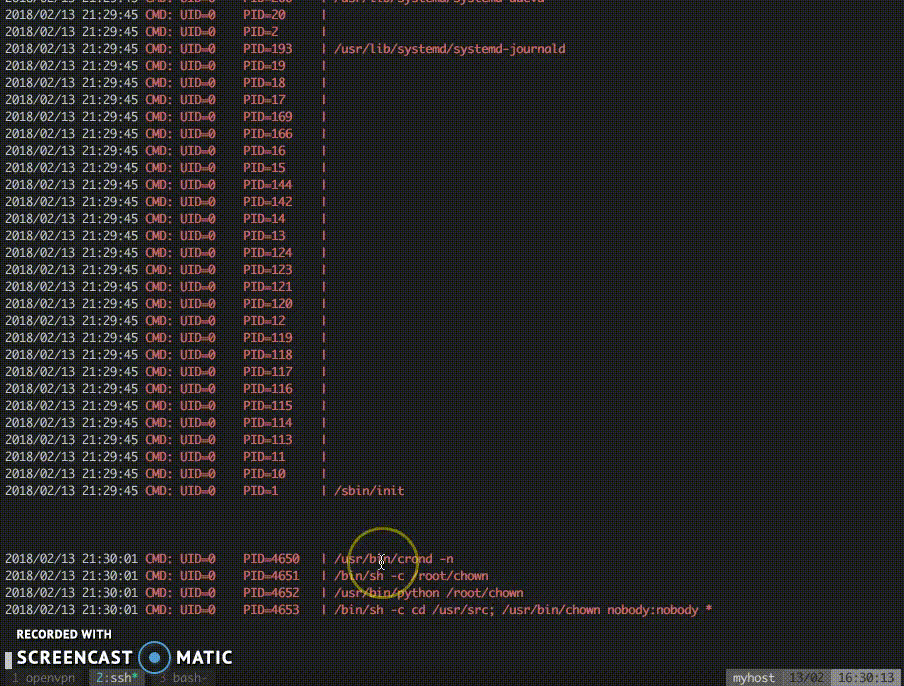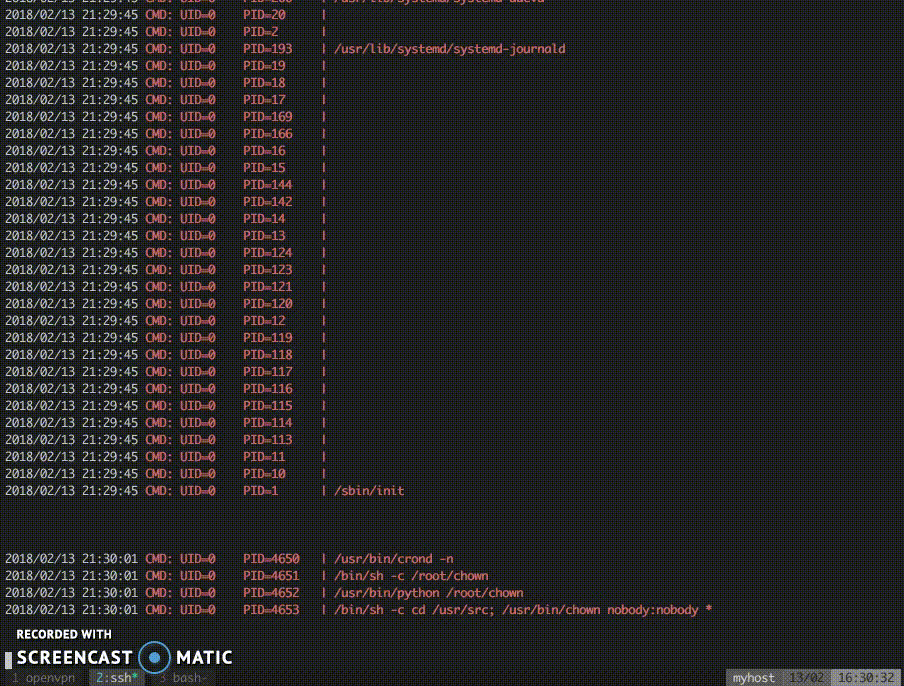 dominicbreuker/pspy
Monitor linux processes without root permissions
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
 ahegazy0/linux-basics-for-hackers-notes
A structured course built from personal study notes of the book Linux Basics for Hackers by OccupyTheWeb.
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
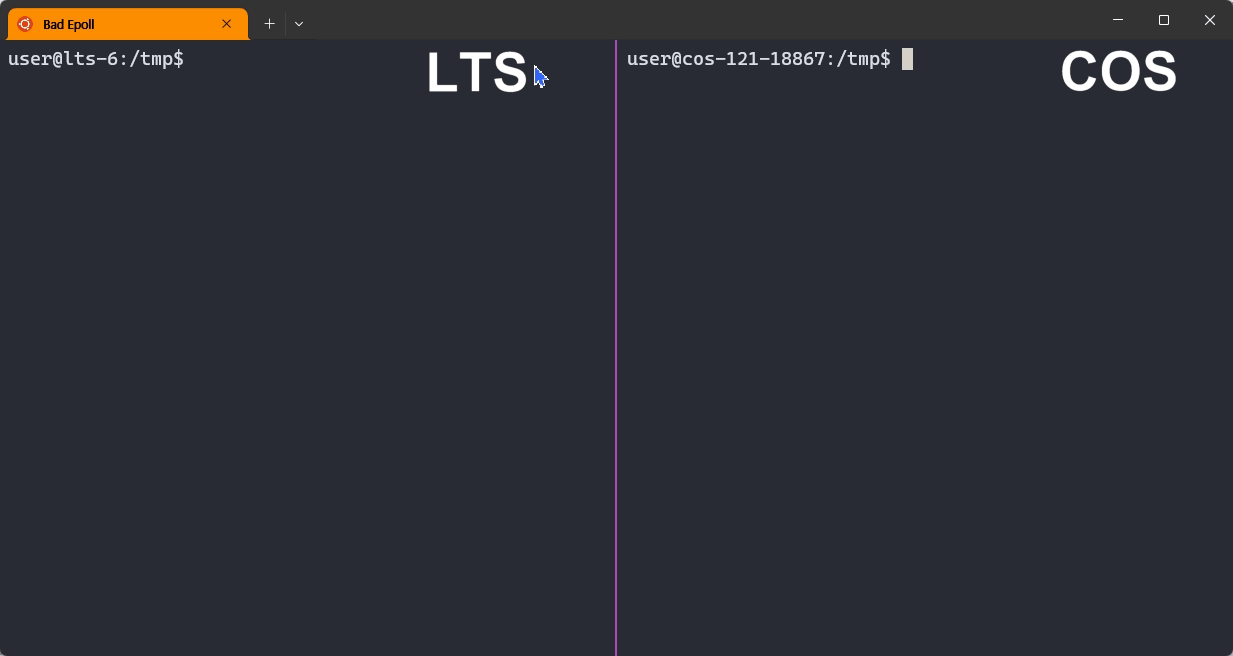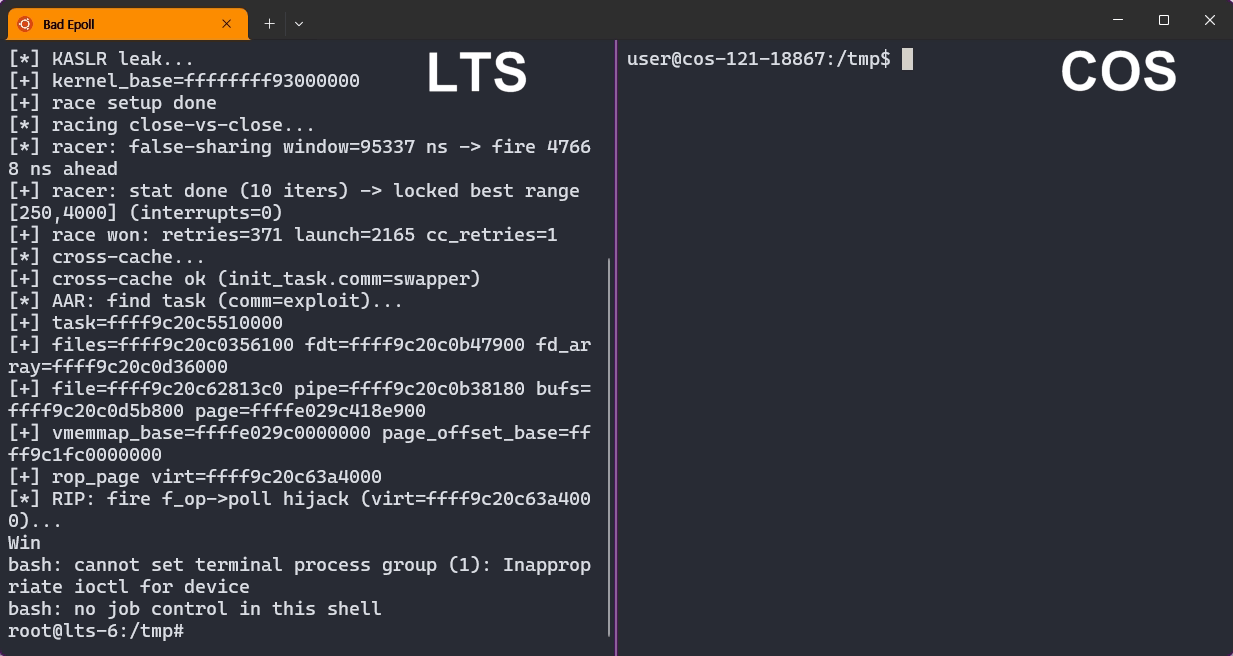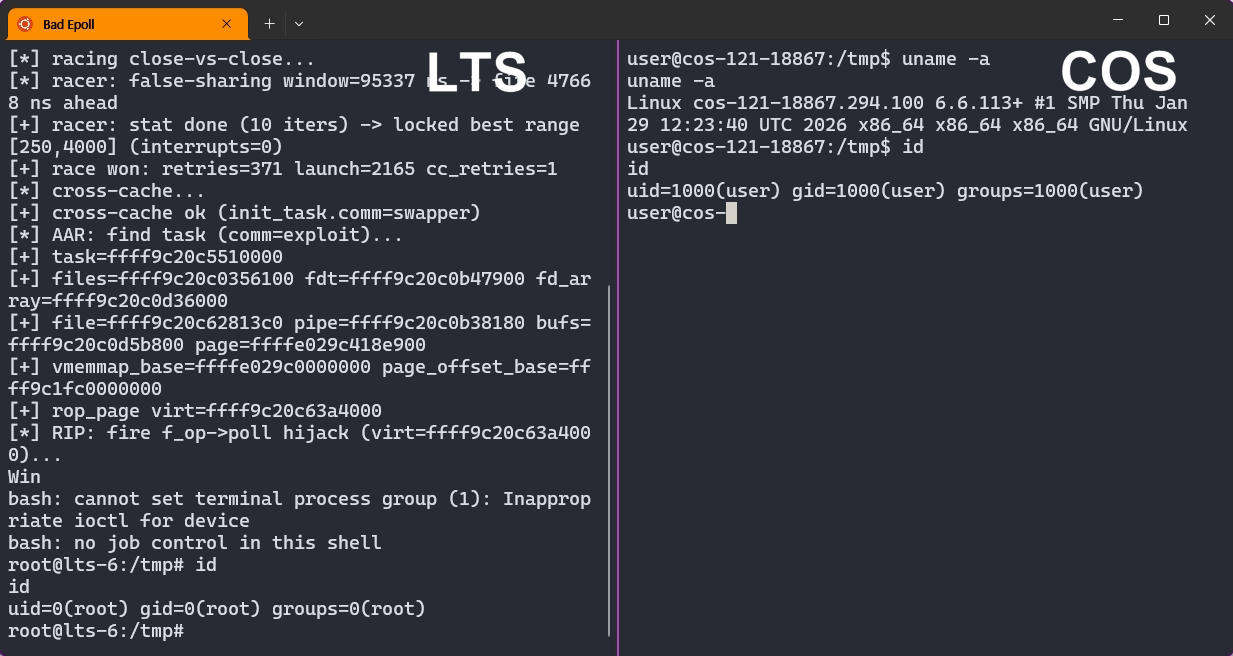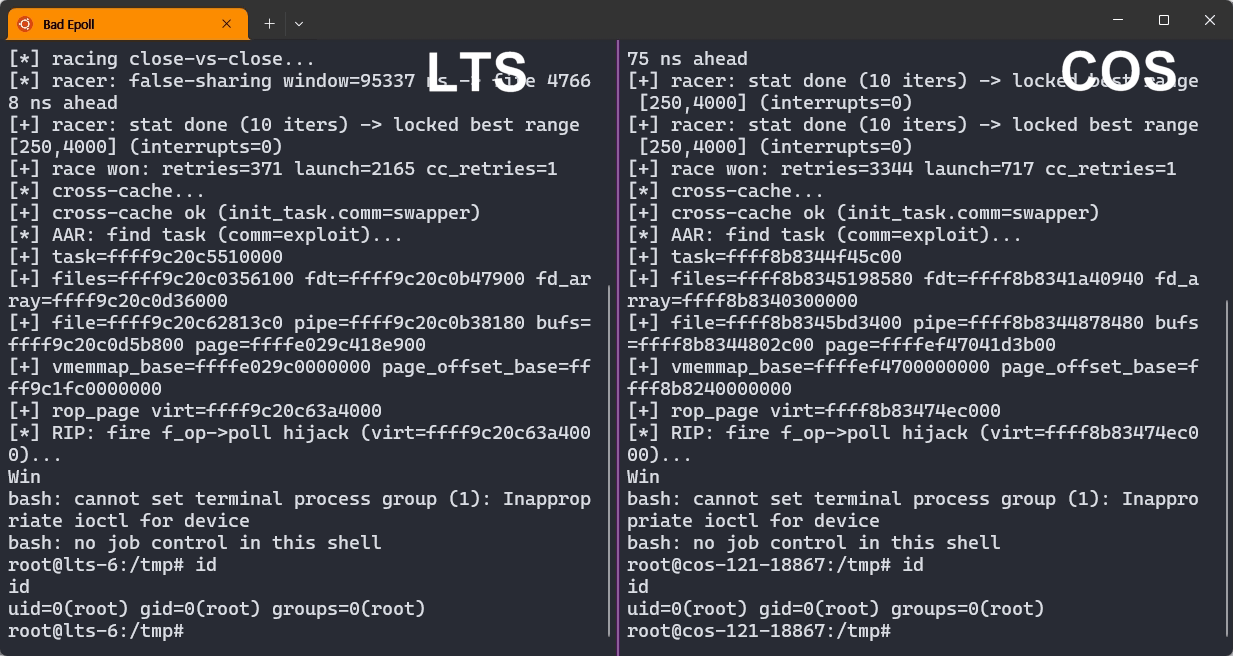 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…