cve-2011-2553
 carlosrpastrana/cve-2011-2553
Bash exploit for CVE-2011-2553 enabling remote code execution and privilege escalation on vulnerable FTP services via a special character in the USER…
ctfeducationexploitation+3
1
carlosrpastrana/cve-2011-2553Bash exploit for CVE-2011-2553 enabling remote code execution and privilege escalation on vulnerable FTP services via a special character in the USER…
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 aljavier/exploit_laravel_cve-2018-15133
Exploit for Laravel Remote Code Execution with API_KEY (CVE-2018-15133)
 phoenhex/files
Curated repository of exploits, proof-of-concept code, and vulnerability research presentations from the phoenhex team, focused on binary…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 naclapor/cve-2024-28397
This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).
 joaoaugustom/drupal_rest-rce_unauthenticated
This exploit is based on CVE-2019-6340 and was built upon the original exploit by leonjza and the Metasploit module, extending it can be executed…
 cd-ratel/cve-2025-32432
Working PoC for CVE-2025-32432 - Craft CMS <= 5.6.16 unauthenticated RCE via Yii2 PhpManager gadget + nginx access.log poisoning
 amusedx/cve-2026-22686
CTF challenge focused on sandbox escape via source code review of a JavaScript execution environment, designed for hands-on vulnerability analysis…
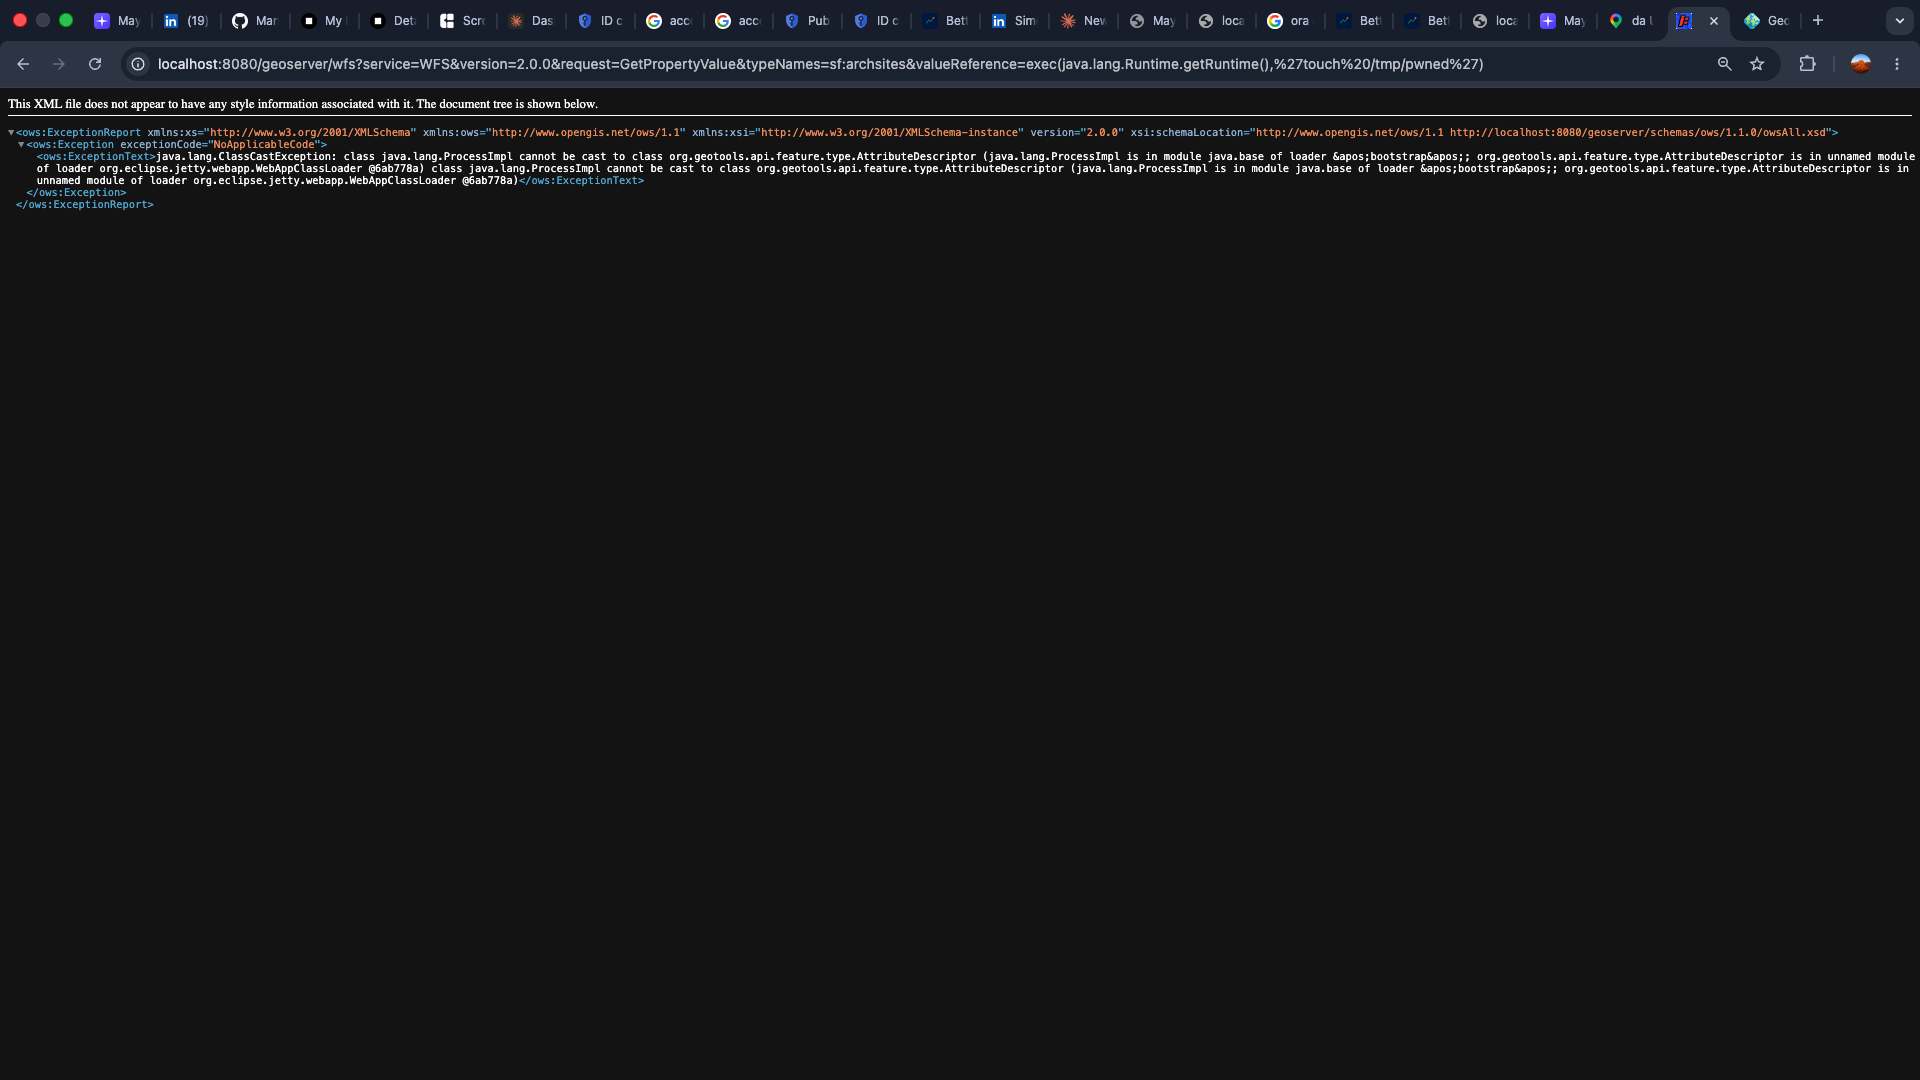 danielegiovanardi2408/cve-2024-36401-geoserver-rce
Reproducible study of CVE-2024-36401: unauthenticated RCE in GeoServer via JXPath eval injection. Includes technical report, working…
 hackerking24/cve-2026-30225-olivetin-rce
Proof-of-concept exploit for OliveTin unauthenticated RCE (CVE-2026-30225) via insecure guest defaults and unvalidated argument types, enabling root…
 josh-blythe/bordair-detector
Two-stage prompt-injection and jailbreak detector: regex gates plus a quantised DeBERTa-v3 ONNX classifier, with image, document, and audio support.…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10