thm-blue-writeup
 fernandotdalcin/thm-blue-writeup
Writeup da sala Blue do TryHackMe — exploração do EternalBlue (MS17-010/CVE-2017-0143).
ctfeducationexploitation+5
fernandotdalcin/thm-blue-writeupWriteup da sala Blue do TryHackMe — exploração do EternalBlue (MS17-010/CVE-2017-0143).
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.
 oscerd/process-injection-playground
A collection of samples and material related to process injection
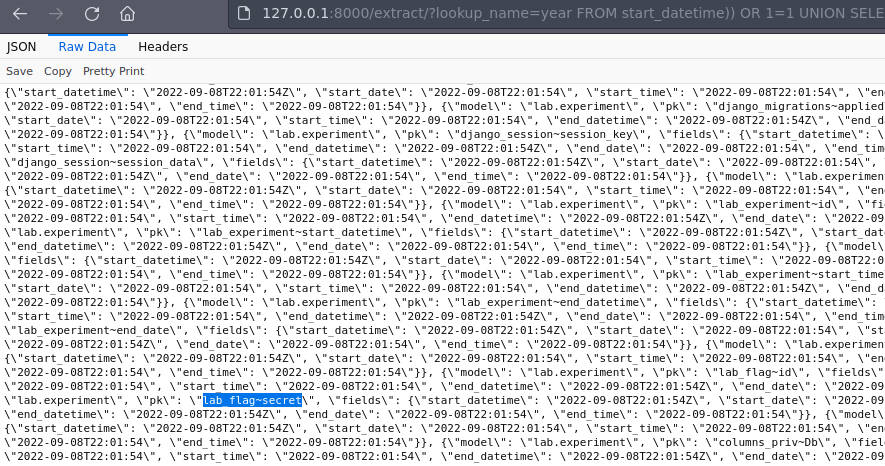 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…

 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 netw0rk7/cve-2012-2122-home-lab
CVE-2012-2122 MySQL Authentication Bypass Home Lab
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 yusufdalbudak/cve-2026-42945
Dockerized lab for training on NGINX rewrite vulnerability (CVE-2026-42945) with vulnerable and patched instances, benign test scripts, and…
 cyberone-teamares/jquery-cve-2022-31160
jquery XSS Proof of Concept (PoC)
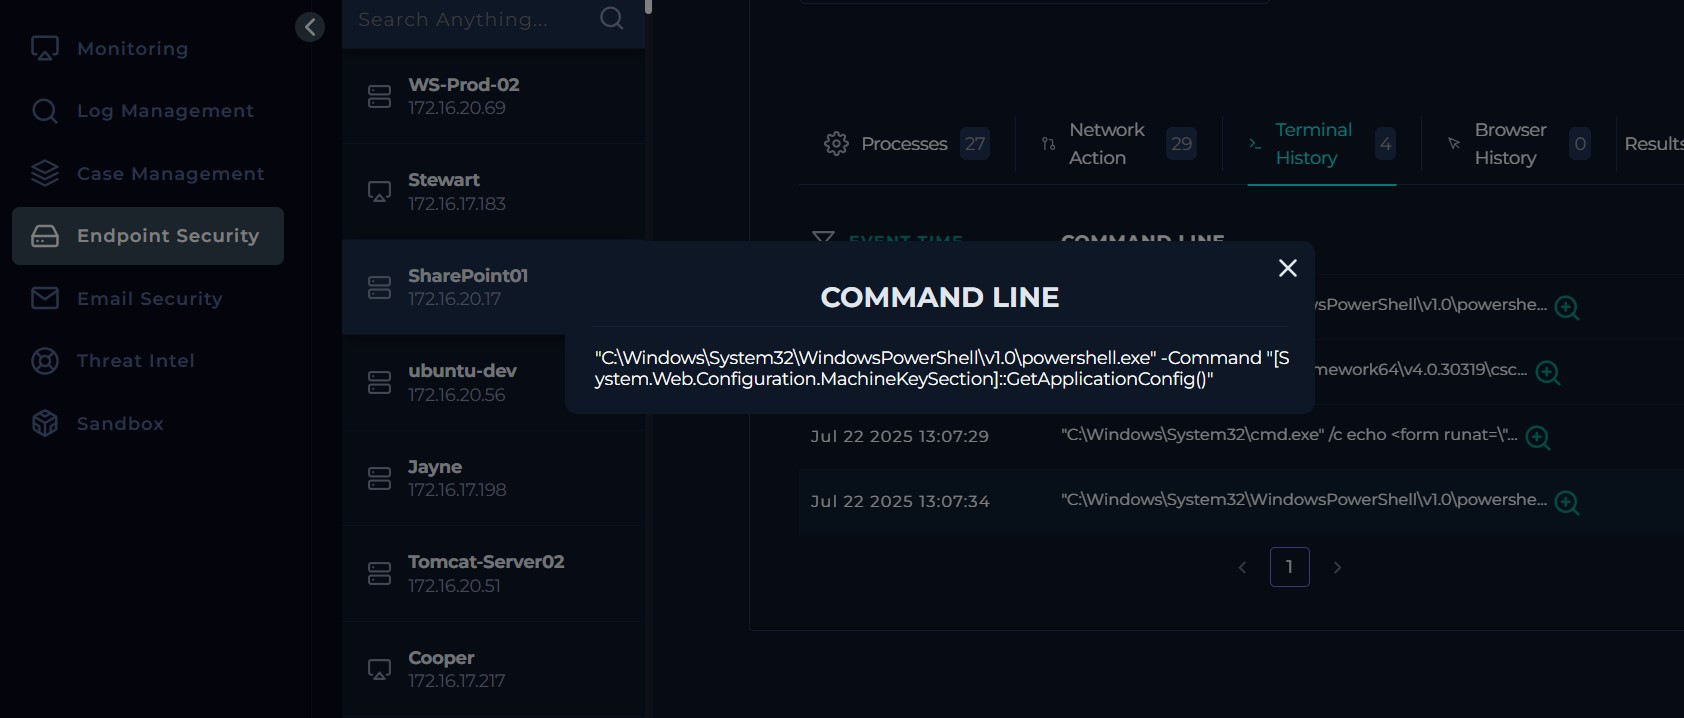 victormbogu1/letsdefend-soc342-cve-2025-53770-sharepoint-toolshell-auth-bypass-andrce-eventid-320
Step-by-step walkthrough of a LetsDefend SOC342 lab analyzing CVE-2025-53770 SharePoint ToolShell auth bypass and RCE, including attack chain,…
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
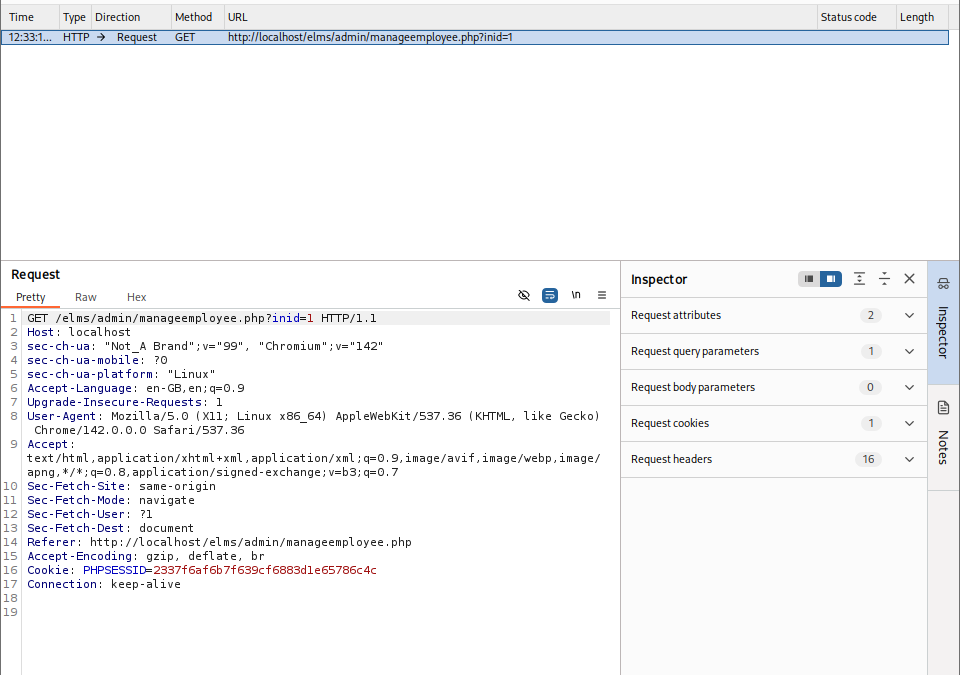 r-pradyun/cve-2025-67315
CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
 tempuss/ctf_cve-2020-7471
CTF challenge exploiting CVE-2020-7471, a Django SQL injection vulnerability in PostgreSQL StringAgg, with Docker setup and exploit scripts.
 gokul-krishnan-v-r/cve-2024-53900
Mongo Vulnub Lab...Try to Hack IT.....!