

linux-smart-enumeration
 diego-treitos/linux-smart-enumeration
Linux enumeration tool for pentesting and CTFs with verbosity levels
ctfinformation-gatheringpenetration-testing+2
4.0k
diego-treitos/linux-smart-enumerationLinux enumeration tool for pentesting and CTFs with verbosity levels
 dolevf/damn-vulnerable-graphql-application
Damn Vulnerable GraphQL Application is an intentionally vulnerable GraphQL service implementation designed for learning about and practising GraphQL…
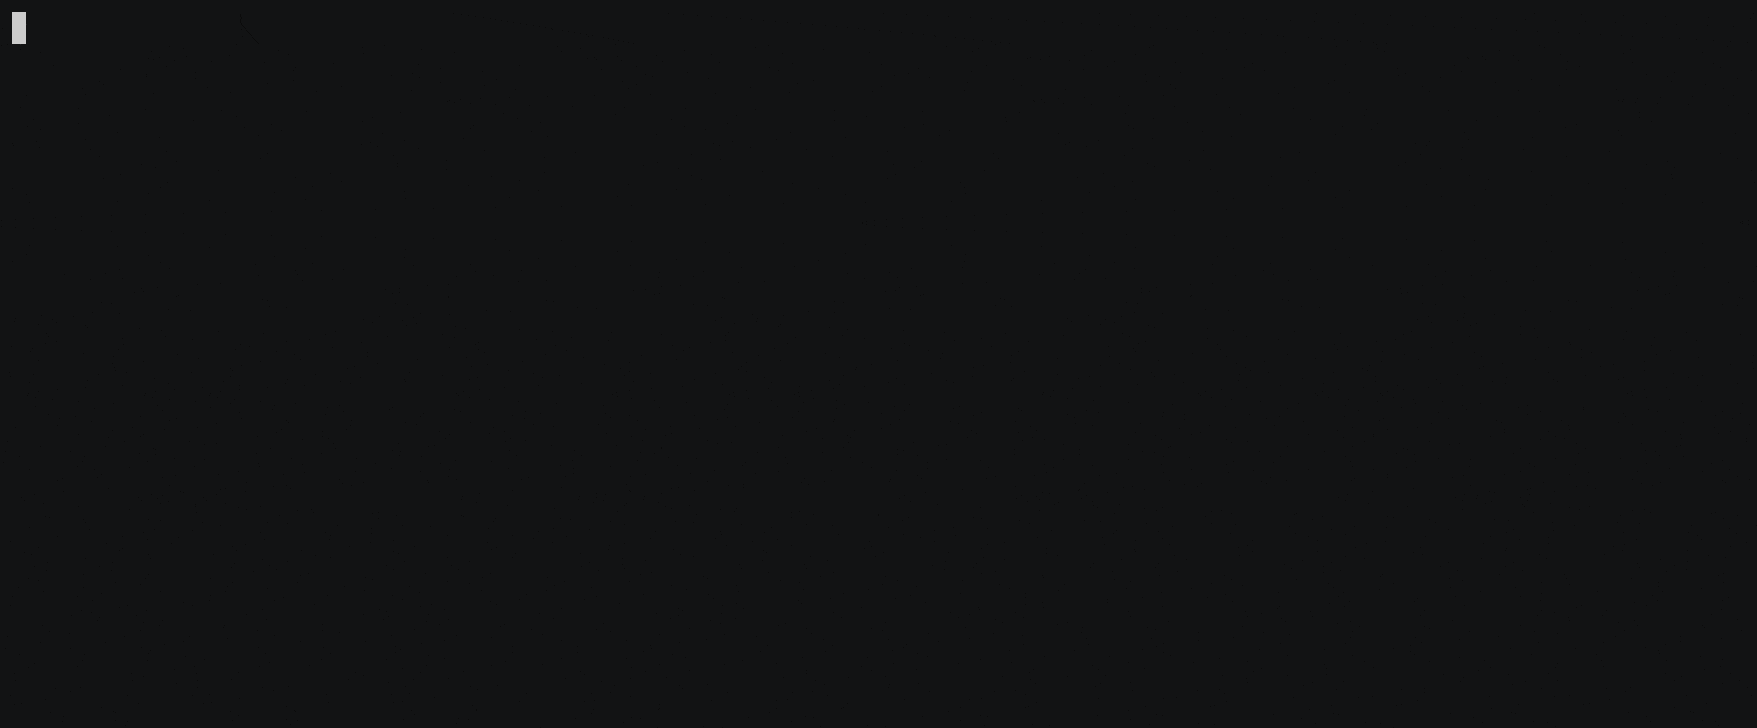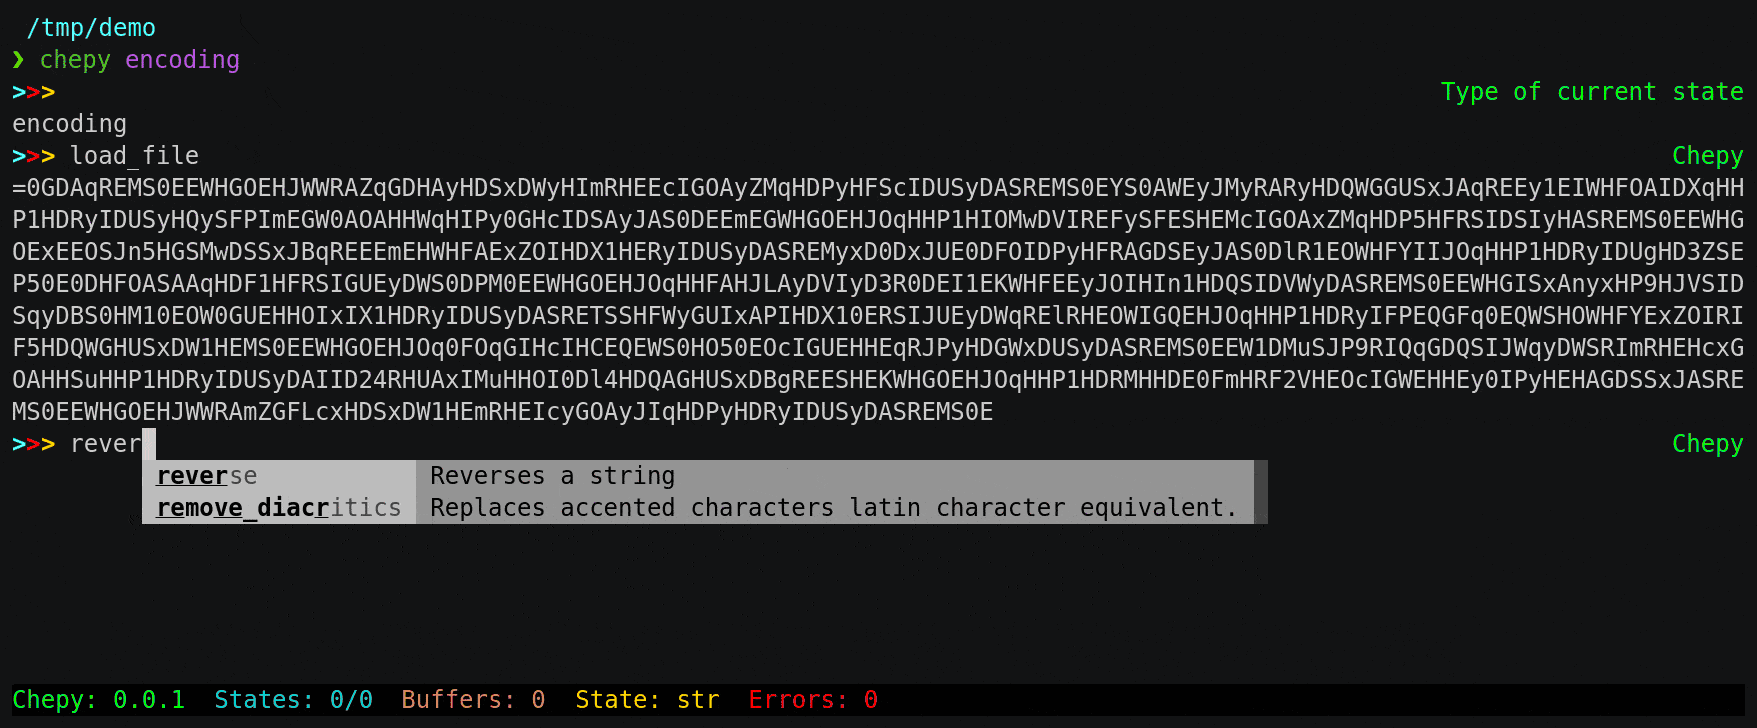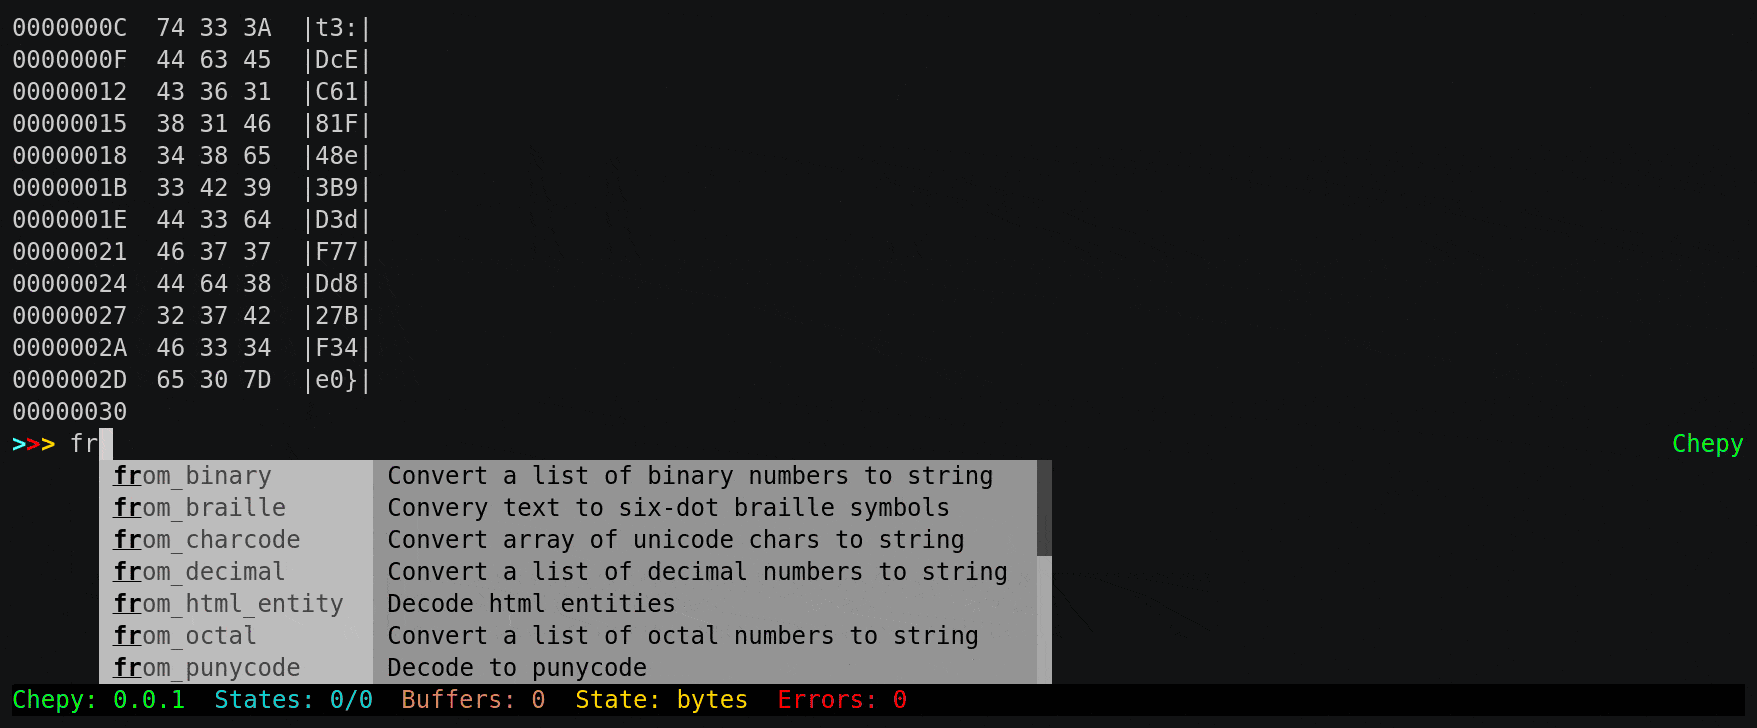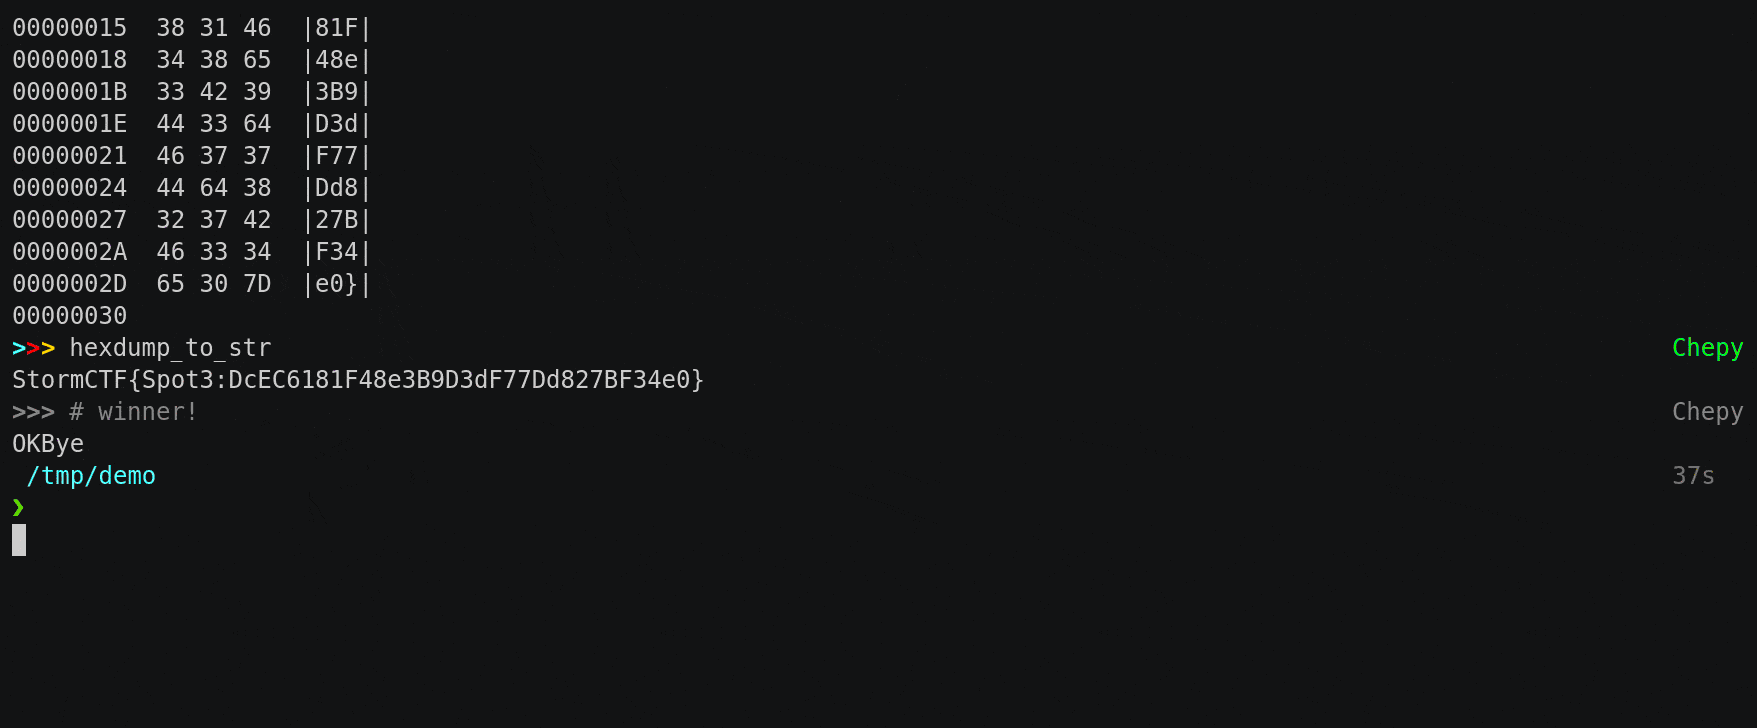 securisec/chepy
Chepy is a python lib/cli equivalent of the awesome CyberChef tool.
 mhaggis/security-detections-mcp
MCP to help Defenders Detection Engineer Harder and Smarter
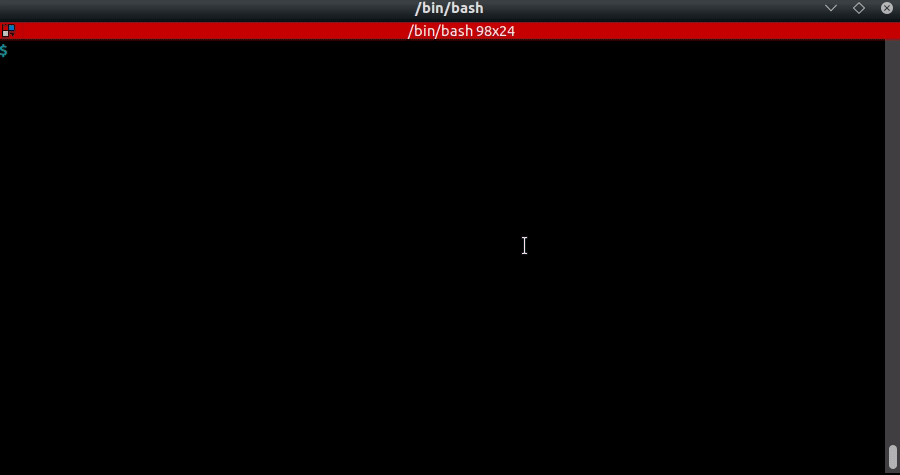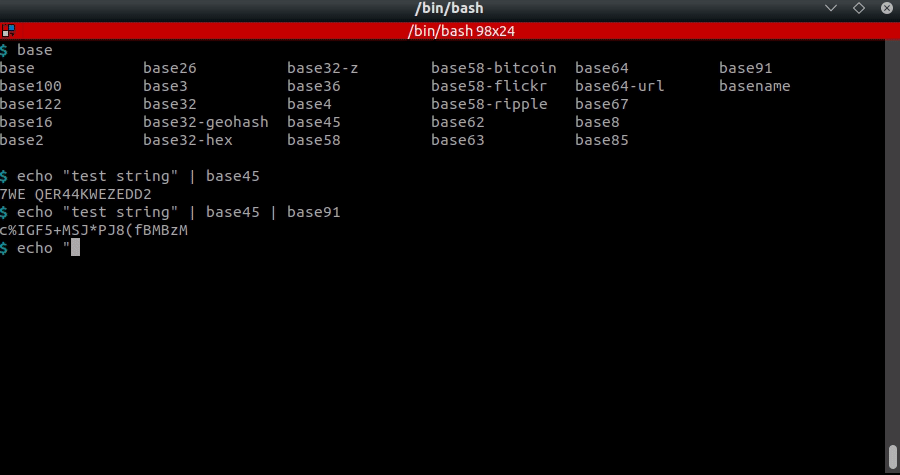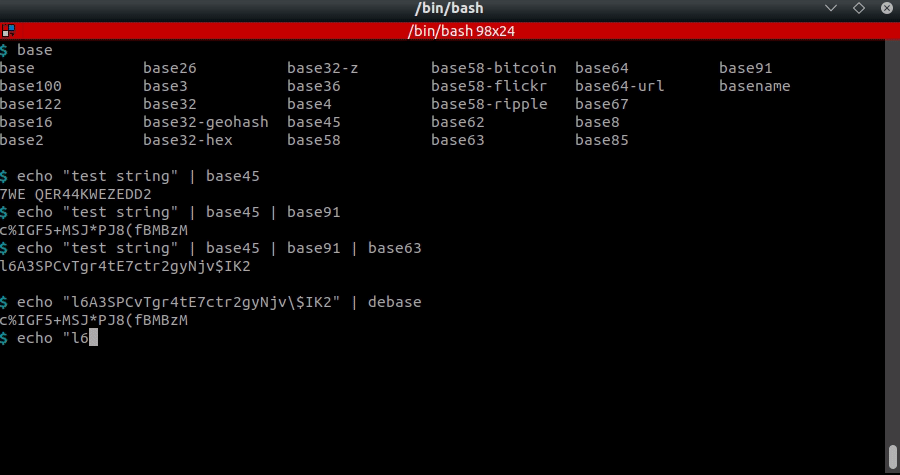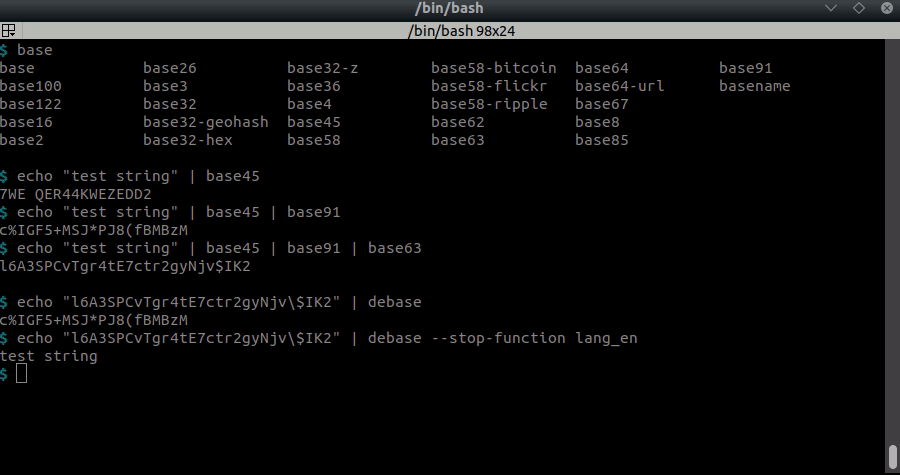 dhondta/python-codext
Python codecs extension featuring CLI tools for encoding/decoding anything
 gmh5225/awesome-ai-security
A curated list of AI Security materials and resources for Pentesters, Bug Hunters, and Security Researchers.
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 vladko312/research_successful_errors
Whitepaper introducing Error-Based and Boolean Error-Based Blind techniques for SSTI and Code Injection, with universal payloads for six programming…

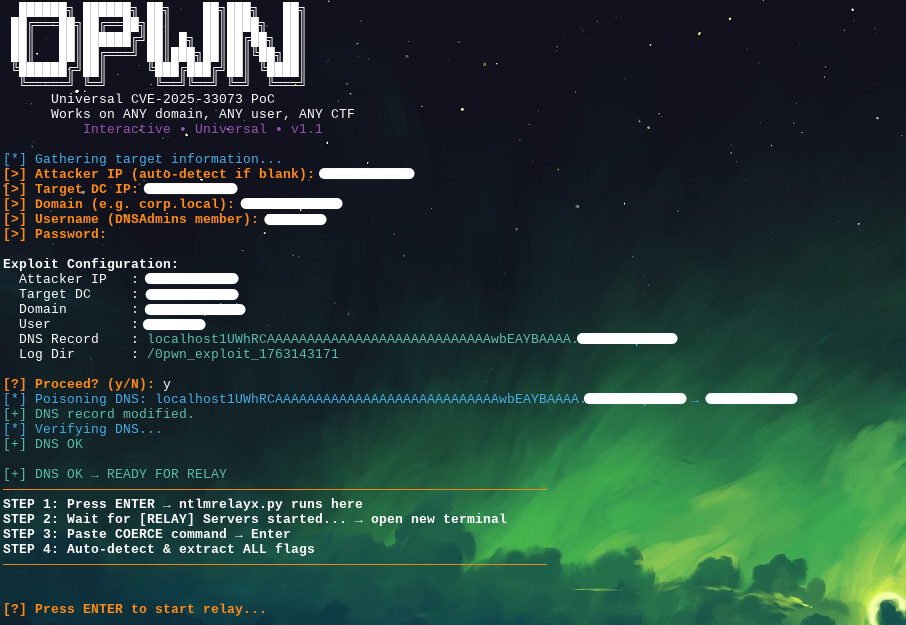 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files
 maxmnml/langflow-cve-2026-33017-poc
CVE-2026-33017 - An unauthenticated remote code execution in Langflow <= 1.8.1 via Public Flow Build Endpoint
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 naclapor/cve-2024-28397
This repository contains a python exploit code for CVE-2024-28397 intended for use on the "CodePartTwo" machine on Hack The Box (HTB).
 adityabhatt3010/react2shell-cve-2025-55182
React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…
 flojboj/cve-2022-0944
SQLPad - Template injection (POC exploit for SQLPad RCE [CVE-2022-0944])
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…