
 mister-iks/pcybox-attackgraph
Open source browser lab to build a simulated infrastructure, watch an attack move through it, and check whether your defense works.
 al1ex/awesome-pentest
Collection of penetration testing tools
 knowledge-wisdom-understanding/recon
Enumerate a target Based off of Nmap Results
 th3xace/offport_killer
This tool aims at automating the identification of potential service running behind ports identified manually either through manual scan or services…
 spritualkb/cve-2025-55182-exp
CVE-2025-55182 React Server Components Remote Code Execution Exploit Tool
 weirdmachine64/sharkmcp
A swiss-knife MCP server for analysing PCAP files

 abrewer251/cve-2025-62215_windows_kernel_pe
This PoC demonstrates a race condition in the Windows kernel leading to a double-free vulnerability, allowing local privilege escalation to SYSTEM.…
 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 muhammednihalmp/google-chrome-zero-day
CVE-2025-6554
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 jimmyader/cheatsheethost
A locally hosted page for cheat sheets. Currently being used for reverse engineering and hosted in labs so I can limit or forgo (lock down firewall)…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
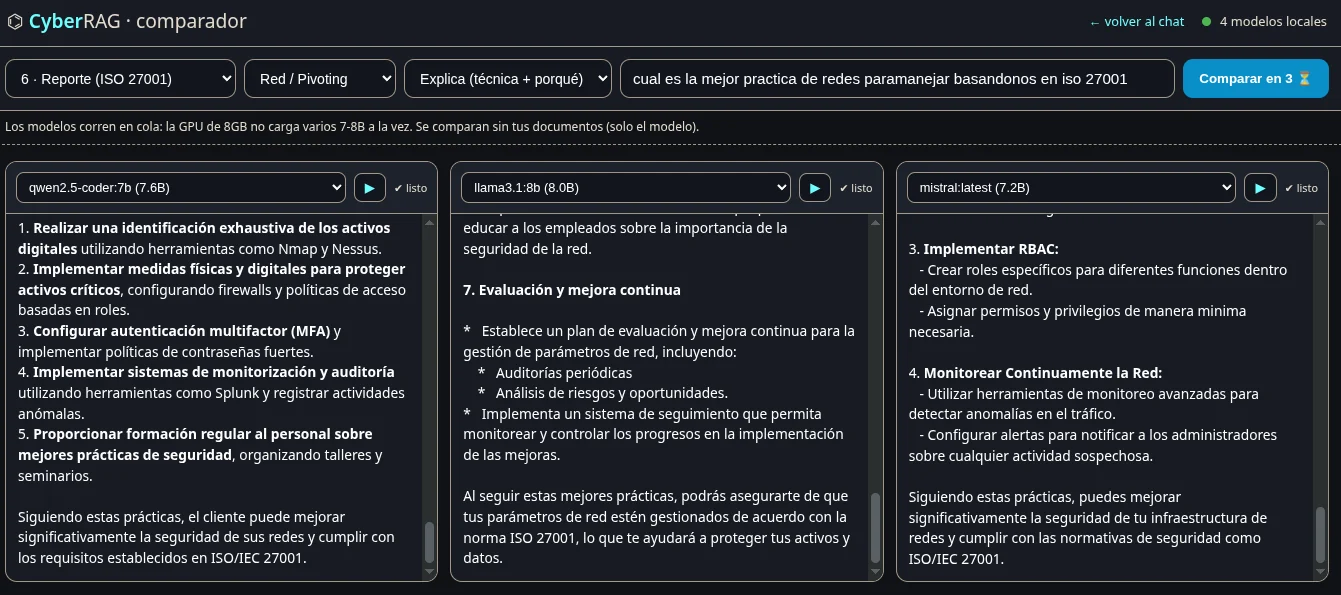
 rdelasierra-uy/rag-seguridad
CyberRAG — RAG 100% local (Ollama) sobre apuntes y libros de ciberseguridad: recuperación híbrida, respuestas con citas, asistente de pentest por…
 0xgh057r3c0n/cve-2025-6934
CVE-2025-6934 is a critical vulnerability in the WordPress Opal Estate Pro plugin (<= 1.7.5) that allows unauthenticated attackers to create new…
 randomuser1983/ikeabuser
A simple tool wrapper to automate the enumeration, fingerprinting, and PSK extraction of an IPSec VPN gateway.
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab