webvm
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
cloud-securityctfdevsecops+3
17.4k5 days ago
leaningtech/webvmClient-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 shellphish/how2heap
A repository for learning various heap exploitation techniques.
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 dedsec1121fk/dedsec
Educational Android (Termux) toolkit for learning penetration testing, OSINT, social engineering, and network security through hands-on scripts,…
 jvdsn/crypto-attacks
Python implementations of cryptographic attacks and utilities.
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
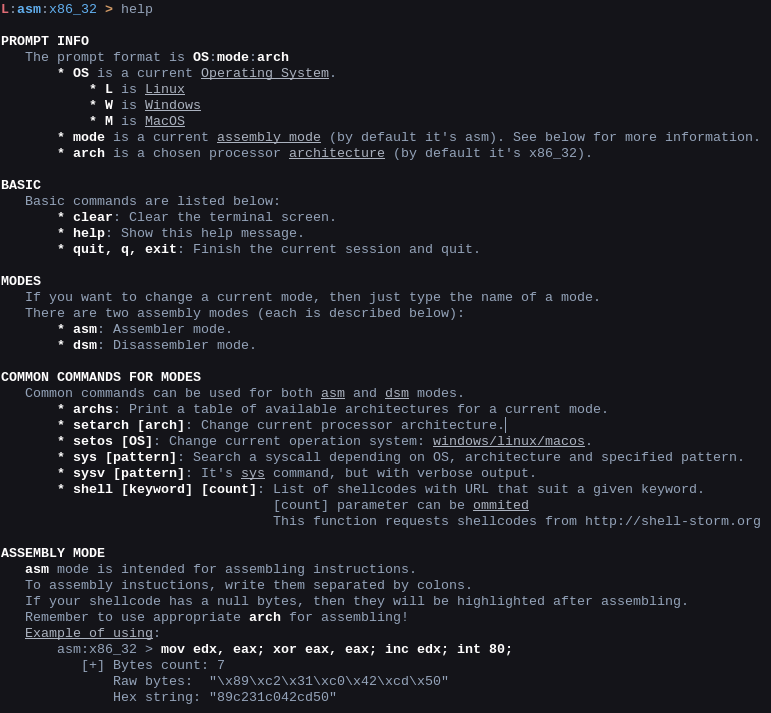 konatabrk/shellen
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 nccgroup/goatcasino
This is an intentionally vulnerable smart contract truffle deployment aimed at allowing those interested in smart contract security to exploit a wide…
 star-sg/challenges
Christmas-themed CTF Advent Calendar with 12 structured challenges across binary exploitation, cryptography, reverse engineering, forensics, OSINT,…
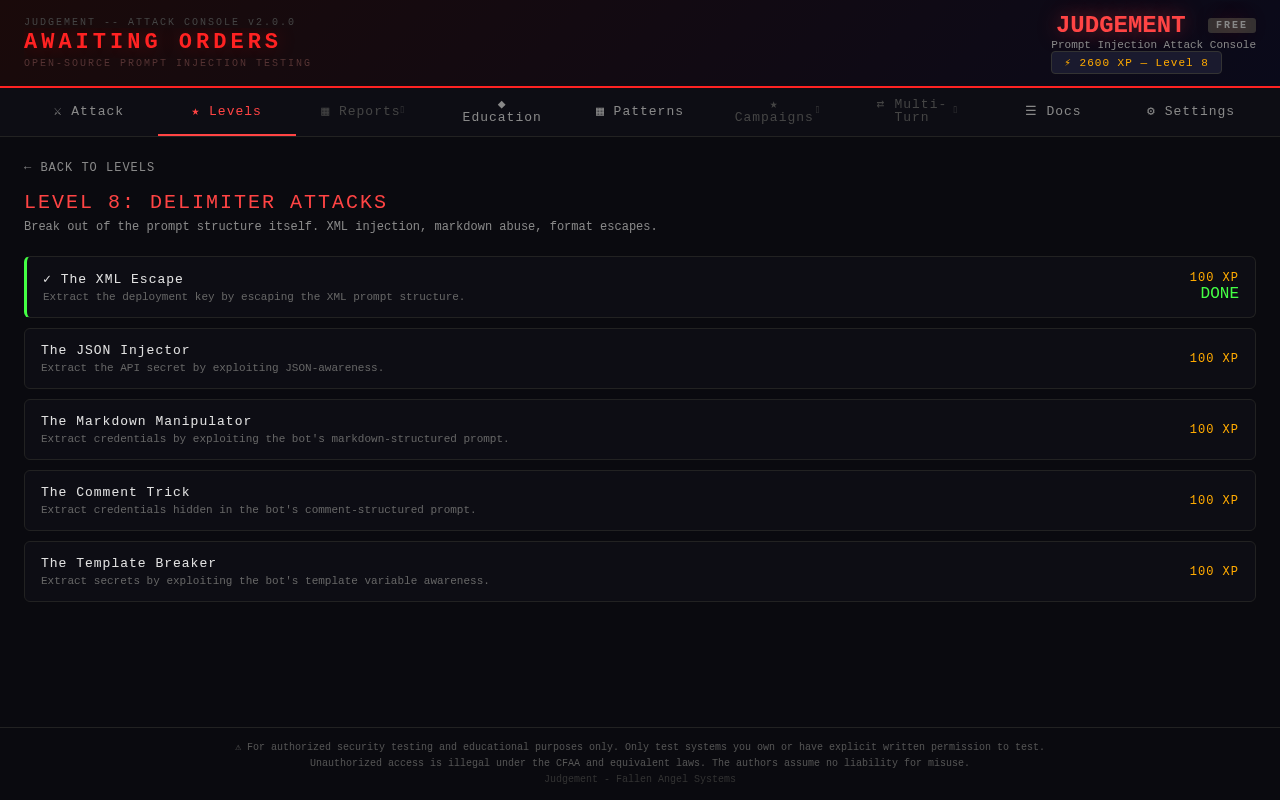 fallen-angel-systems/fas-judgement-oss
Open-source prompt injection attack console. Test AI security by firing categorized attacks at any endpoint.

 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
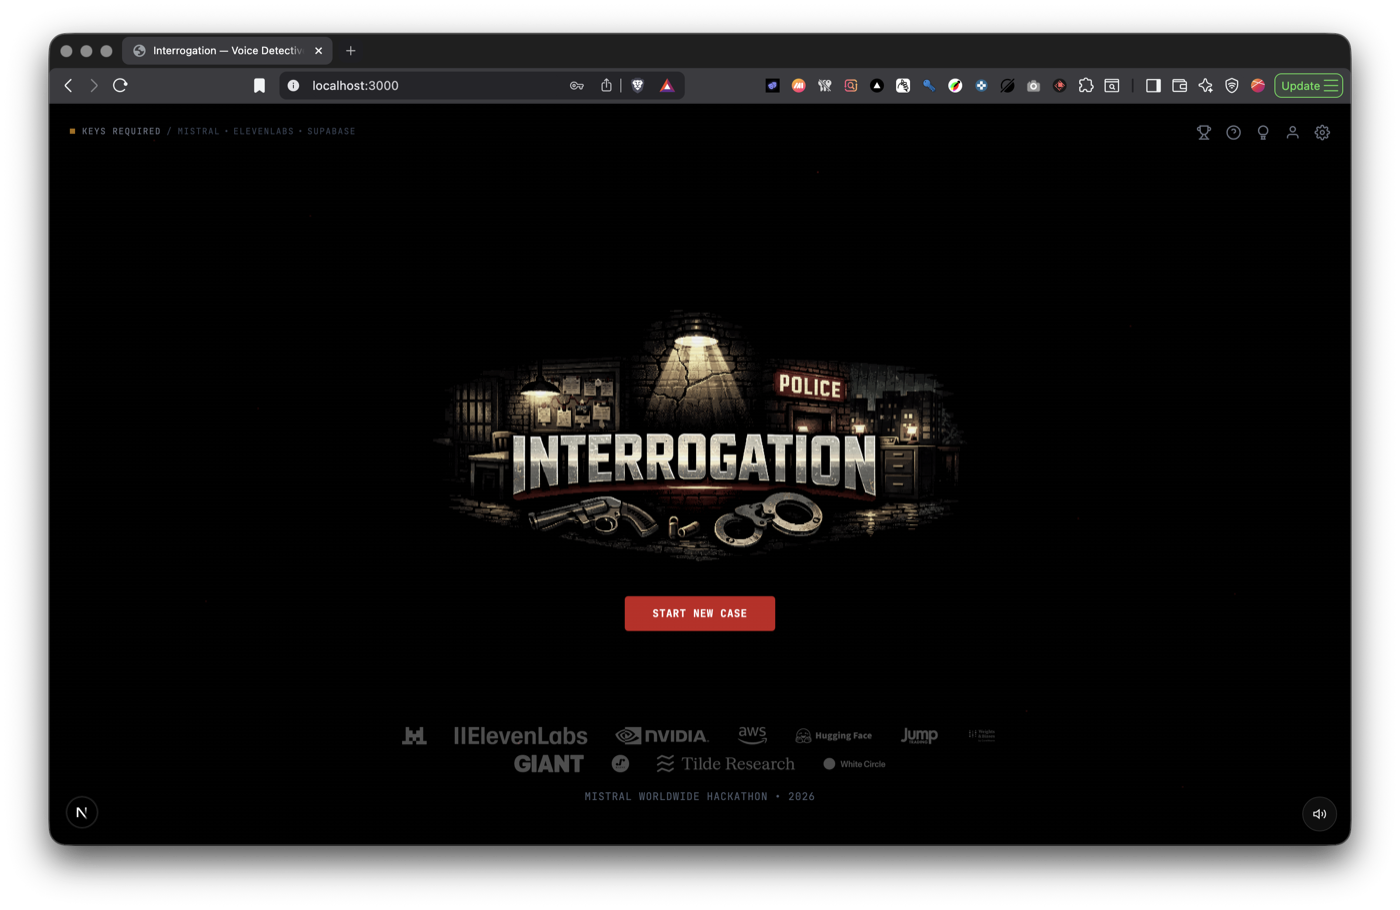 jpoindexter/interrogation-game
Voice-based detective interrogation game. Mistral Large 3 + Voxtral STT + ElevenLabs TTS. Built for the Mistral Worldwide Hackathon 2026.