

metasploitable3-pentest-writeup
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
adfortunato/metasploitable3-pentest-writeupHome-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 ledksv/pterodactyl
HackTheBox Pterodactyl walkthrough chaining CVE-2025-49132 path traversal, hash cracking, and CVE-2025-6018/6019 PAM and XFS race for root.
 aiyakami/cve-2021-21974
自研针对ESXI 堆栈溢出的CVE-2021-21974 POC,只支持项目给出的的目标和环境,用于学习和研究
 ayham-megdadi/zero-day-legacy
A vulnerable Boot-to-Root CTF lab machine simulating a hospital environment. Features a realistic 17-step attack chain including SQL Injection, XSS,…
 saku0512/cve-2026-54686-poc
Local PoC for CVE-2026-54686 demonstrating DCS lifecycle hook spoofing in Warp terminal. Simulates spoofed CWD and SSH metadata acceptance in…
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
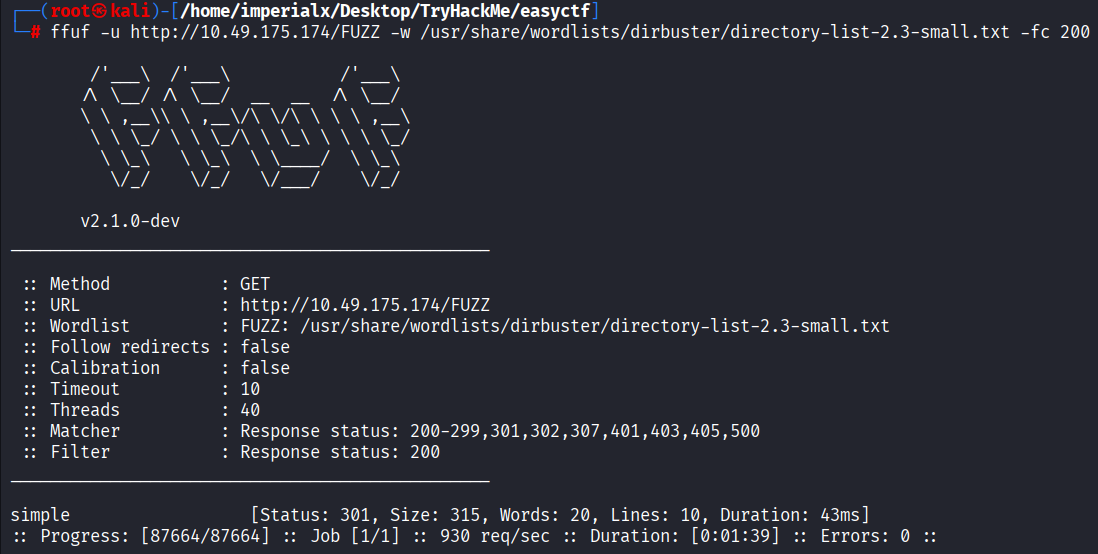 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 ledksv/principal-hackthebox
Detailed walkthrough of exploiting CVE-2026-29000 in pac4j-jwt to bypass authentication, extract credentials from API settings, and escalate…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
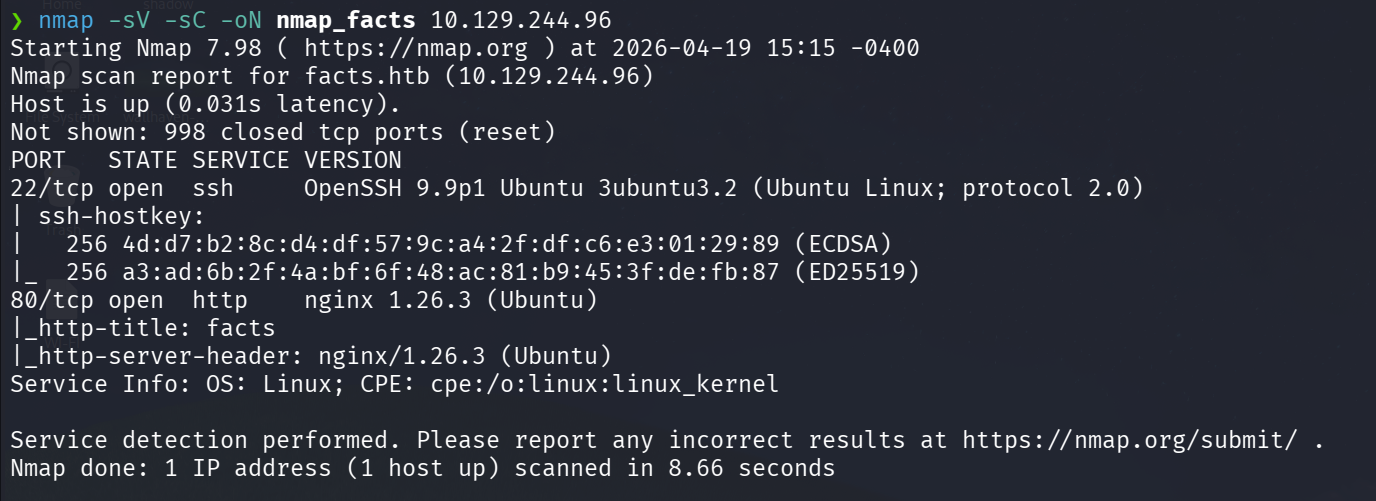 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 revshellxd/lfi-destruction
This program Prompts you for the Local File Inclusion information and will automatically search the /etc/passwd and using the users names found will…
 trevohack/dynastypersist
Linux persistence toolkit with 11 modules for SSH key backdoors, cronjobs, systemd services, LKM rootkits, and LD_PRELOAD privilege escalation.…
 niteeshpujari/cve-2025-32433-poc
Proof-of-concept exploit for CVE-2025-32433, enabling unauthenticated remote code execution in Erlang/OTP SSH. Includes Docker setup and reverse…