
 shauryarathore357-hub/thm-moniker-link-cve-2024-21413-writeup
TryHackMe room walkthrough of CVE-2024-21413, covering the Outlook Moniker Link Protected View bypass, NTLM hash leaking, and credential capture with…
 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 xmyronn/cve-2026-11518-xss
Proof-of-concept for unauthenticated stored XSS in SourceCodester Inventory System, demonstrating admin session hijacking via crafted registration…
 scottalt/ai-email-threat-research
A cybersecurity research game measuring how humans detect AI-generated phishing emails. Built as a retro terminal experience.
 c-g-creator/letsdefend-soc336-windows-ole-zero-click-rce-exploitation-detected-cve-2025-21298
LetsDefend SOC336 case study on CVE-2025-21298
 pedro-lucas-melo/estudo-de-caso-cve-2024-21413
Um estudo de caso do CVE-2024-21413. Usado como parâmetro a sala do TryHackMe Moniker Link (CVE-2024-21413). Feito edições com claude code no exploit.
 themursalin/htb-mailing-a-complete-walkthrough
If you've been grinding through HackTheBox machines, Mailing is one of those boxes that genuinely teaches you something. It's rated Easy, runs on…
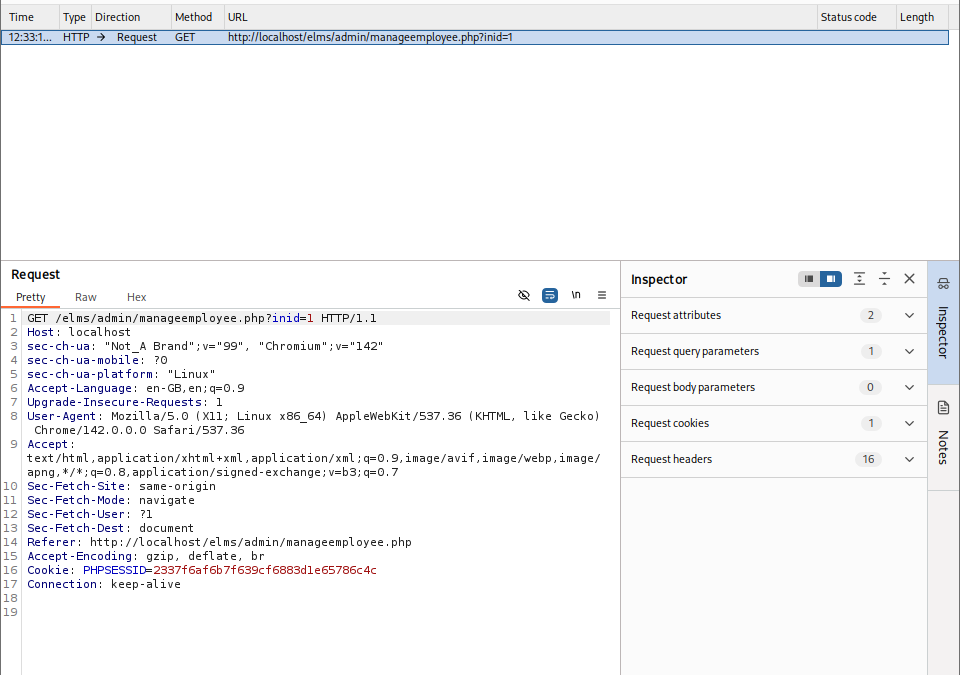 r-pradyun/cve-2025-67315
CSRF vulnerability PoC and remediation guide for employee deactivation in an admin panel. Includes CVSS scoring, attack reproduction steps, and…
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 ash1996x/cve-2025-50154-aggressor-script
Cobalt Strike Aggressor script that weaponizes LNK and Library-MS files to trigger SMB NTLMv2 hash disclosure, including CVE-2025-24054 bypass, for…
 rpgsec/roundcube-cve-2024-42008-poc
Proof-of-concept exploit for CVE-2024-42008, a Cross-Site Scripting vulnerability in RoundCube webmail. Delivers XSS payloads via contact forms to…
 mqkgithub/moniker-link-cve-2024-21413
Step-by-step walkthrough of exploiting CVE-2024-21413 in Microsoft Outlook to bypass Protected View and leak NTLM credentials via Moniker Links,…