

CVE-2024-1813-POC
 mobetasec/cve-2024-1813-poc
PoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
ctfeducationlabs-practice+4
mobetasec/cve-2024-1813-pocPoC exploit for CVE-2024-1813: PHP object injection in Simple Job Board WordPress plugin, achieving unauthenticated RCE via gadget chain. Includes…
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
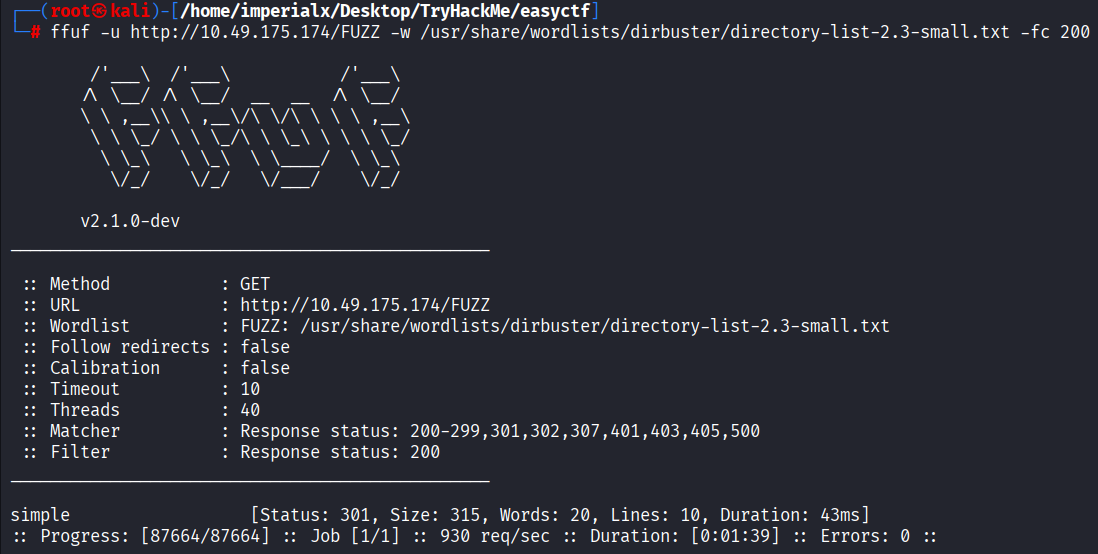 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 maradonam18/-cve-2025-59528-poc
A simple python script to exploit CVE-2025-59528, this an Authenticated RCE vulnerability in Flowise application, a popular AI tool. That is also…
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…
 ztrxwzy/joomla.3.7.0exploit
Proof of Concept exploit for the Joomla 3.7.0 com_fields SQL injection vulnerability (CVE-2017-8917), demonstrating detection, enumeration, and data…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 nxploited/cve-2025-4334
Simple User Registration <= 6.3 - Unauthenticated Privilege Escalation
 d1se0/cve-2024-10924-bypass-mfa-wordpress-lab
Lab environment and exploit script for CVE-2024-10924, demonstrating MFA bypass in WordPress via the Really Simple SSL plugin's skip_onboarding…
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 rishabh-kumar-cyber-sec/cve-2023-27163-ssrf-to-port-scanning
It is a simple script to automate internal port scanning dueto SSRF in requests-baskets v 1.2.1. this script can also assisst in solving 'SAU'…
 behindsecurity/htb-wifinetictwo-exploit
A simple python script to exploit CVE-2021-31630 on HTB WifineticTwo CTF
 cberman/cve-2023-2822-demo
Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.