

x64dbg
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
ai-assisted-reversingbinary-analysisbinary-exploitation+7
50.1k11h 49m ago
x64dbg/x64dbgAn open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty

 mytechnotalent/reverse-engineering
A FREE comprehensive reverse engineering tutorial covering x86, x64, 32-bit/64-bit ARM, 8-bit AVR and 32-bit RISC-V architectures.
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 planners1490/sclock
Hardware-Bound 256-Slot Polymorphic VM, Non-Linear MBA & Apple Secure Enclave Binary Protector for macOS arm64 (Apple Silicon) — Public CrackMe & SDK…
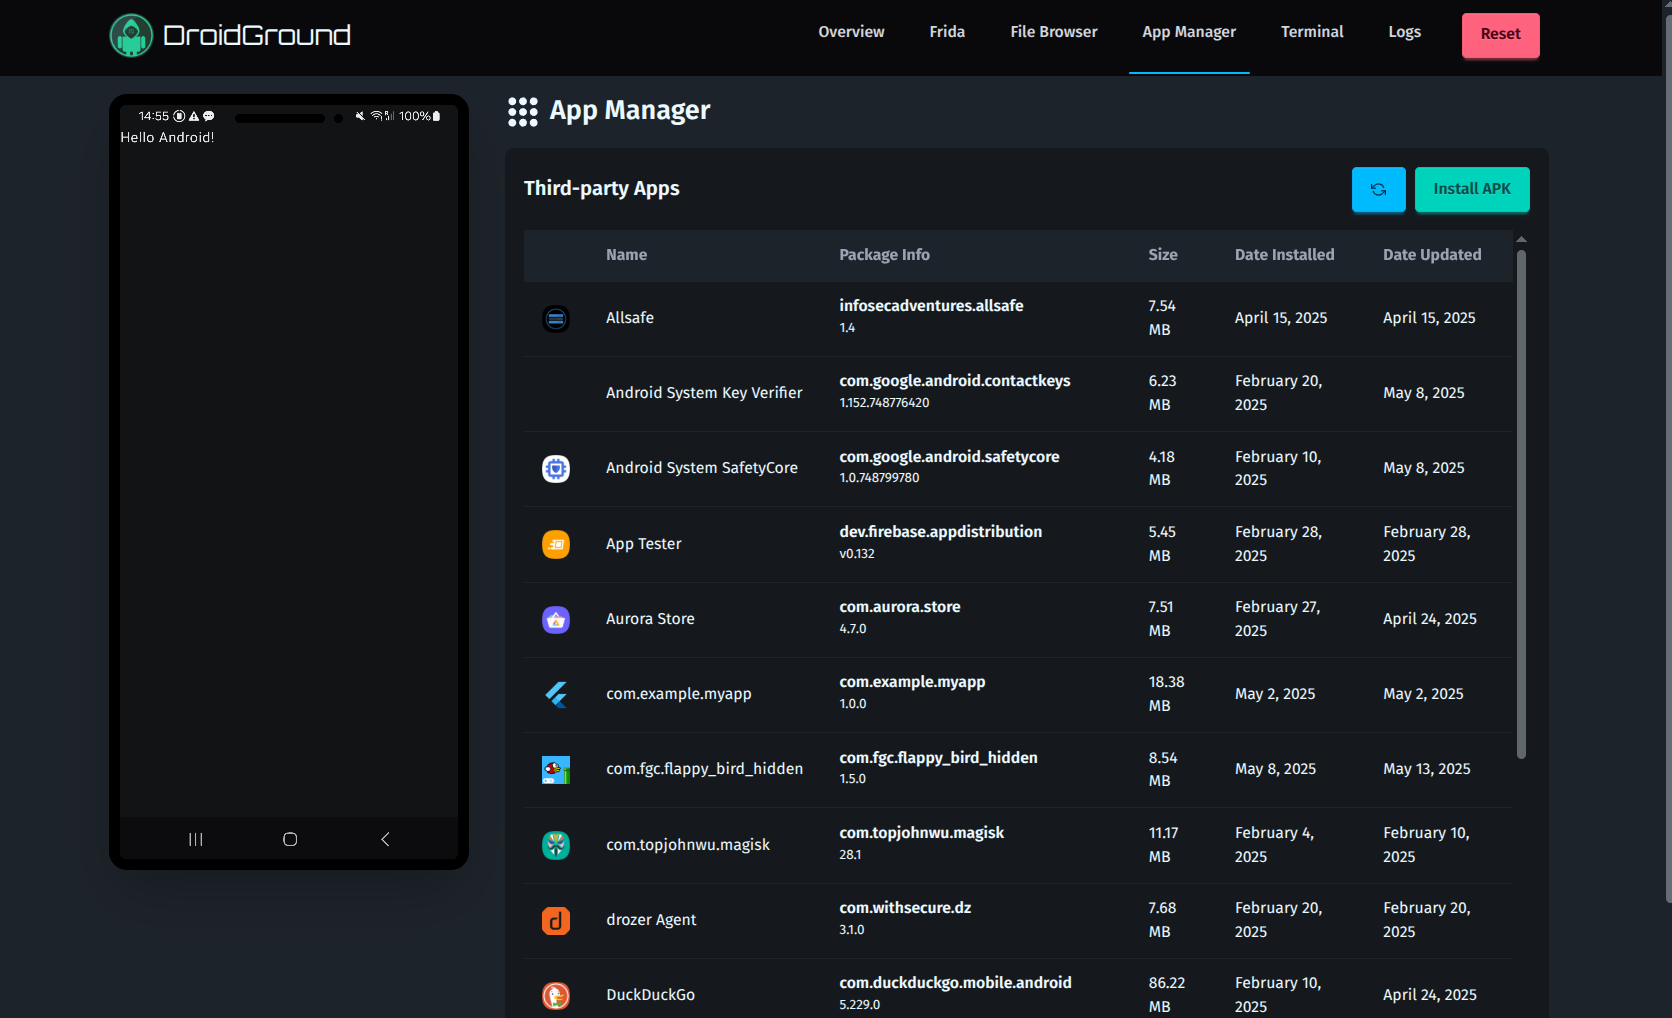 secforce/droidground
A flexible playground for Android CTF challenges.
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…

 ph4l4nx/ctf-s-tools
Repository to index useful tools for CTF's
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
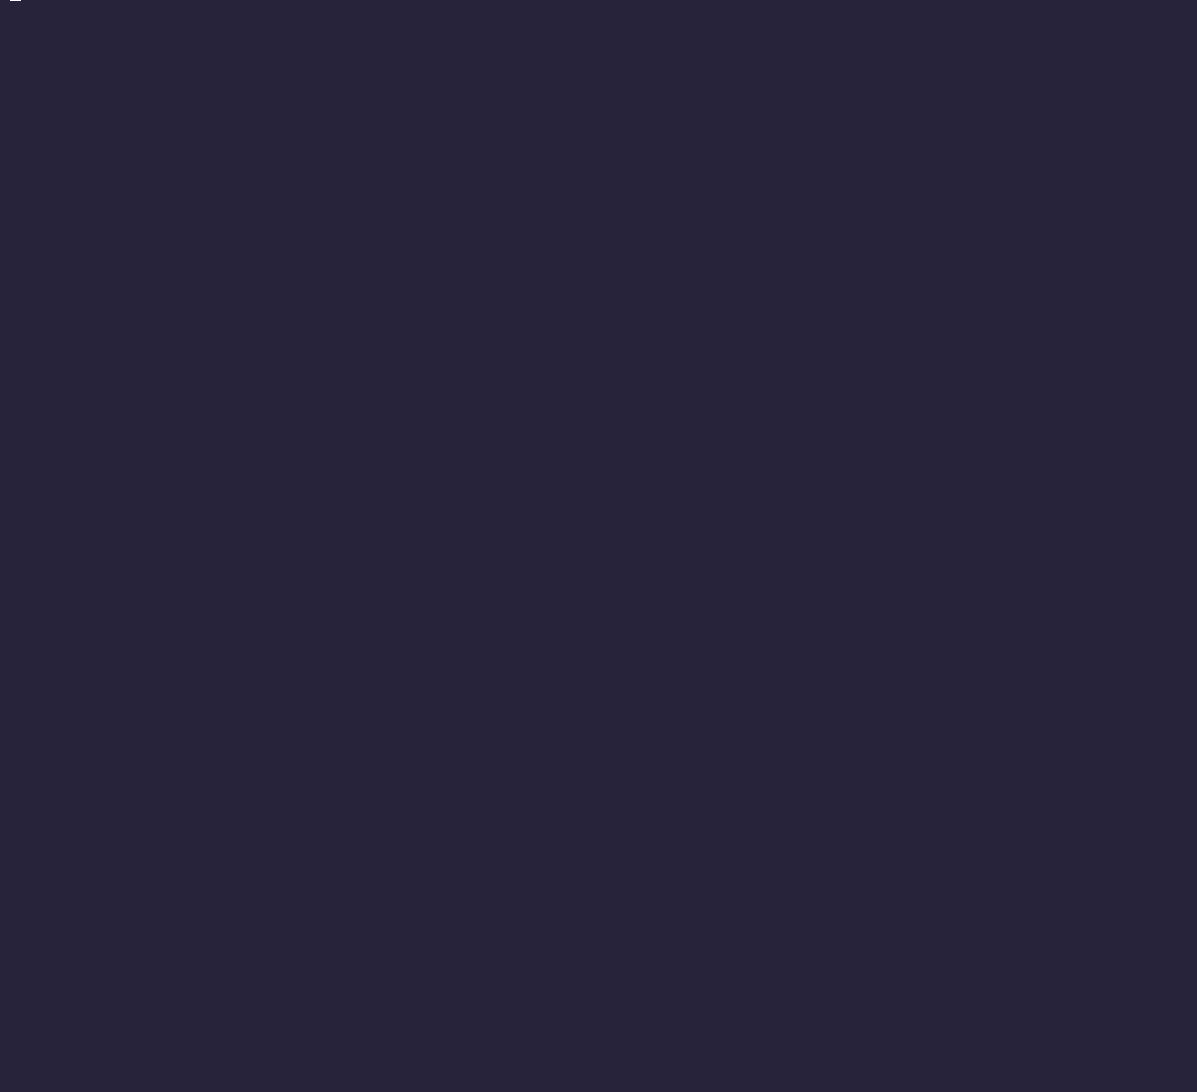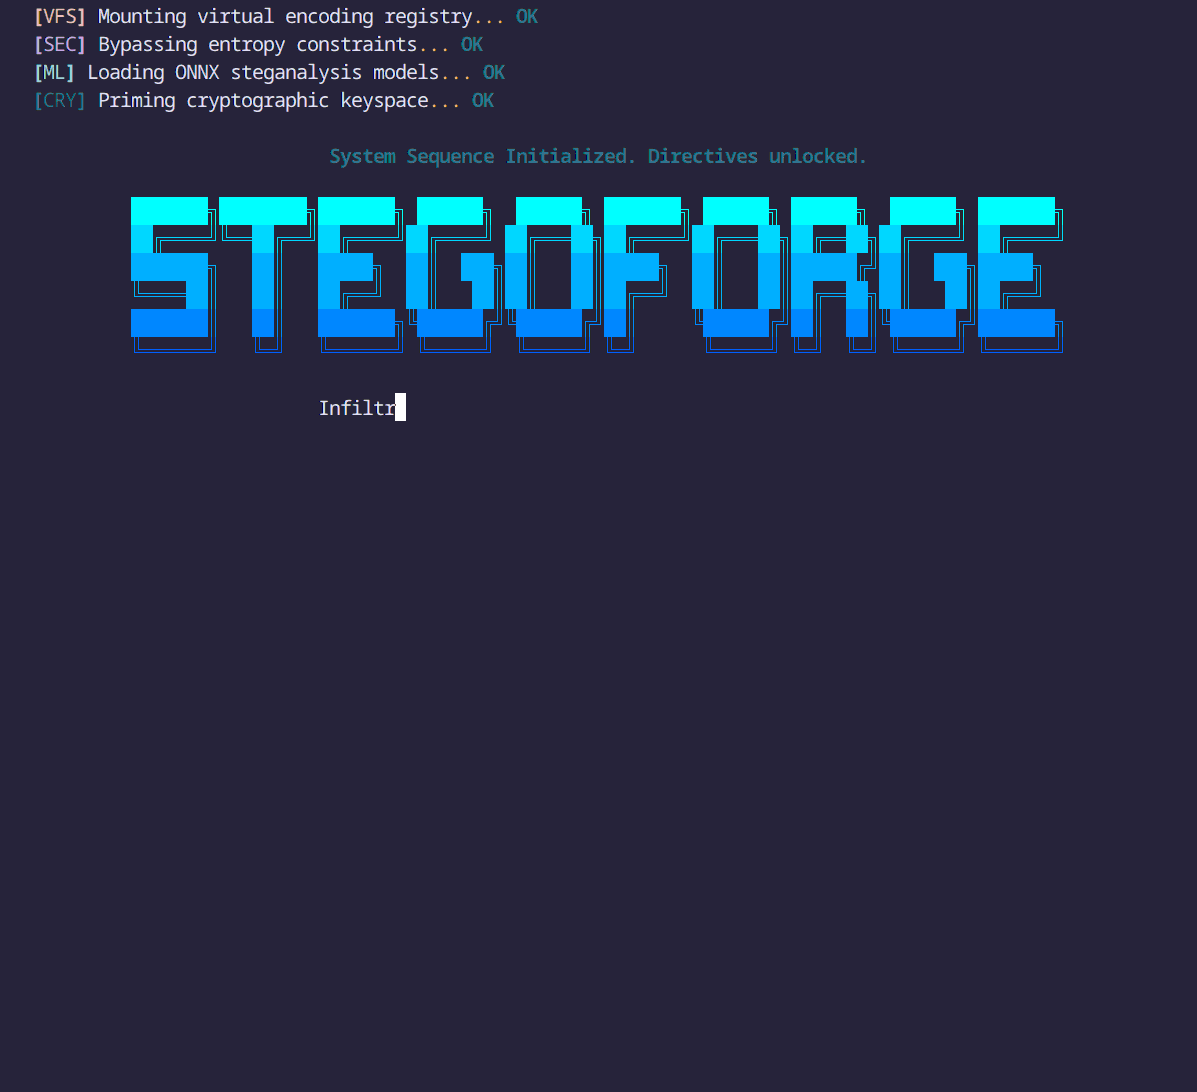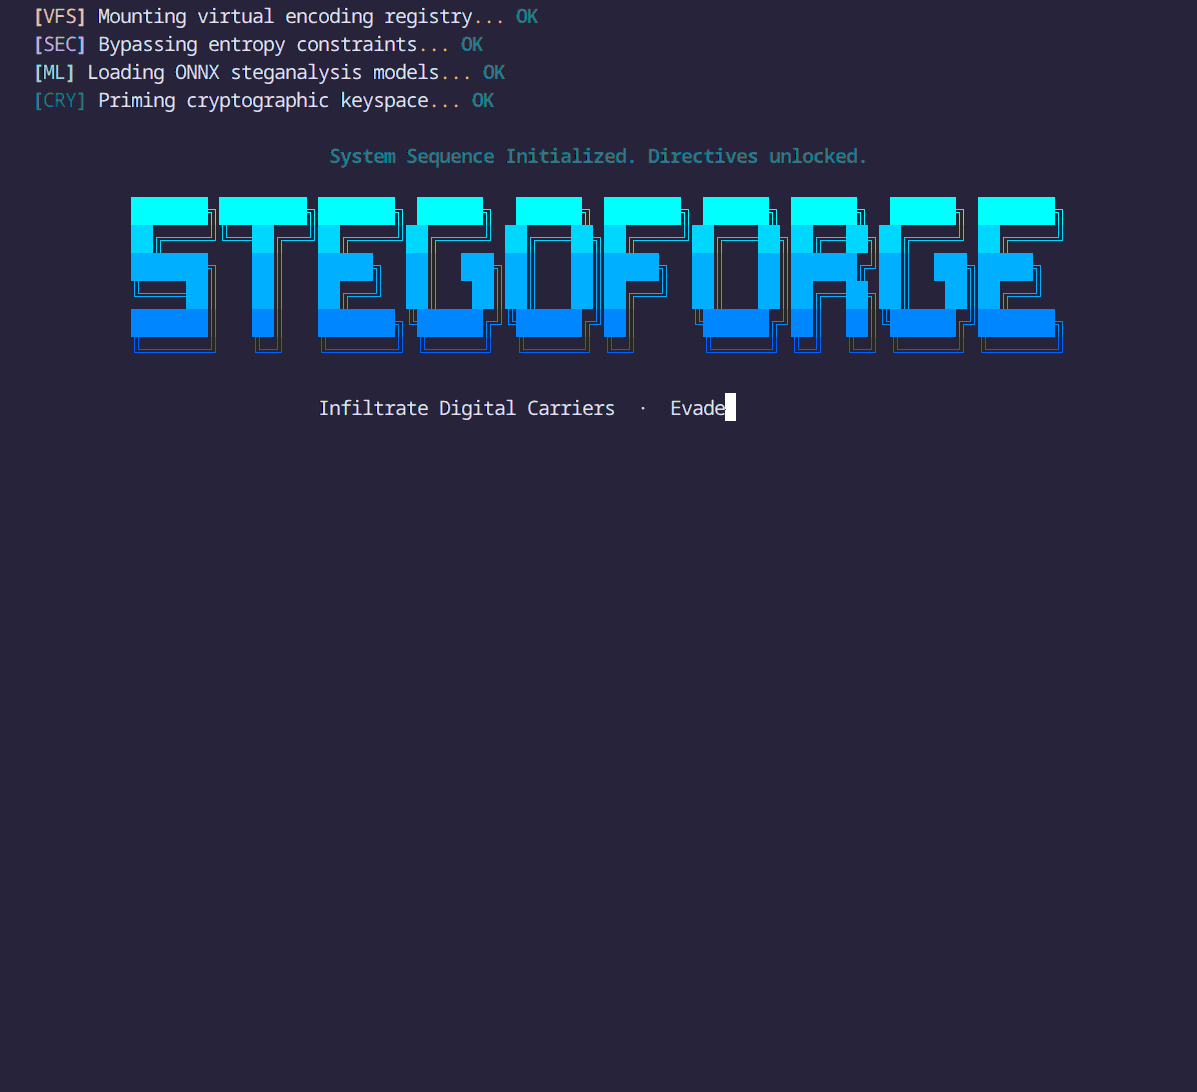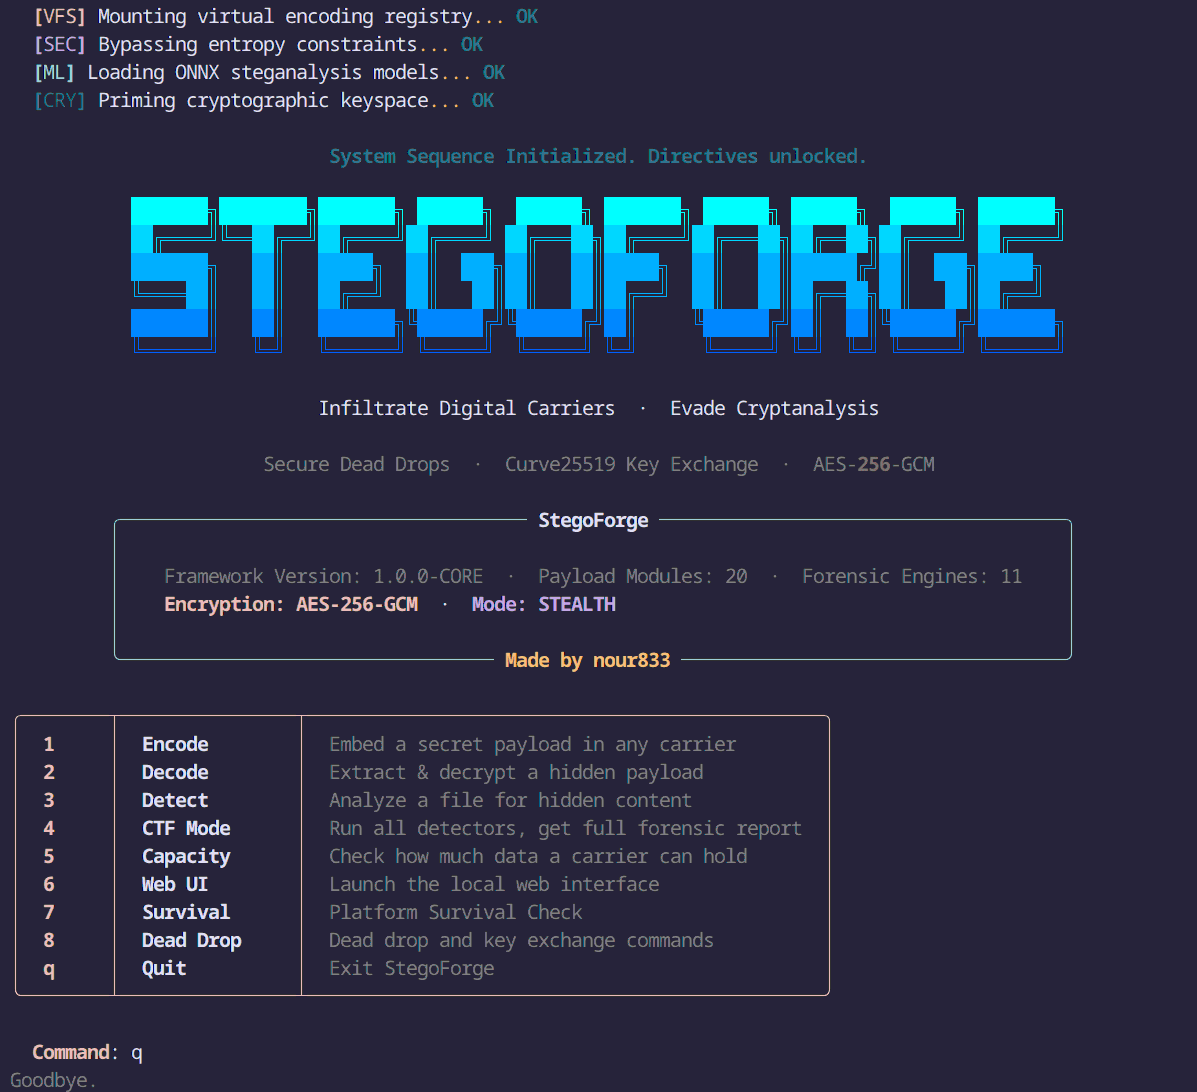 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…