
screenpipe
 screenpipe/screenpipe
YC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
ctfcurated-resourceseducation+8
screenpipe/screenpipeYC (S26) | Open Computer History | Continuously record your company computer work, map your workflows, help you find work worth automating, and power…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 angr/angr
A powerful and user-friendly binary analysis platform!
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
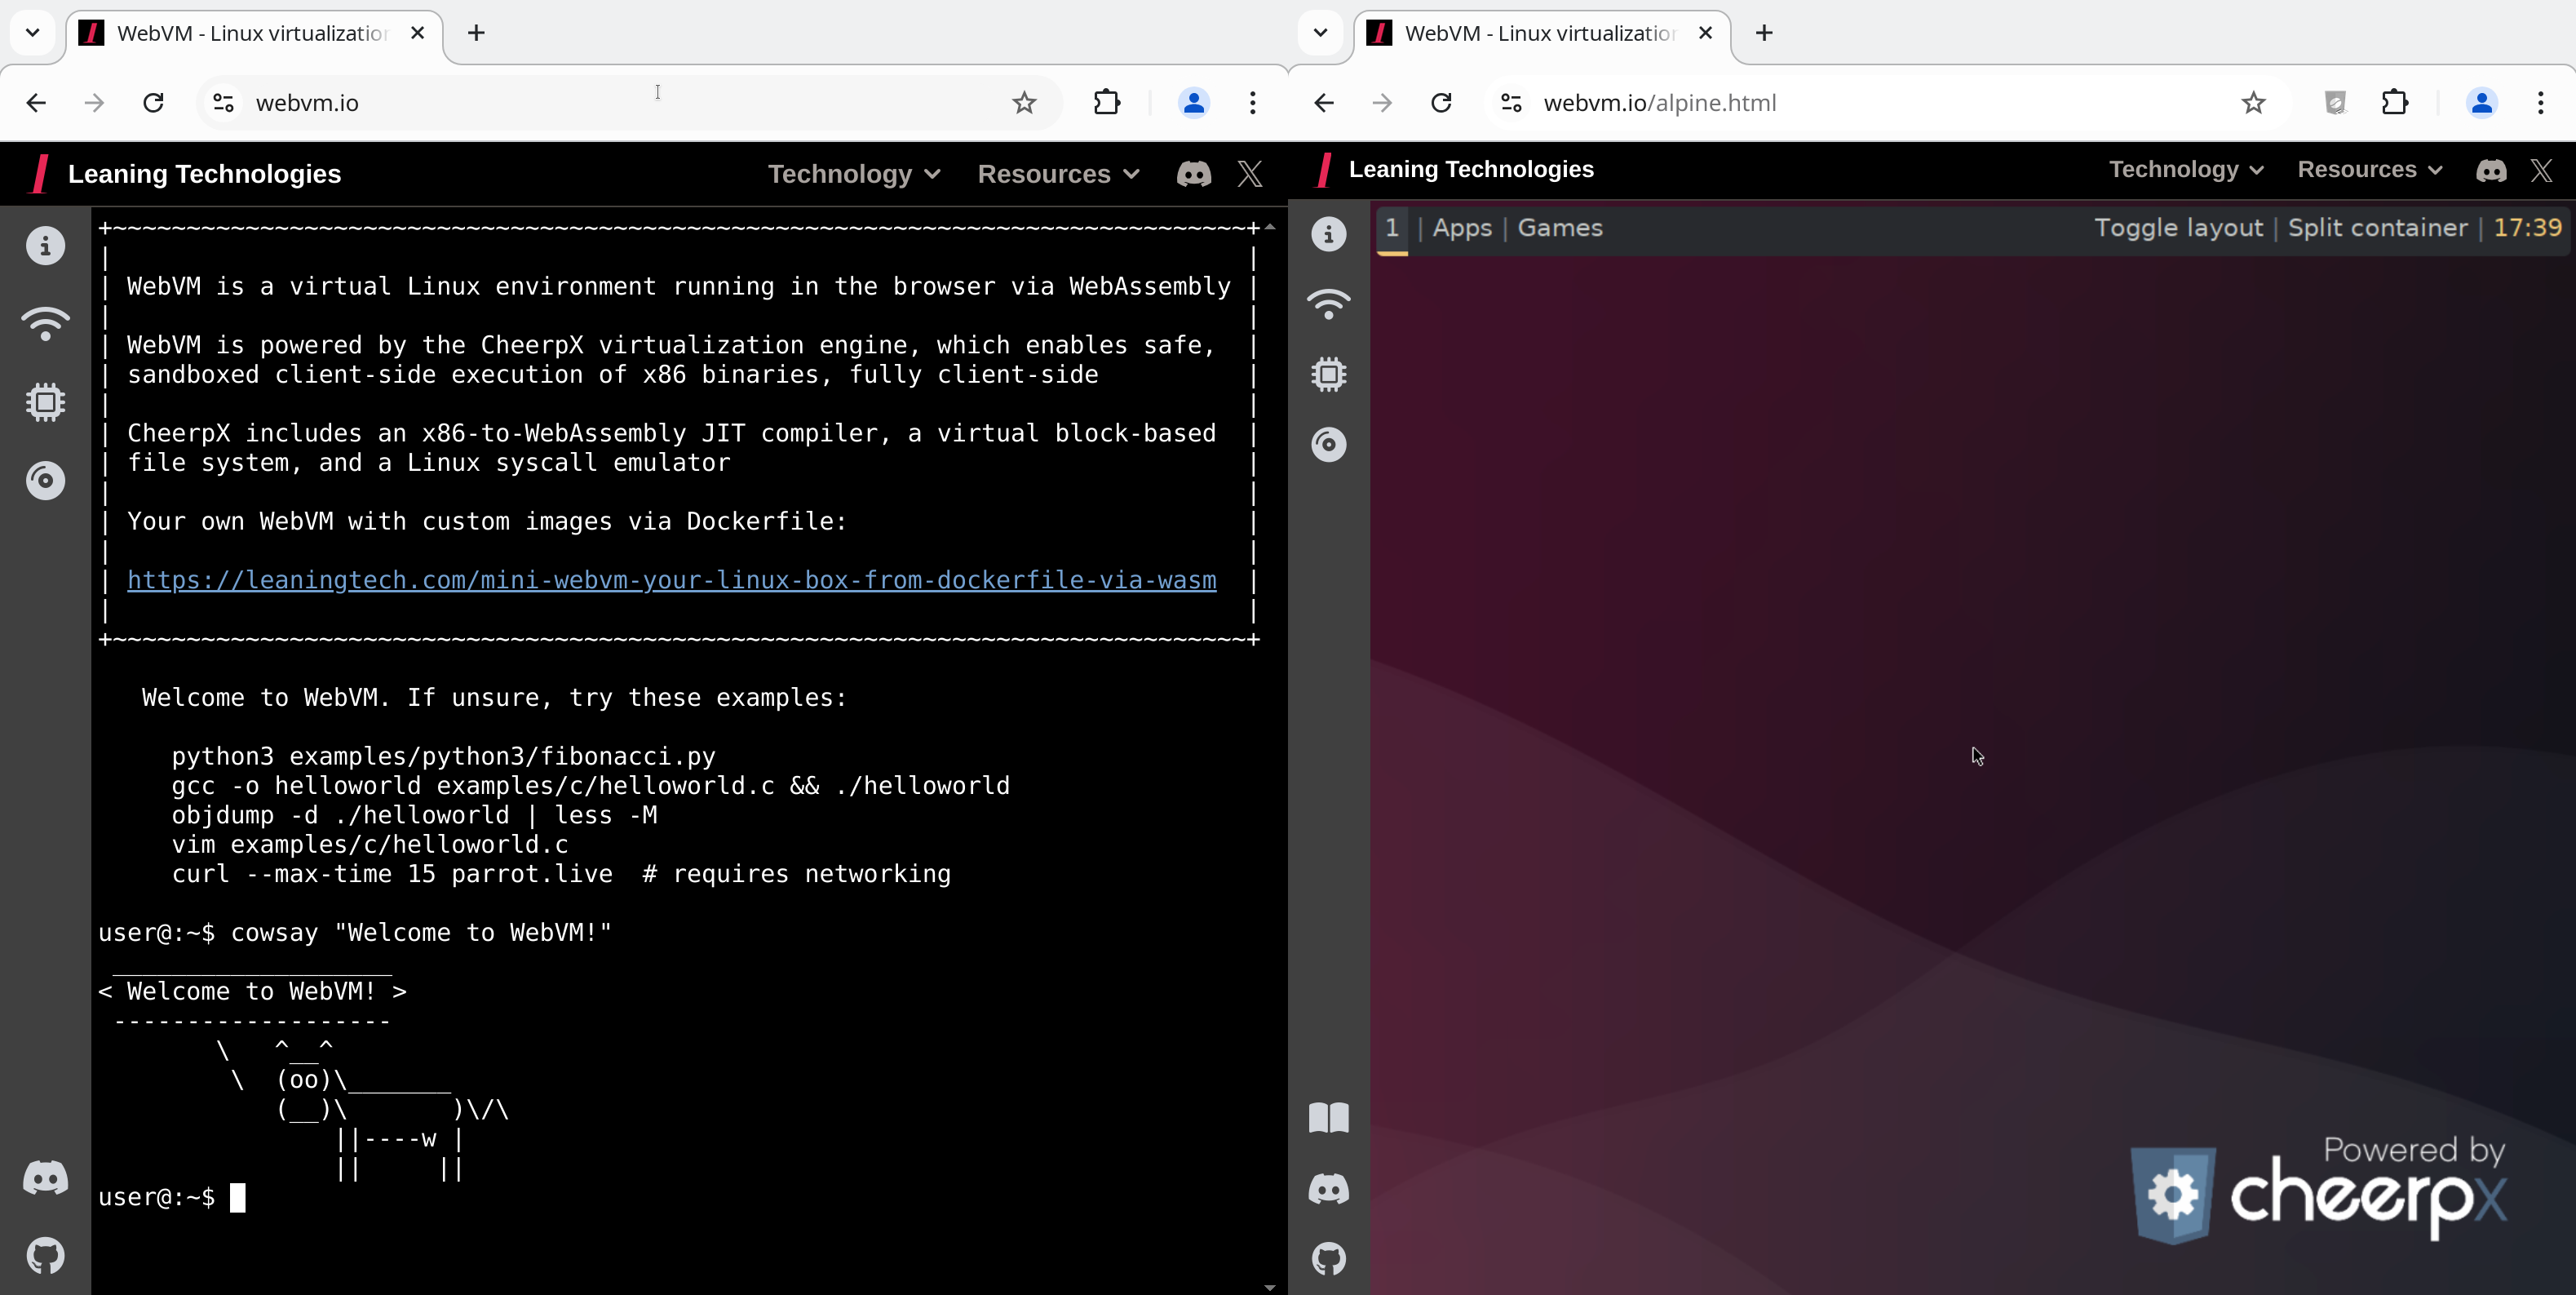 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 sparkyniner/netryx-astra-v2-geolocation-tool
The world's most sophisticated street level image geolocation software
 hack-with-github/awesome-hacking
A collection of various awesome lists for hackers, pentesters and security researchers
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.