
oss-oopssec-store
 koadt/oss-oopssec-store
Security training for the apps you actually ship. Open your browser and start hacking.
ai-securityctfeducation+7
343h 3m ago
koadt/oss-oopssec-storeSecurity training for the apps you actually ship. Open your browser and start hacking.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
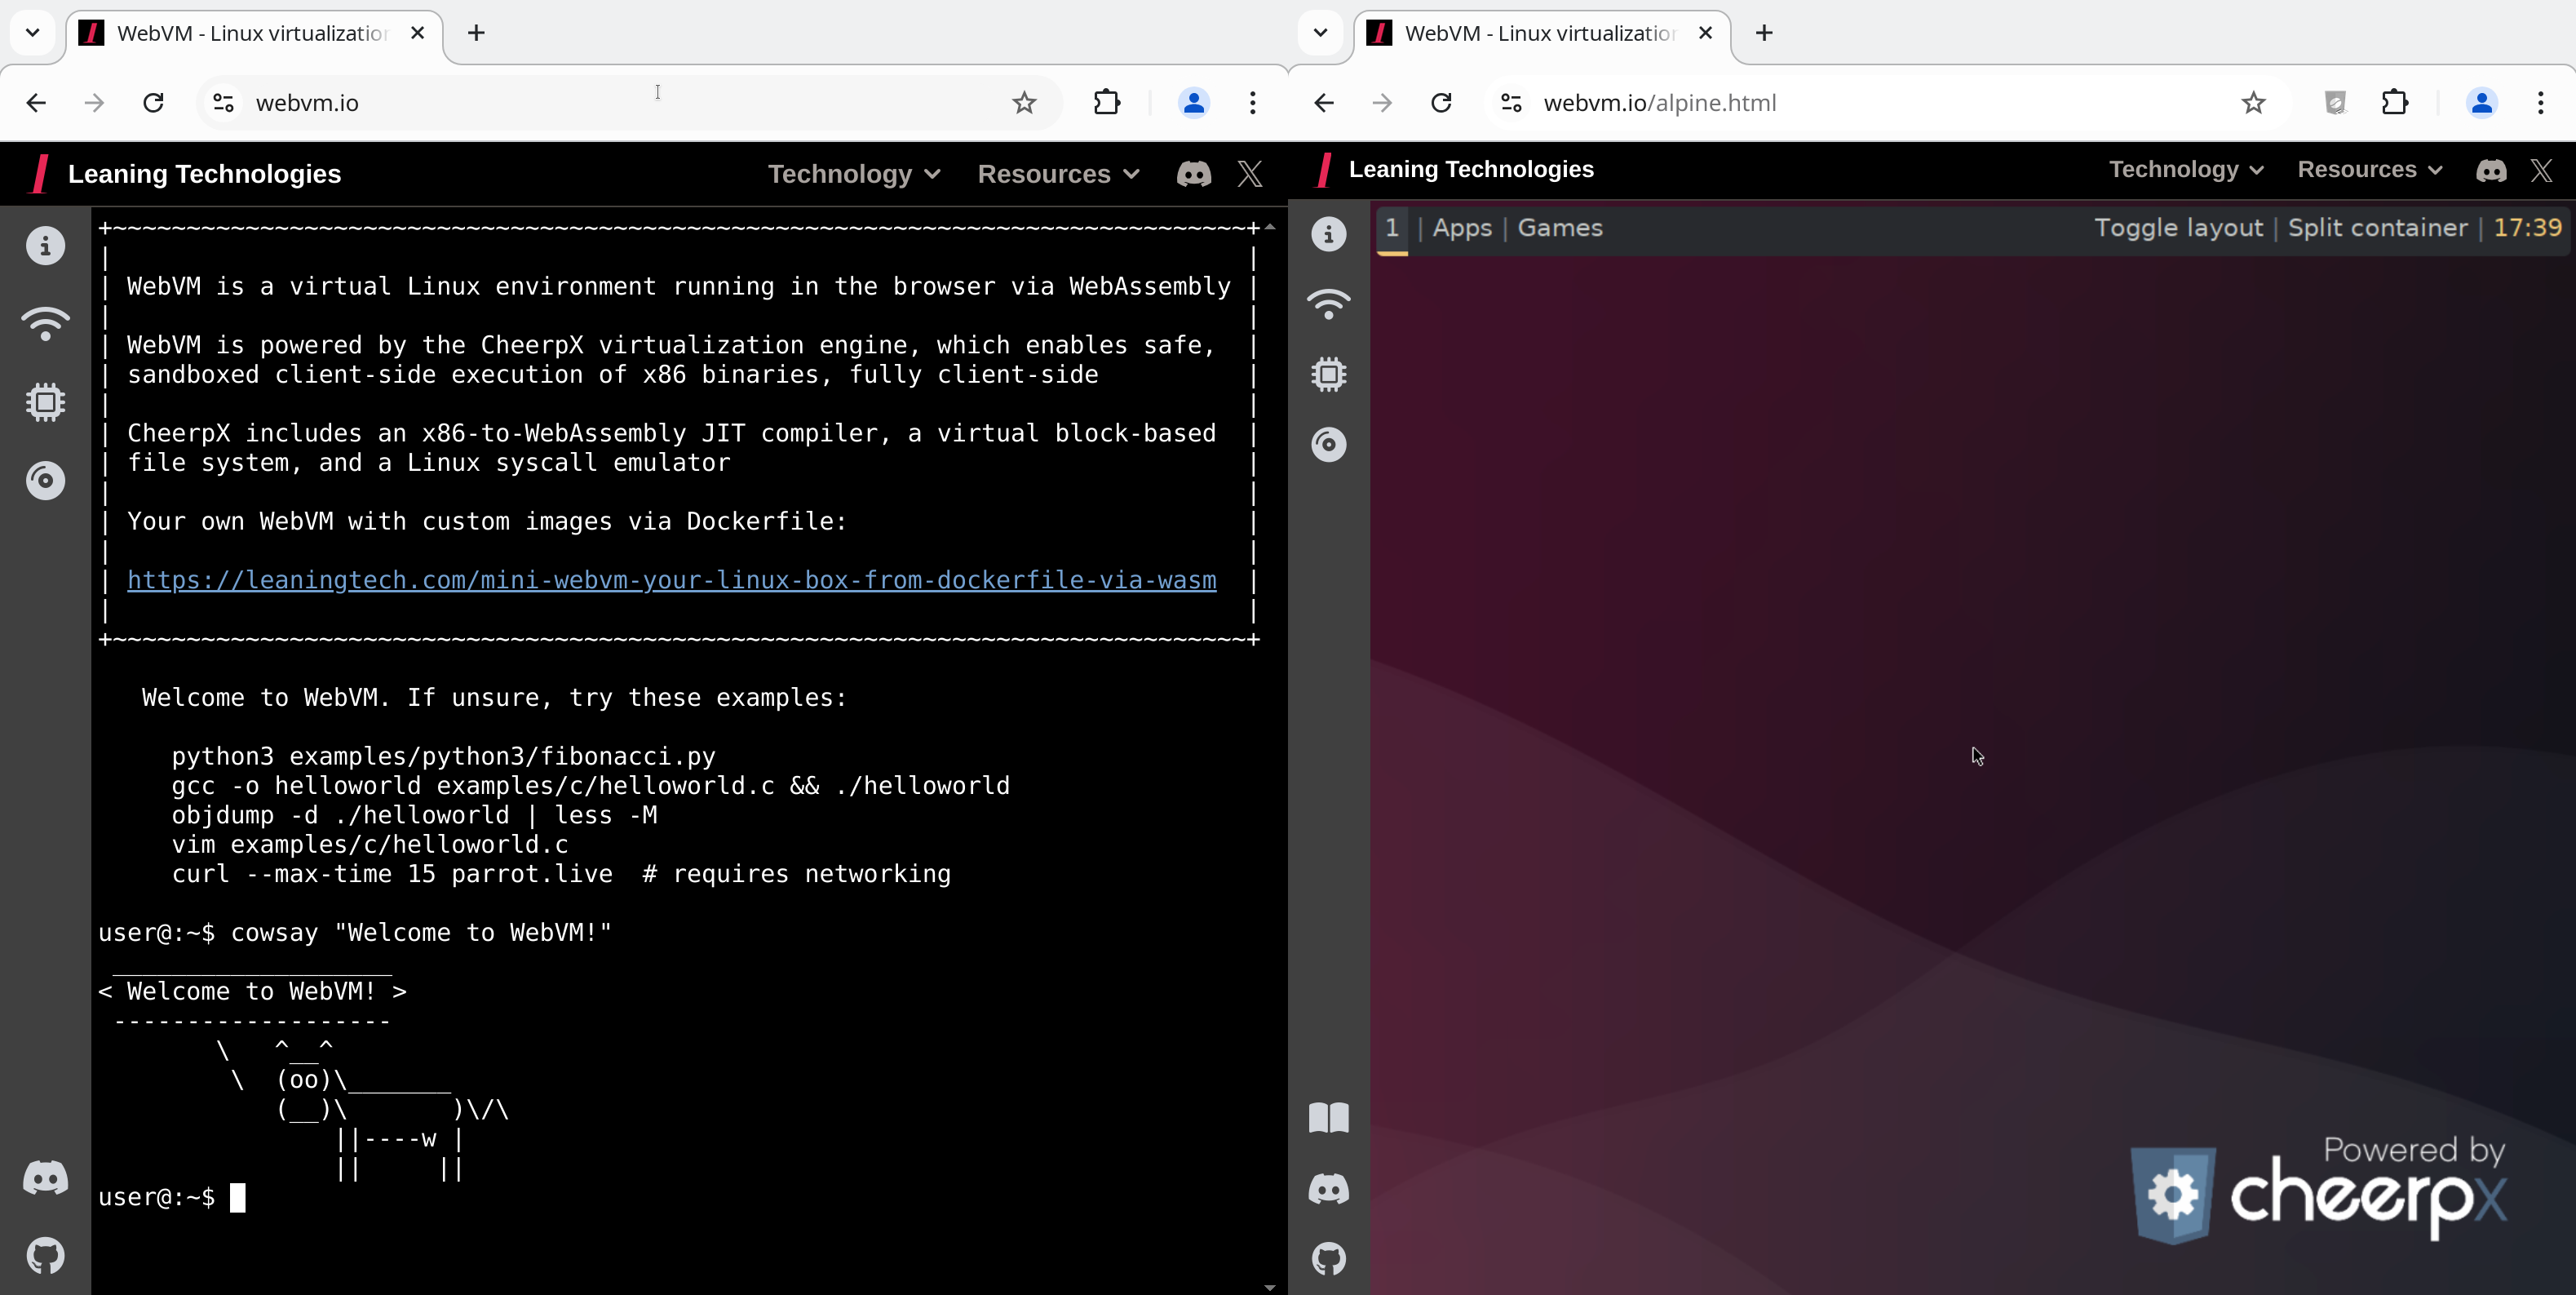 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
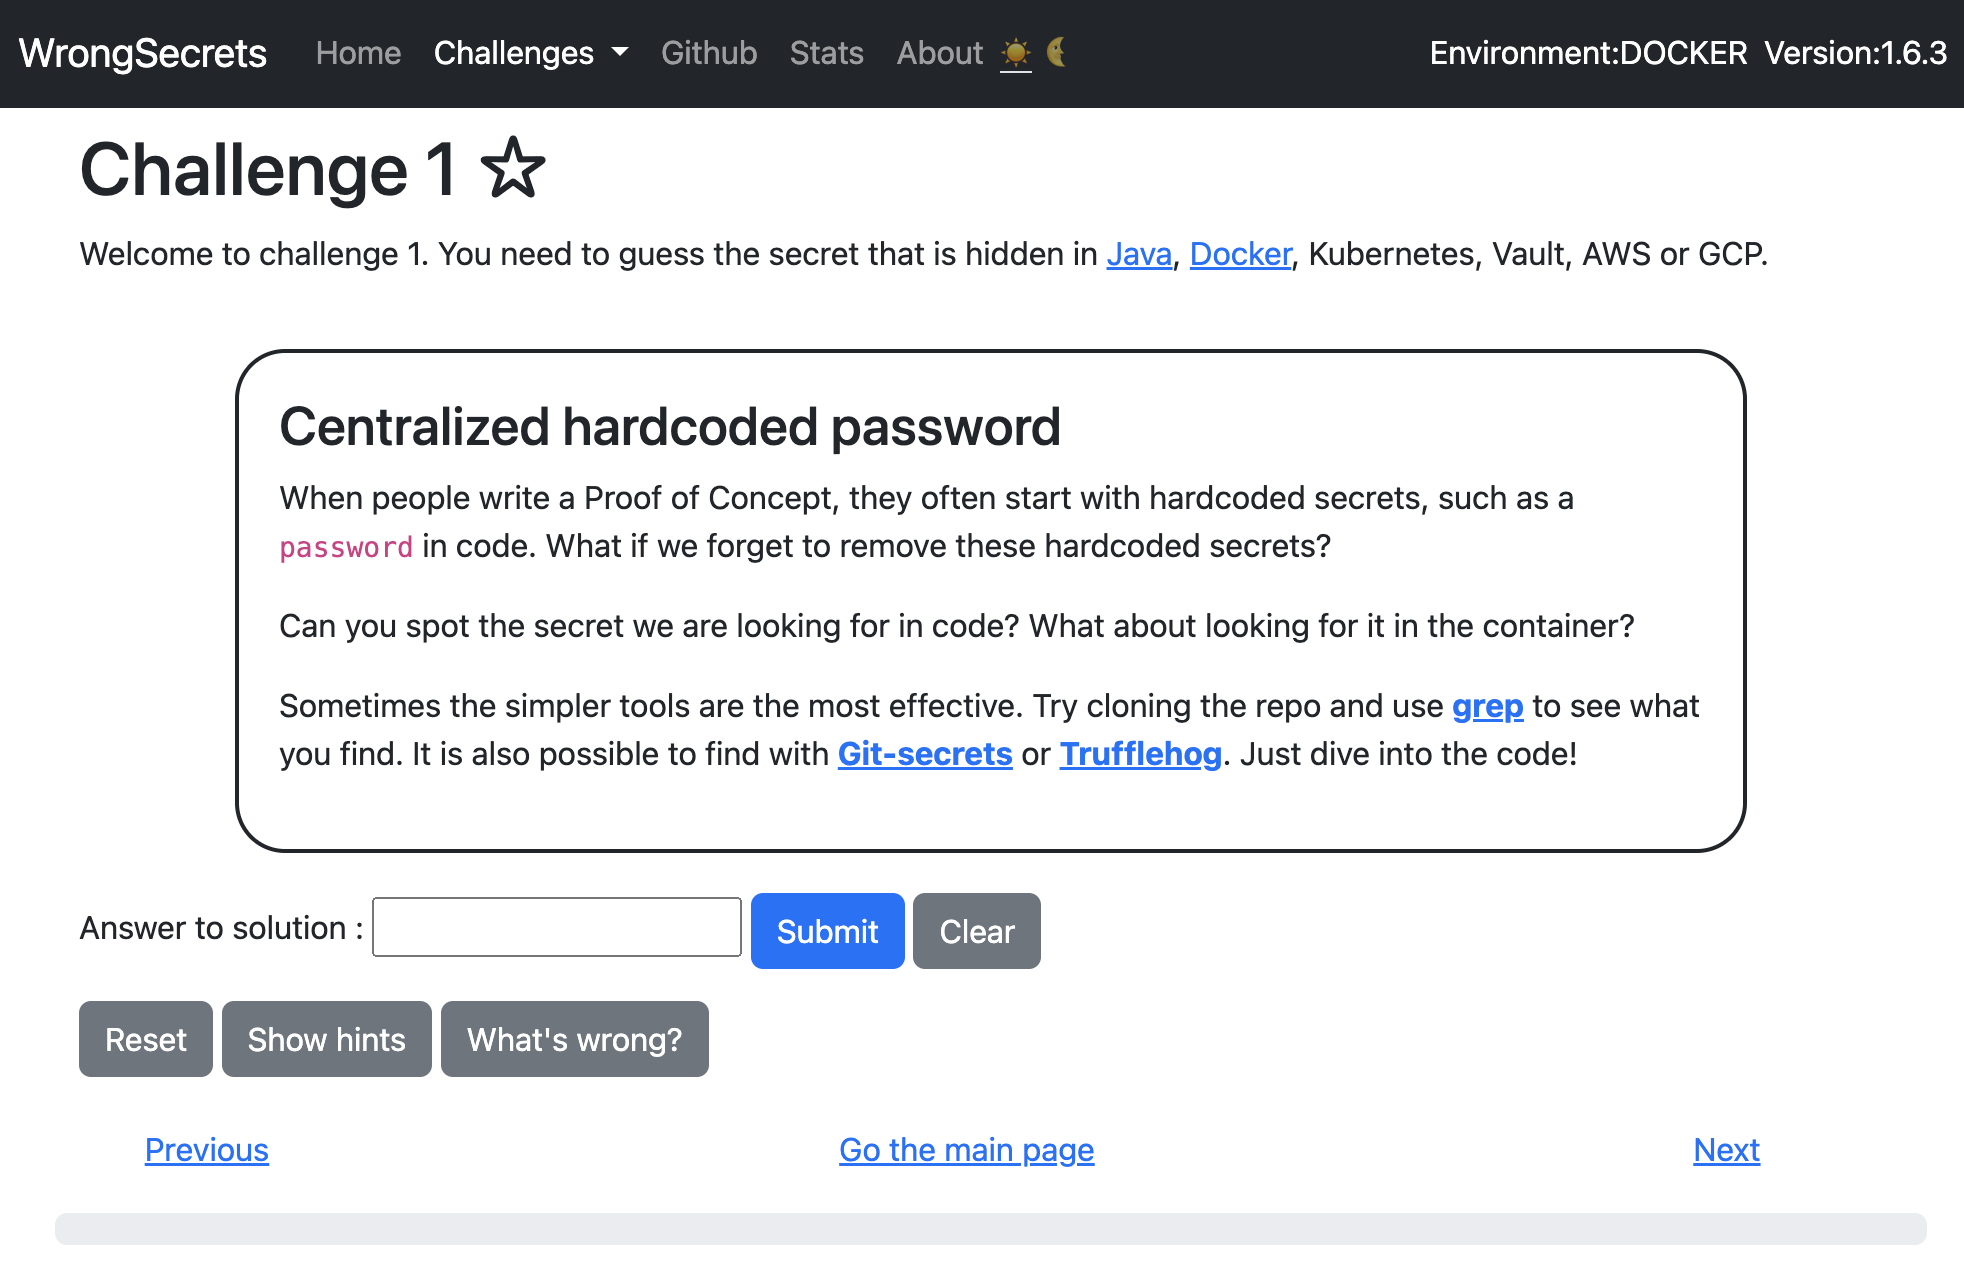 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 tencent/ai-infra-guard
A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.
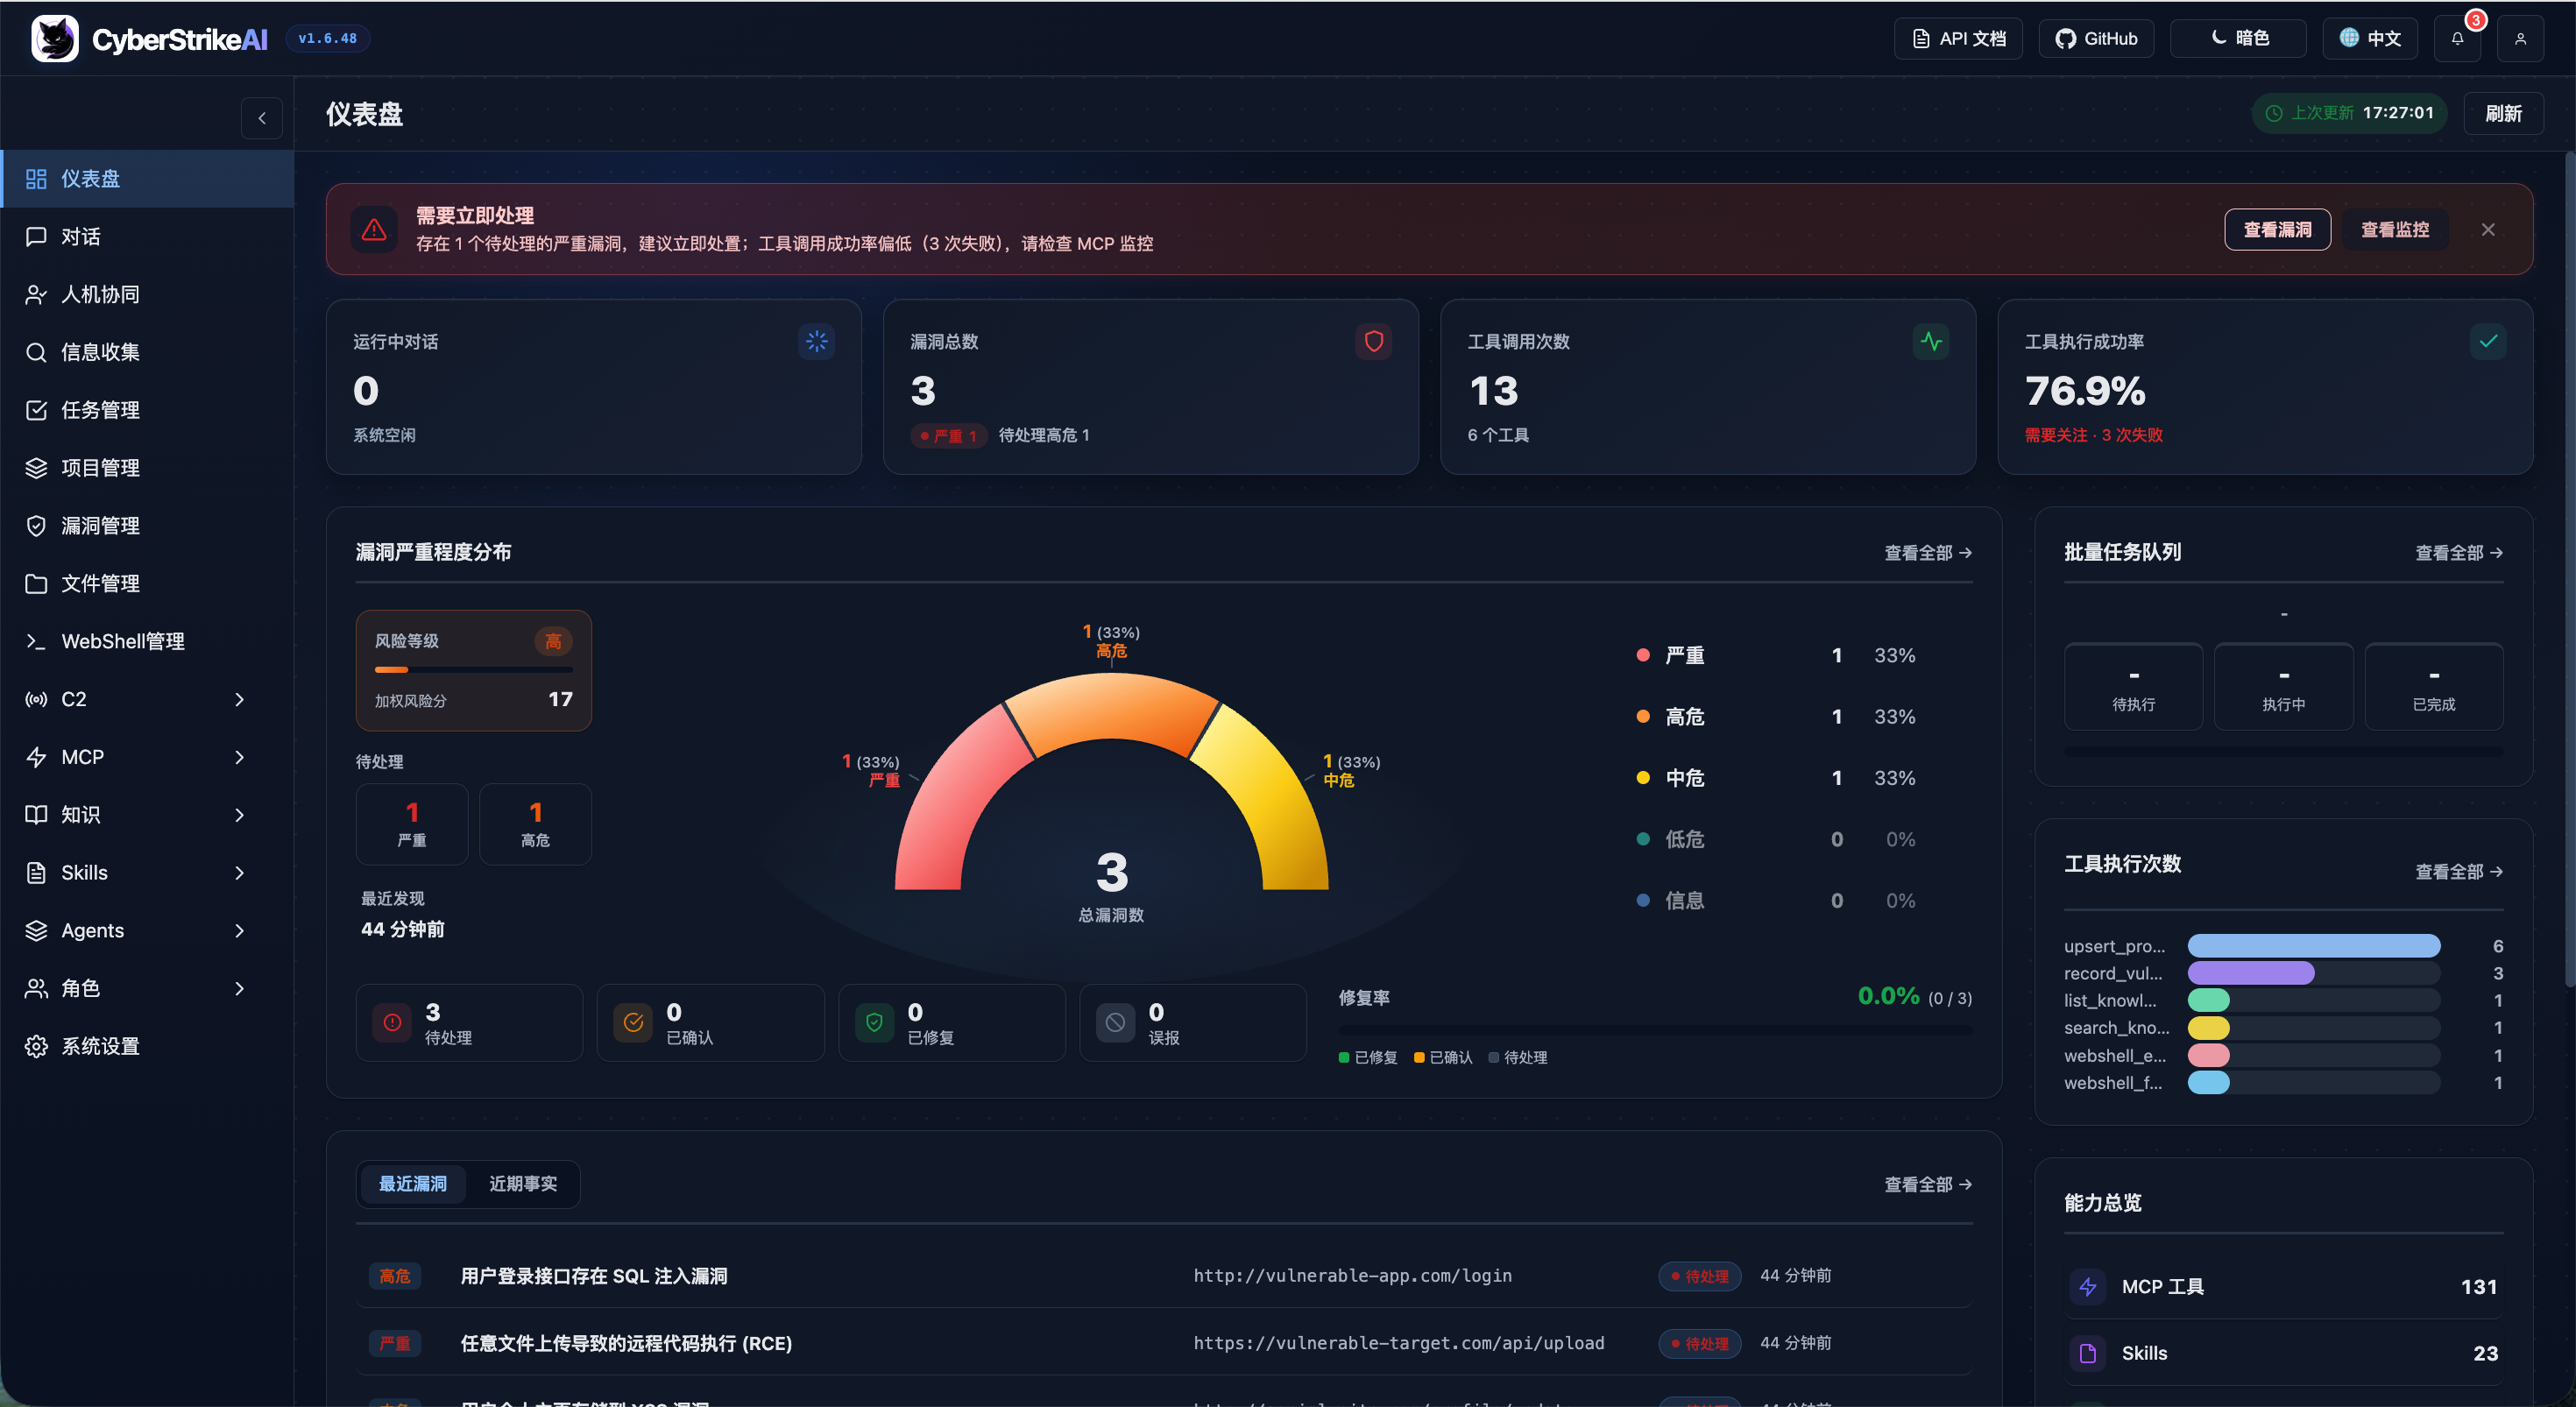 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

 owasp/securityshepherd
Web and mobile application security training platform
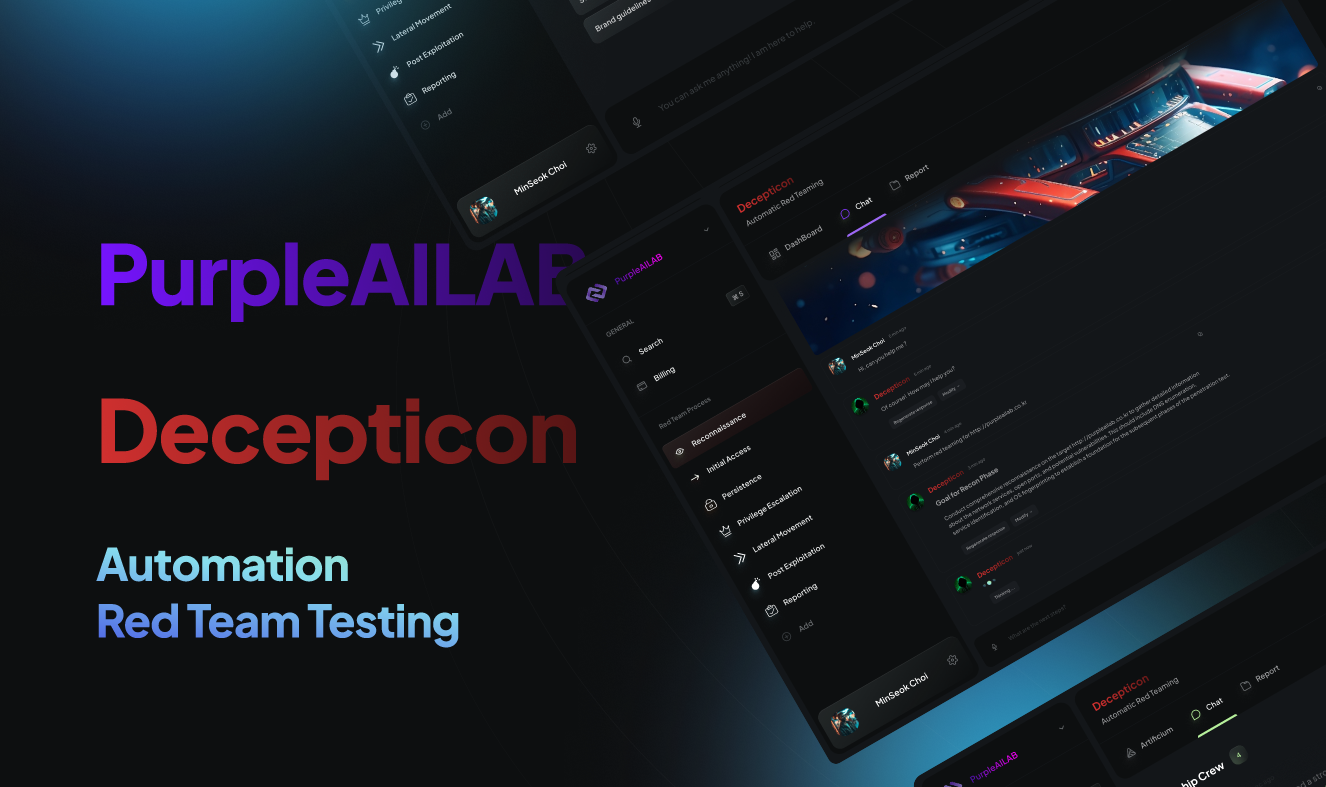 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
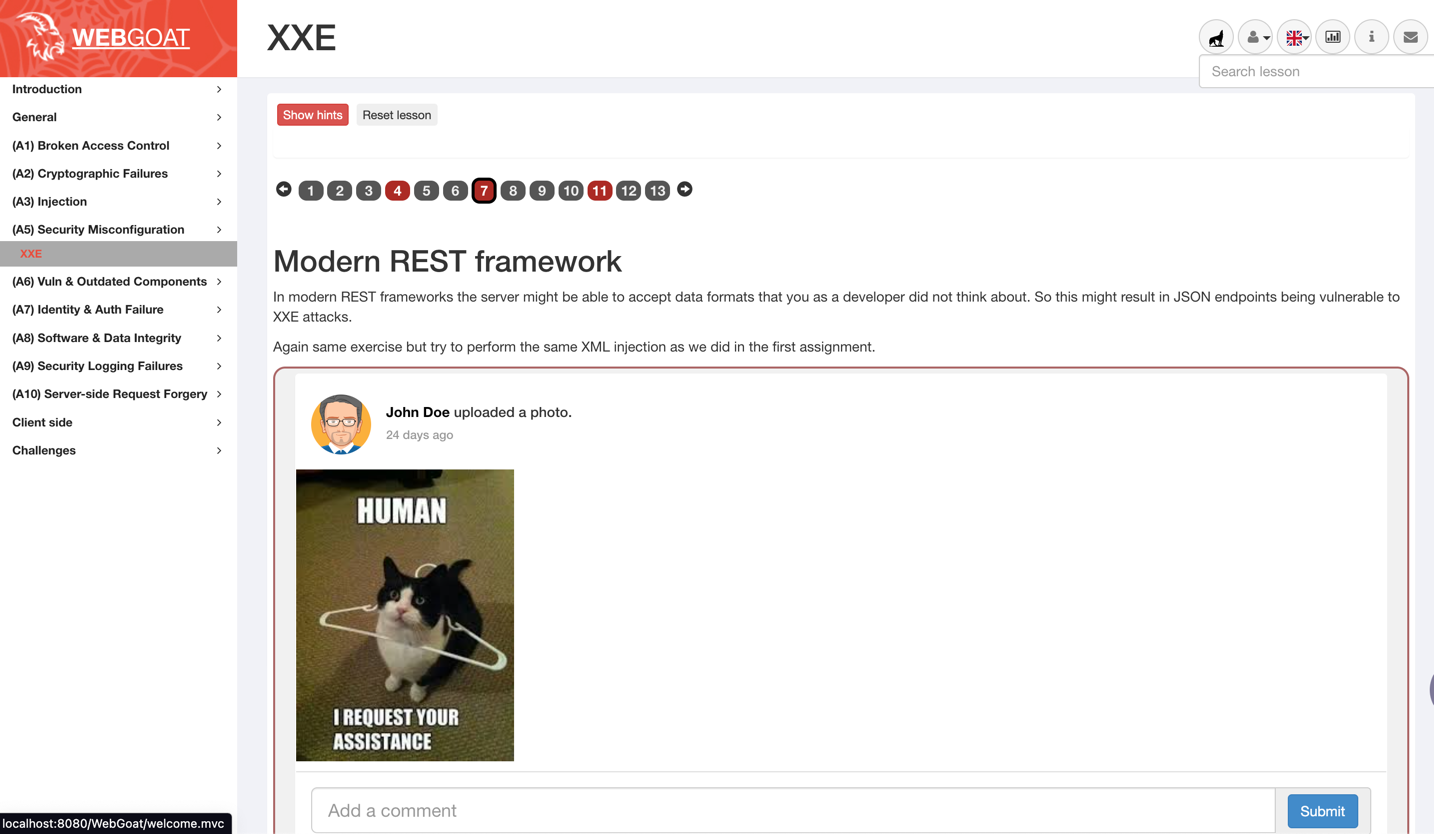 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
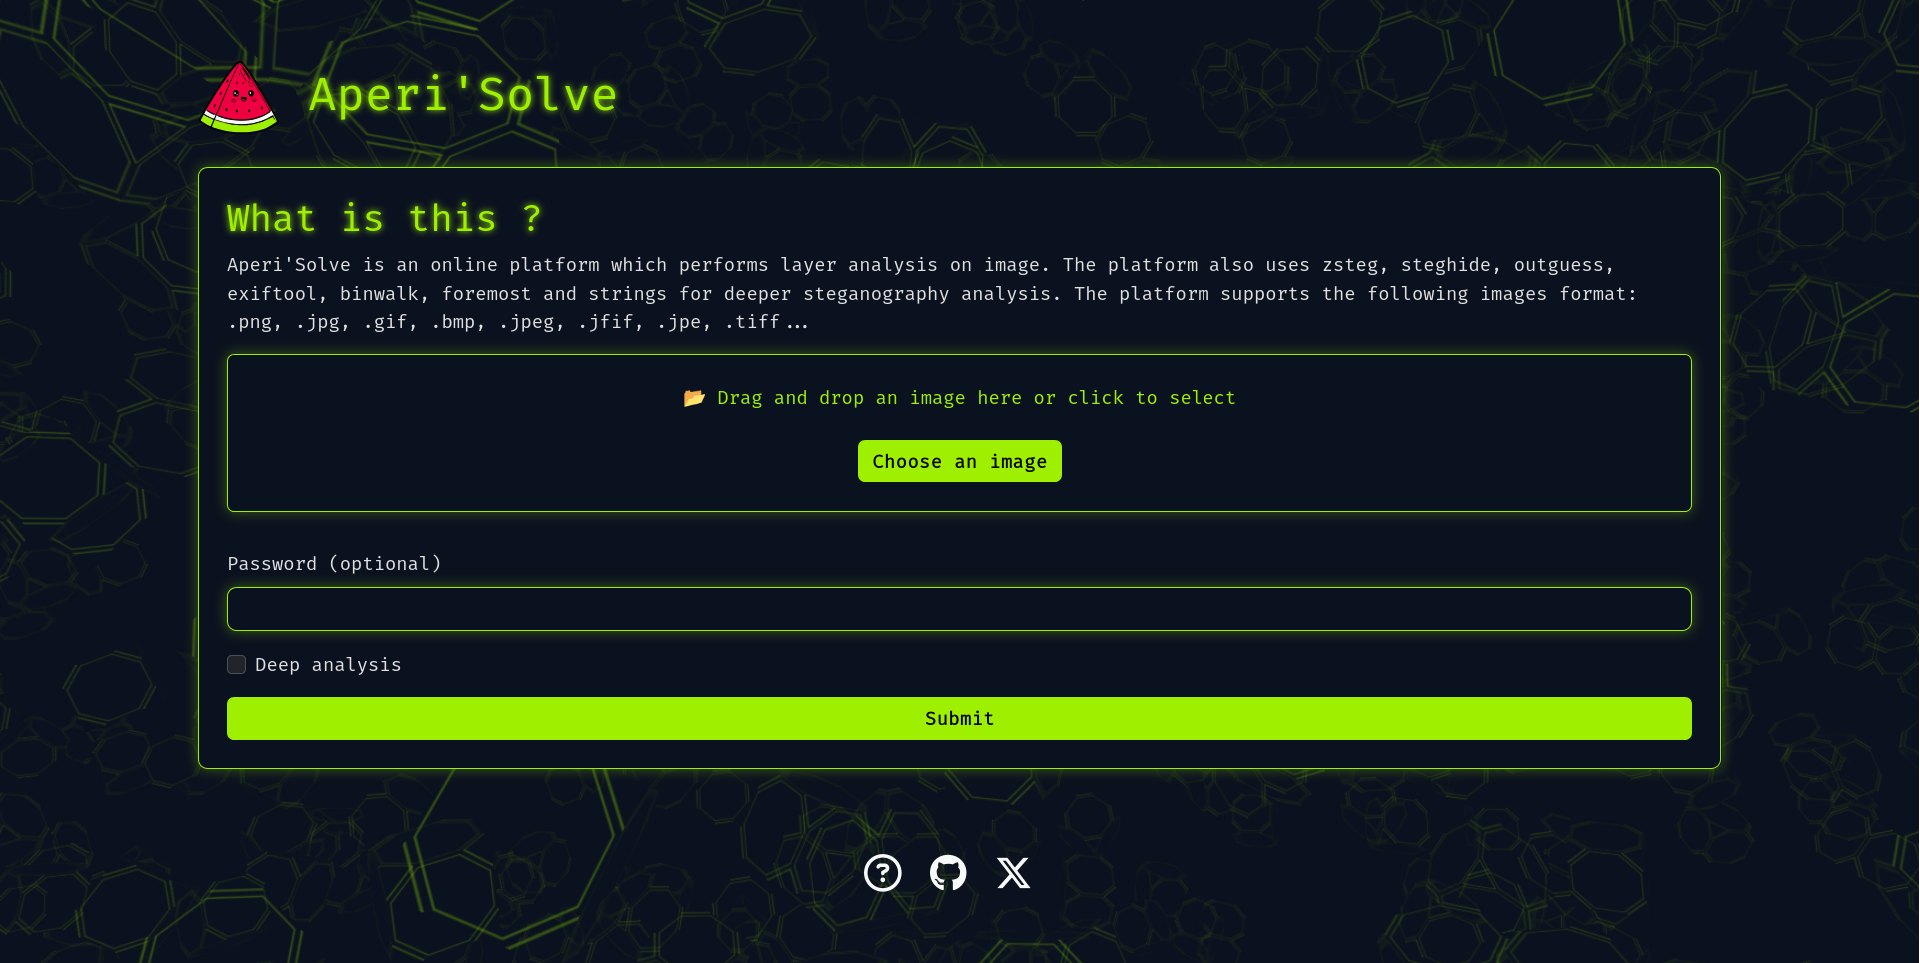 zeecka/aperisolve
Automated steganalysis platform that detects hidden data in images using 16 parallel analyzers, bit-layer visualization, and an in-app wiki for CTF…
 rdelasierra-uy/portfolio
Vitrina profesional: writeups de Hack The Box, informes, casos de estudio GRC (ISO 27001/27002/27005/27035, ISO 31000 + MAGERIT), scripts de…