
CVE-2026-38526
 mrdark-ops/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
ctfexploitationpayload-development+5
mrdark-ops/cve-2026-38526Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticates, uploads a PHP webshell via /admin/tinymce/upload, and executes commands…
 harry178945/cve-2026-38526
Python PoC exploiting CVE-2026-38526 in Krayin CRM <= 2.2.x: authenticated PHP webshell upload via /admin/tinymce/upload leading to remote code…
 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 noraj/ctf-party
:triangular_flag_on_post: A CLI tool & library to enhance and speed up script/exploit writing with string conversion/manipulation.
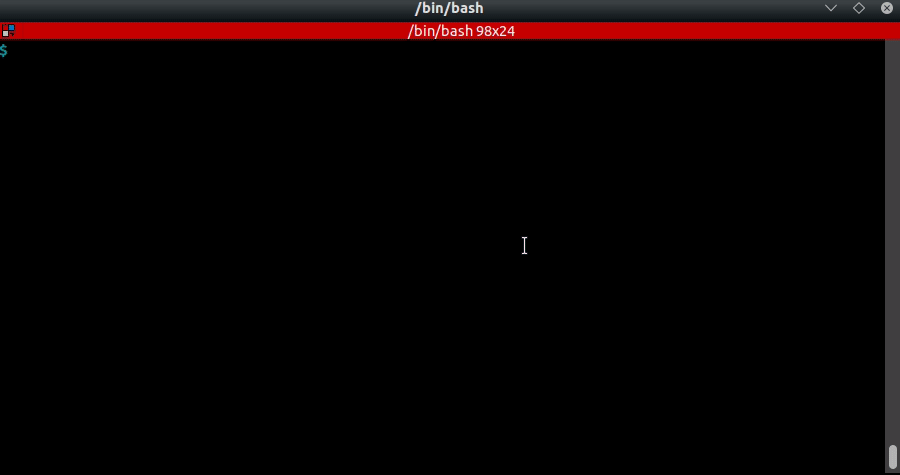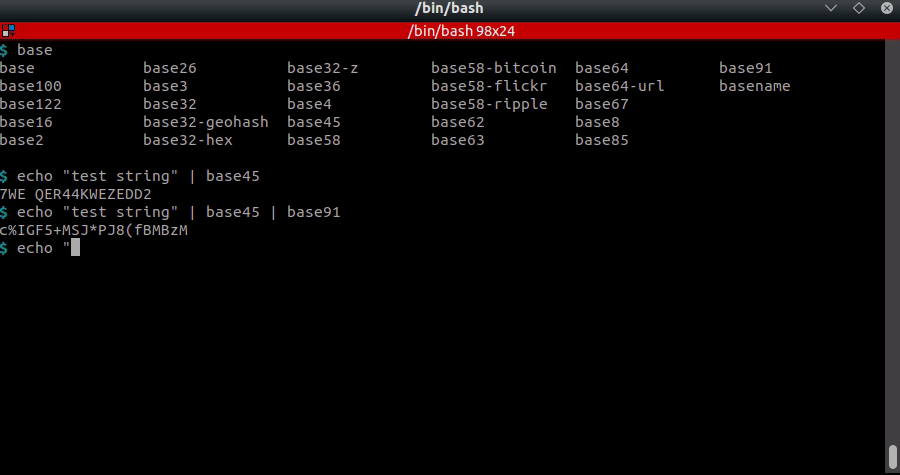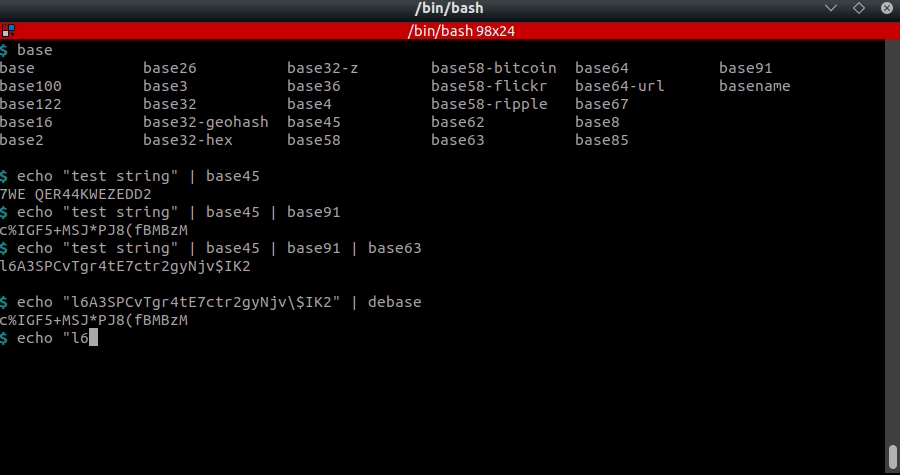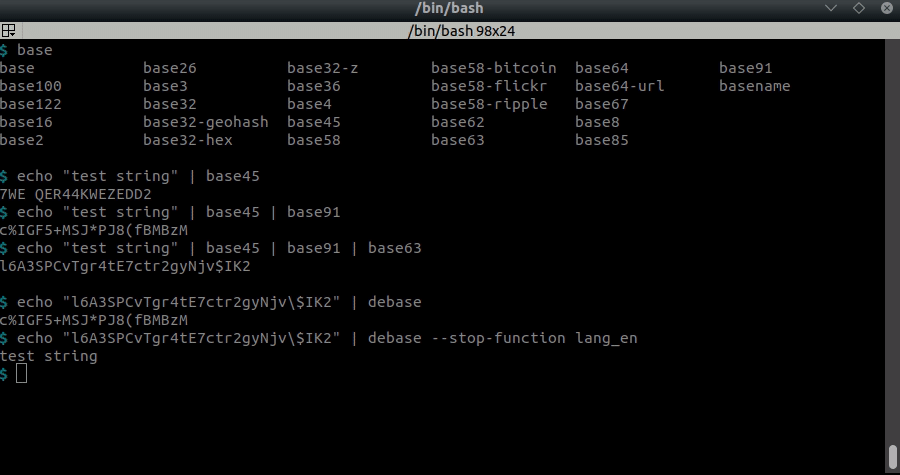 dhondta/python-codext
Python codecs extension featuring CLI tools for encoding/decoding anything
 fabse-hack/cve-2024-3829
Python exploit for CVE-2024-3829 targeting Qdrant snapshot import/export, enabling file read, file write, and reverse shell execution via symlink…
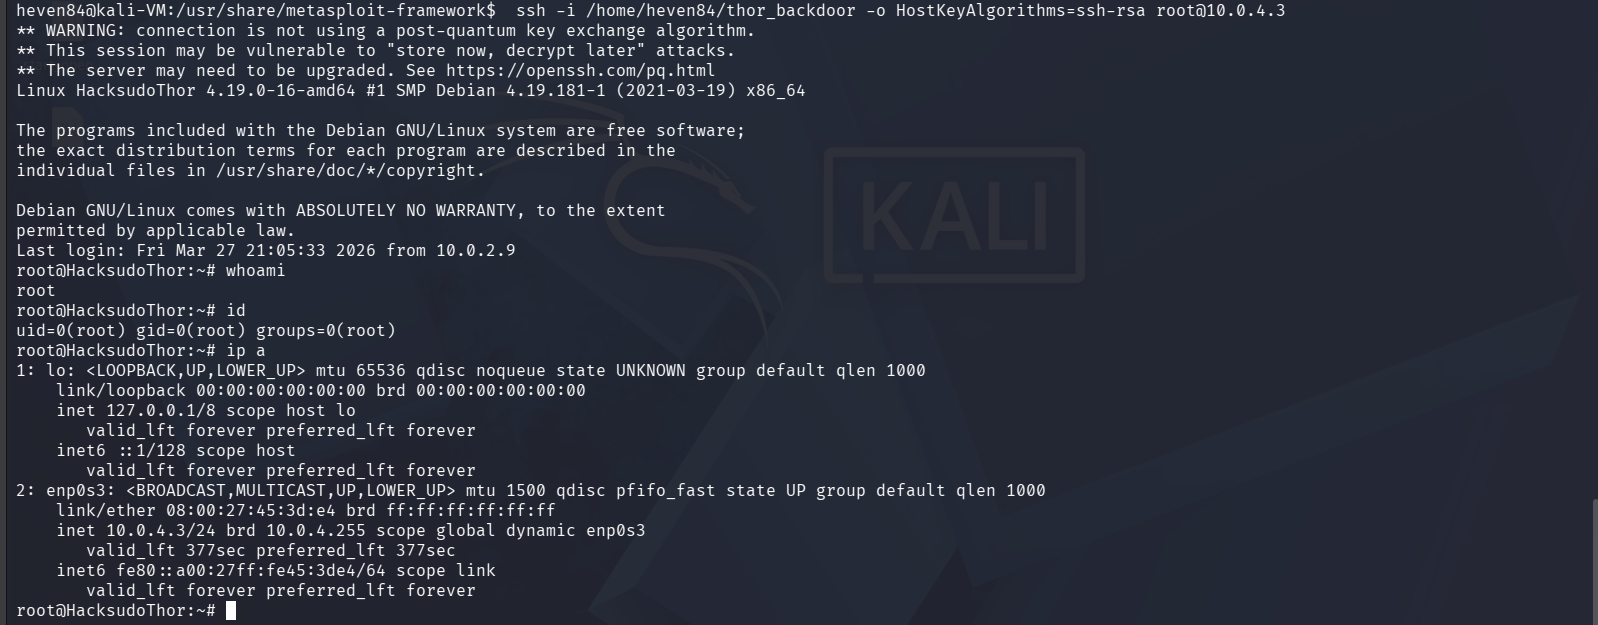 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 4nuxd/cve-2025-66034
CVE-2025-66034 - fontTools varLib Arbitrary File Write → RCE PoC exploit for an Arbitrary File Write + XML Injection vulnerability in…
 h0w1tzxr/tryhack3m-bricks-heist
🧱 CVE-2024-25600 WordPress Bricks Builder RCE Exploit + TryHackMe Bricks Heist CTF Write-up
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 thieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm
Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
 n0m4d22/poc-cve-2015-10141-xdebug
Proof-of-Concept exploit script for Xdebug 2.5.5 and earlier versions (CVE-2015-10141).
 hklabcr/cve-2011-2523
Manual and automated exploitation walkthrough for vsftpd 2.3.4 backdoor (CVE-2011-2523) with custom reverse shell payload and Metasploit integration…
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
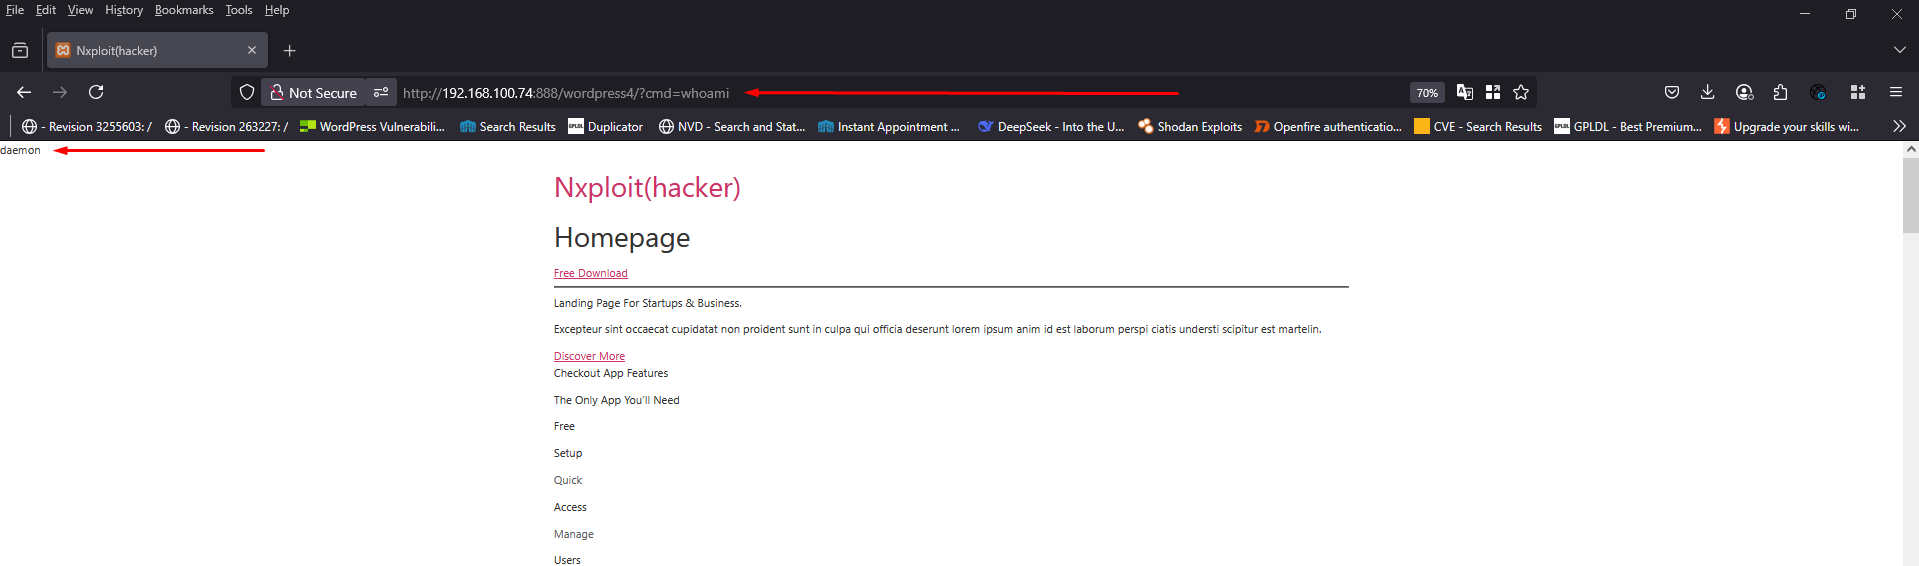 nxploited/cve-2025-39601
WordPress Custom CSS, JS & PHP plugin <= 2.4.1 - CSRF to RCE vulnerability
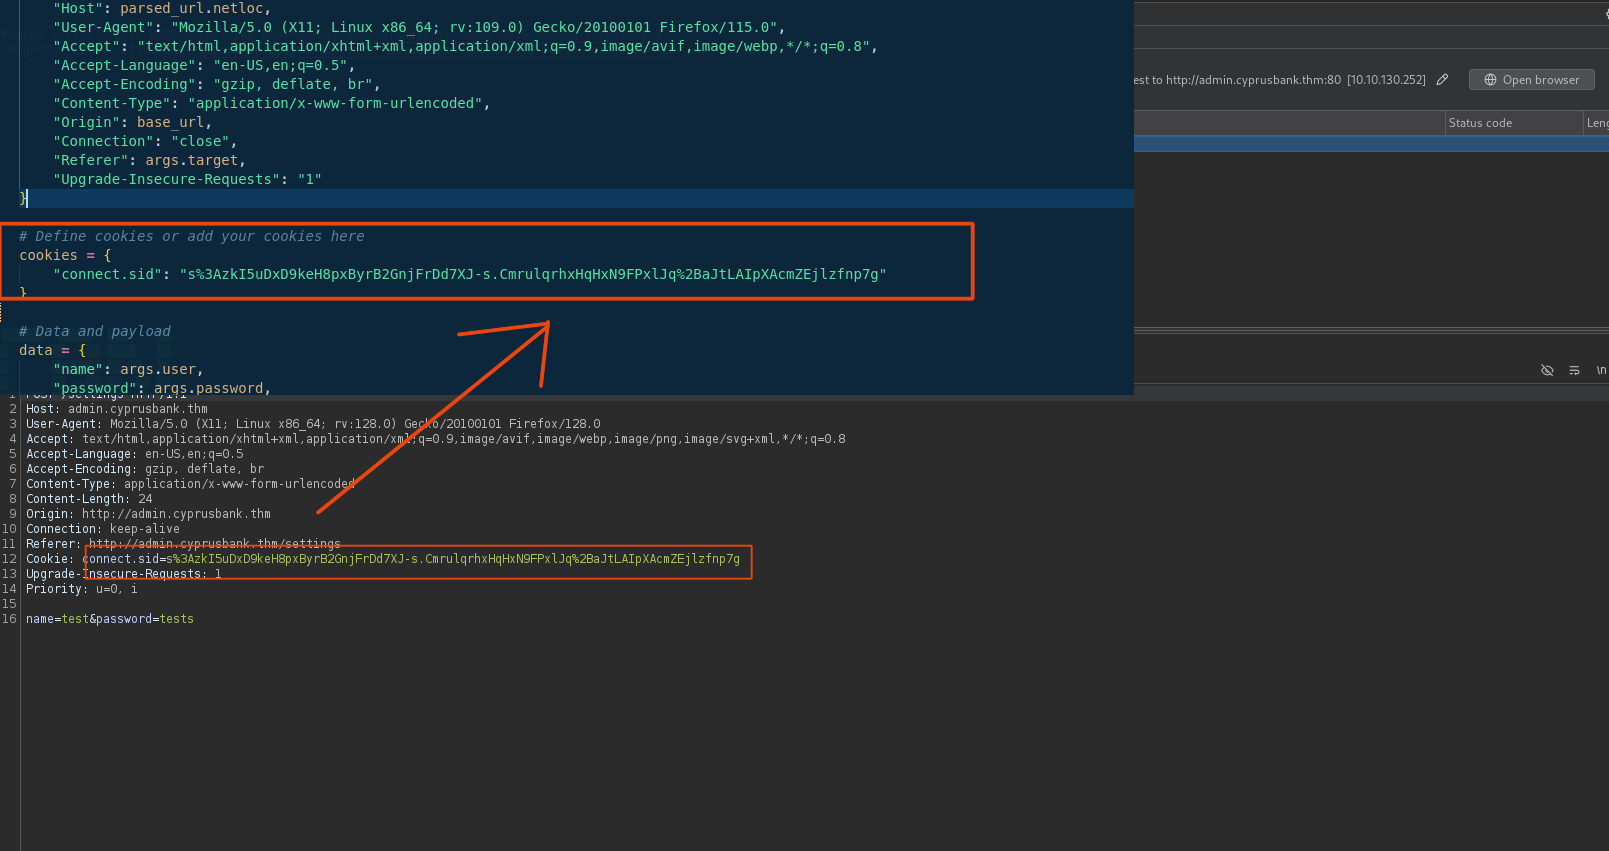 l0n3m4n/cve-2022-29078
Serverside Template Injection (SSTI) RCE - THM challenge "whiterose"