

JavaSecLab
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
code-analysisctfdevsecops+6
881
whgojp/javaseclabComprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 fknmega/aether
AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
 deadexpl0it/wp2shell-poc
wp2shell — WordPress Core Pre-Auth RCE Chain poc for CVE-2026-63030 and CVE-2026-60137
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 alreadyclosed/cve-2026-39987
CVE-2026-39987 for marimo 0.20.4 PoC
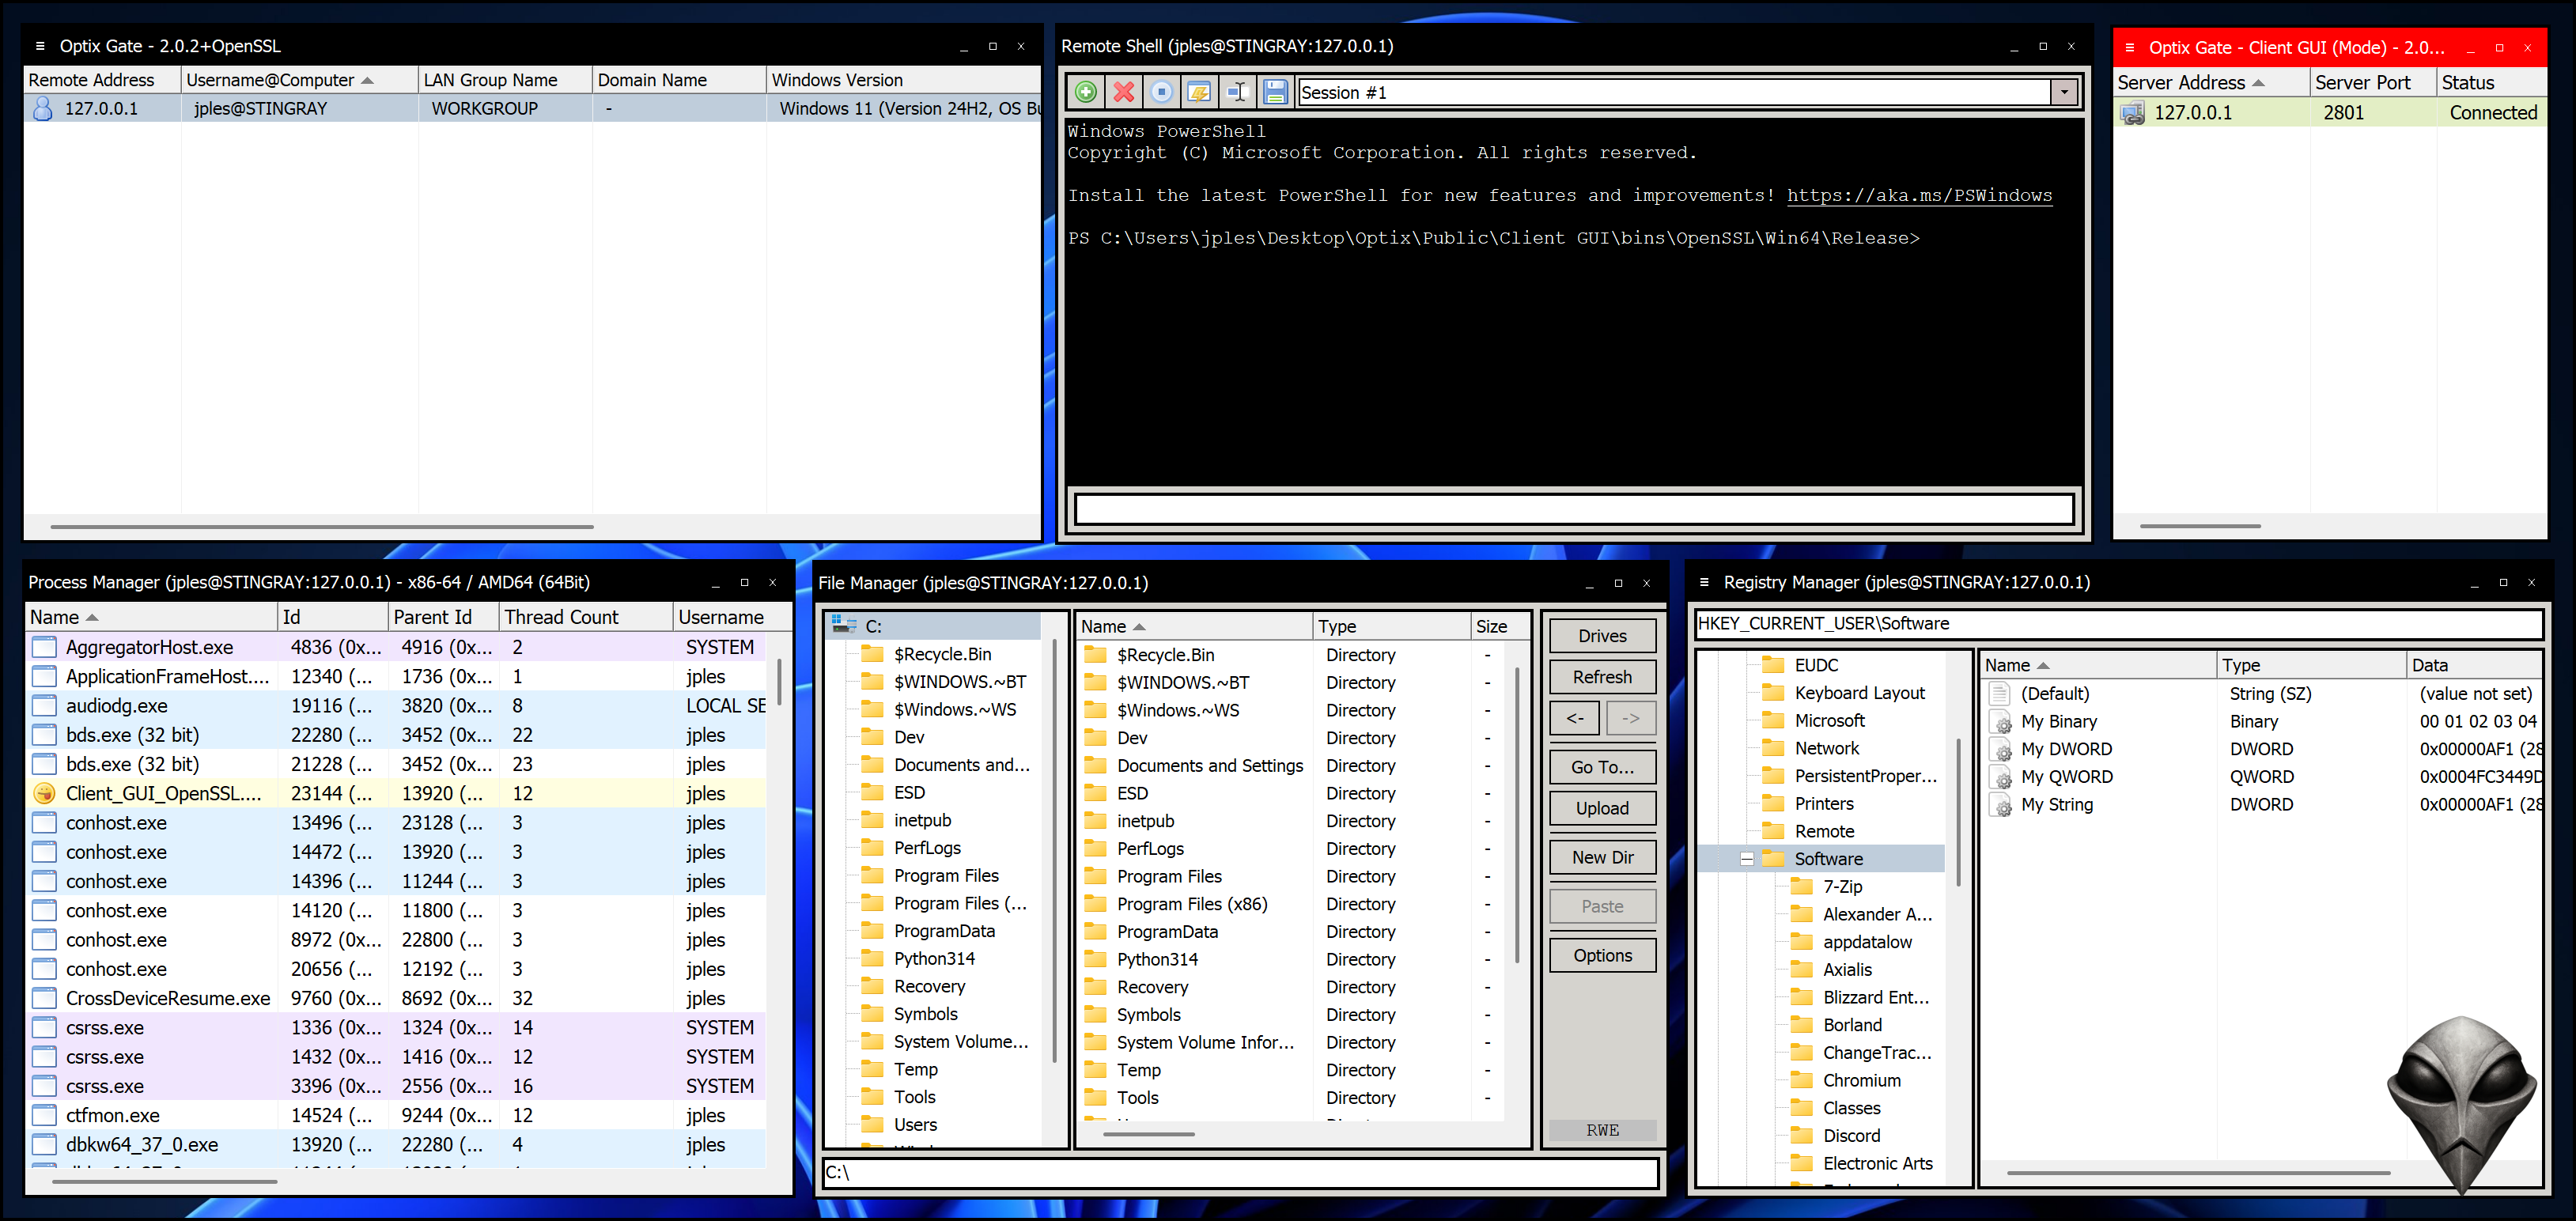 darkcodersc/optixgate
Open-source multi-purpose remote access tool for Microsoft Windows
 vanhari/cve-2026-39987
Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.


 bishopfox/otto-support
An implementation of a vulnerable MCP server using mcp-go
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 uziii2208/cve-2025-33073
Universal exploitation tool for CVE-2025-33073 targeting Windows Domain Controllers with DNSAdmins privileges and WinRM enabled.
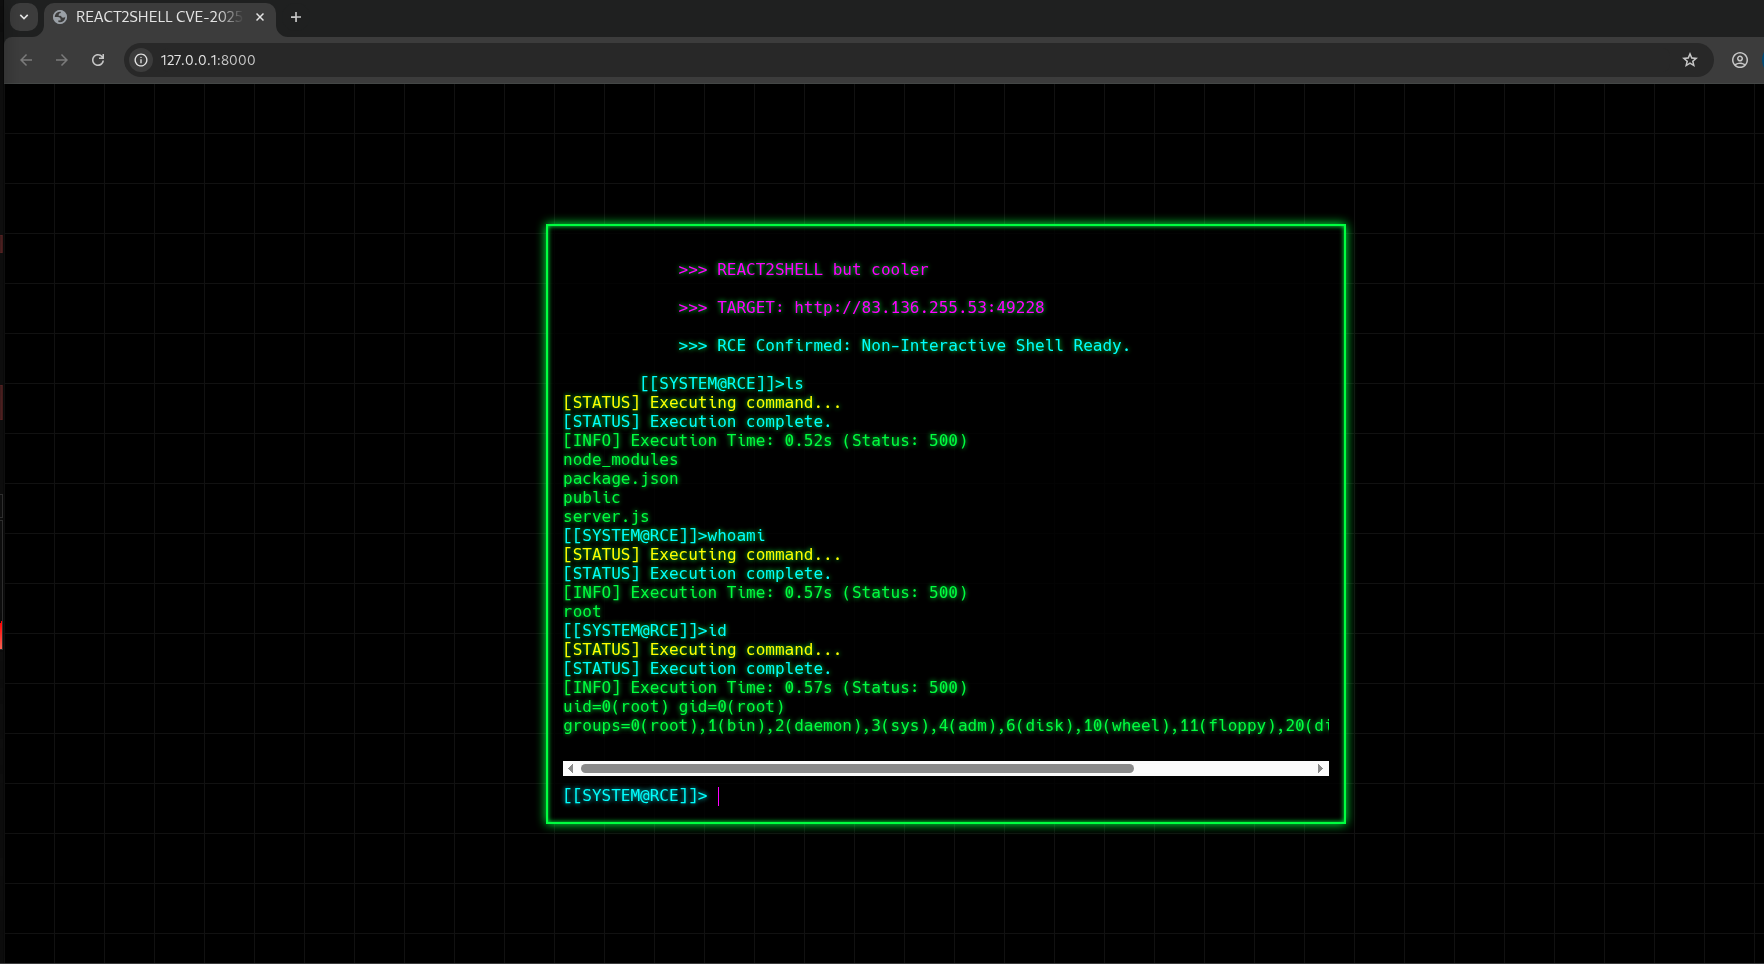 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…