
metasploitable3-pentest-writeup
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
adfortunato/metasploitable3-pentest-writeupHome-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 nongiach/sudo_inject
[Linux] Two Privilege Escalation techniques abusing sudo token
 foxyproxys/cve-2023-52654
Automated privilege escalation script exploiting misconfigured setuid/sgid binaries, sudo, cron, and LD_PRELOAD on Unix systems. Designed for CTF and…
 moscvv/thm-cybersec-portfolio
Write-ups from completed TryHackMe rooms — Linux privilege escalation, sudo buffer overflow (CVE-2019-18634), and OWASP Top 10 (2025).
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 mikivirus0/sudoinjection
Sudo Local Privilege Escalation CVE-2025-32463 (Best For Cases Where the shell is not stable to spawn a new root shell)
 mirchr/cve-2025-32463-sudo-chwoot
PoC for CVE-2025-32463 - Sudo chroot Elevation of Privilege Vulnerability
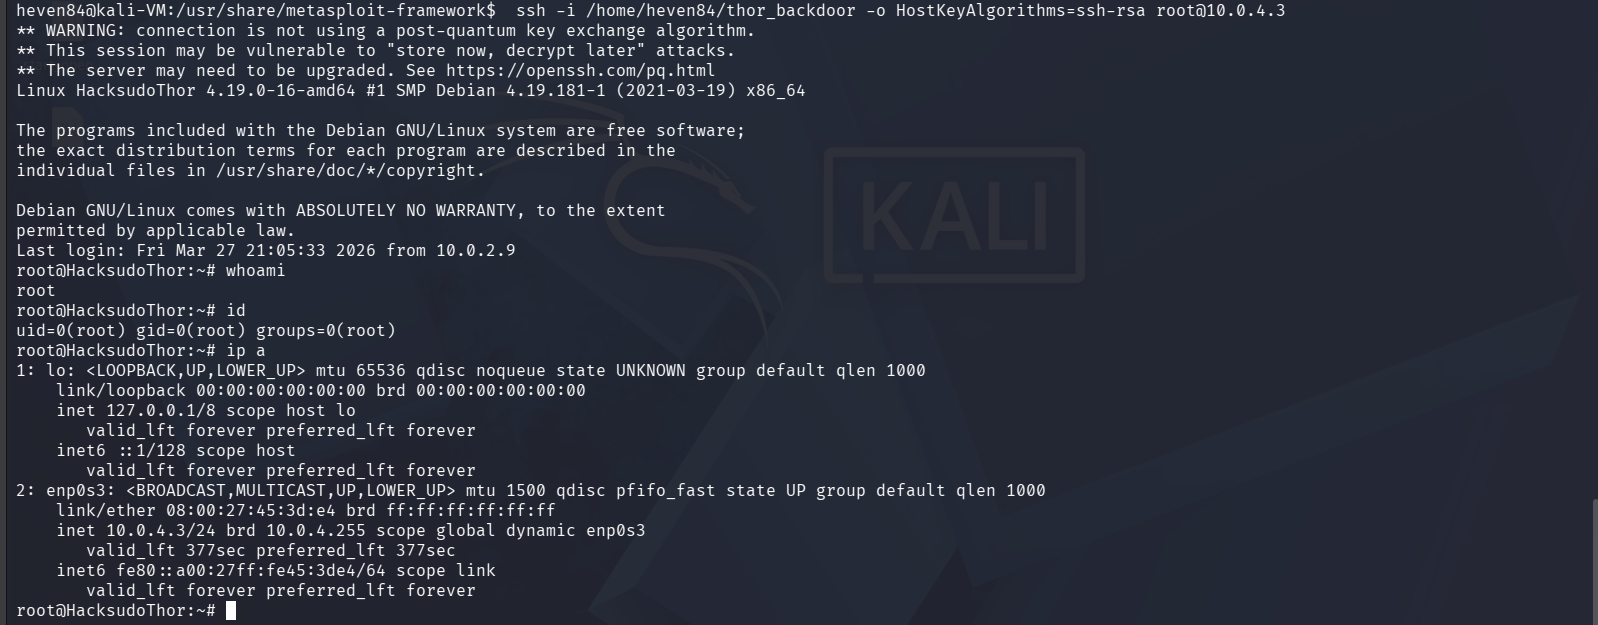 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 j3r1ch0123/cve-2025-32462
Exploit for CVE-2025-32462 enabling privilege escalation by bypassing sudo host restrictions on Linux systems with affected sudo versions and…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 adityabhatt3010/room-walkthrough-billing
A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…