
Enigm-Writeup
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
ctfeducationexploitation+7
1
abdelhakimgafernetworksec/enigm-writeupComprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…
 danreis20/pentest-lab-metasploitable2
Laboratório de pentest em rede isolada: enumeração com nmap/nikto e exploração manual do Metasploitable2 (backdoor vsFTPd CVE-2011-2523, bindshell)…
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
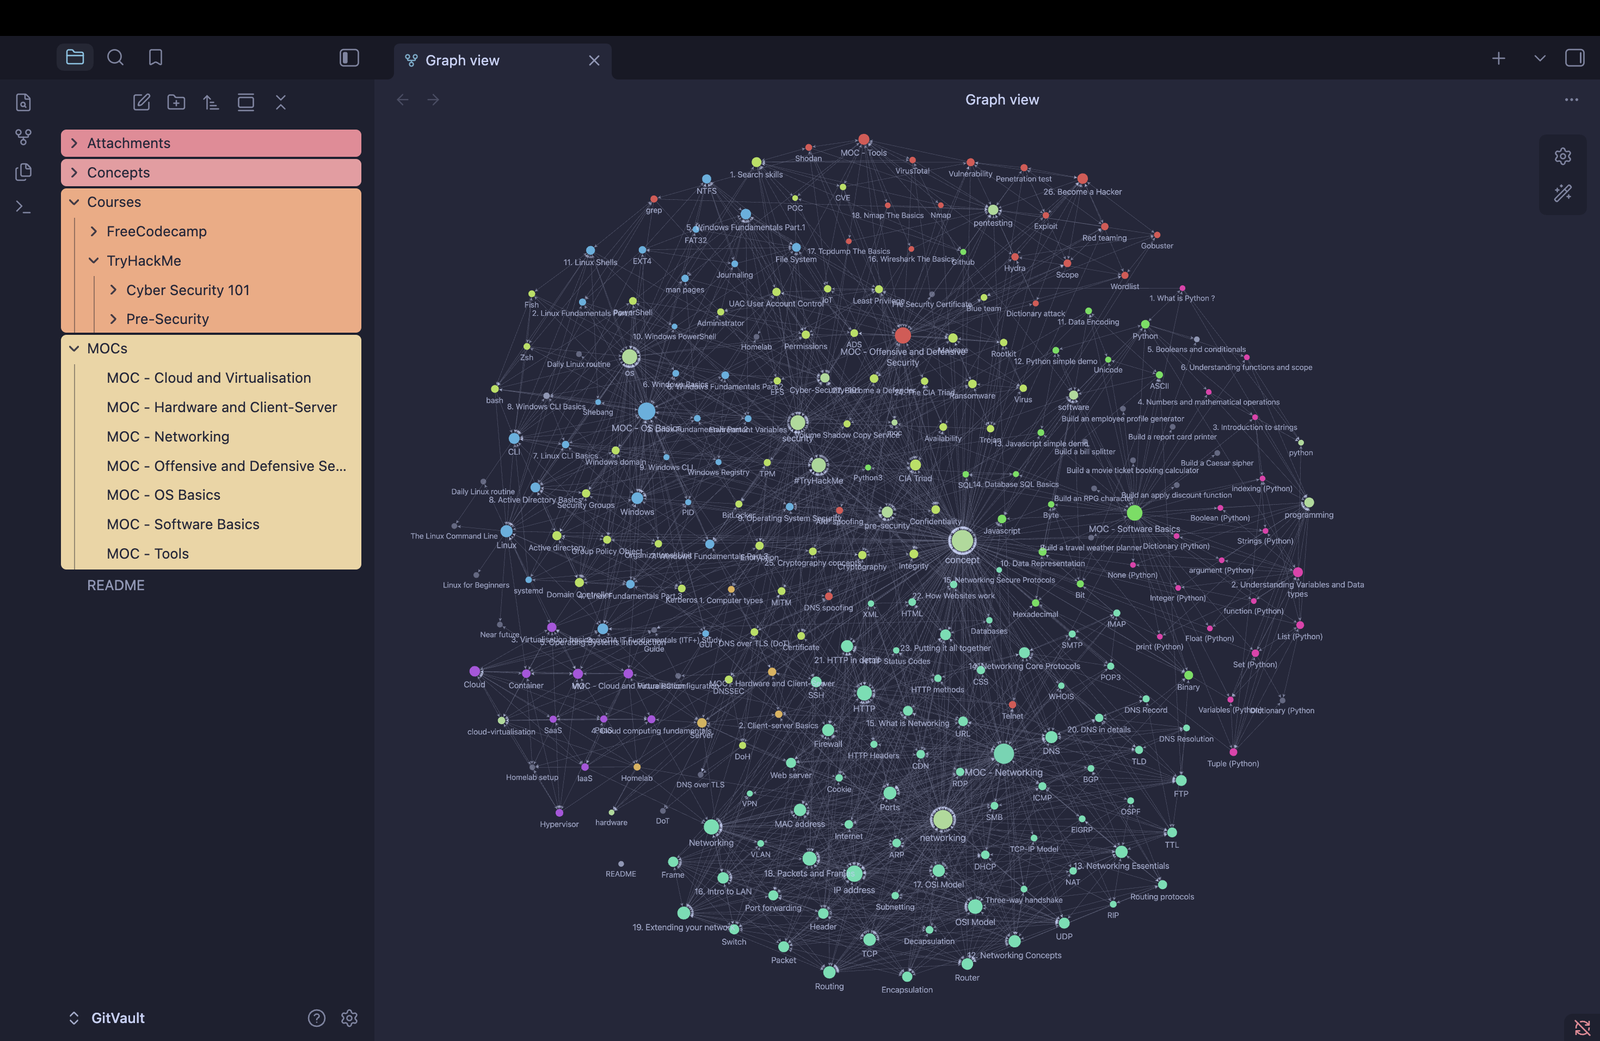 gitowl58/gitvault
A beginner Obsidian Vault structure for Cybersecurity, Linux, Homelabbing / Self-hosting, all about sharing knowledge.
 pczbuilds/monikerlink-cve-2024-21413-writeup
Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…
 horkimhab/cve-2026-74469
Proof-of-concept and educational research repository for CVE-2026-74469 (DiagSpill), providing vulnerability analysis material for authorized lab…
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
 s3v3n-jg/cve-2026-76461
Intentionally vulnerable Python lab demonstrating unsafe YAML deserialization leading to code execution, with three difficulty levels, exploit…
 shivammittal2403/cve-2025-57819-freepbx-range
Isolated educational FreePBX-compatible cyber range for CVE-2025-57819 (CWE-89/CWE-288). Docker lab — not official Sangoma FreePBX.
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
 whereisxuezugi/cplhf
Modular Bash toolkit that hardens Debian/Ubuntu systems for CyberPatriot competitions, automating account, firewall, SSH, PAM, and service hardening…
 taktak0x/htb-nanocorp-cve-2024-0670
PowerShell exploit for CVE-2024-0670 that abuses CheckMK Agent MSI repair to escalate privileges to SYSTEM on the NanoCorp Hack The Box machine.