
All-In-One-CyberSecurity-Resources
 vatsalgupta67/all-in-one-cybersecurity-resources
List of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
ctfcurated-resourceseducation+9
610
vatsalgupta67/all-in-one-cybersecurity-resourcesList of CyberSecurity Resources and some different Sub-Domains of CyberSecurity
 hunterdii/tryhackme-roadmap
Hello, aspiring hackers! 🕵️♂️ Here’s a list of 500+ Free TryHackMe rooms to kickstart your cybersecurity journey. These rooms are absolutely free,…
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
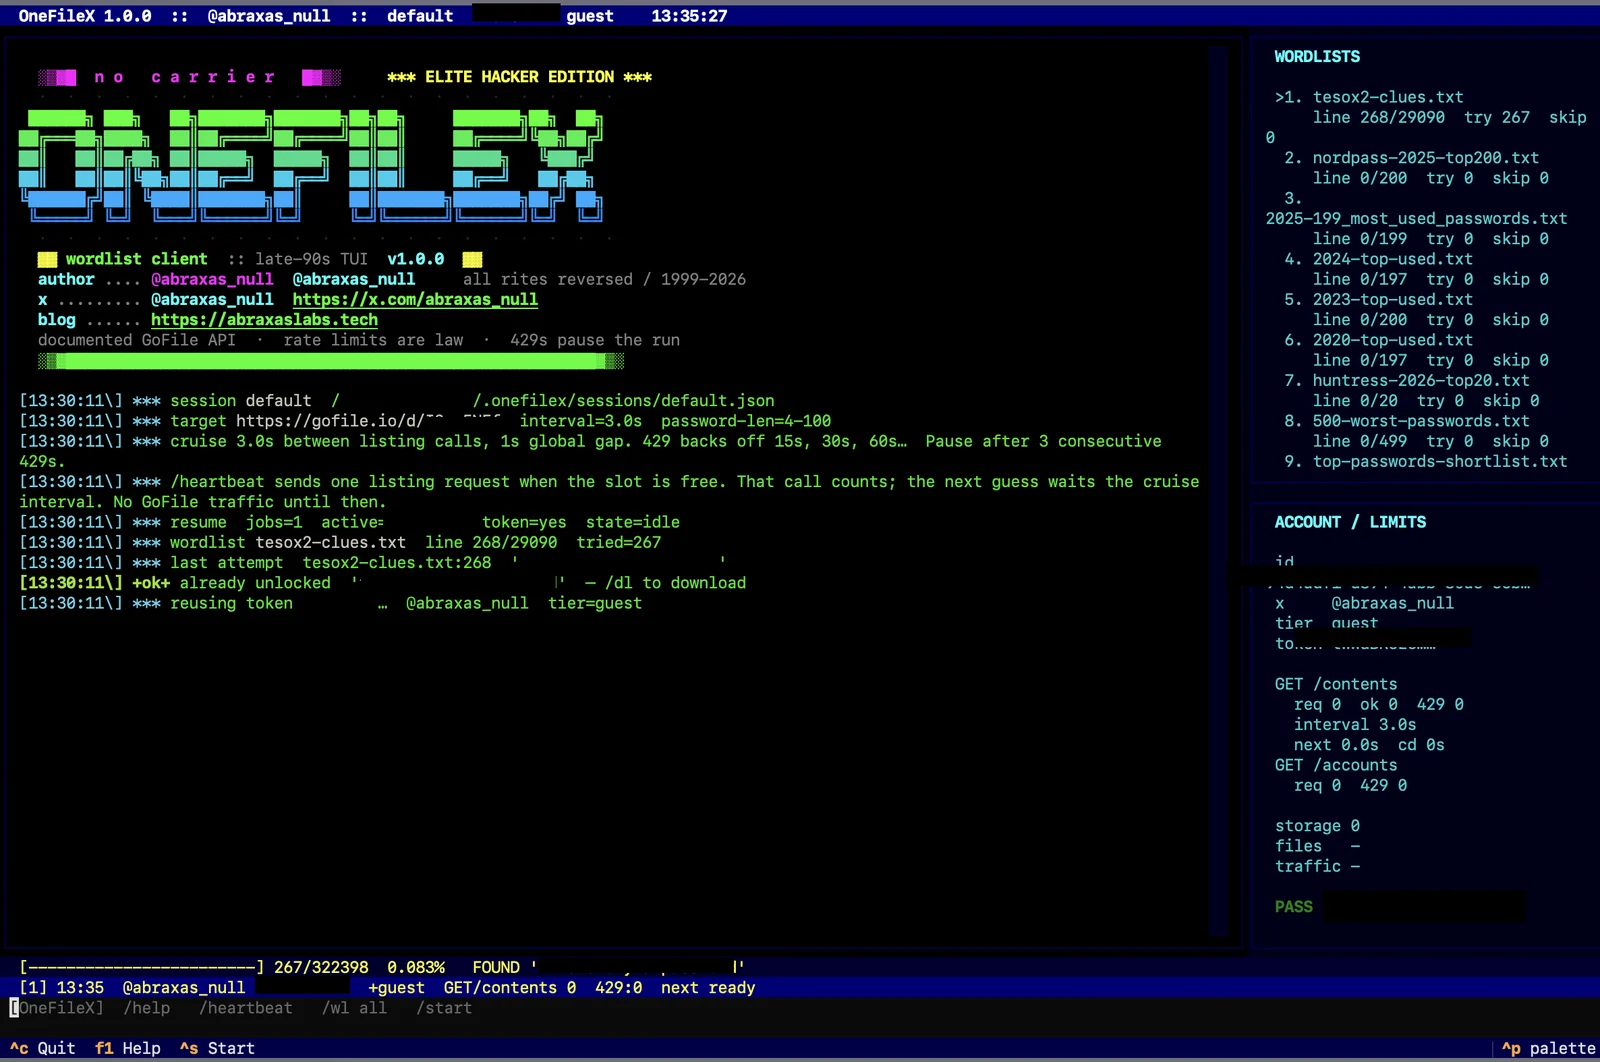 abraxas/gofilex
Wordlist Bruteforcer for GoFile (gofile.io) Download Passwords
 mitsu-bis/security-portfolio
Security portfolio of original responsible-disclosure findings, CTF and lab write-ups, methodology notes, and purpose-built pentest tooling covering…
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 r3fr4kt/devvortex
HackTheBox Devvortex walkthrough covering subdomain fuzzing, Joomla API enumeration, template-based web shell, bcrypt hash cracking, and Apport-CLI…
 rhimavanth32-max/metasploitable2-reconnaissance-and-unrealircd-backdoor-exploitation
End-to-end recon and exploitation of a known backdoor (CVE-2010-2075) on Metasploitable2 using Nmap and Metasploit.
 quincyomoruyi6-lang/blue-writeup-cve-2017-0144
Conducted a complete security assessment of an unpatched Windows 7 target ("Blue") to demonstrate the impact of legacy service vulnerabilities in an…
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…

 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 cves-labs/cve-2026-21877
Dockerized vulnerable lab environment with a Python-based network monitor and dedicated exploit script, enabling hands-on exploitation, privilege…
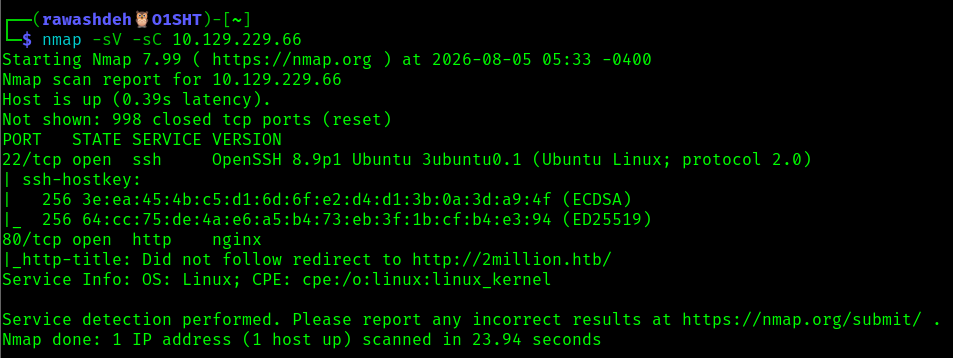 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
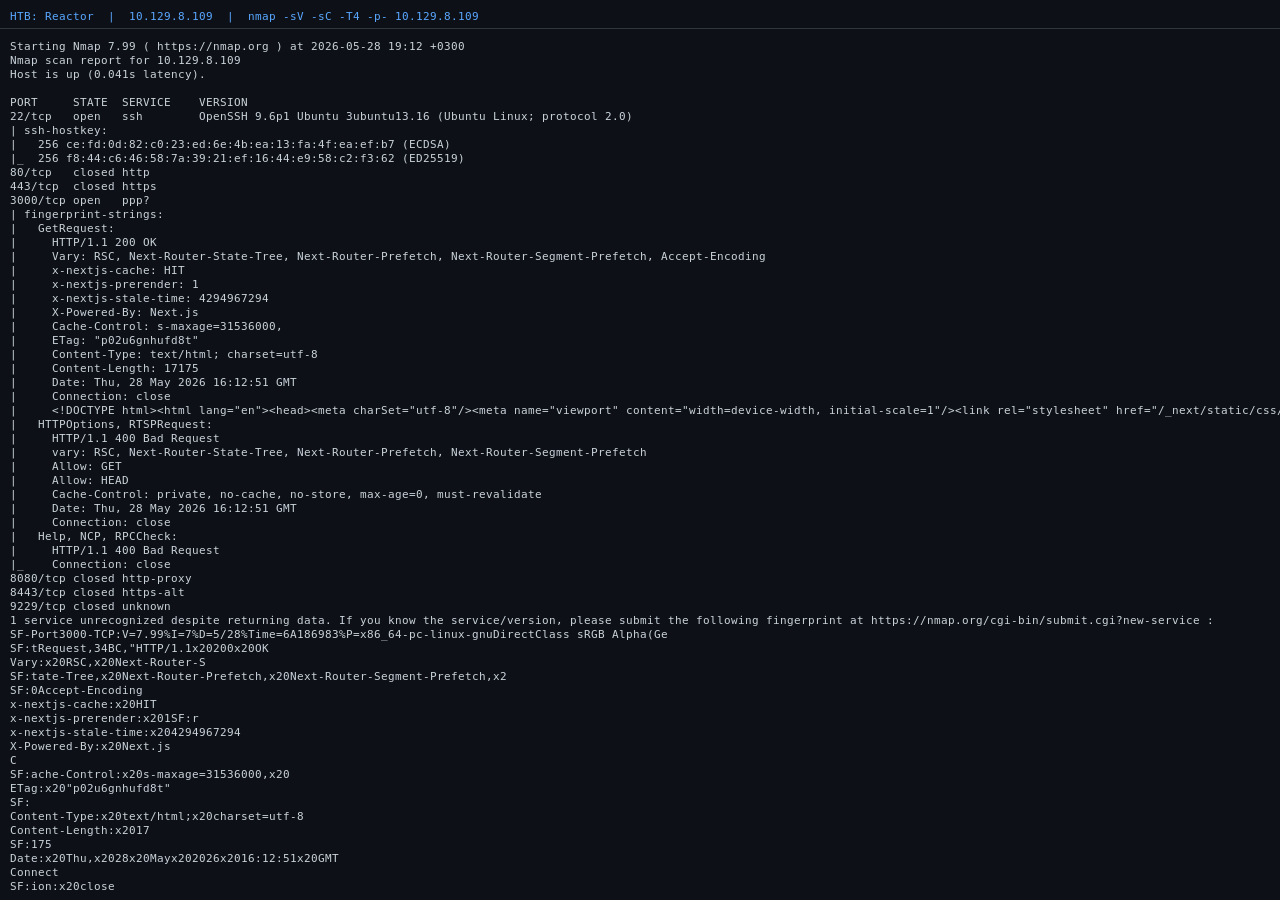 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
 joe-shenouda/awesome-cyber-skills
A curated list of hacking environments where you can train your cyber skills legally and safely