
CVE-2026-76461
 s3v3n-jg/cve-2026-76461
Intentionally vulnerable Python lab demonstrating unsafe YAML deserialization leading to code execution, with three difficulty levels, exploit…
ctfeducationexploitation+3
1
s3v3n-jg/cve-2026-76461Intentionally vulnerable Python lab demonstrating unsafe YAML deserialization leading to code execution, with three difficulty levels, exploit…
 pelock/crackmez3s-ctf-crackme-tutorial
How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 mindcrypt/covertchannels-steganography
A list of covert channels and steganography/steganalysis resources (books, papers & tools)
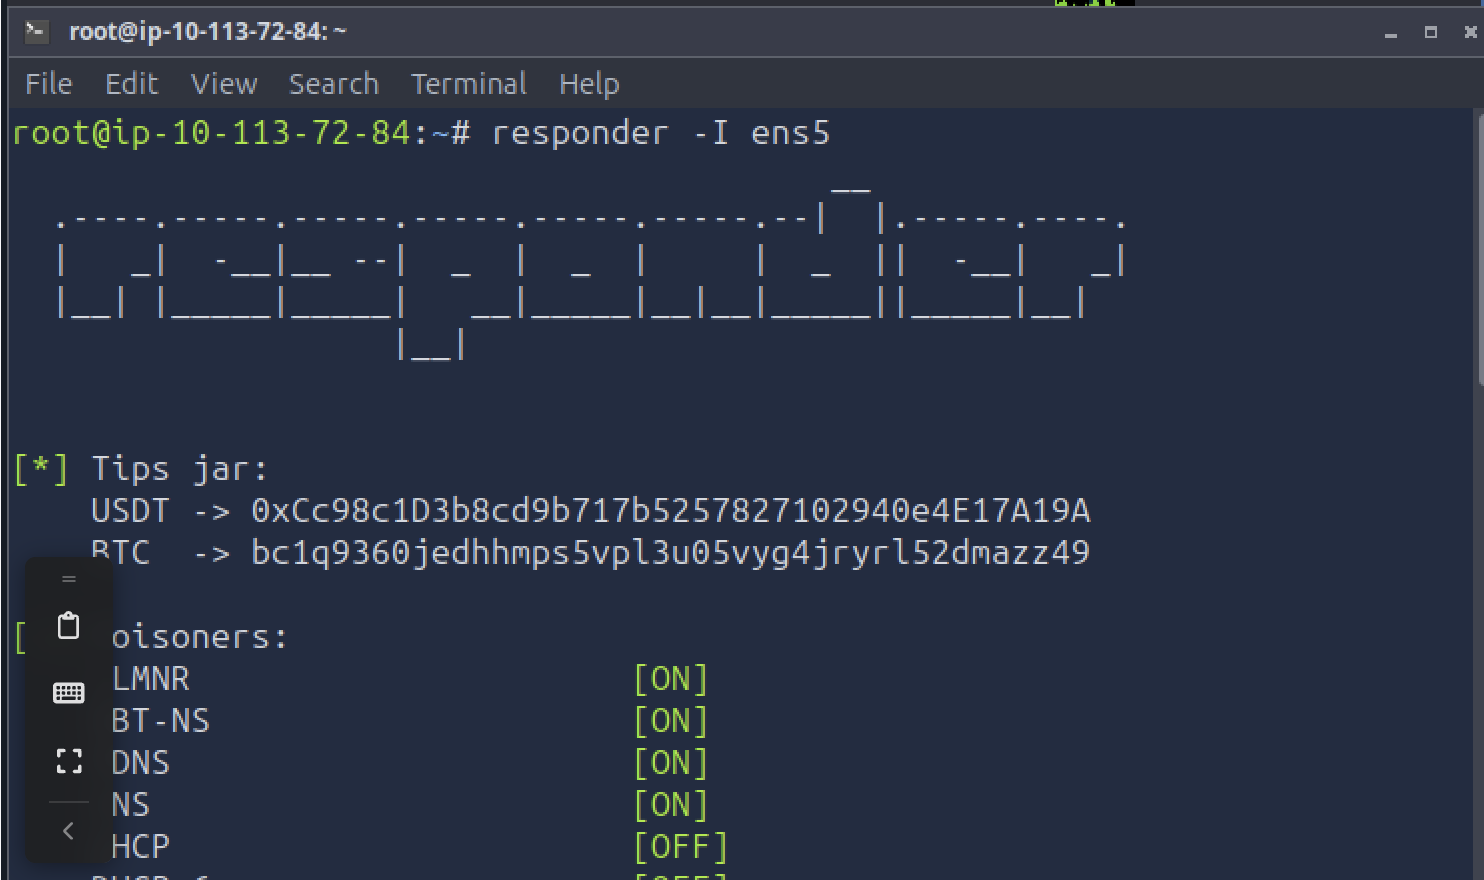 omarmahmoud1024/tryhackme-monikerlink-writeup
TryHackMe Moniker Link (CVE-2024-21413) walkthrough: Outlook Protected View bypass leading to NTLMv2 hash capture via a crafted moniker link.
 screenpipe/screenpipe
YC (S26) | Open Computer History | Record your screen continuously locally and provide context to your agents (Claude, Codex, Openclaw, Hermes,…
 pouriam23/vulnerability-in-remix-react-router-cve-2025-31137-
CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.
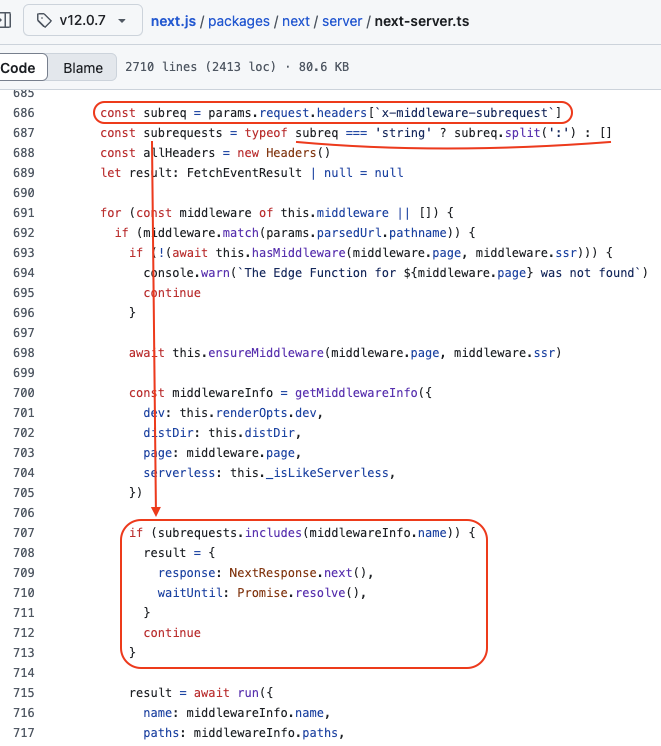 gokul-krishnan-v-r/cve-2025-29927
Next.js and the corrupt middleware...TRY TO HACK IT..!
 lavanya2085/solar-exploiting-log4j
This repository provides a detailed walkthrough of the *Solar Exploiting Log4j room* on TryHackMe, focusing on exploiting the critical Log4Shell…
 pouriam23/next.js-middleware-bypass-cve-2025-29927-
CTF challenge to learn and practice exploiting the Next.js middleware bypass vulnerability (CVE-2025-29927) by finding a flag in an admin page.
 macaroniwdcheese/cve-2025-55182-lab
Local lab for understanding CVE-2025-55182 RCE in React Server Components/Next.js. Includes a deliberately vulnerable app and optional scanner helper…
 0ca/boxpwnr
A modular framework for benchmarking LLMs and agentic strategies on security challenges across HackTheBox, TryHackMe, PortSwigger Labs, Cybench,…
 demining/digital-signature-forgery-attack
How CVE-2025-29774 Vulnerabilities and the SIGHASH_SINGLE Bug Threaten Multi-Signature Wallet Operational Methods with Fake RawTX
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 benedictejepu/cve-2024-24945-nginx-rift---tryhackme-lab-walkthrough
This lab demonstrates the exploitation of CVE-2024-24945, a heap corruption vulnerability affecting NGINX. The objective was to understand how memory…
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…