

pentest
 zishanadthandar/pentest
Jekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
ctfcurated-resourceseducation+7
748
zishanadthandar/pentestJekyll-based pentesting knowledge base with methodology guides, cheatsheets, tool indexes, certification roadmaps, and curated practice lab and CTF…
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 abdelhakimgafernetworksec/enigm-writeup
Comprehensive penetration testing write-up and exploit details for Hack The Box - Enigma machine, covering local enumeration, OliveTin CVE-2026-27626…
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
 zales2004/sunset-noontide-pentesting
Description Professional penetration testing assessment of the Sunset: Noontide VulnHub machine, covering reconnaissance, service enumeration,…
 germarr93/cybersecurity-pentest-lab
CVE-2004-2687 (Distcc 3.2.1) exploitation, methodology & remediation — Metasploitable2 lab
 luiskrnr/htb_helix_cve-2023-34468
Writeup of the Hackthebox Helix machine, detailing exploitation of CVE-2023-34468 and penetration testing steps.
 n1et/cve-2021-4034
Shell script that exploits CVE-2021-4034 (PwnKit) for local privilege escalation, intended for CTF use.
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 s0ld13rr/pentestcode
Autonomous AI penetration testing agent that orchestrates multi-agent recon, exploitation, post-exploitation, and reporting with persistent…
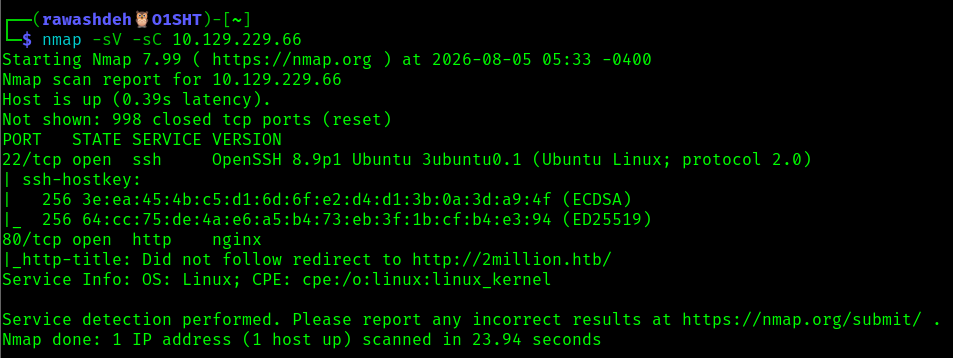 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
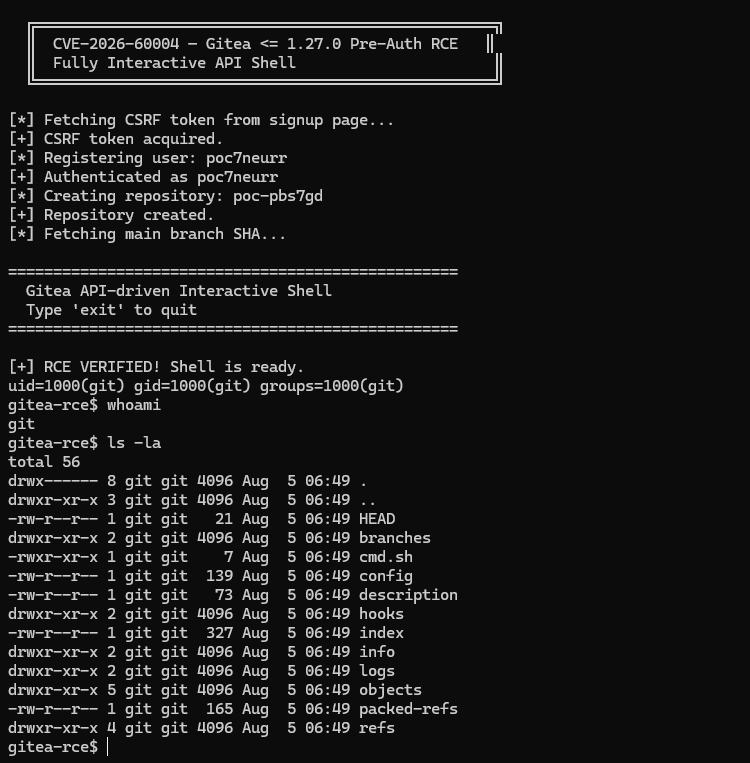 sachinart/cve-2026-60004-gitea-0day
CVE-2026-60004 — Gitea <= 1.27.0 Pre-Auth RCE
 gbuyssens/cve-2026-41651
Local privilege escalation via TOCTOU race condition in PackageKit's.
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 r3tr074/exploits
Personal collection of exploits including n-days, 0-days, CTFs, kernel and browser vulnerabilities for security research and penetration testing.
 al1ex/awesome-pentest
Collection of penetration testing tools