CVE-2019-18634-writeup
 devteam6rabbit/cve-2019-18634-writeup
analysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
binary-exploitationctfeducation+4
devteam6rabbit/cve-2019-18634-writeupanalysis of the sudo buffer overflow affect sudo version <1.8.26 and how to use GCC to compile publicly availible exploits
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
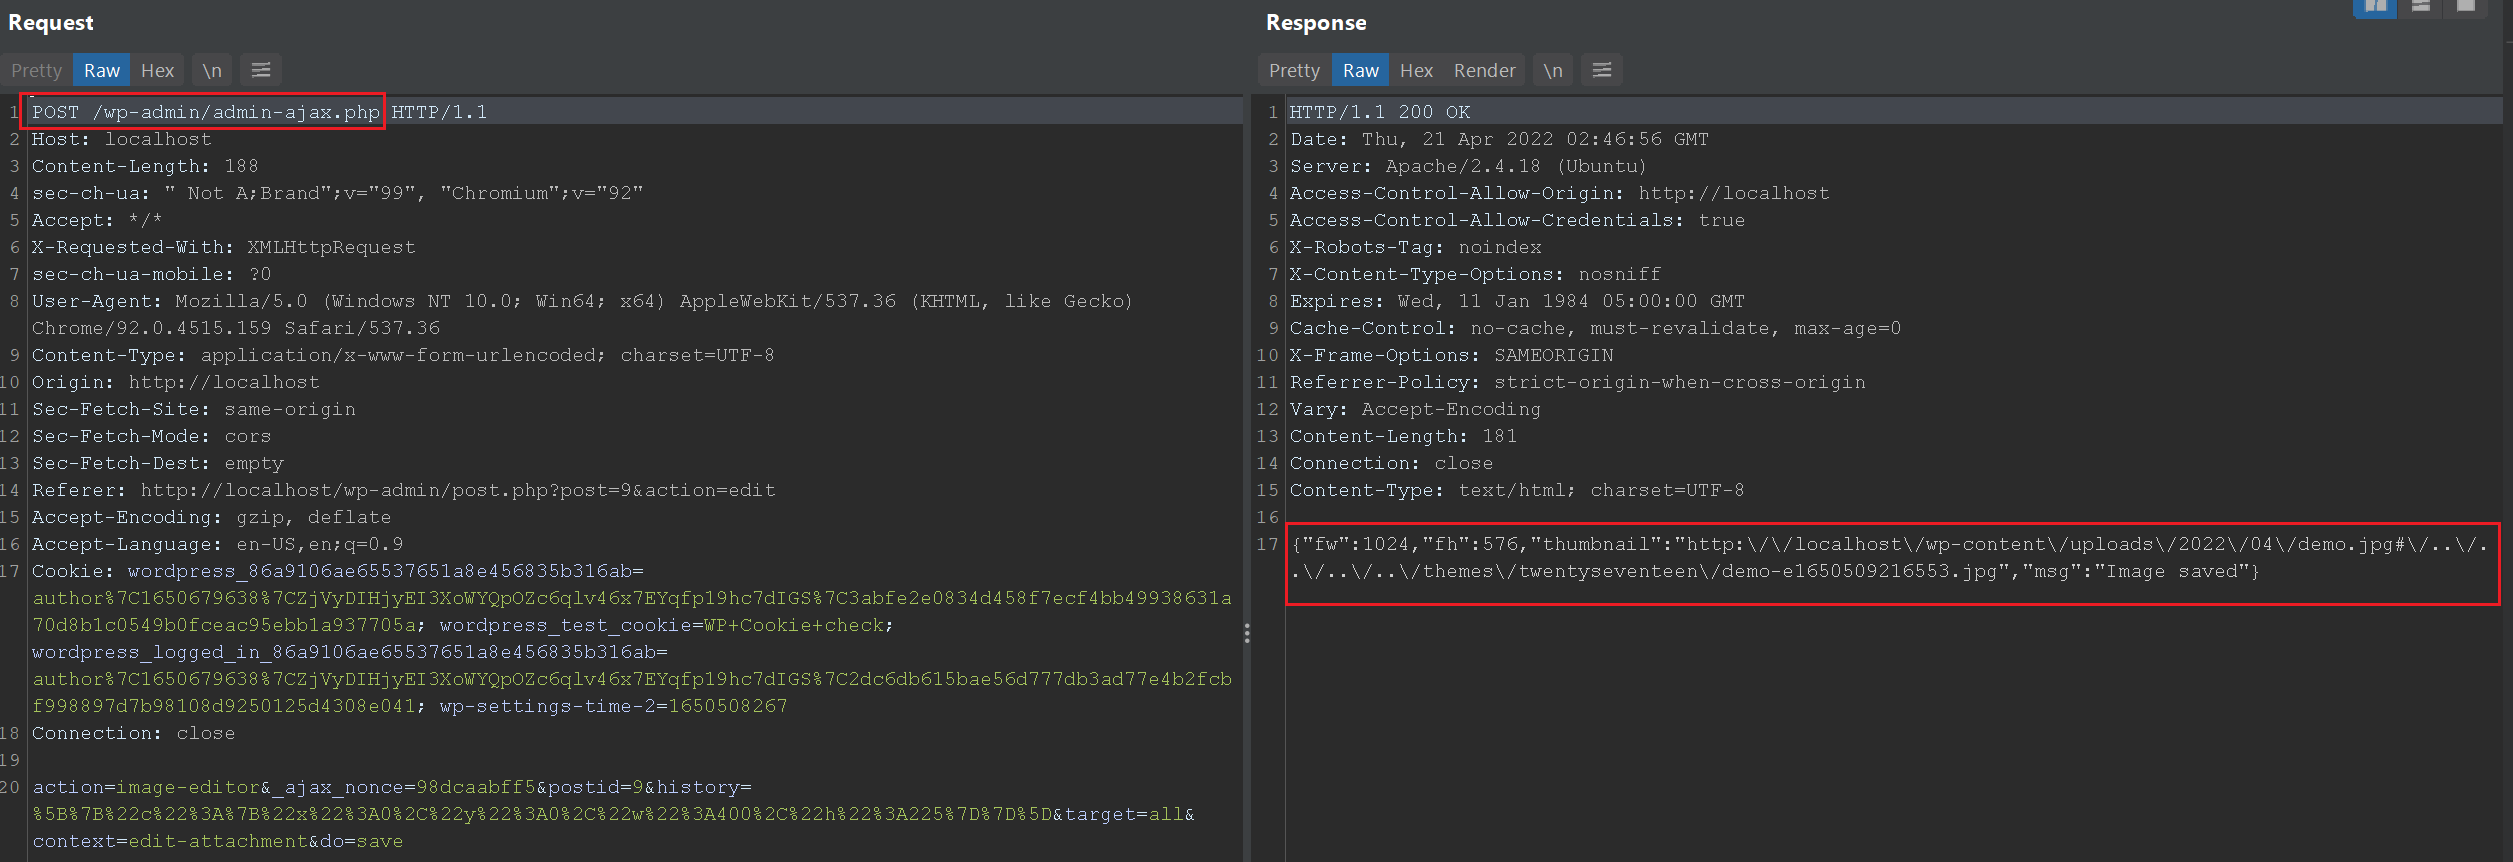 tuannq2299/cve-2019-8942
Detailed technical analysis and proof-of-concept exploit for WordPress RCE vulnerabilities CVE-2019-8942 and CVE-2019-8943, demonstrating LFI-to-RCE…
 hackhoven/strapi-rce
Exploit script showcasing a mixture of CVE-2019-18818 and CVE-2019-19609 for unauthenticated remote code execution in Strapi CMS.
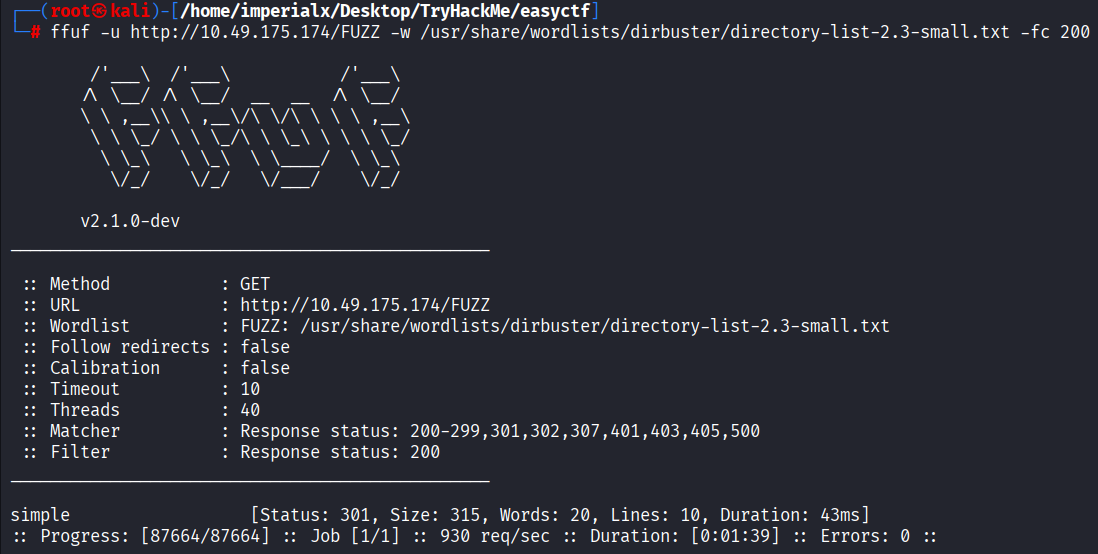 imperialx1104/simple-ctf-writeup
Professional TryHackMe Simple CTF walkthrough covering enumeration, CMS Made Simple SQL Injection (CVE-2019-9053), credential recovery, SSH access,…
 juliourena/cve-2019-19470-redteamrd
CVE-2019-19470 exploit replication with source code, WinDbg commands, PEB modification, and decompilation examples for educational red team training.
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 joaoaugustom/drupal_rest-rce_unauthenticated
This exploit is based on CVE-2019-6340 and was built upon the original exploit by leonjza and the Metasploit module, extending it can be executed…
 cmnatic/dockerized-cve-2019-14287
Containerized and deployable use of the CVE-2019-14287 vuln. View README.md for more.