
WebGoat
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
ctfeducationlabs-practice+4
9.3k
webgoat/webgoatDeliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 owasp/railsgoat
A vulnerable version of Rails that follows the OWASP Top 10
 owasp/wrongsecrets-binaries
Source code for the Binaries of OWASP WrongSecrets
 vitalysim/awesome-hacking-resources
A collection of hacking / penetration testing resources to make you better!
 owasp/donkai
DonkAI is a hands-on lab for the OWASP Top 10 for LLM Applications (2025) - no real LLM required.
 webpwnized/mutillidae
OWASP Mutillidae II is a free, open-source, deliberately vulnerable web application providing a target for web-security training. This is an…
 infoslack/awesome-web-hacking
Curated list of web application security resources including books, tools, cheat sheets, labs, and courses for learning penetration testing and…
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 swisskyrepo/graphqlmap
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
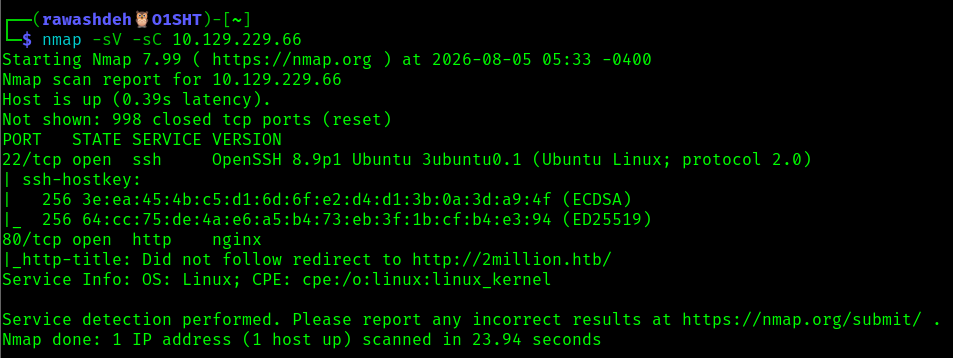 abedallarawashdeh/htb-twomillion-machine
Hack The Box TwoMillion machine writeup — JWT/invite-code bypass, IDOR, command injection, and CVE-2023-0386 privilege escalation.
 husnainfareed/awesome-ethical-hacking-resources
😎 🔗 Awesome list about all kinds of resources for learning Ethical Hacking and Penetration Testing.
 owasp/securityshepherd
Web and mobile application security training platform
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
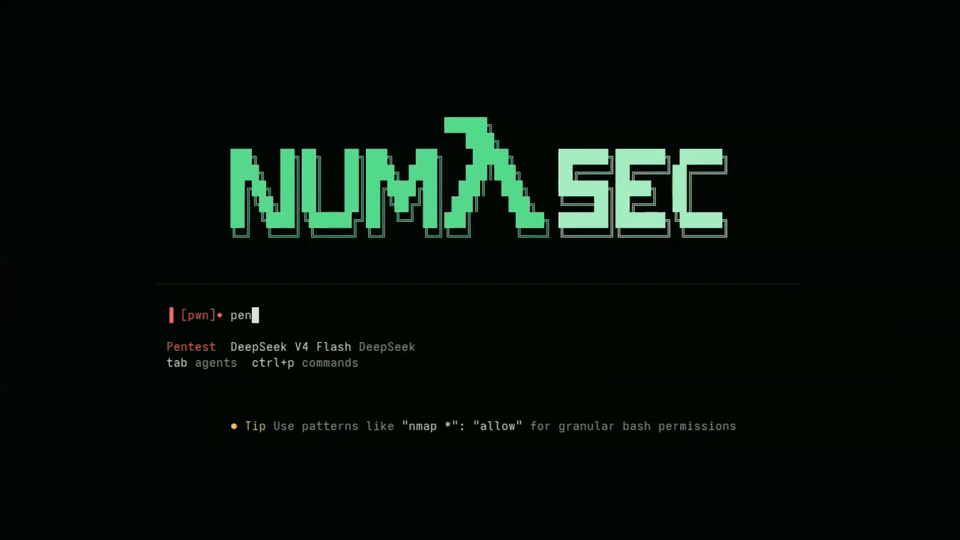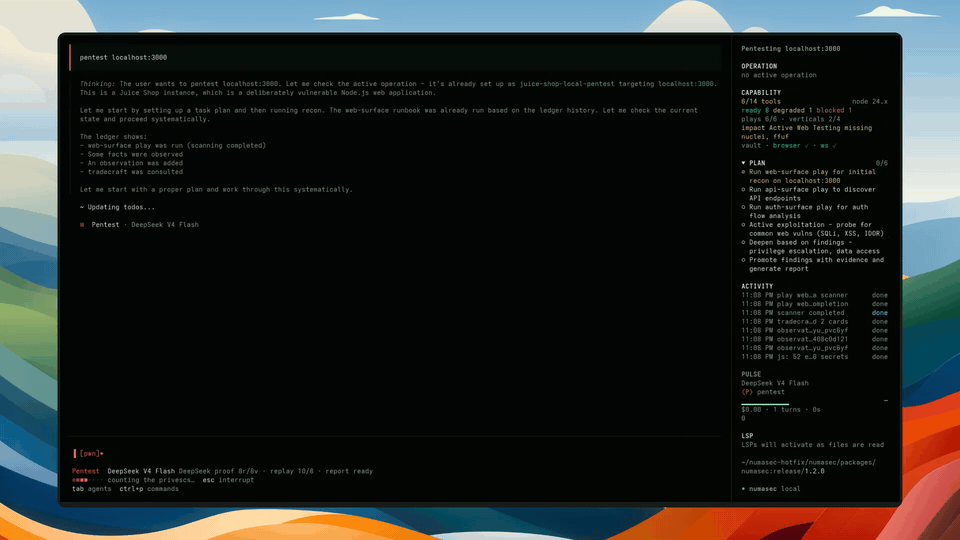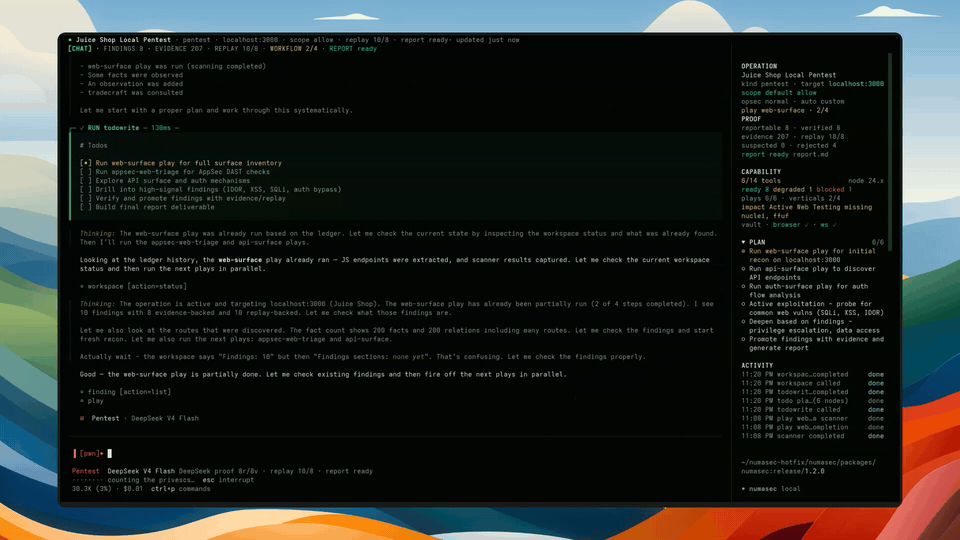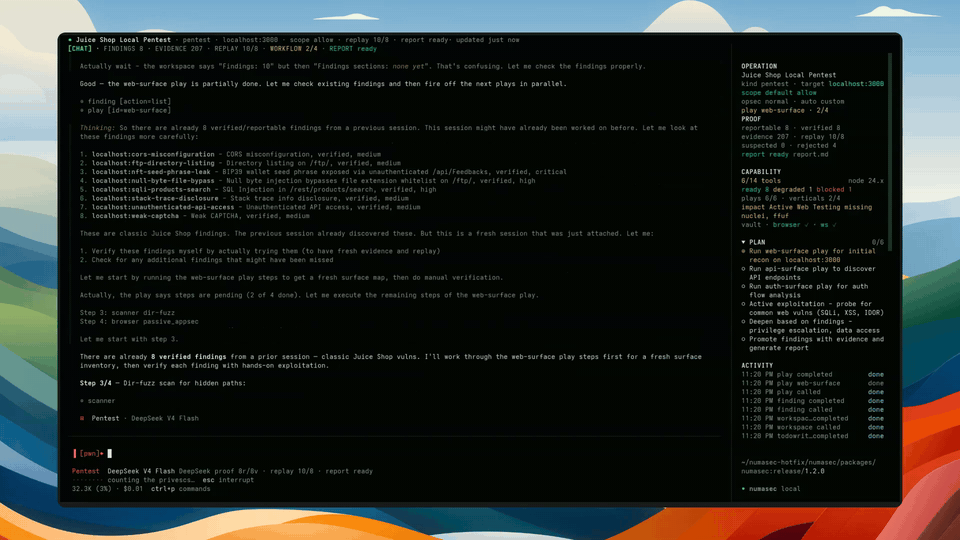 francescostabile/numasec
AI security agent that runs in your terminal, orchestrating local tools, runbooks, and agents for authorized AppSec, pentest, OSINT, and CTF…
 dhotrey/awesome-cybersec
A collection of awesome platforms, blogs, documents, books, resources and cool stuff about security