
Exegol
 theporgs/exegol
Fully featured and community-driven hacking environment
ctfeducationlabs-practice+3
theporgs/exegolFully featured and community-driven hacking environment
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 s1n6h/pentest-harness
Self-hosted AI agent harness for authorized pentests, bug bounty, security labs, and CTFs. Plugin-based, multi-provider LLM support with local…
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 bee-san/ciphey
⚡ Automatically decrypt encryptions without knowing the key or cipher, decode encodings, and crack hashes ⚡
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
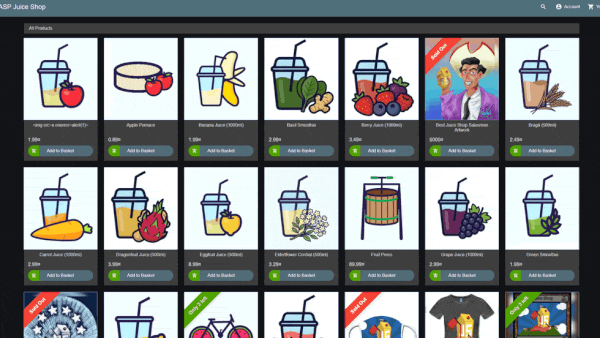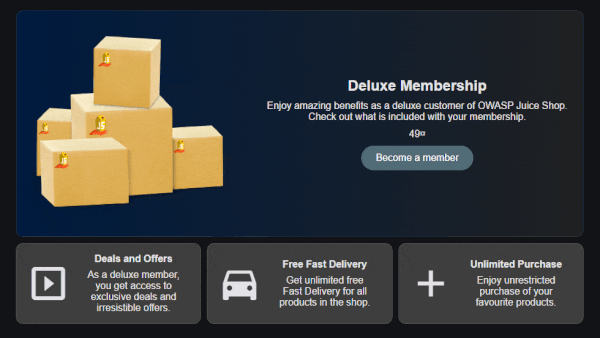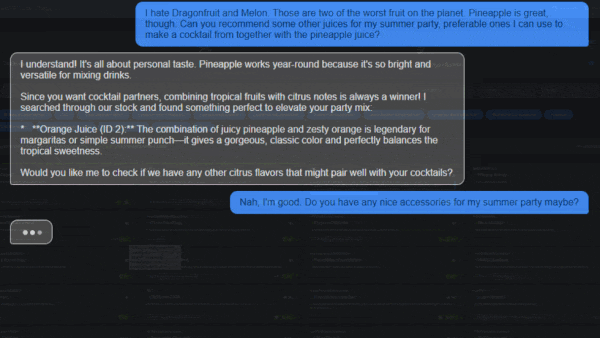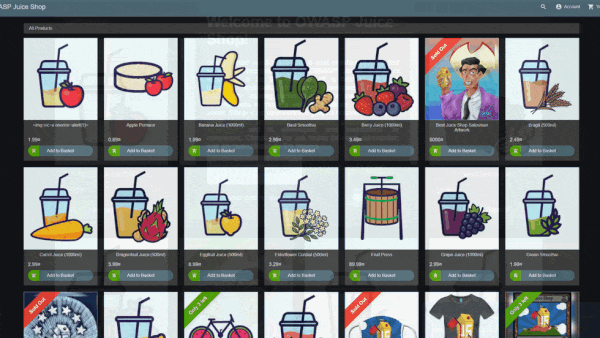 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
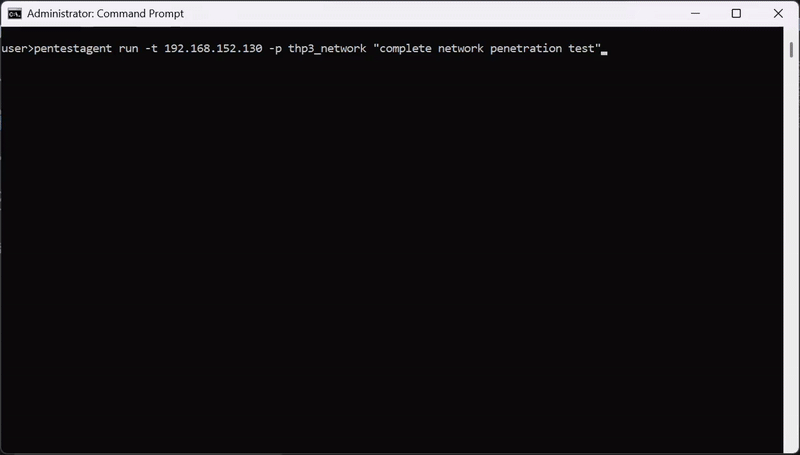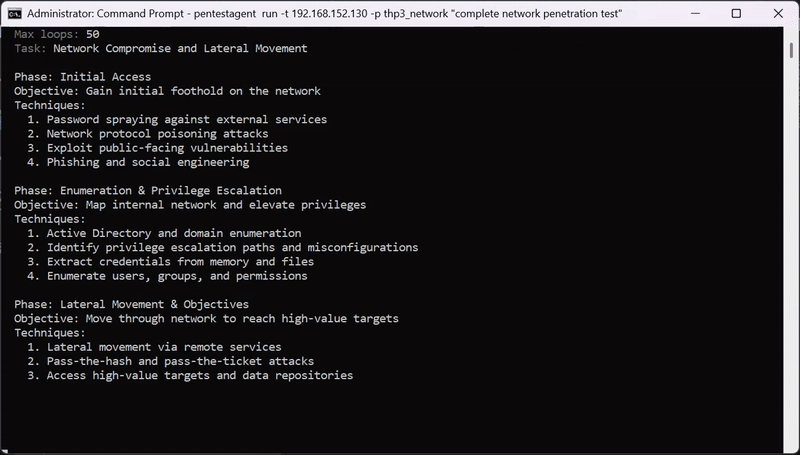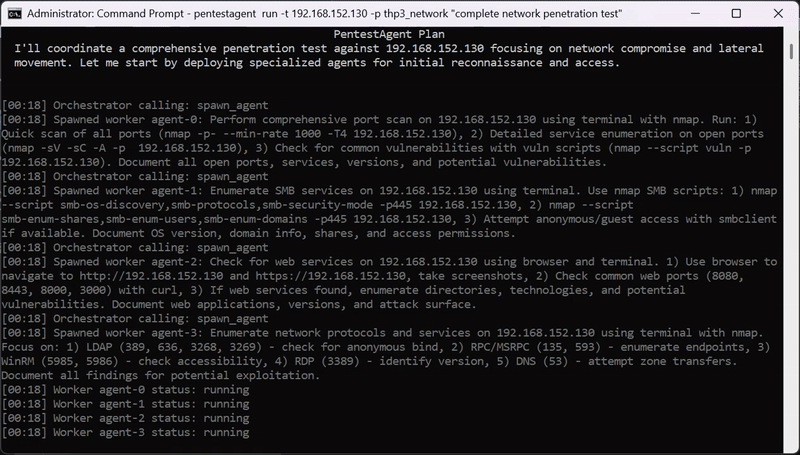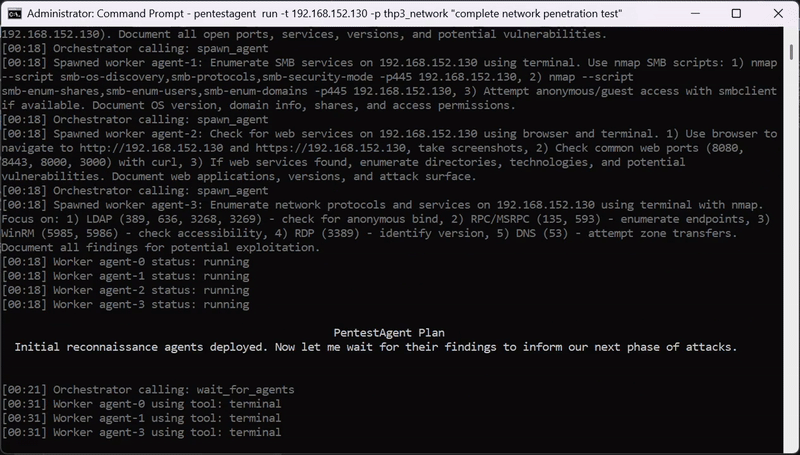 gh05tcrew/pentestagent
AI agent framework for black-box security testing with autonomous multi-agent orchestration, built-in pentesting tools, and MCP integration for bug…
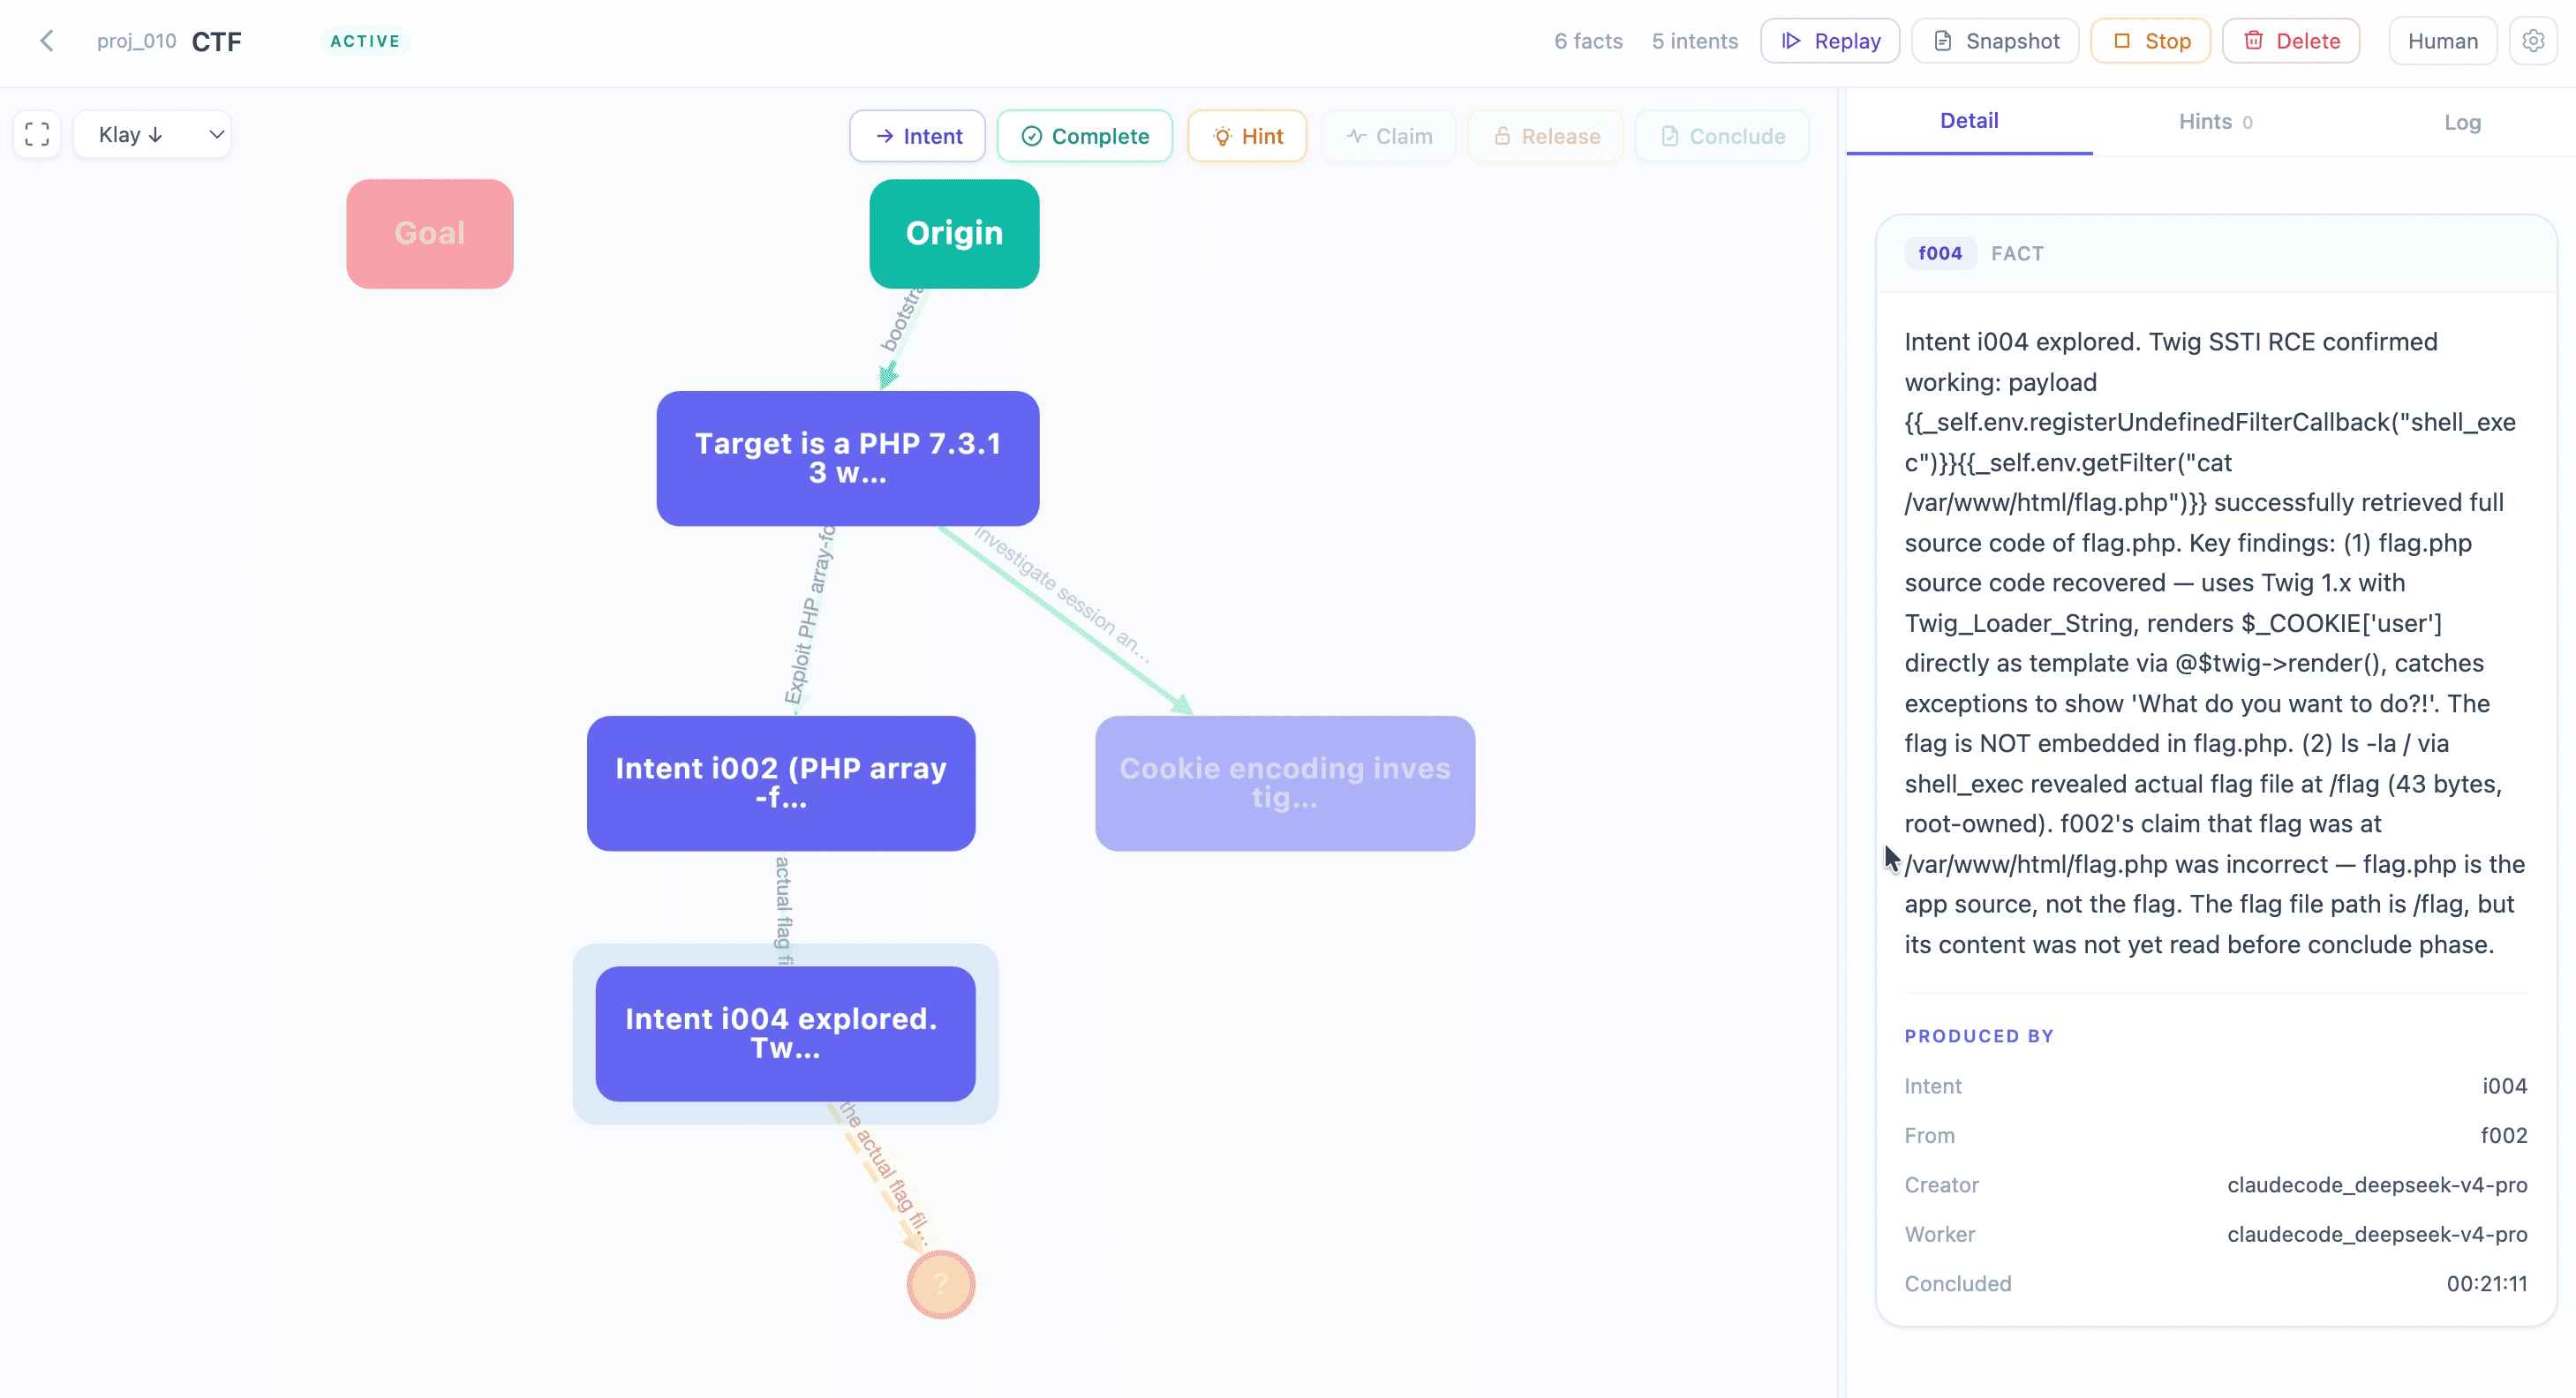 oritera/cairn
LLM-driven state-space search engine for autonomous penetration testing, CTF solving, and vulnerability research. Uses blackboard architecture with…
 user1342/awesome-android-reverse-engineering
A curated list of awesome Android Reverse Engineering training, resources, and tools.
 b4sith-sec/gu3ssweak
Deliberately vulnerable Android app for mobile security research and bug bounty practice - OWASP Mobile Top 10
 rufflabs/ludus_crushftp_cve-2025-31161_sim
Ansible role that simulates a realistic CrushFTP CVE-2025-31161 exploitation scenario with rotating sensitive data files and automated defender…