

awesome-ctf
 apsdehal/awesome-ctf
A curated list of CTF frameworks, libraries, resources and softwares
cryptographyctfcurated-resources+7
apsdehal/awesome-ctfA curated list of CTF frameworks, libraries, resources and softwares
 jedisct1/cve-2025-65945-poc
PoC for CVE-2025-65945 (Improper Verification of Cryptographic Signature in node-jws)
 shreyas-challa/cve-2026-46395-haxcms-hmac-key-leak
PoC and writeup for CVE-2026-46395: unauthenticated private key disclosure via broken HMAC in HAXcms Node.js (CWE-321/CWE-200). Authorized security…
 c0gnit00/cve-2026-29000
Python POC, Exploit for CVE-2026-29000
 mostafasoliman/oracle-oam-padding-oracle-cve-2018-2879-exploit
Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…
 compasssecurity/samlraider
SAML2 Burp Extension
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 davwwwx/cve-2022-21449
repo showcasing generating "psychic signatures for java" implemented in a nodejs environment 😅
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
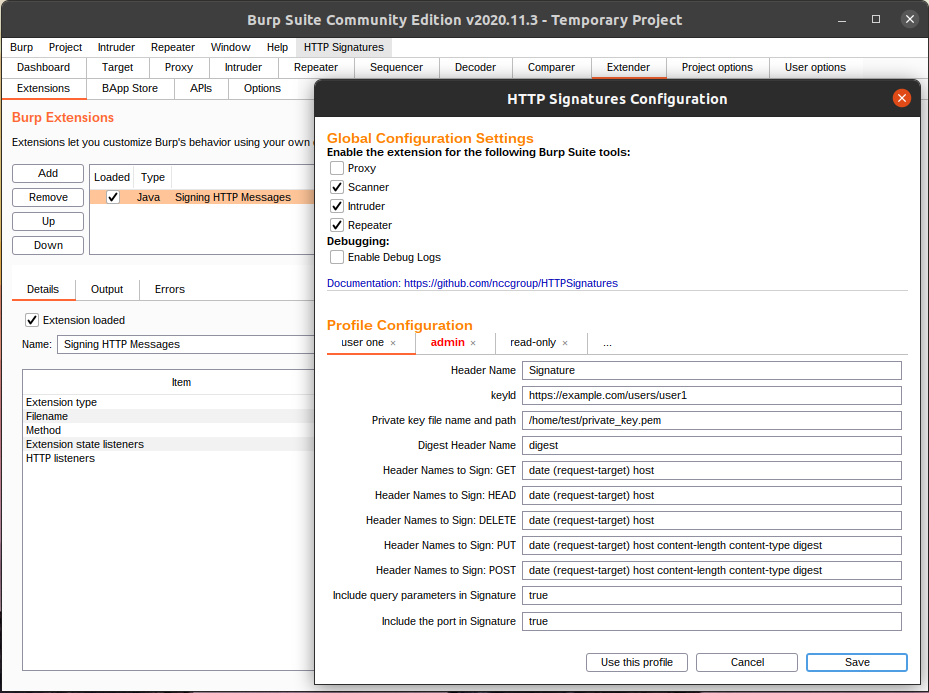 nccgroup/httpsignatures
A Burp Suite extension implementing the Signing HTTP Messages draft-ietf-httpbis-message-signatures-01 draft.
 zilbonn/owasp-wstg-rag
OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
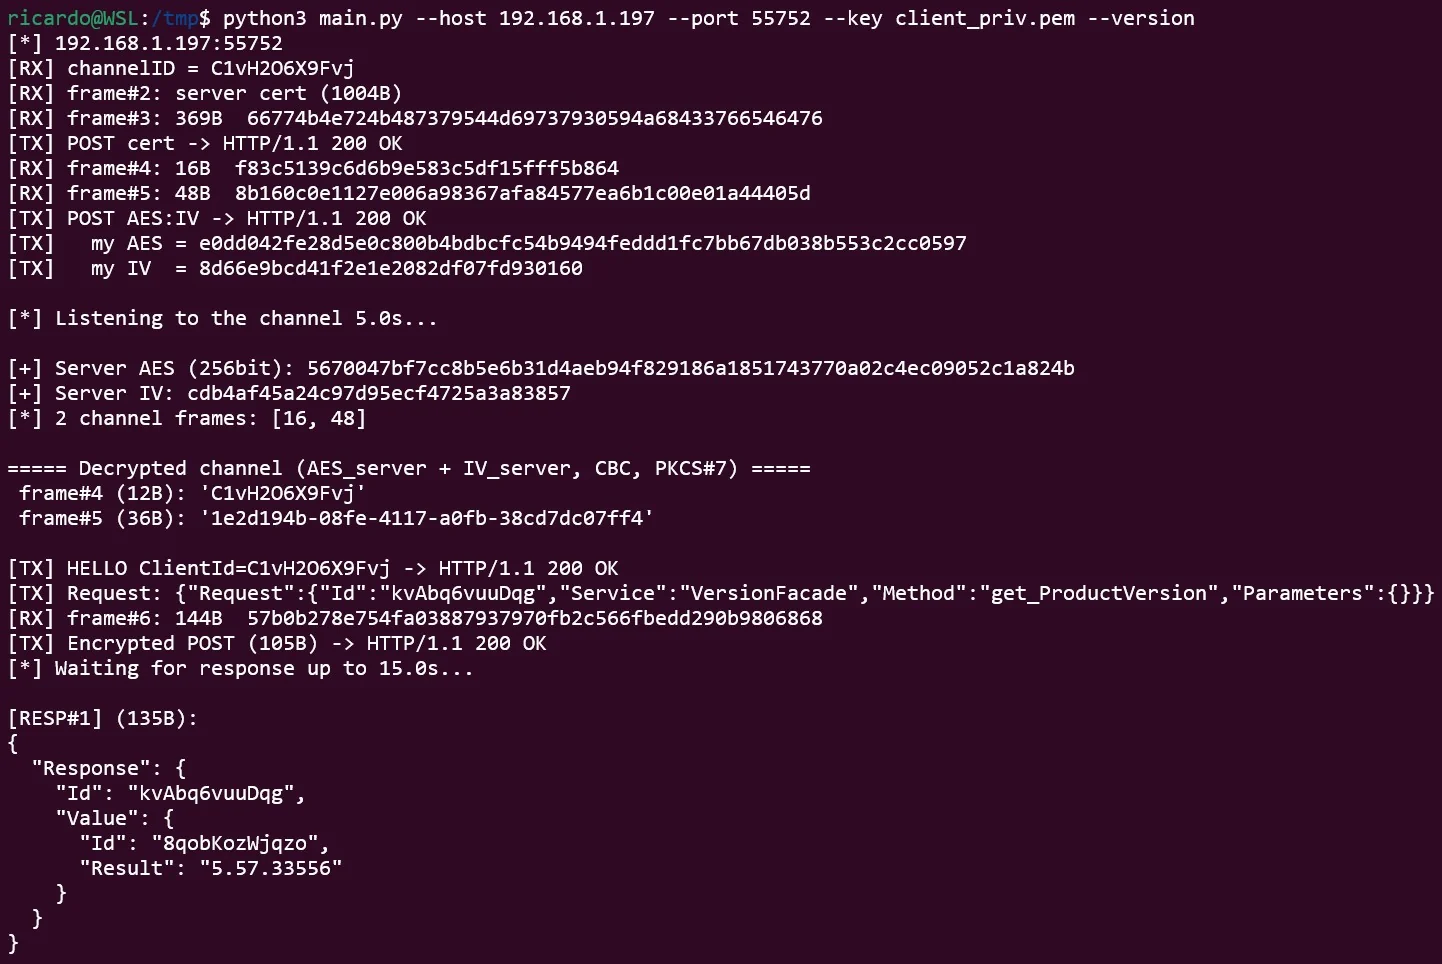 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 trailofbits/testing-handbook
Trail of Bits Testing Handbook - appsec.guide
 p1ckzi/cve-2022-35513
CVE-2022-35513 | blink1-pass-decrypt
 codingo/minesweeper
A Burpsuite plugin (BApp) to aid in the detection of scripts being loaded from over 23000 malicious cryptocurrency mining domains (cryptojacking).