
cve-2026-105221-gist-tls
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
cryptographyexploitationlabs-practice+4
abraxas/cve-2026-105221-gist-tlsCVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 wvllxe/cve-2026-104356-pictshare-weak-delete-code
Predictable delete_code via rand() in PictShare < 3.7.1 (CWE-338). PoC + advisory writeup.
 covepseng/cve-2026-102268-poc
Exploitability PoC for CVE-2026-102-268 (PyJWT Asymmetric-PEM detection bypass).
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 fkie-cad/sandroid_dexray-intercept
A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…
 minanagehsalalma/zte-smartlife-app-pwned
ZTE SmartLife security findings leading to account takeover: 100K+ Google Play downloads and CVE-2026-86552 through CVE-2026-86555.
 abraxas/cve-2026-13447
Proof-of-concept exploit for CVE-2026-13447, a critical authentication bypass in the WordPress MStore API plugin via forged Firebase JWT tokens, with…
 isaca0315/cve-2026-44351-poc
Proof-of-concept for CVE-2026-44351, an authentication bypass in fast-jwt <6.2.4 where an empty HMAC key lets attackers forge arbitrary JWTs accepted…
 freire007-byte/sentric-core
Autonomous AI agent with its own crypto identity — hunts CVEs, builds exploit labs, validates vulnerabilities (first public PoC of CVE-2026-86283),…
 tori-tech/mandating-honeypots-project
This repository conducts security audits on digital identity verification systems, identifies vulnerabilities through whitepapers and technical POCs,…
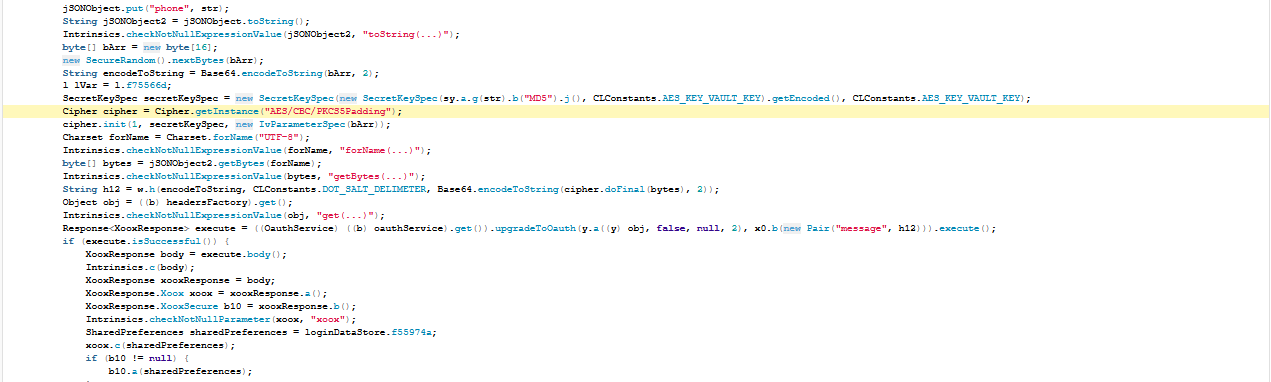 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 threedr3am/learnjavabug
Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…
 priyanshu-rawa/cybersecurity-handbook
Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.
 george0papasotiriou/cve-2026-11119-padding-oracle-attack-on-cbc-mode-encryption
Demonstrates a padding oracle attack against AES-CBC encryption using a vulnerable Flask decrypt endpoint and a Python exploit script to decrypt…
 phith0n/collision-webshell
A webshell and a normal file that have the same MD5
 azureadtrent/cve-2026-52824
Technical analysis and PoC of CVE-2026-52824: default APP_SECRET in the Kimai Docker image enabling unauthenticated login link forgery. Affects <=…