
IDAChef
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
binary-analysiscode-analysiscryptography+6
18
exporx/idachefCyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 jschauma/emudhra
Example programs in Go, Java, Node, Perl, Python, Ruby, Rust, and curl that test whether a TLS trust store rejects connections to known-bad eMudhra…
 firmianay/ctf-all-in-one
Open-source CTF guidebook covering Pwn, reverse engineering, and web security, with structured chapters, worked examples, and tooling setup for…
 ktekeli/audio-steganography-algorithms
Octave/MATLAB library of audio steganography and watermarking algorithms, including LSB coding, echo hiding, spread spectrum, and phase coding with…
 izcoser/stegpy
Simple steganography program based on the LSB method.
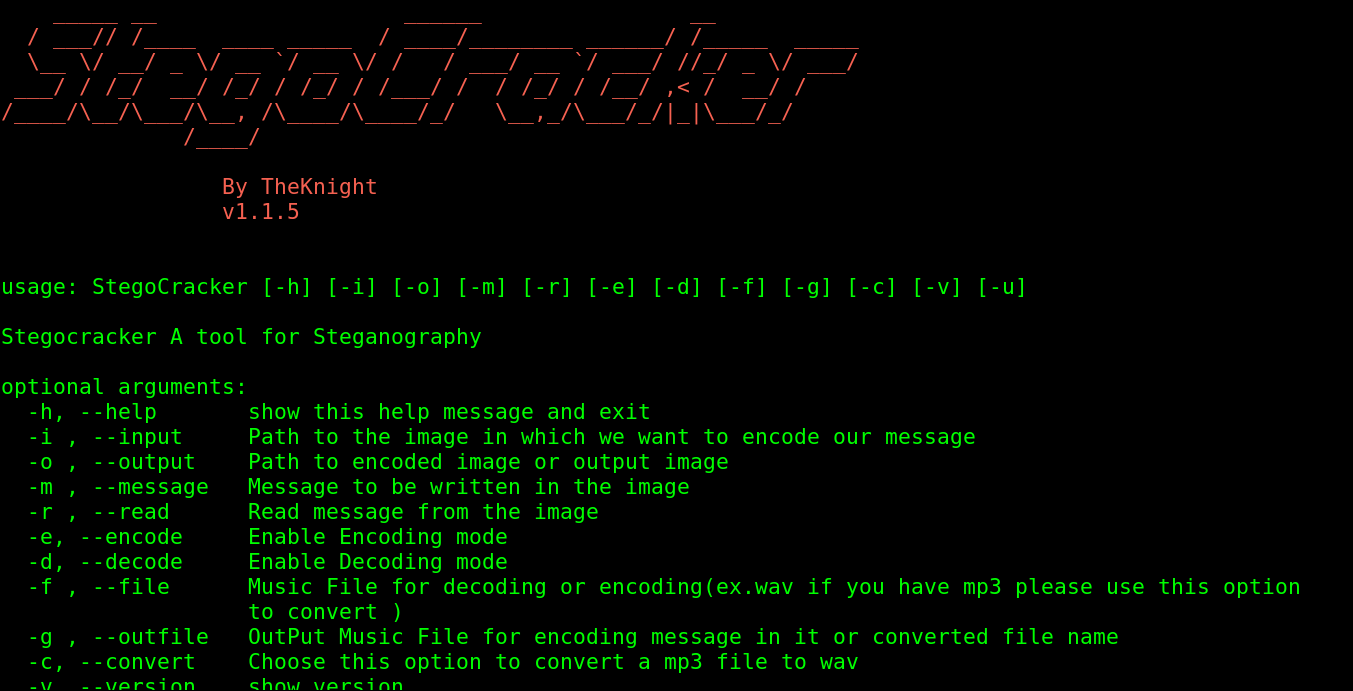 w1ldn16h7/stegocracker
Stego is an open-source and free steganography tool that lets you hide your secret message in an image or audio file. You will not notice any change…
 0xade1a1de/mastik
C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 0xajstrike/emsign-trust-scan
Offline scanner for the October 2026 eMudhra/emSign CA key compromise, finds affected certificates across OS trust stores, CA bundles, Java cacerts,…
 glen-testing/low-int-cert-monitor
Monitor Certificate Transparency logs for certificates with trivially small EC private keys (the eMudhra weak-key class). P-256/384/521.
 planners1490/sclock
Hardware-Bound 256-Slot Polymorphic VM, Non-Linear MBA & Apple Secure Enclave Binary Protector for macOS arm64 (Apple Silicon) — Public CrackMe & SDK…
 endrazine/rocq-cve-poc-21682
CVE-2026-72703 — Rocq Guard Checker Accepts Non-Terminating Fixpoint via Unchecked Cross-Calls
 neitzert/picard
Protocol-Introspecting Chunk Adapter for Resilient Data
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…

 ritwick7/sudostamp
Approve sudo on a Linux workstation with a fingerprint on your Android phone. LAN only; the ECDSA key never leaves the phone's TEE and speaks the…
 crypto-unict/ghostfacempc
Reference implementation of privacy-preserving face recognition using replicated secret sharing in MP-SPDZ, with quantized GhostFaceNet inference,…
 oscerd/cve-2026-85296
Runnable Spring Boot and Quarkus proof-of-concept reproducing CVE-2026-85296, a camel-as2 cross-partner MDN signing key confusion (CWE-488), with…
 oscerd/cve-2026-85300
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85300, demonstrating camel-pqc writing private keys with permissive umask-derived file…