

glimmer
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
command-and-controlcryptographydata-exfiltration+8
44 months ago
linnemanlabs/glimmerAdversary emulation and C2 framework for security research
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 v-pun215/tourmaline
Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
 demon-i386/zoshrinkc2
DNS over HTTPS targeted malware (only runs once)
 naacbin/covenantdecryptor
Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…
 softdeadlock/voron-crypto
Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested
 zeoday/cobaltstrike4.5_cdf-1
cobaltstrike4.5版本破/解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等

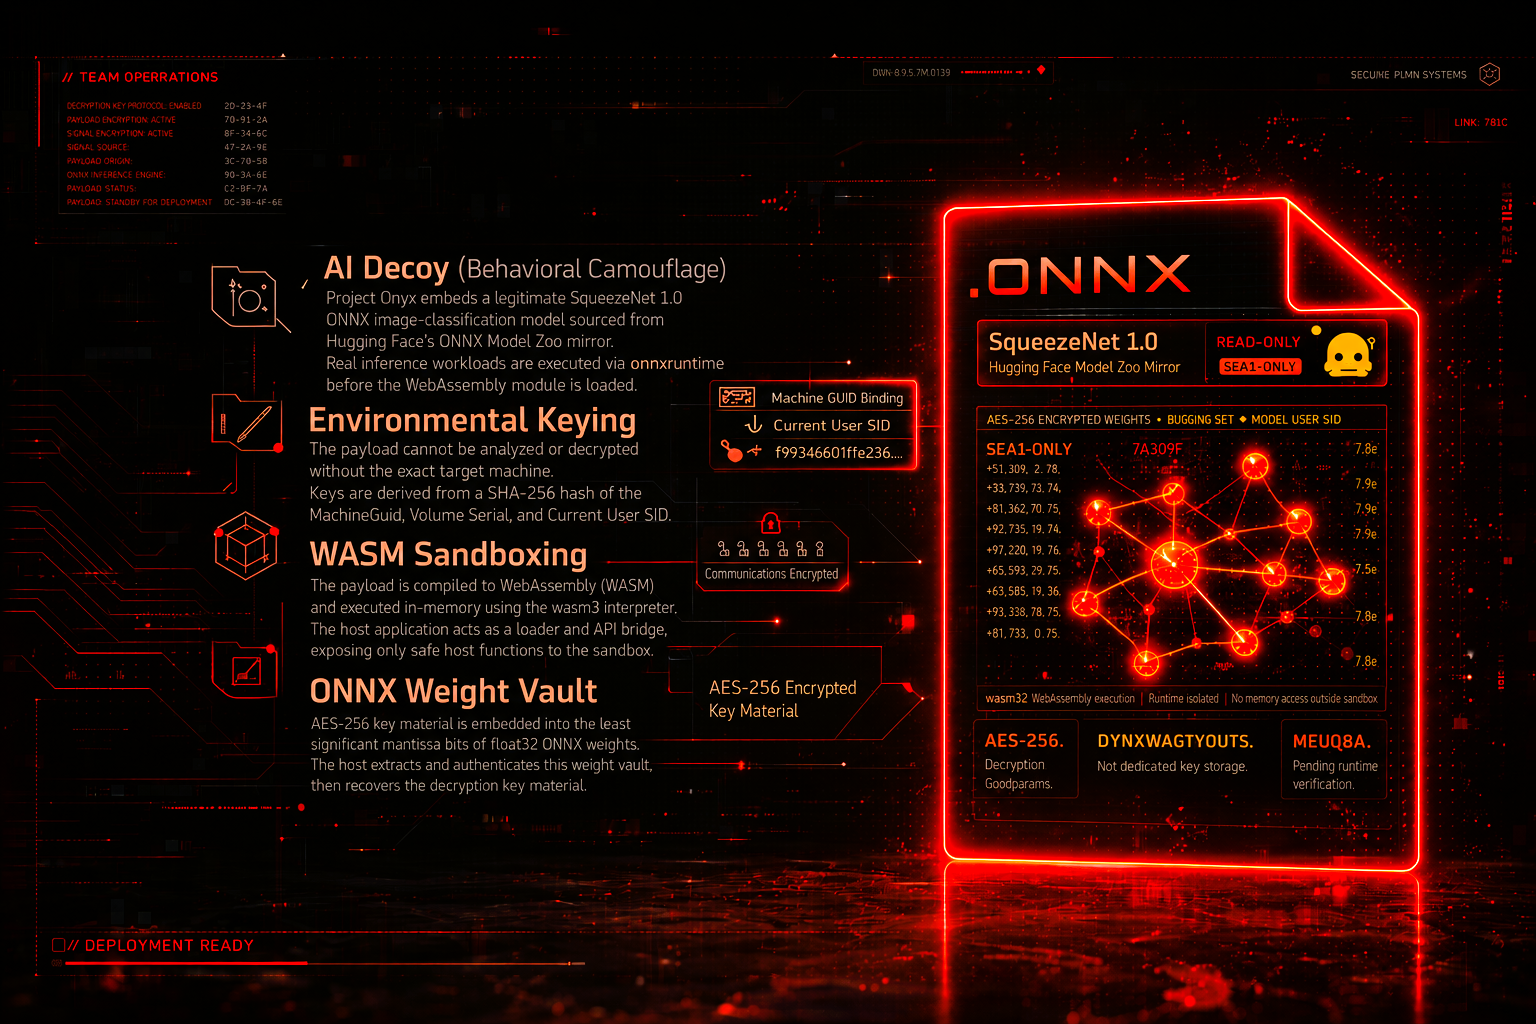 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 xyplex3/redteamcoin
Red Team Coin for crypto-mining operations.
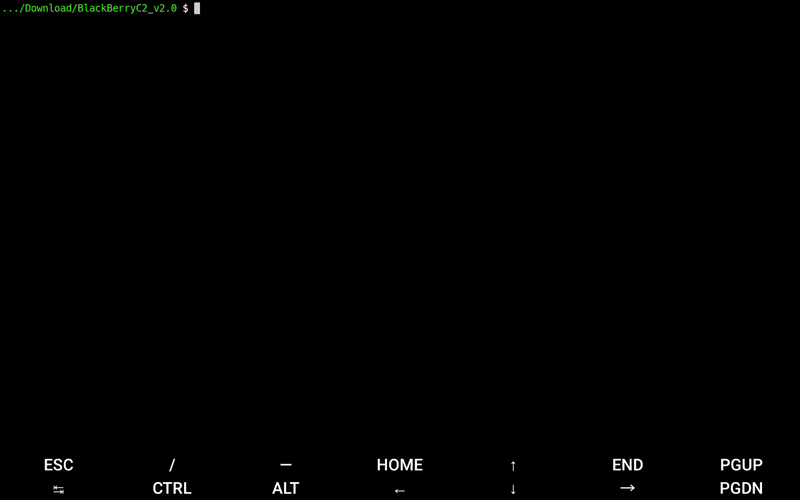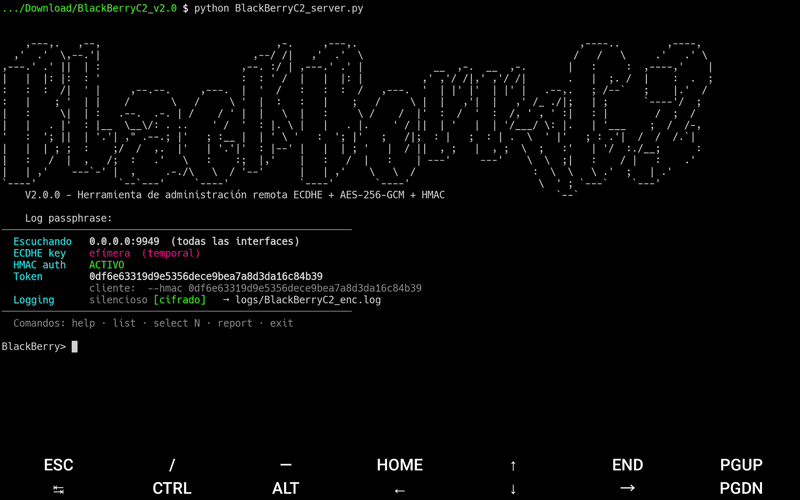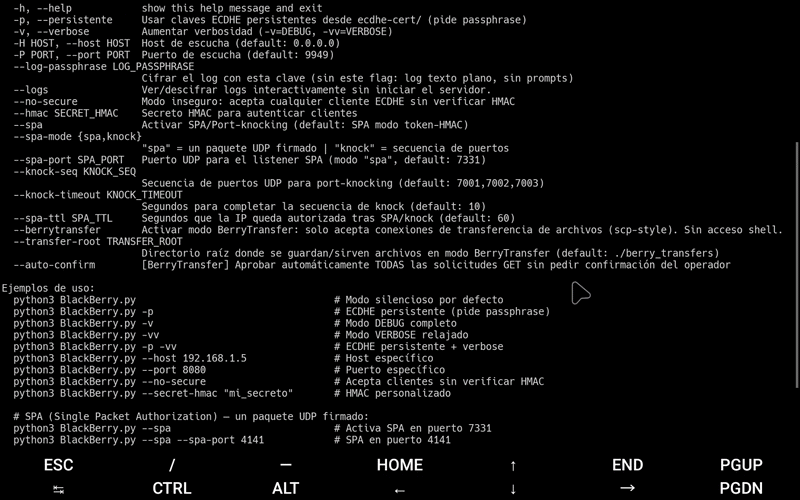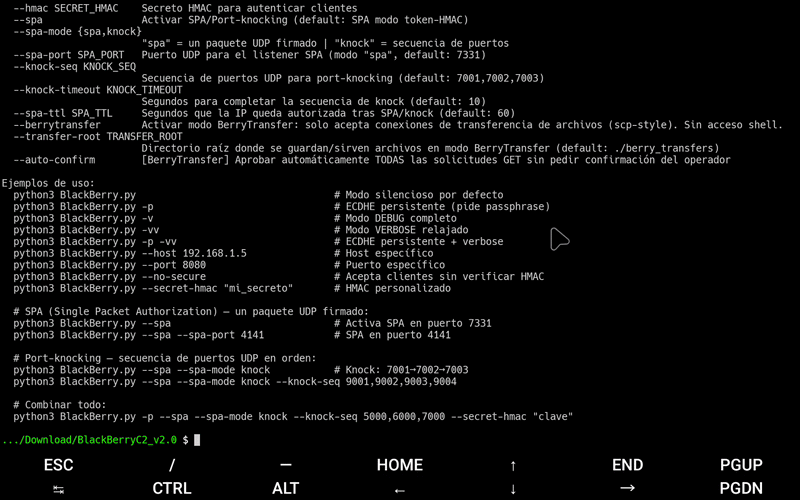 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 dereeqw/bitlock-crypto-research
Framework de investigación sobre criptovirología avanzada. Implementación de Handshake ECDHE, cifrado autenticado AES-GCM y ejecución fileless en…
 redcode-labs/coldfire
Golang malware development library
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 jacopodl/pulsar
Data exfiltration and covert communication tool