
vmsan
 angelorc/vmsan
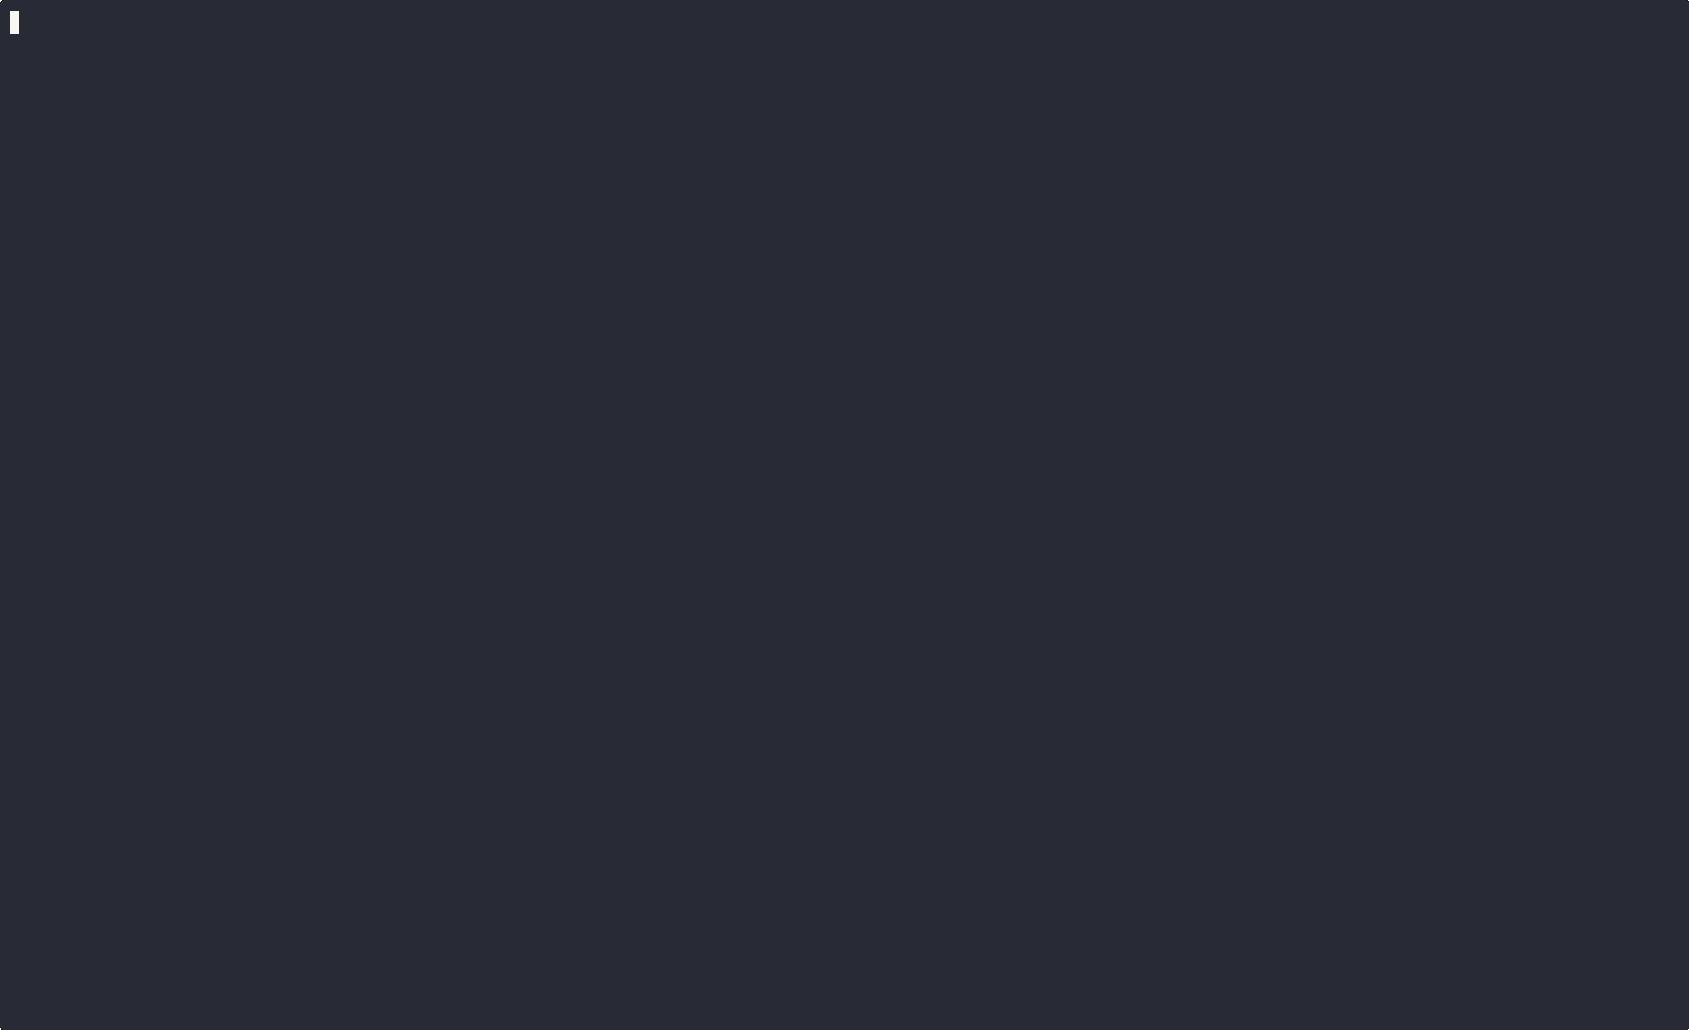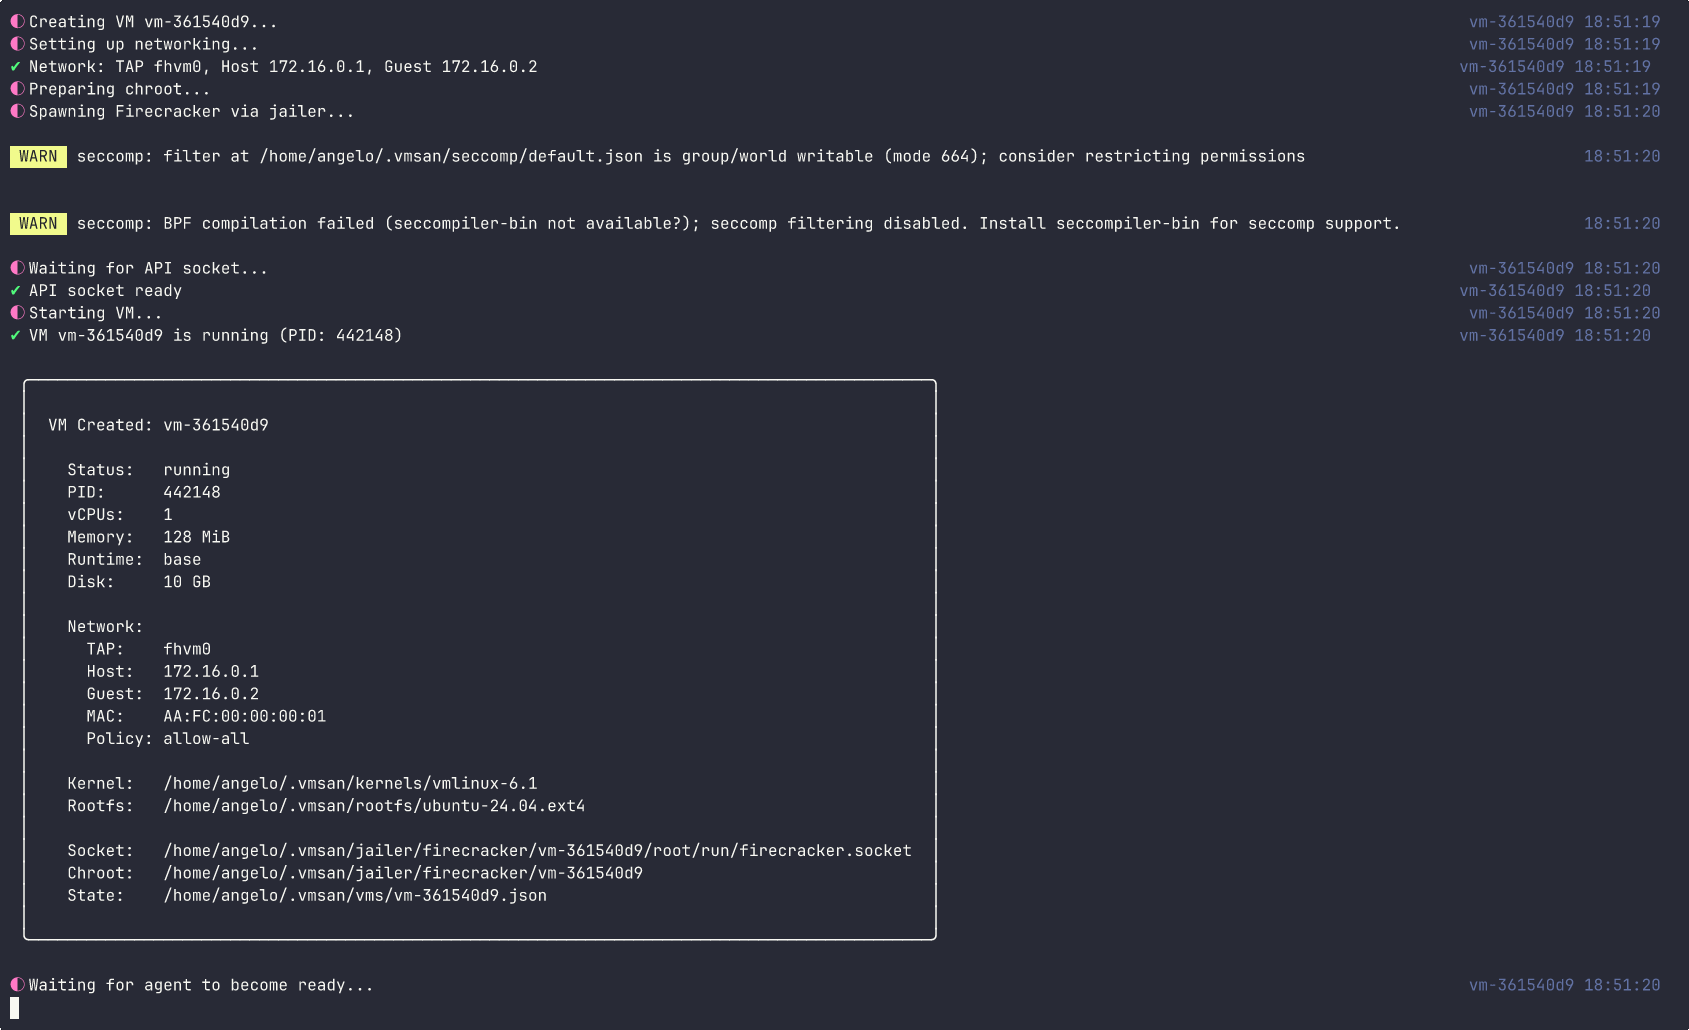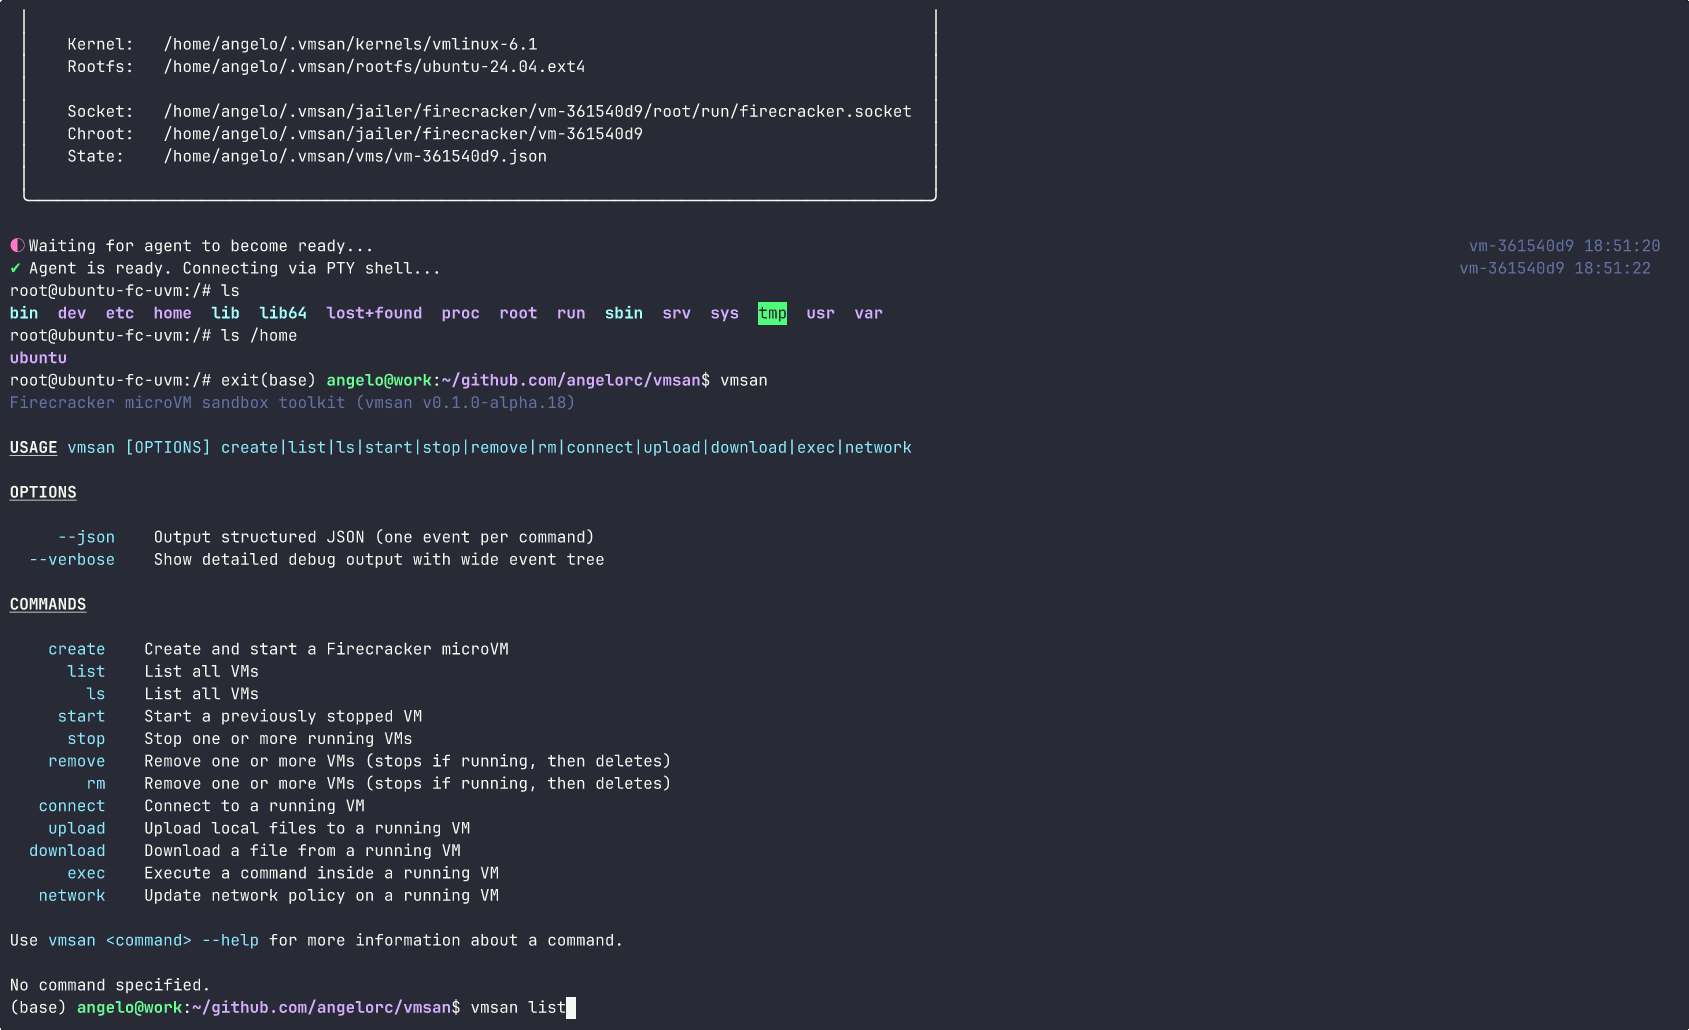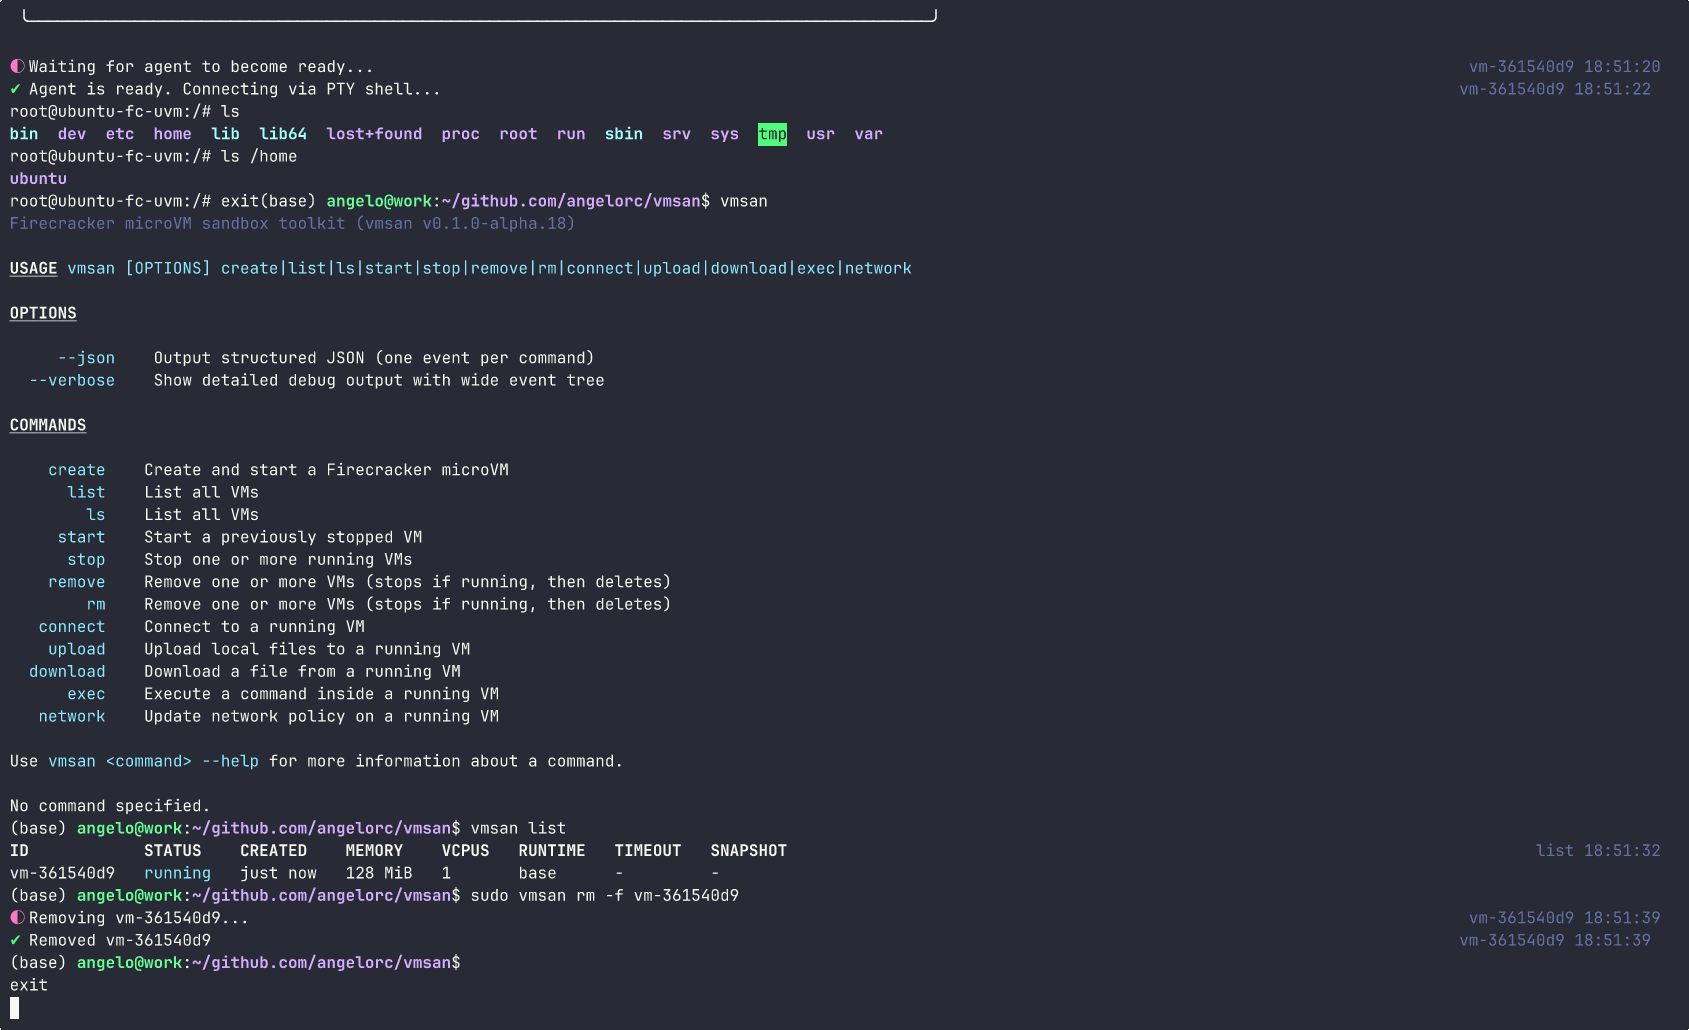
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
cloud-infrastructure-securitycontainer-securitydevsecops+3
84
angelorc/vmsanFirecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 srcporter/cve-2021-44228
DO NOT USE FOR ANYTHING REAL. Simple springboot sample app with vulnerability CVE-2021-44228 aka "Log4Shell"
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 spiarh/webhook-cve-2022-0811
Simple webhook to block exploitation of CVE-2022-0811
 weaveworks/weave-gitops
Weave GitOps is transitioning to a community driven project! It provides insights into your application deployments, and makes continuous delivery…
 optiopay/klar
Integration of Clair and Docker Registry
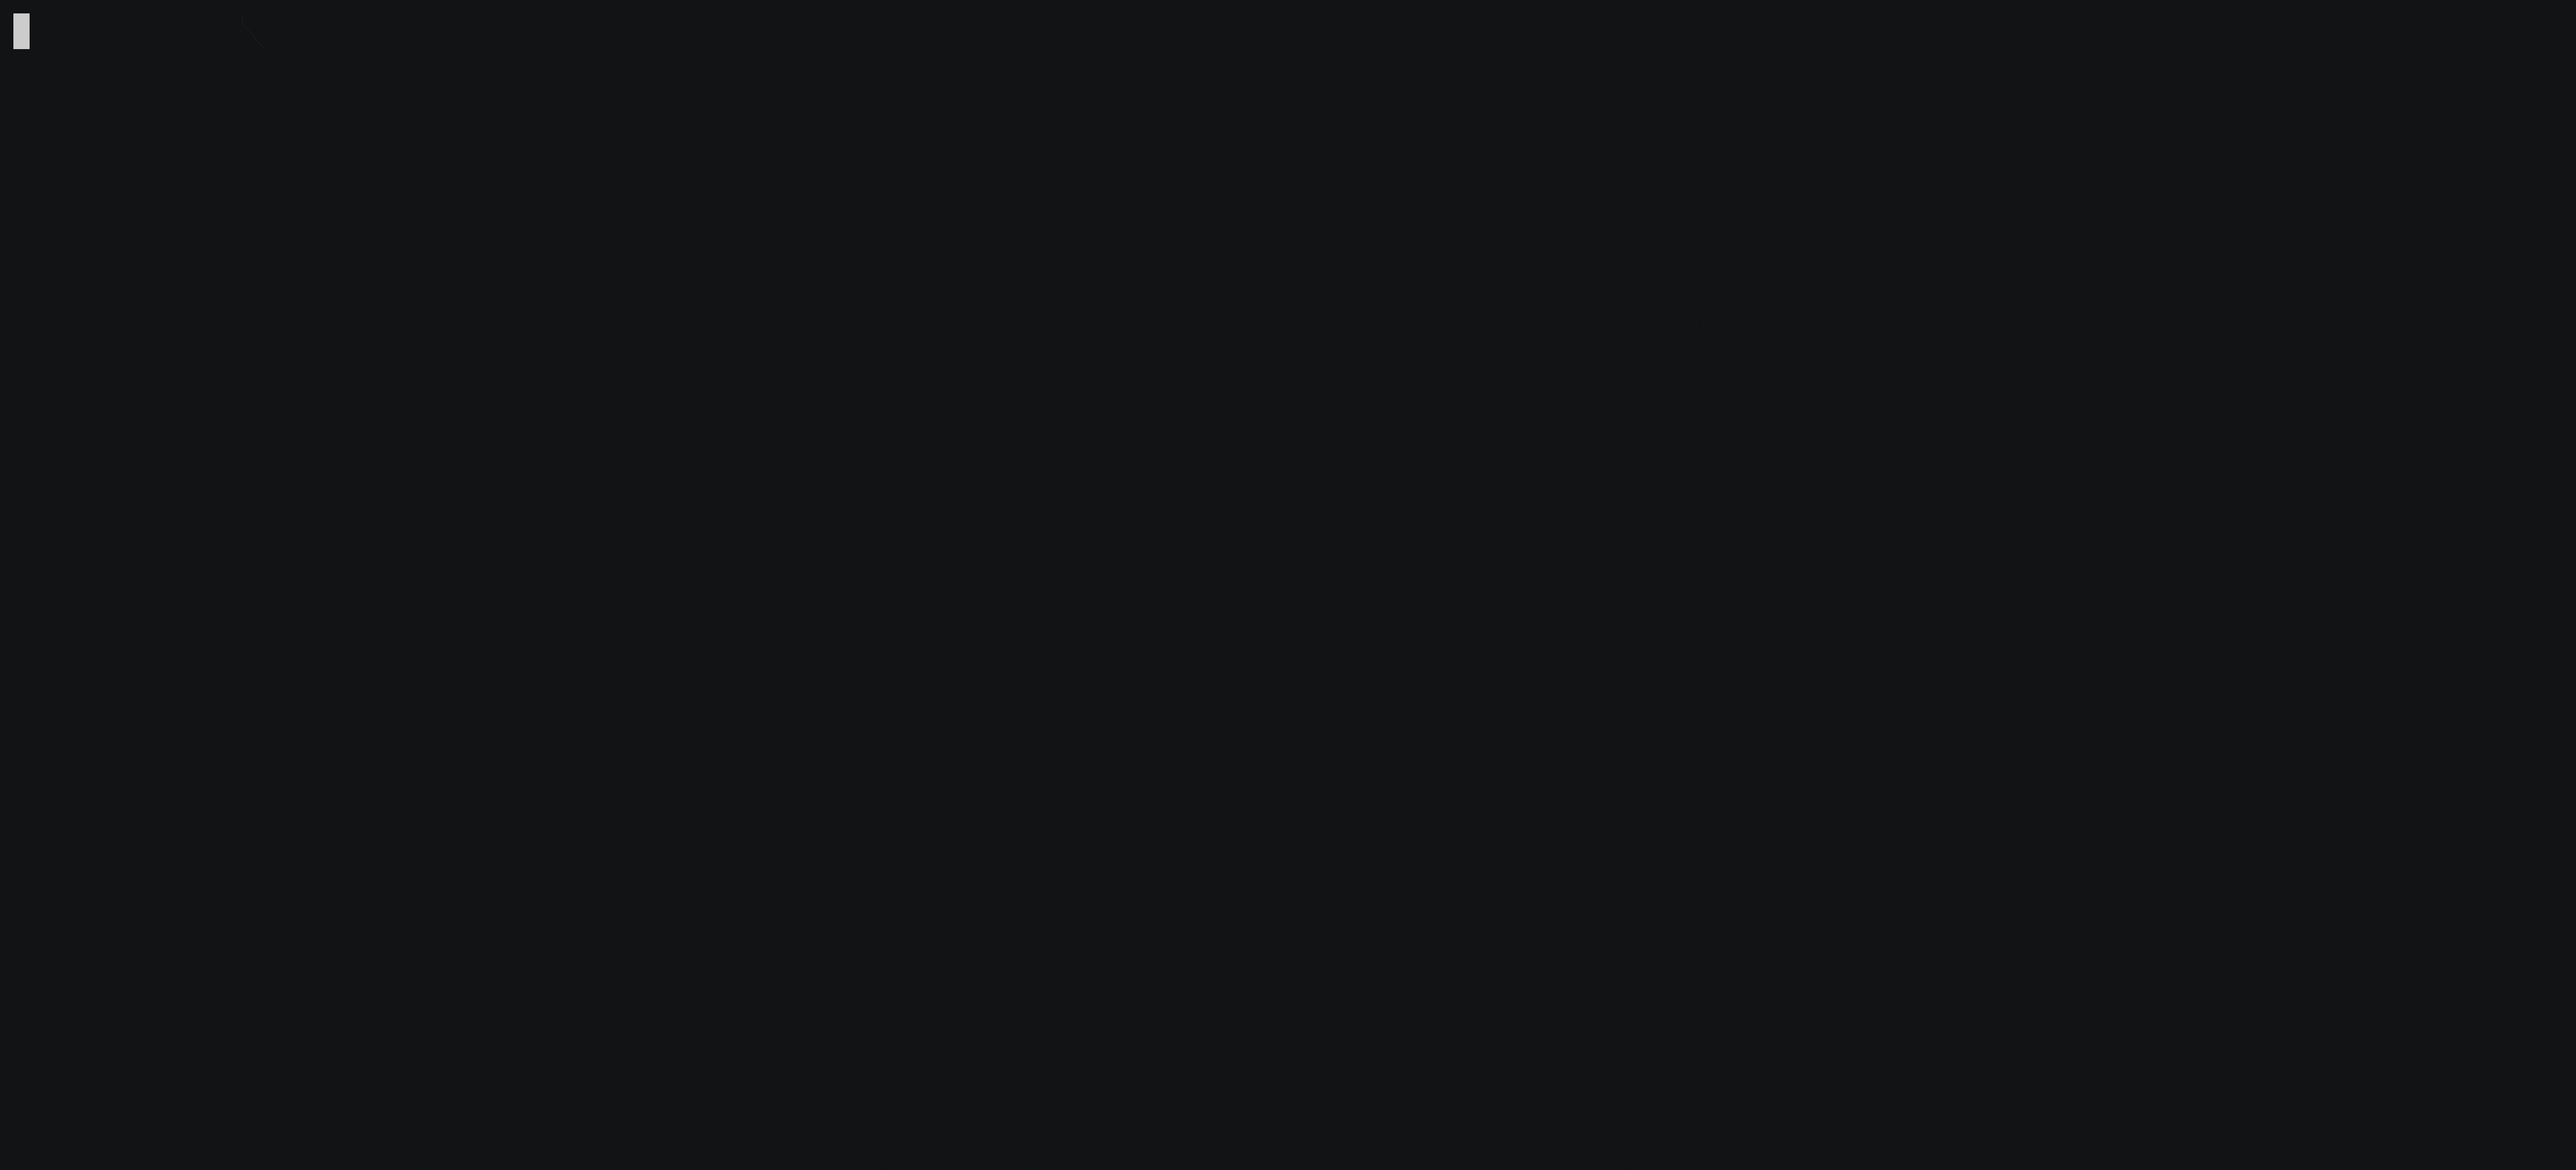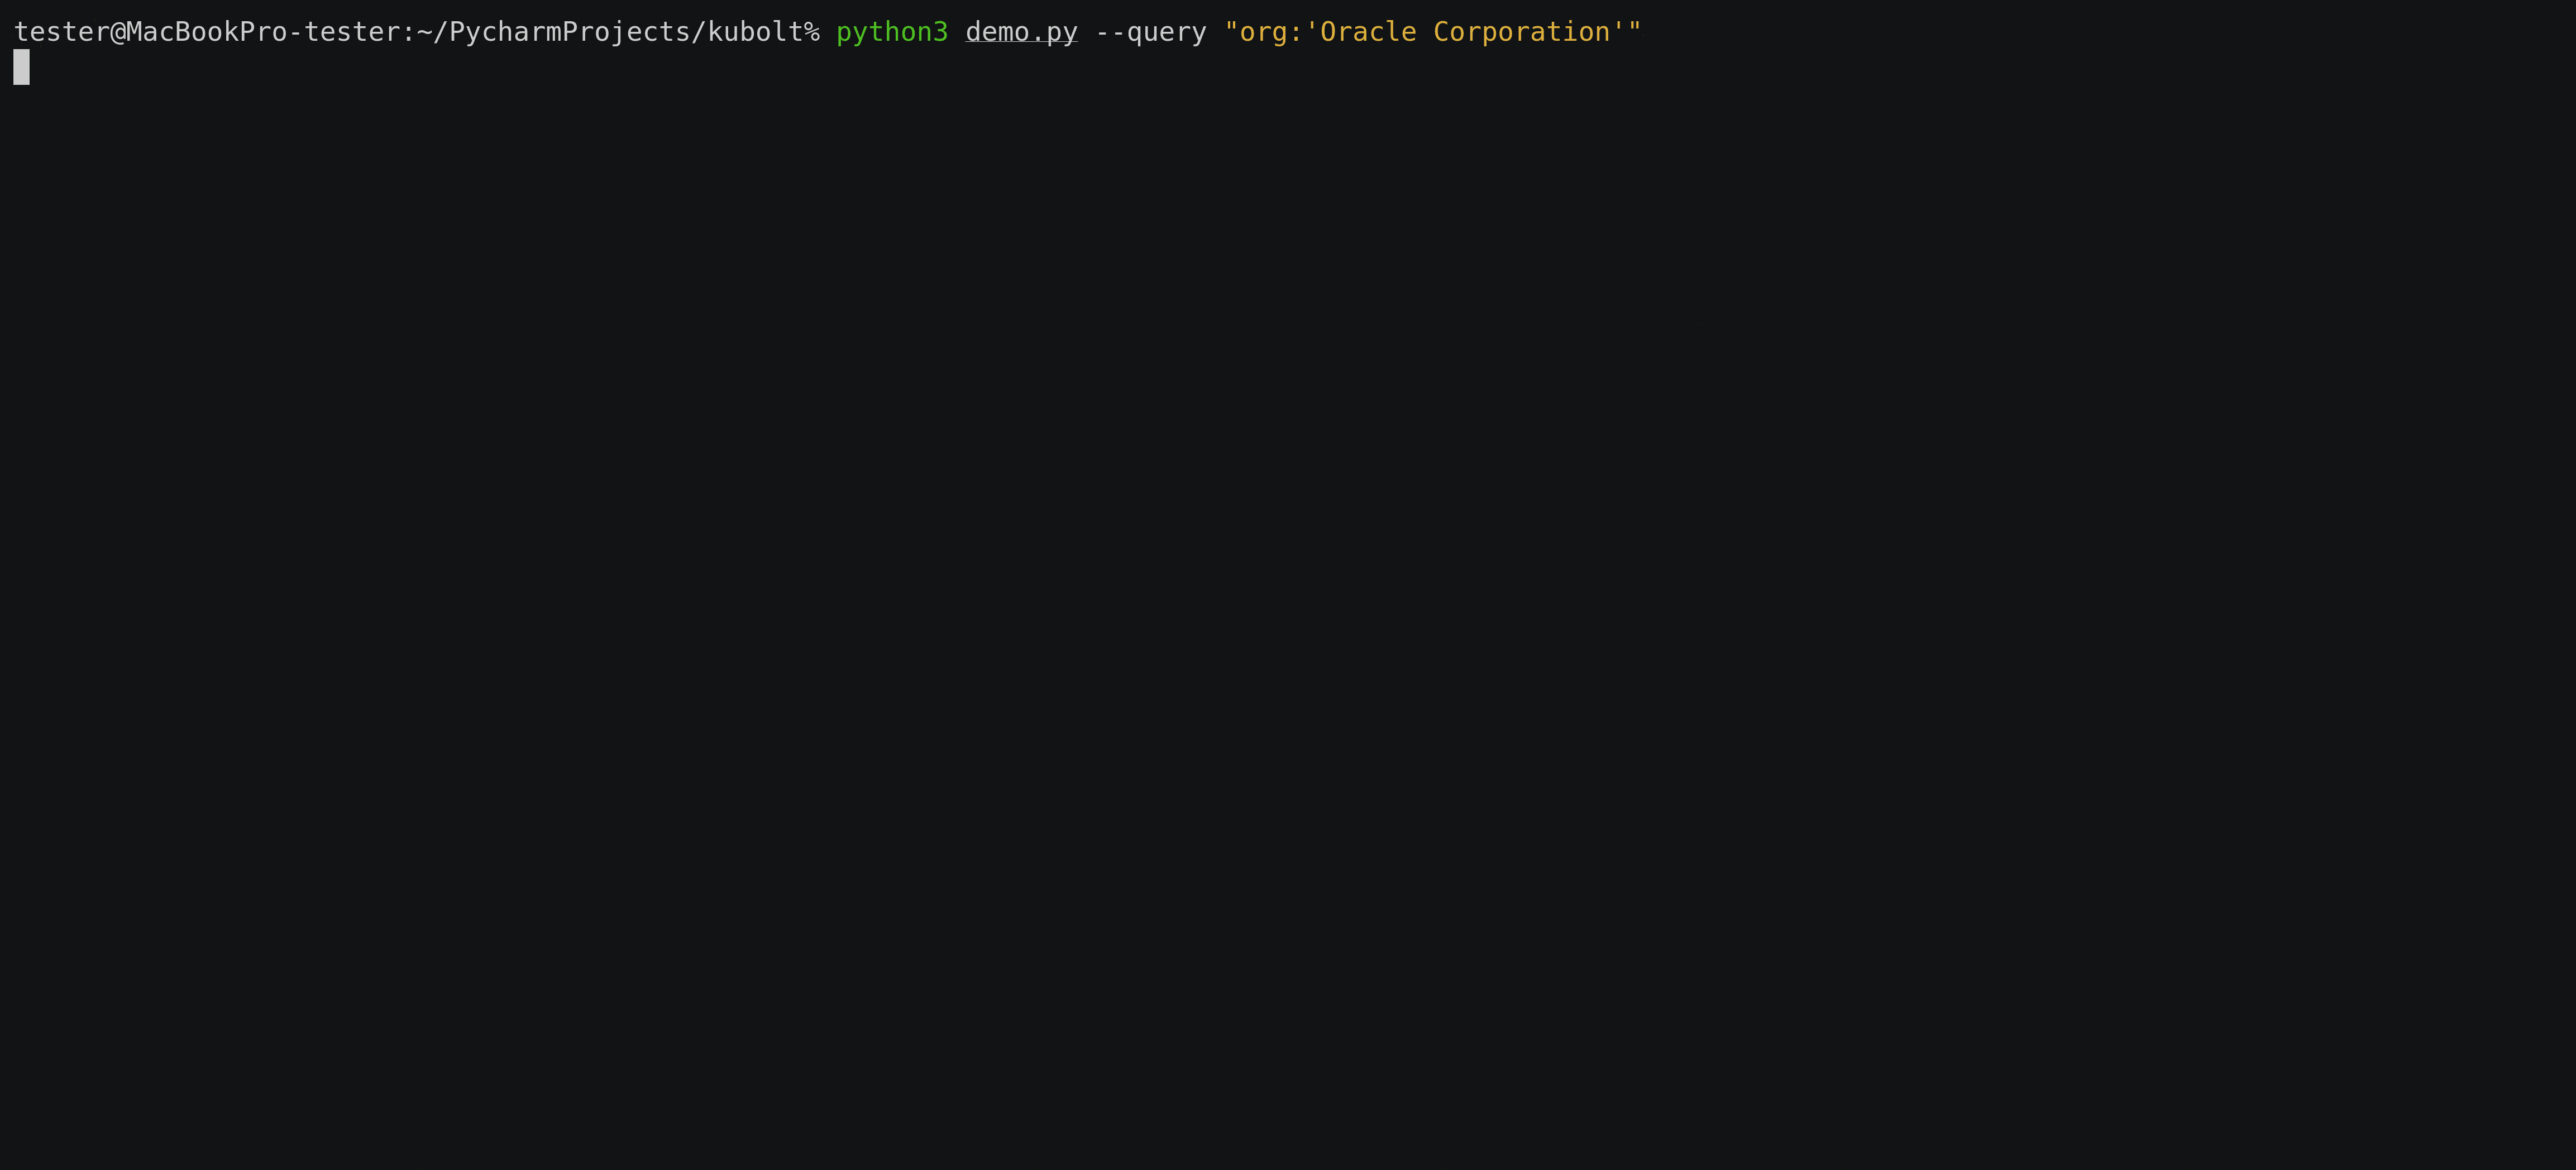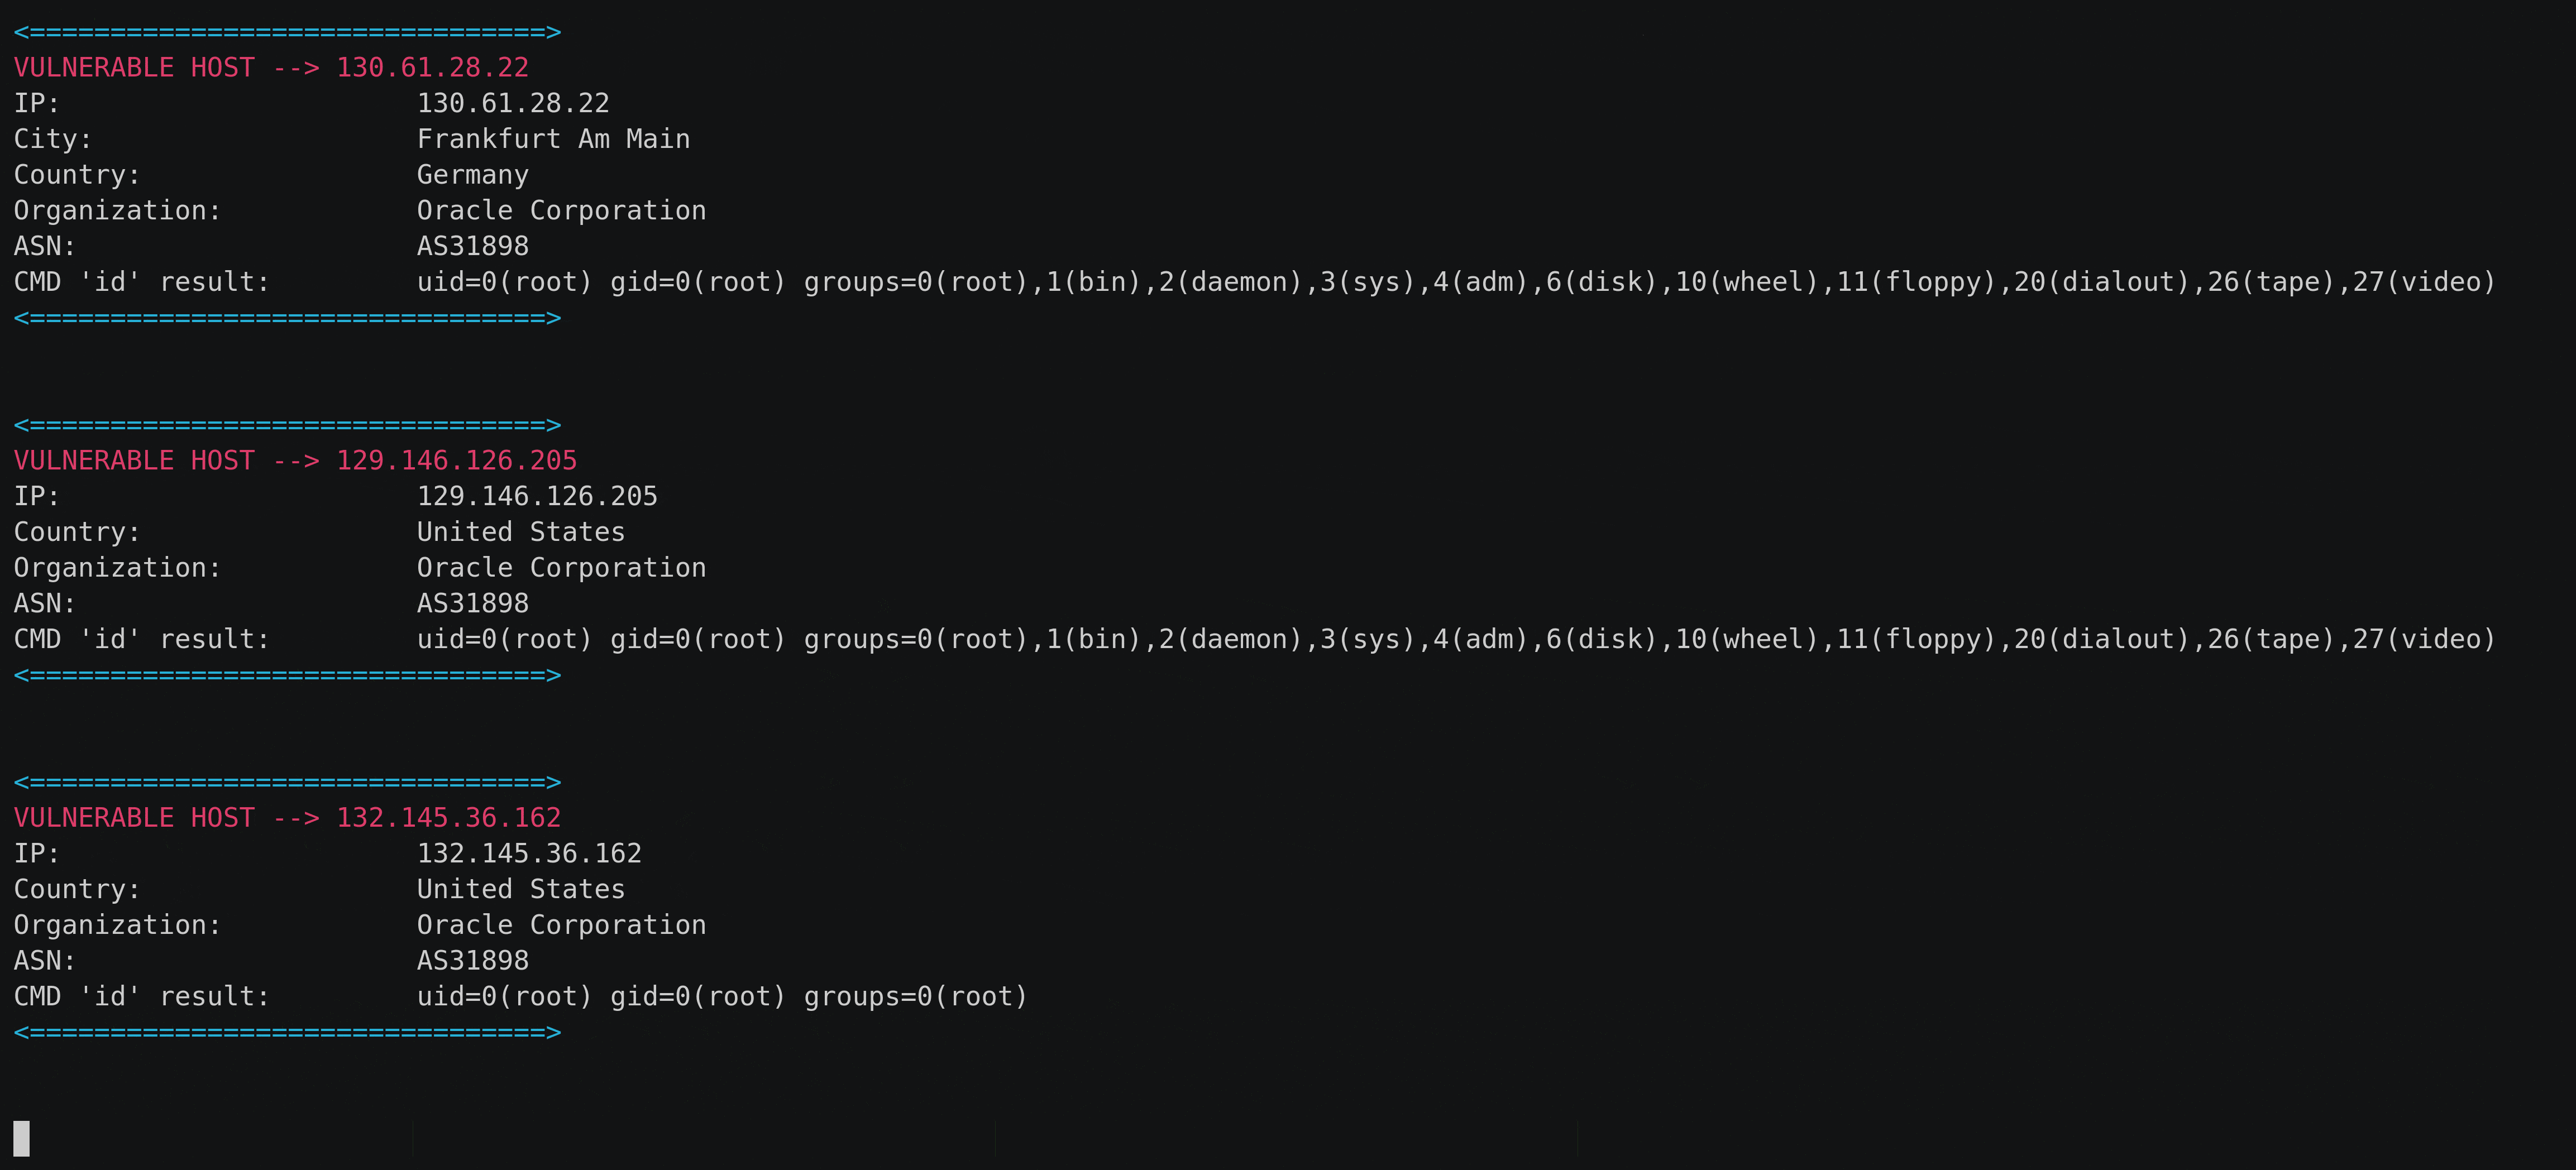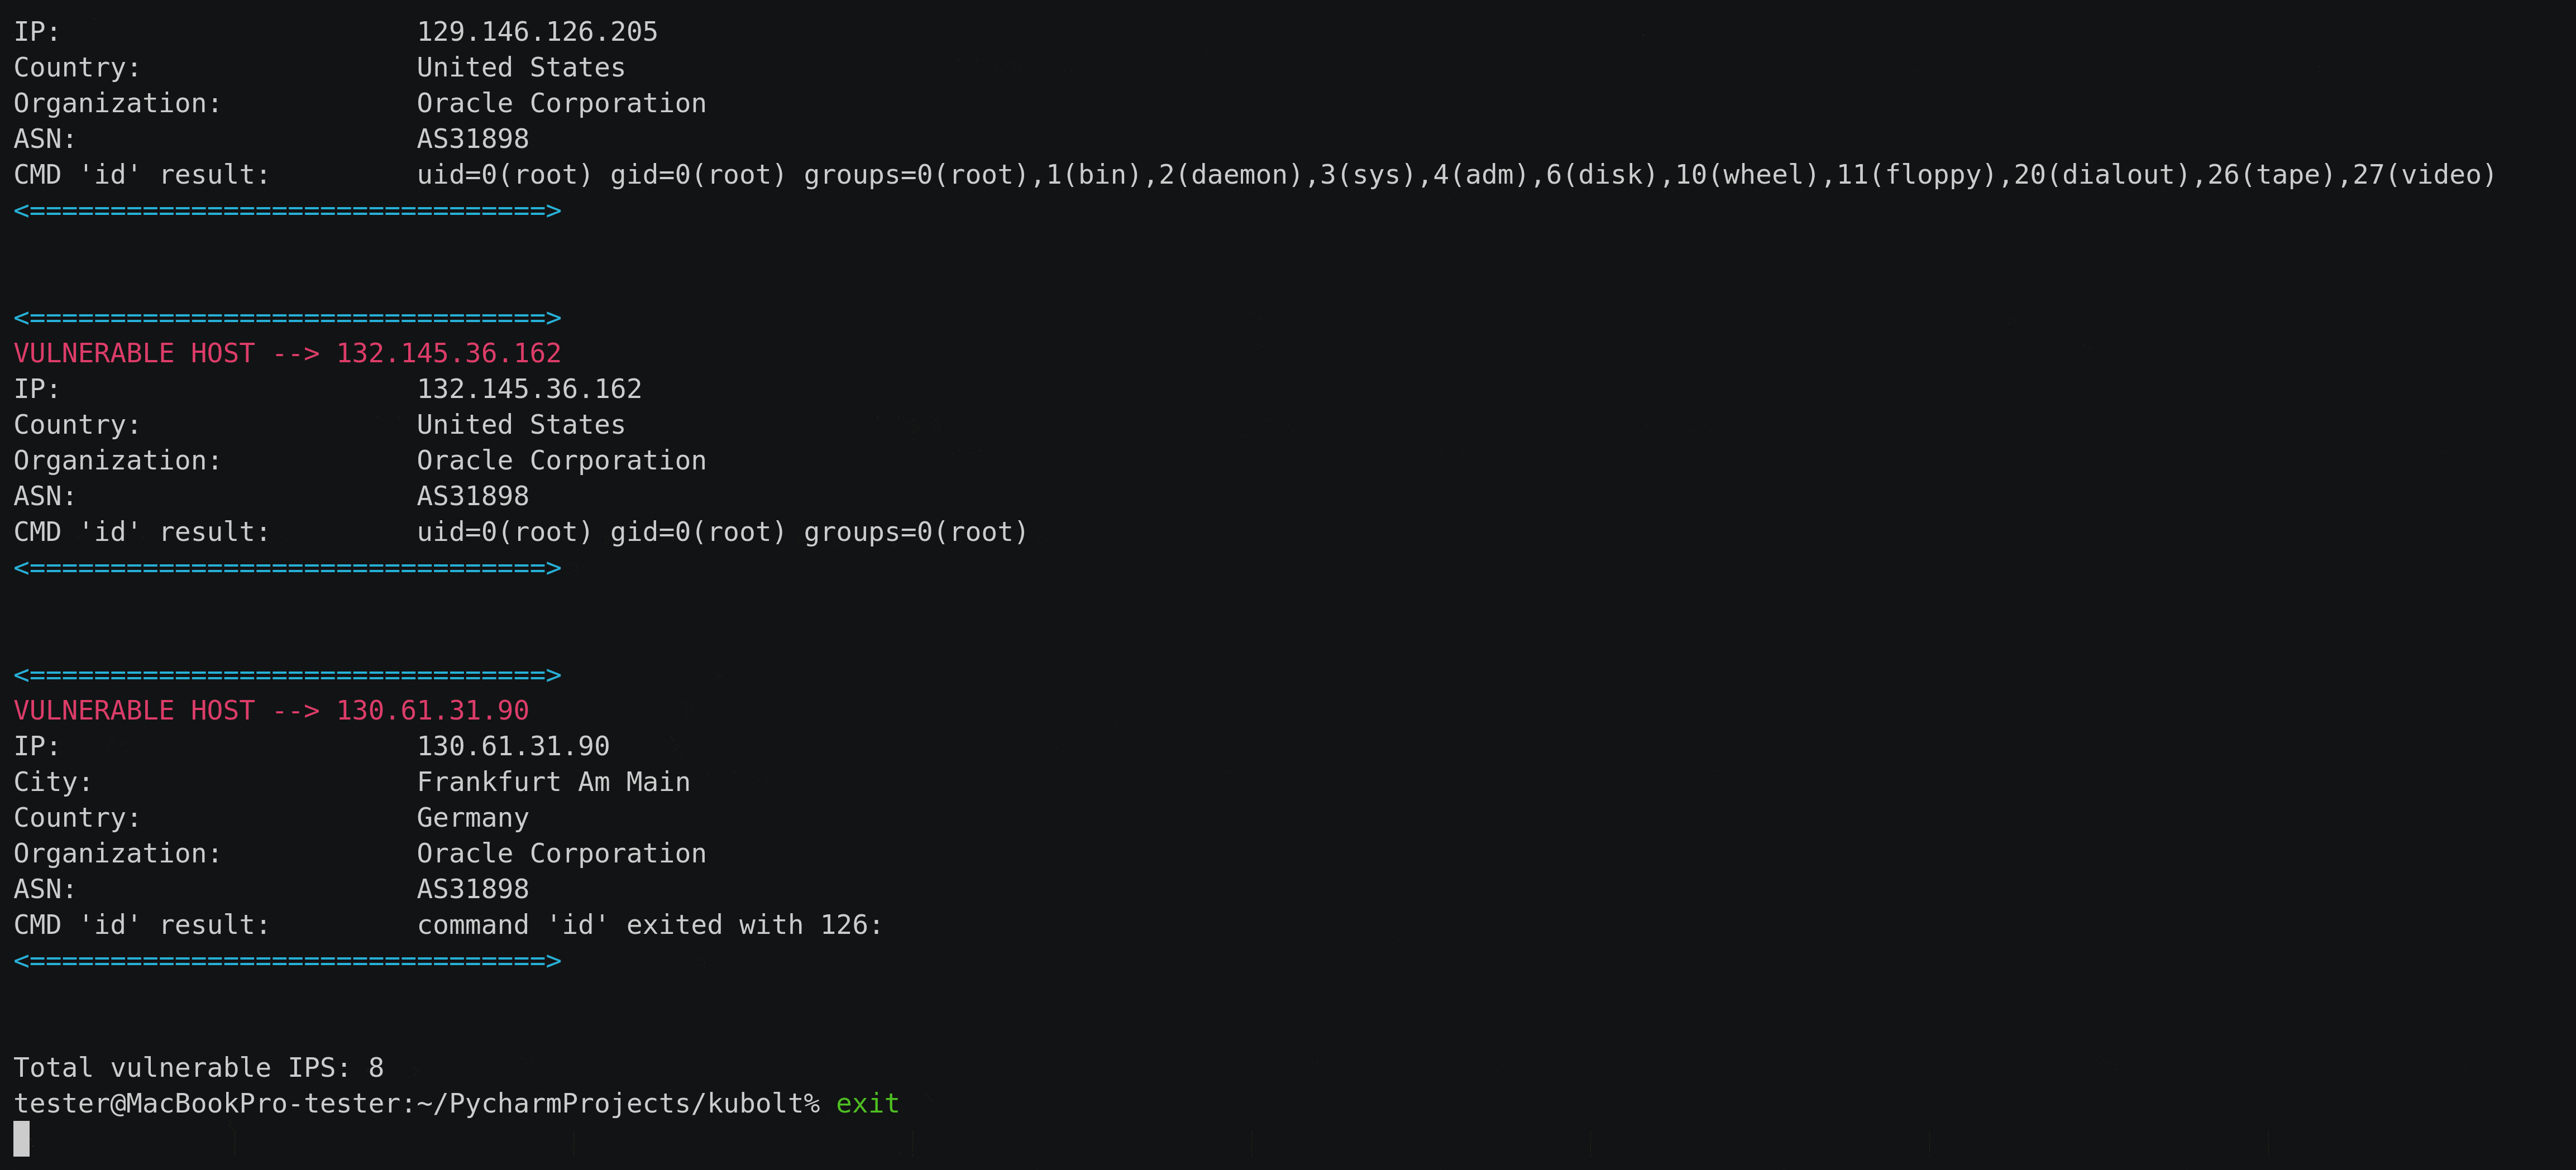 averonesis/kubolt
Kubolt utility for scanning public kubernetes clusters
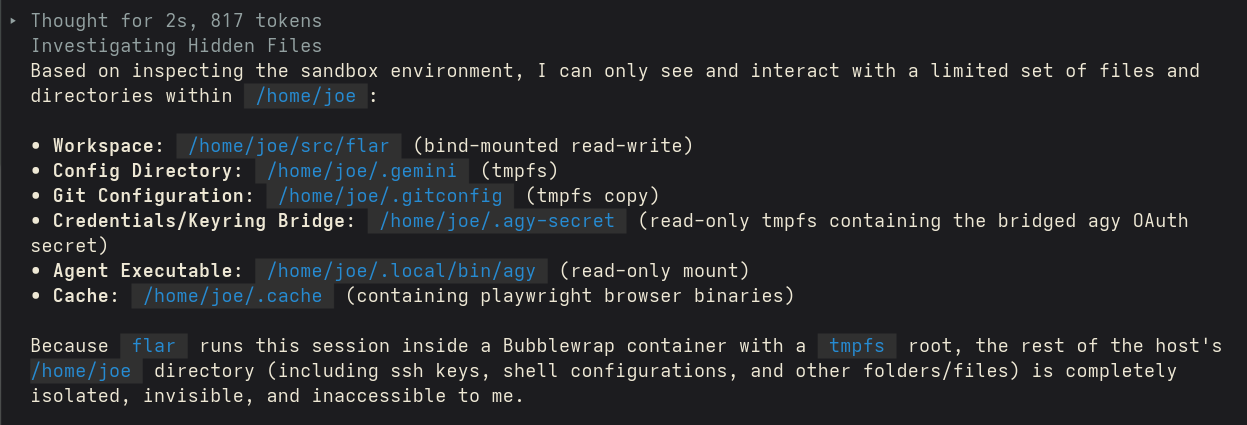 swelljoe/flar
Lightweight CLI tool that runs AI coding agents inside isolated Bubblewrap sandboxes with strict filesystem, network, and credential isolation to…
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 cyberhades/hardening-k8s-containers
Hands-on lab demonstrating Kubernetes container hardening by comparing default vs. security-enhanced deployments of a vulnerable note-taking…
 masahiro331/kube-trivy
Trivy for Kubernetes
 e-bounce/cve-2010-1622_learning_environment
cve-2010-1622 Learning Environment
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…