
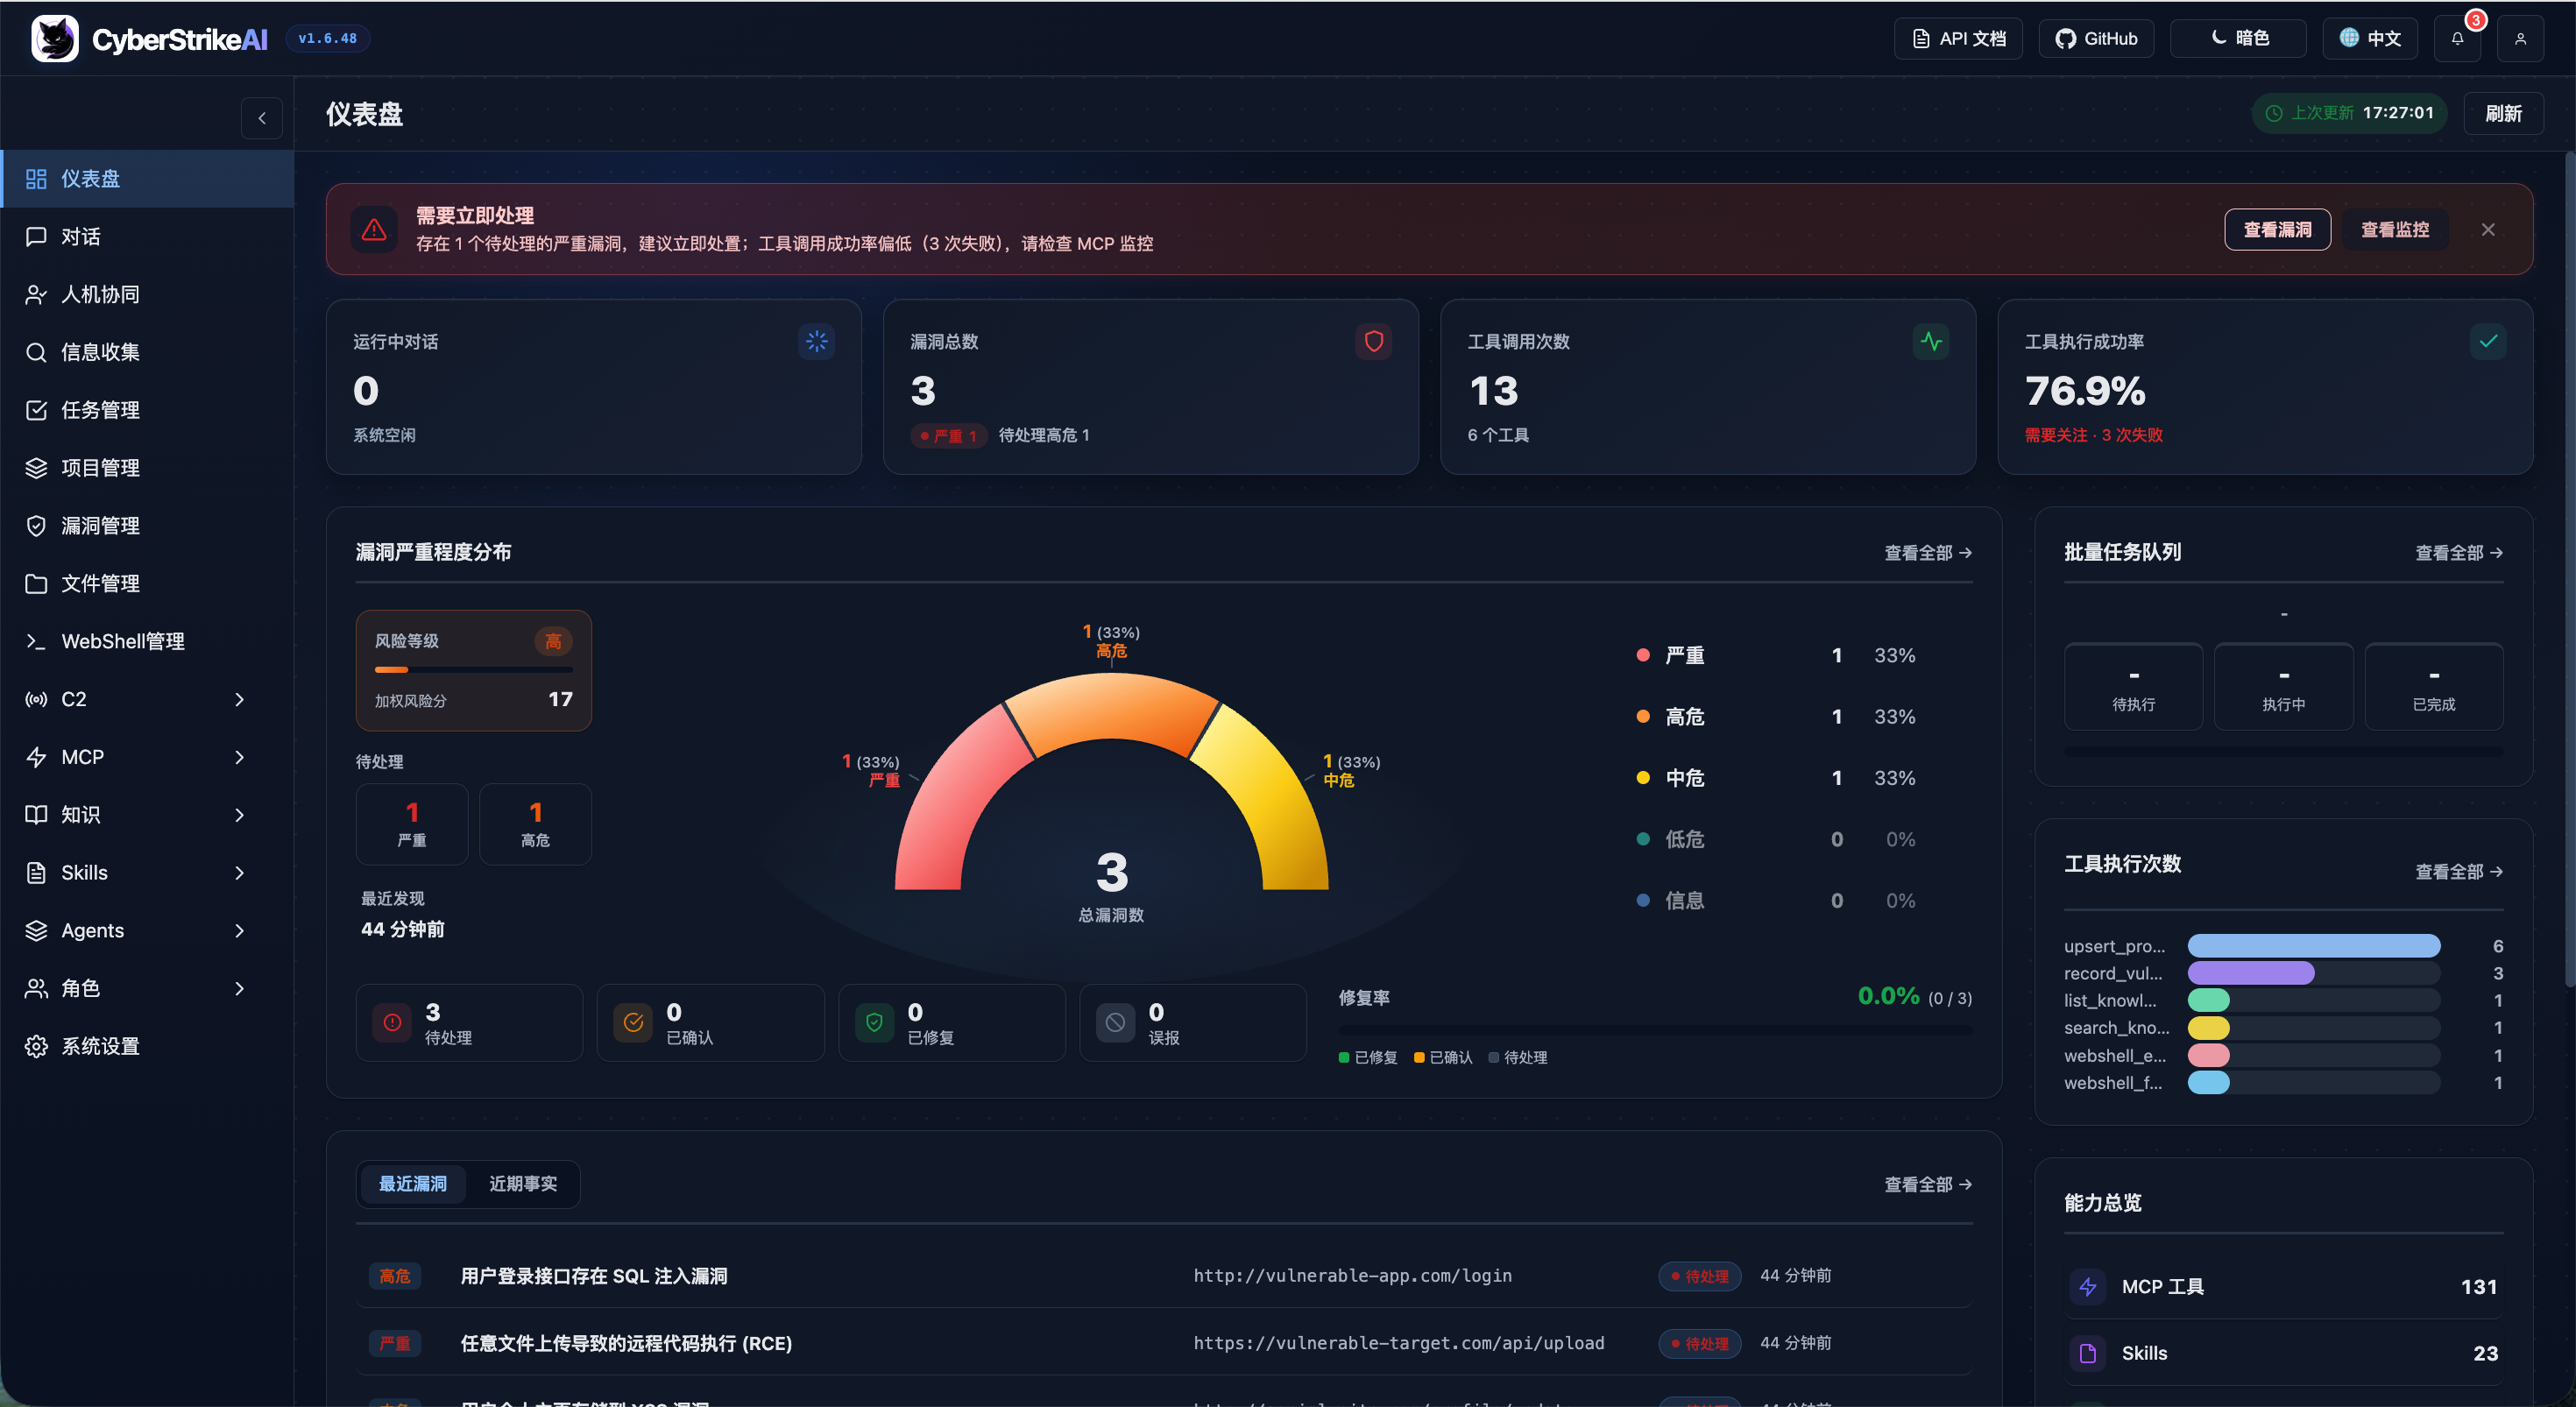
CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
6.6k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 cybersecsi/dockerized-android
A container-based framework to enable the integration of mobile components in security training platforms
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 darkarnium/log4j-cve-detect
Detections for CVE-2021-44228 inside of nested binaries
 aquasecurity/binfinder
Find binary files not installed through package manager
 rishvic/xpdf-docker
Docker images of Xpdf 4.04, vulnerable to CVE-2022-30524
 lacinquette/practice-22-23
CVE-2017-9608 analysis