

discover
 leebaird/discover
Custom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
api-security-testingcloud-securitycontainer-security+9
3.9k
leebaird/discoverCustom Bash and Python scripts used to automate various penetration testing tasks including recon, scanning, enumeration, and malicious payload…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 dipjyotimetia/hybridtestframework
End to End testing of Web, API, Cloud, Events and Security

 invuls/pentest-projects/pcf
Opensource, cross-platform and portable toolkit for automating routine processes when carrying out various works for testing!
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
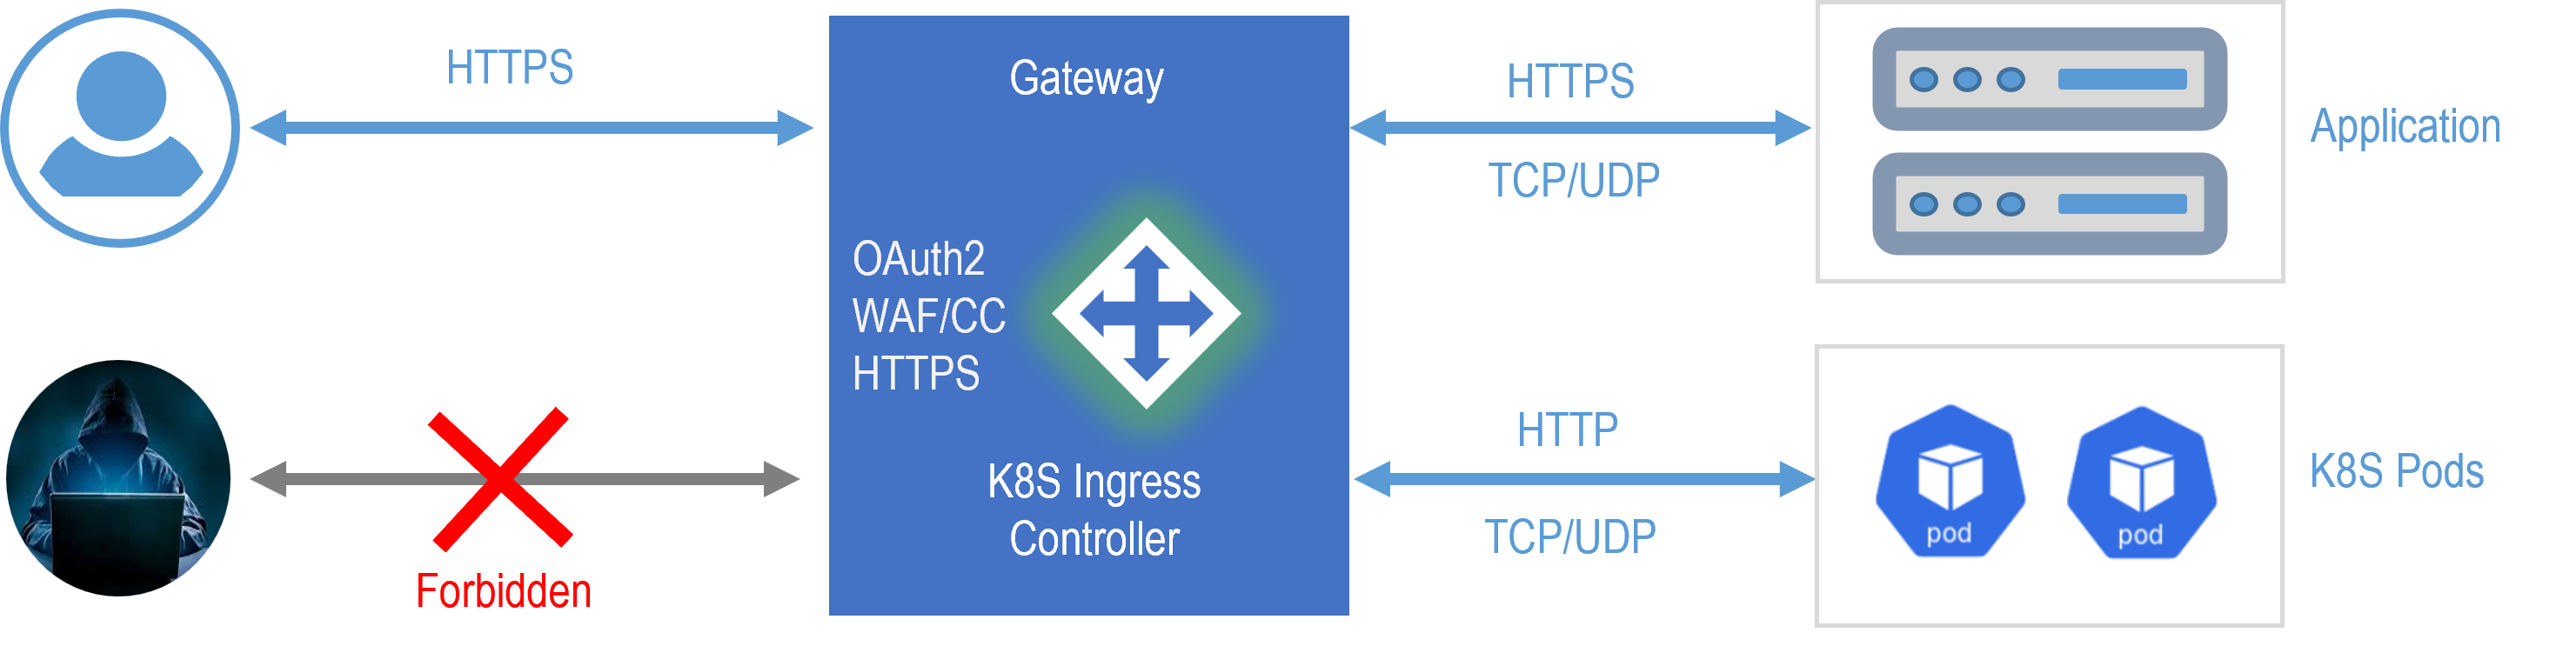 janusec/janusec
Unified application gateway providing reverse proxy, WAF, CC defense, OAuth2 authentication, ACME certificate automation, and GSLB for secure,…
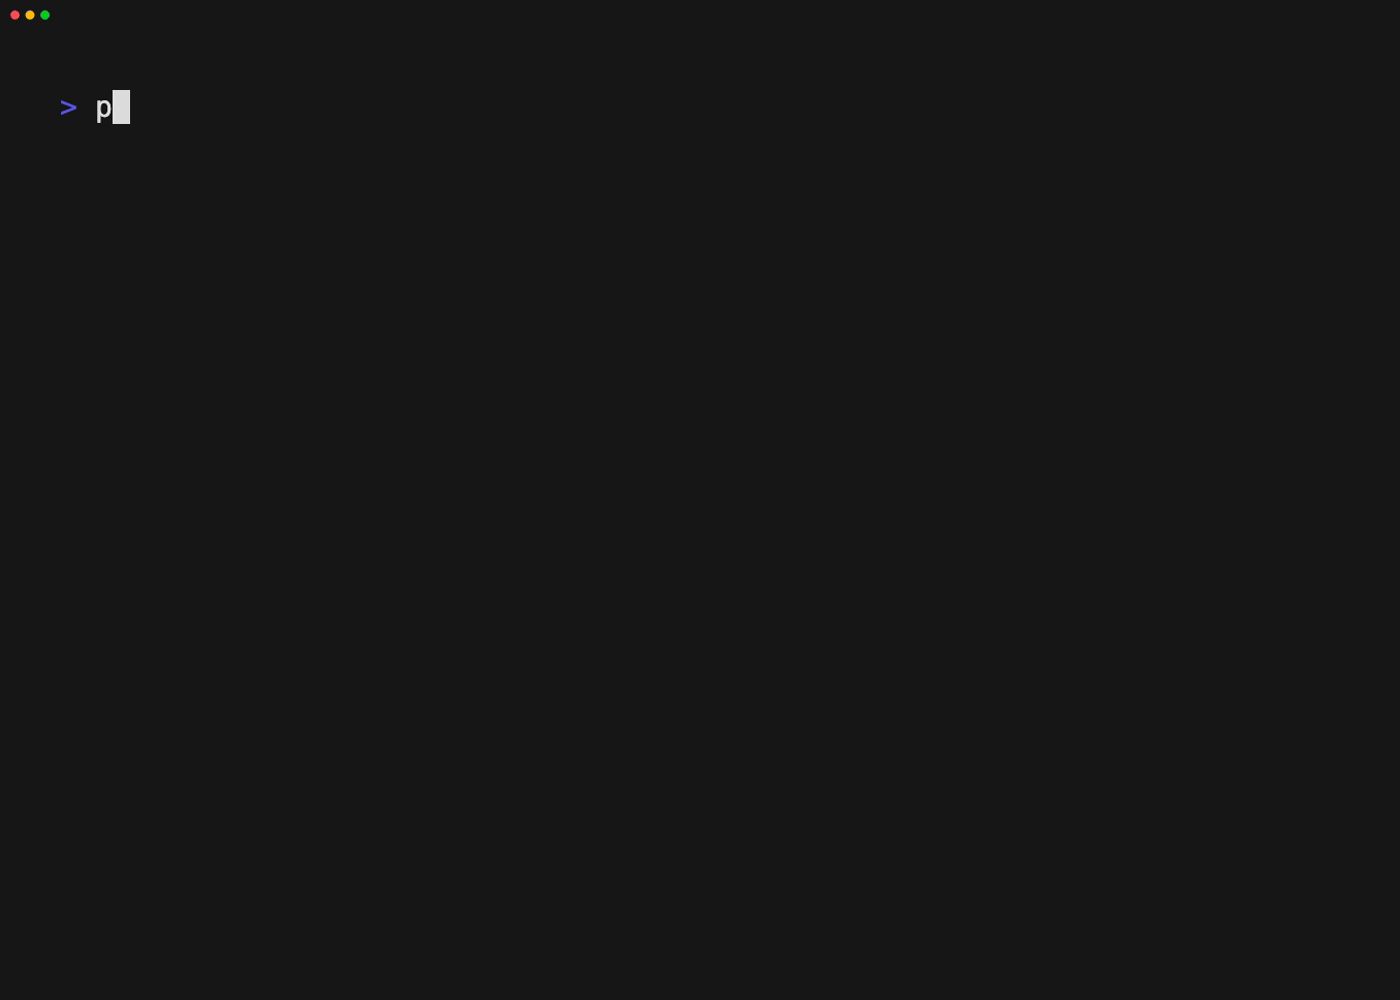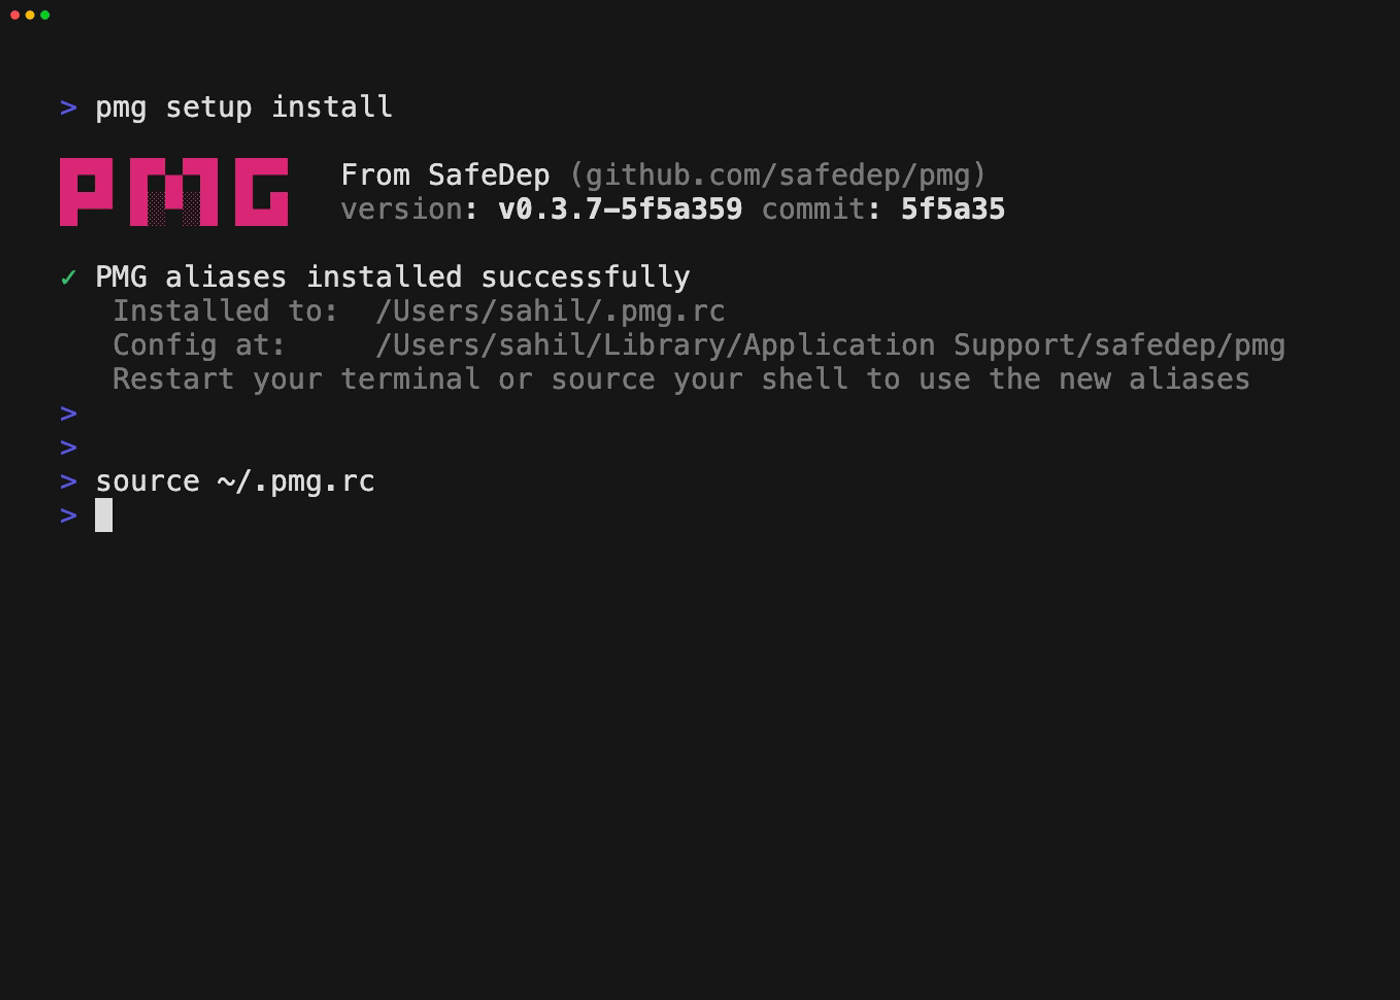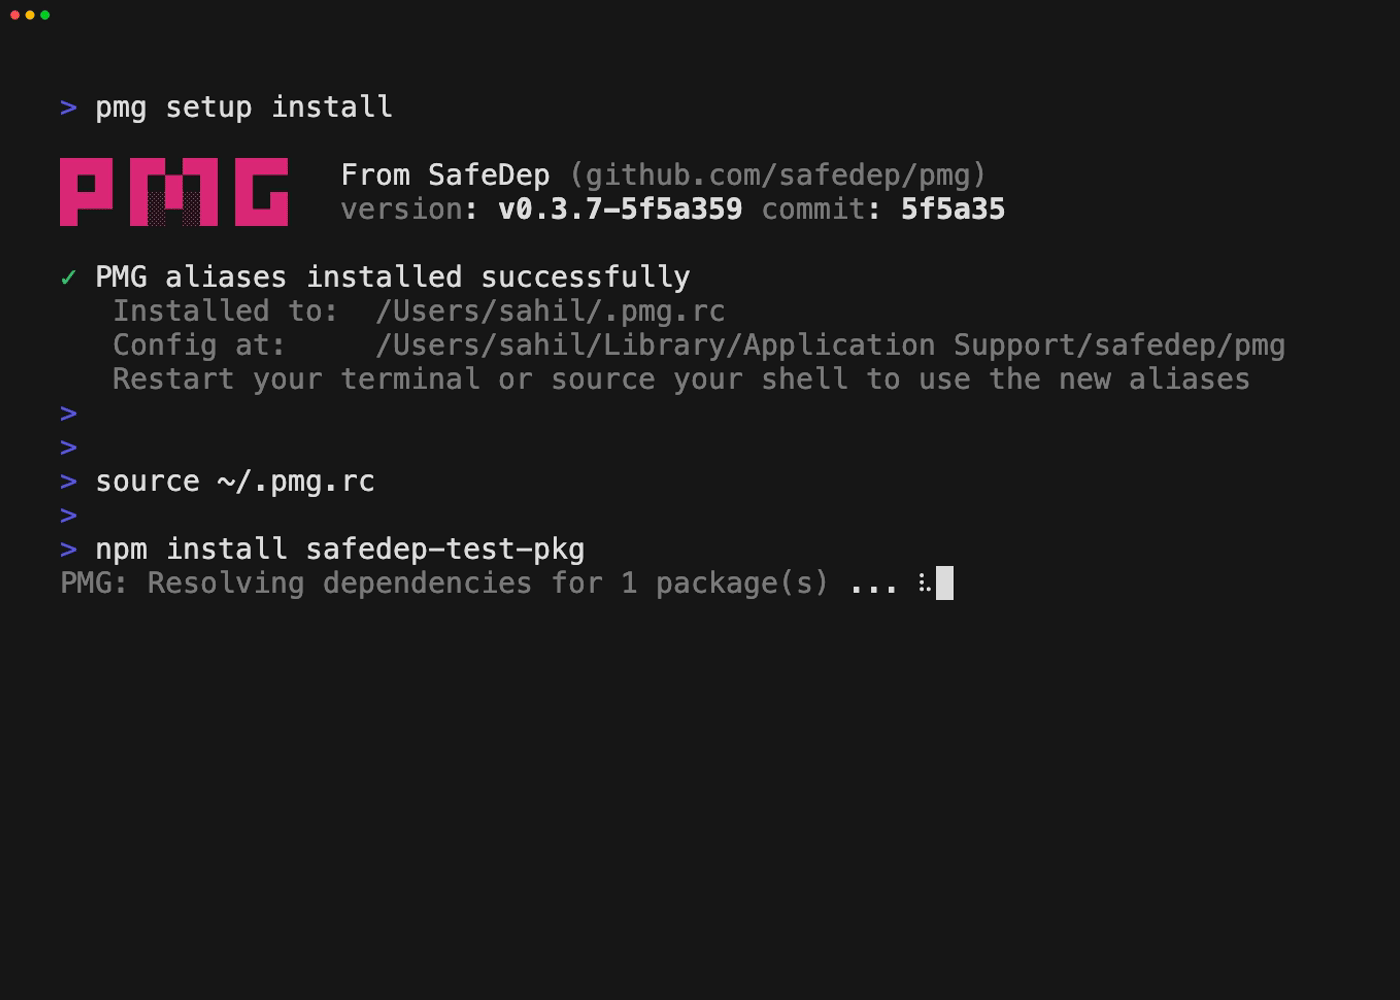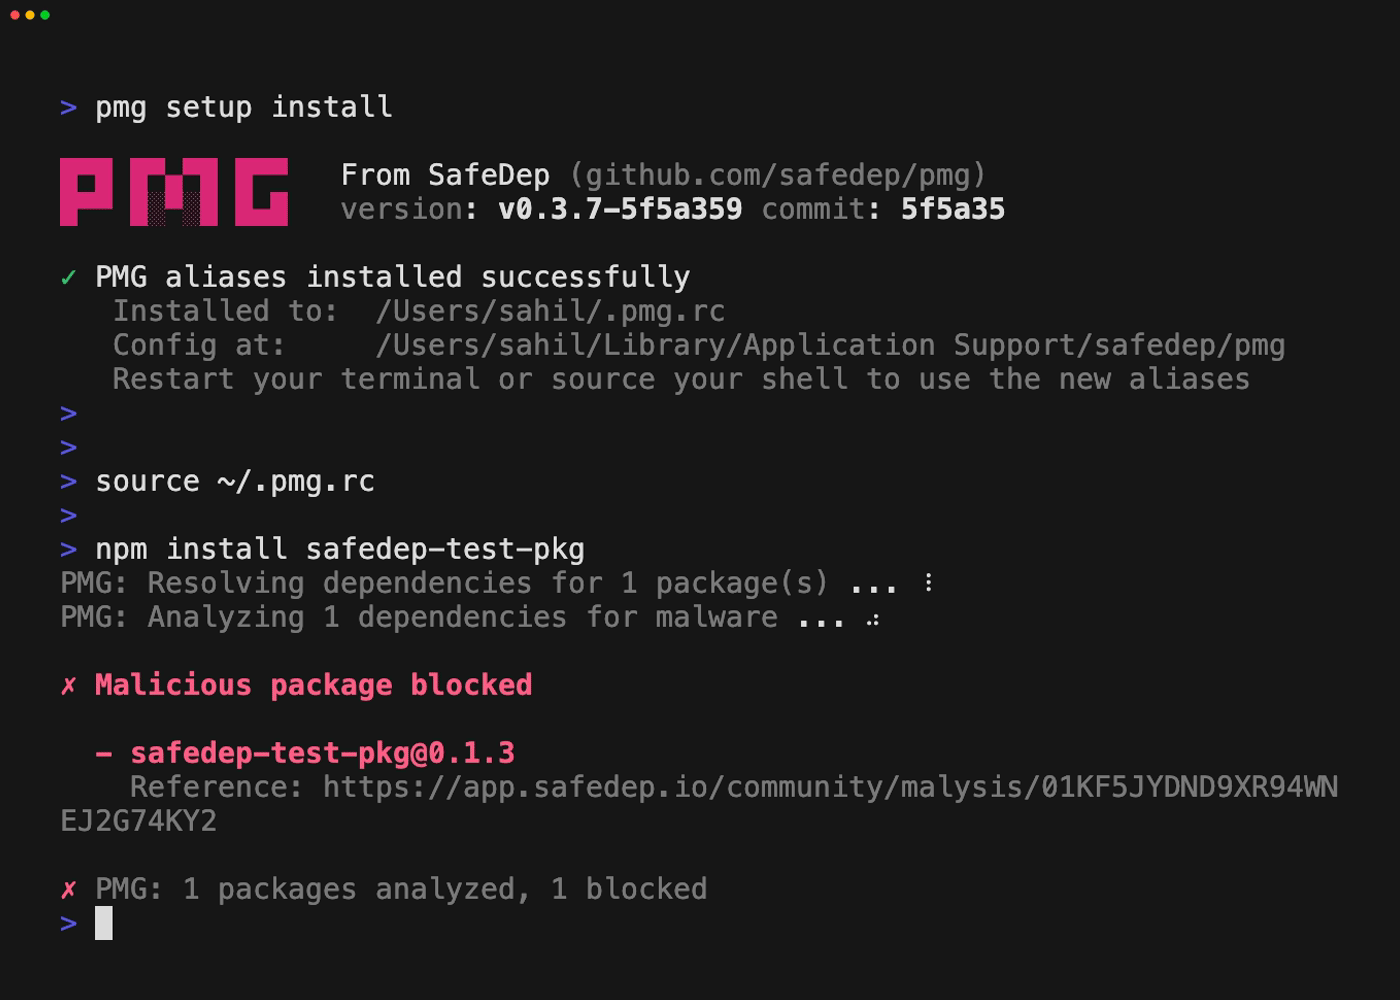 safedep/pmg
PMG protects developers, AI agents from malicious open source packages using proxy, sandbox and SafeDep's threat intelligence feed.
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 thodoristsampouris/agentguard
Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…
 leitwacht/leitwacht-agent
eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/
 paradigmxyz/iron-proxy
An egress firewall for untrusted workloads.
 tabbysable/poc-2020-8558
Information about Kubernetes CVE-2020-8558, including proof of concept exploit.
 legendile7/cve-2026-78122-poc
Proof-of-concept exploit for CVE-2026-78122, demonstrating container filesystem and environment variable exfiltration through docker-socket-proxy's…
 alixiacf/rep-openai-artifactory
Forensic Analysis and Local Replication of the OpenAI-Artifactory Privilege Escalation Incident (CVE-2026-65616)
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)