
CVE-2023-5044
 kubernetesbachelor/cve-2023-5044
Poc for CVE 2023 5044
cloud-infrastructure-securitycloud-securitycontainer-security+4
kubernetesbachelor/cve-2023-5044Poc for CVE 2023 5044
 stealthcopter/deepce
Docker Enumeration, Escalation of Privileges and Container Escapes (DEEPCE)
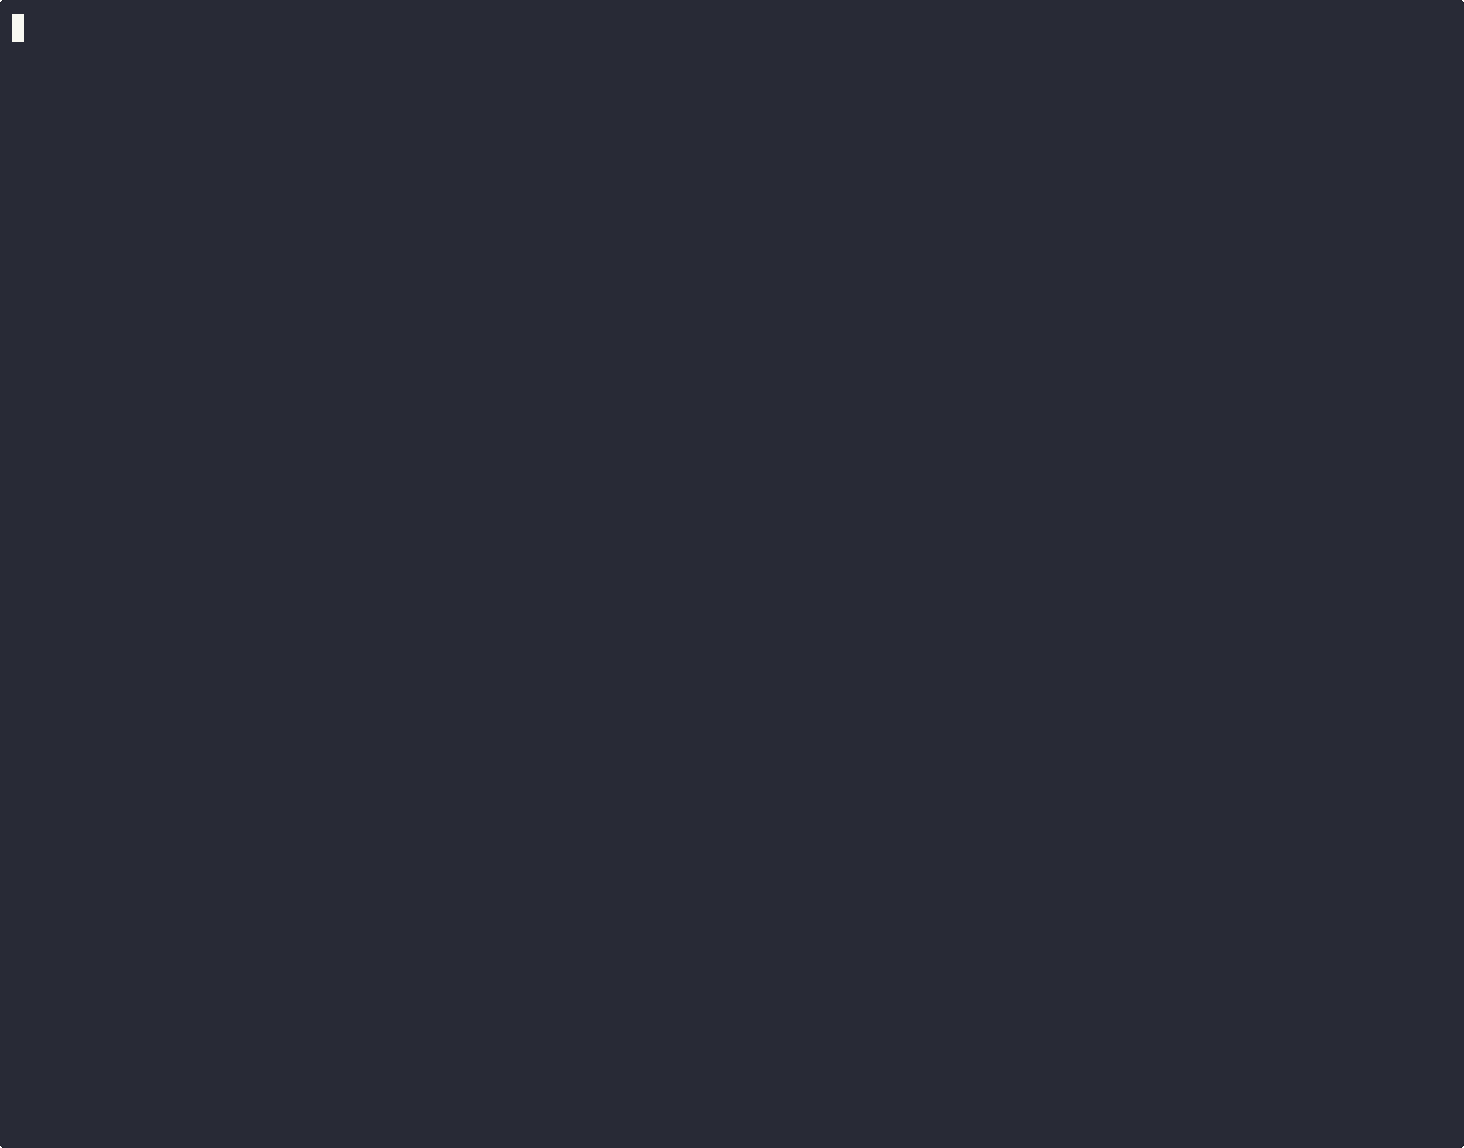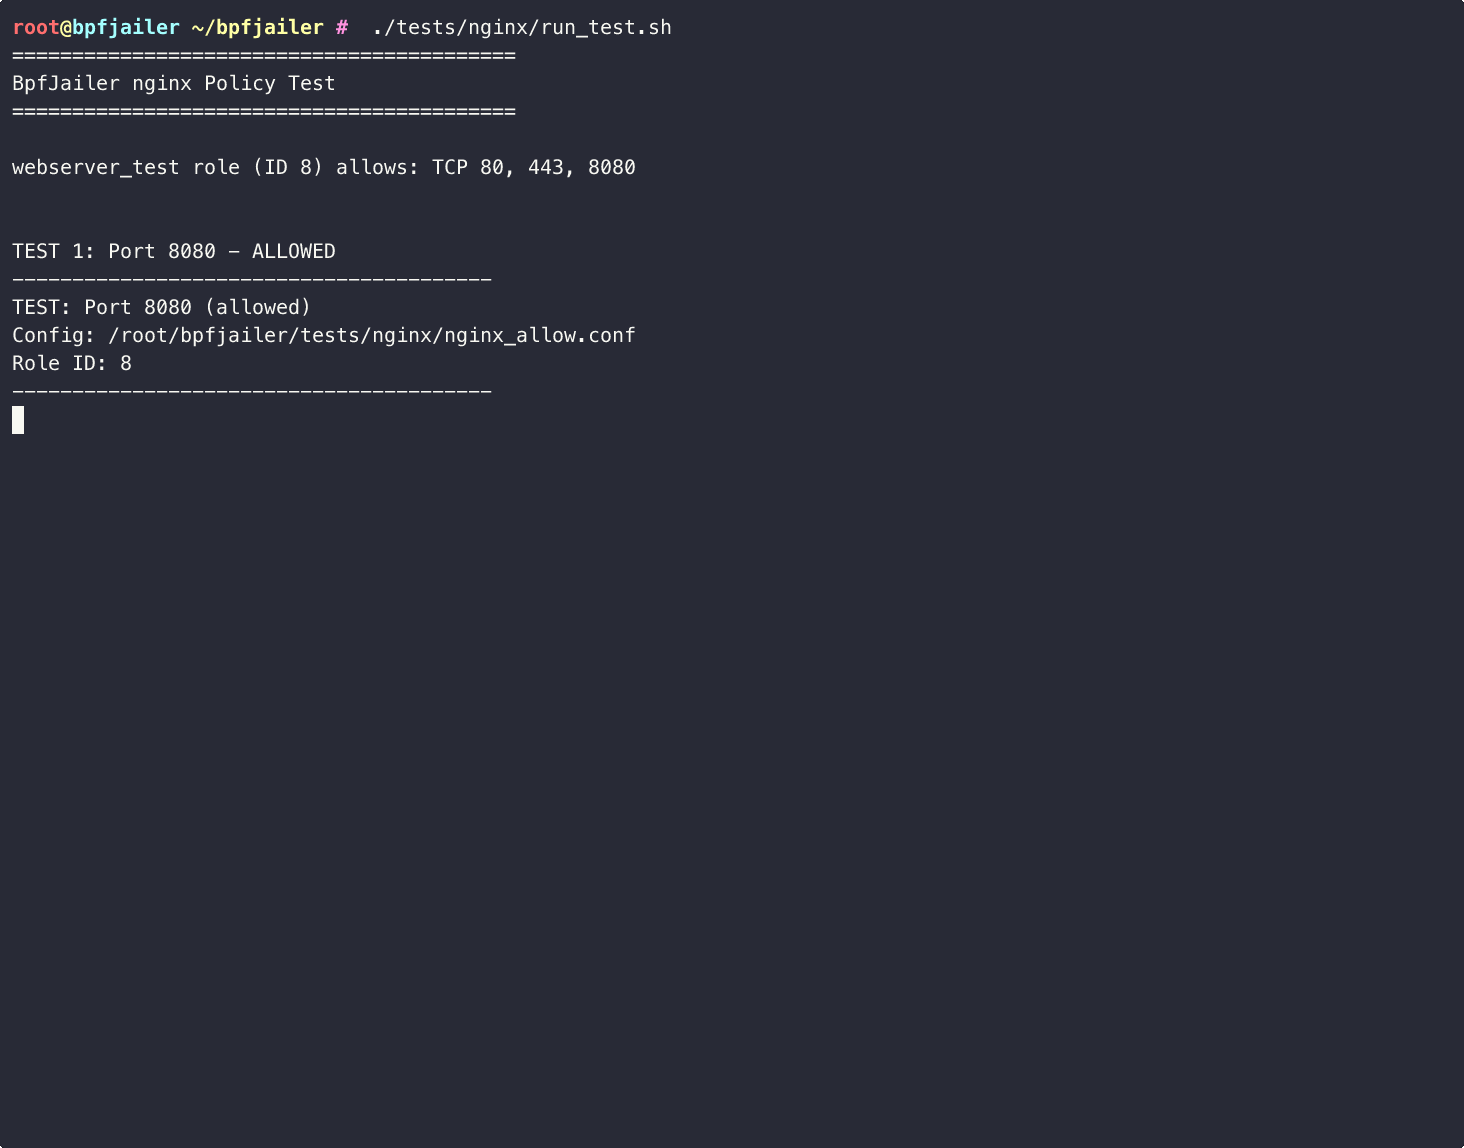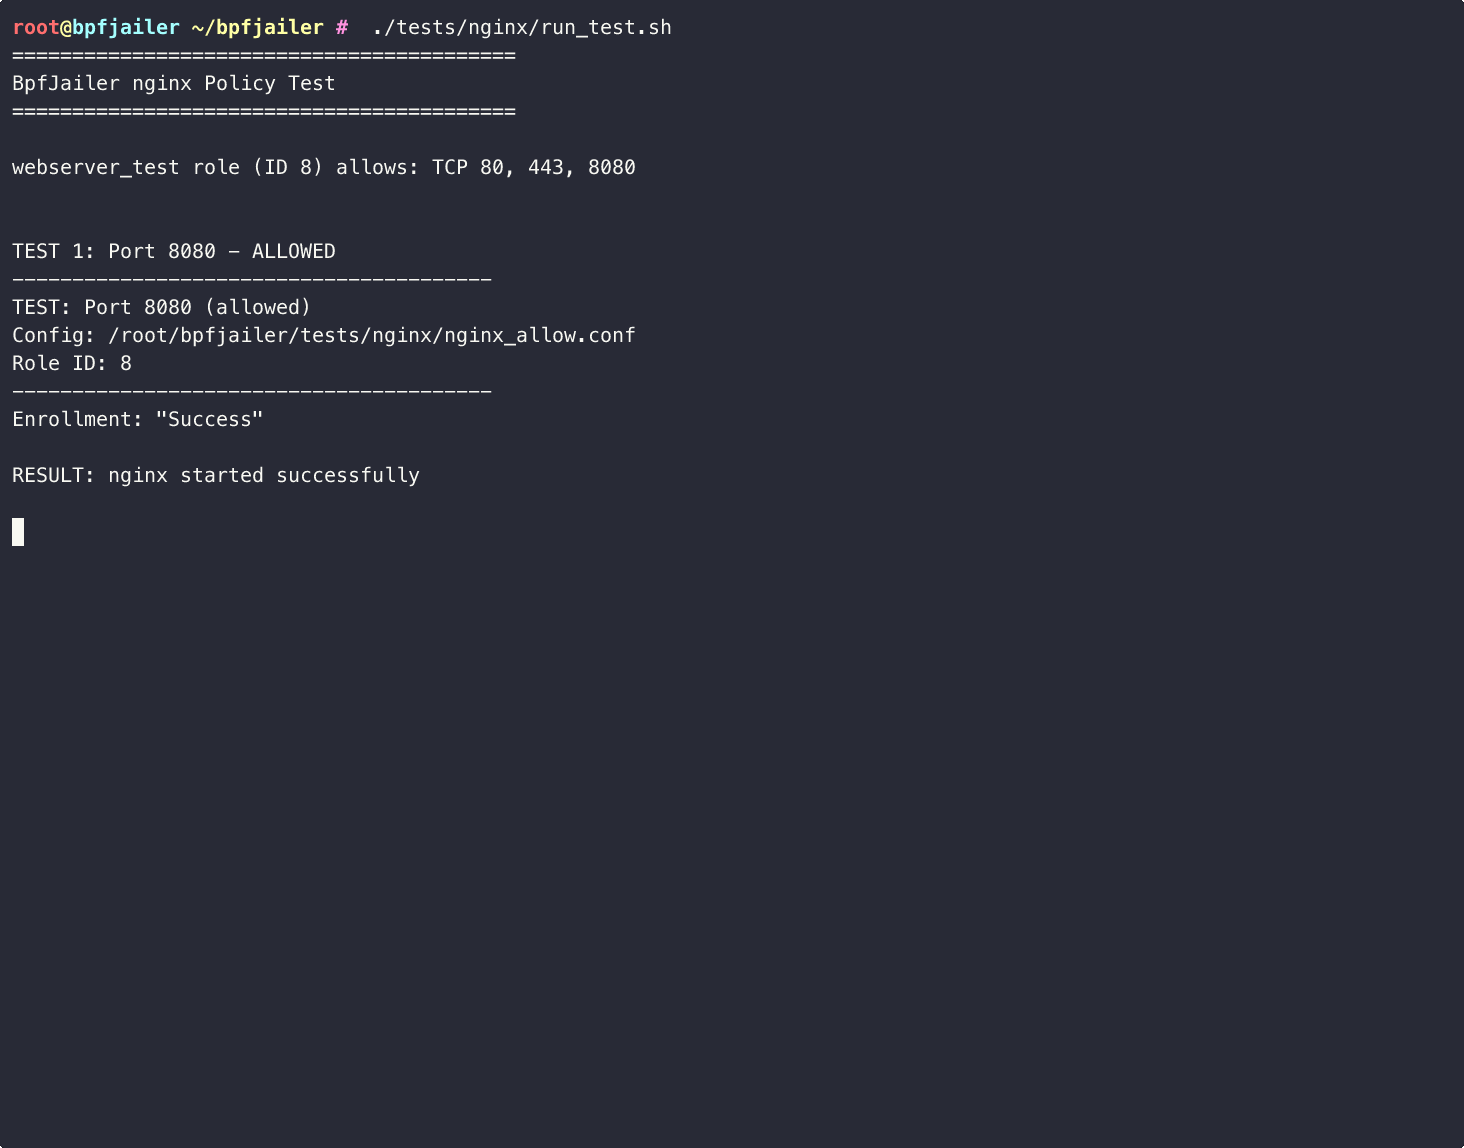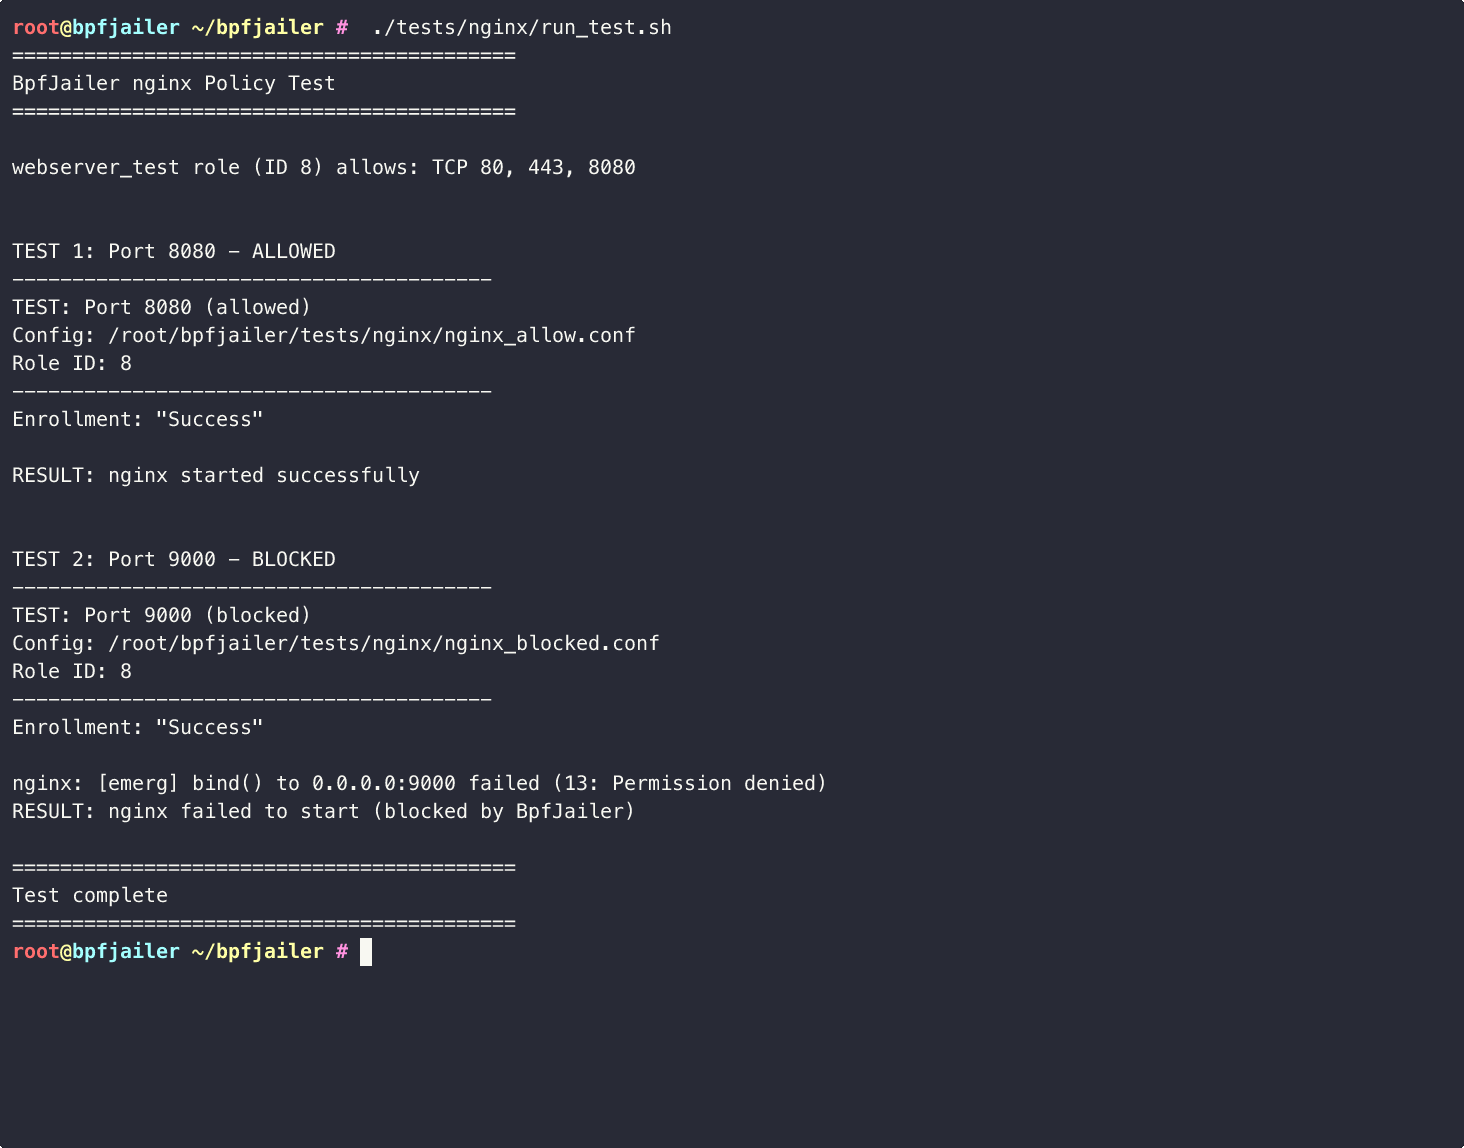 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 zzugab/juice-shop-with-kubeadm-and-tf
Automated deployment of OWASP Juice Shop on Kubernetes using kubeadm and Terraform, with integrated Trivy vulnerability scanning for DevSecOps…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 nccgroup/insject
insject is a tool for poking at containers. It enables you to run an arbitrary command in a container or any mix of Linux namespaces.
 roxanne_ardary/securekit
Securekit is a protocol-agnostic security kernel that enforces zero-trust, sandboxed execution for AI tool use. It sits between any LLM or agent…
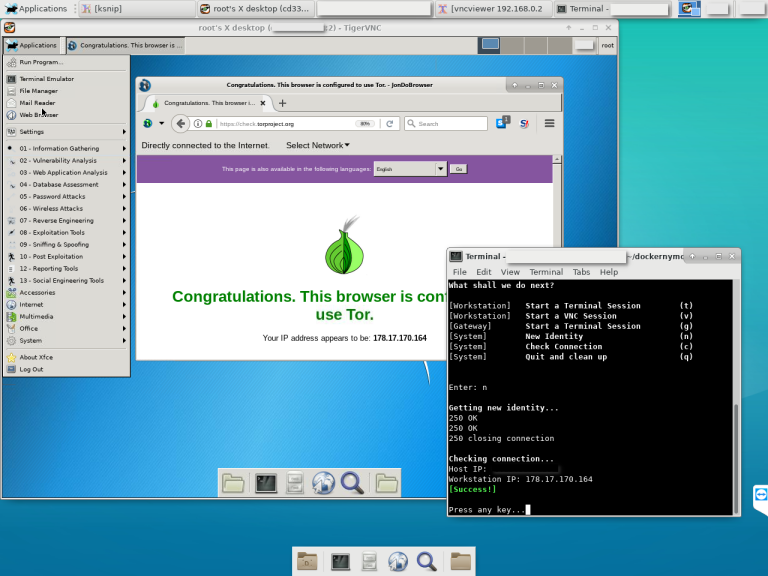 bcapptain/dockernymous
A script used to create a whonix like gateway/workstation environment with docker containers.
 shopify/kubeaudit
kubeaudit helps you audit your Kubernetes clusters against common security controls
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 thegebirge/cve-2025-32375
This repository includes everything needed to run a PoC exploit for CVE-2025-32375 in a Docker environment. It runs the latest vulnerable version of…
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 vinieger/vinieger-cve-2025-48384-dockerfile
PoC dockerfile image for CVE-2025-48384
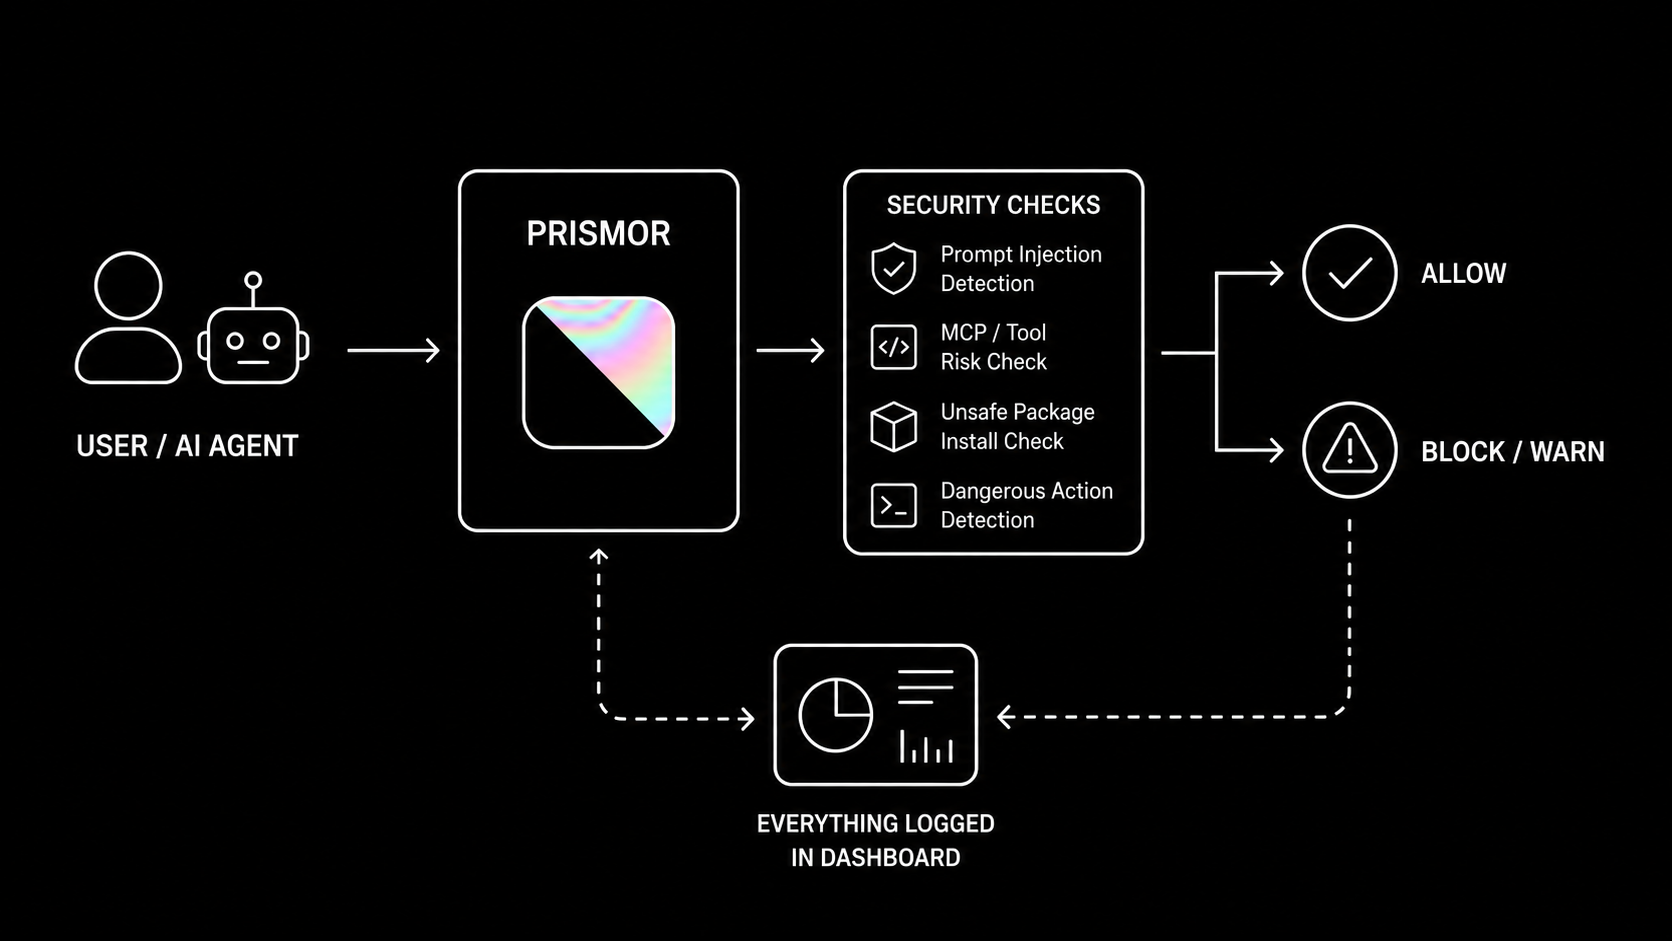 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…