
xzwhy
 neuralinhibitor/xzwhy
XZ Utils CVE-2024-3094 POC for Kubernetes
cloud-securitycontainer-securityeducation+4
neuralinhibitor/xzwhyXZ Utils CVE-2024-3094 POC for Kubernetes
 joebeeton/cve-2024-4701-poc
POC for CVE-2024-4701
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 vt0x78/cve-2024-31989
Exploit for CVE-2024-31989.
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 laysakura/cve-2024-21626-demo
Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…
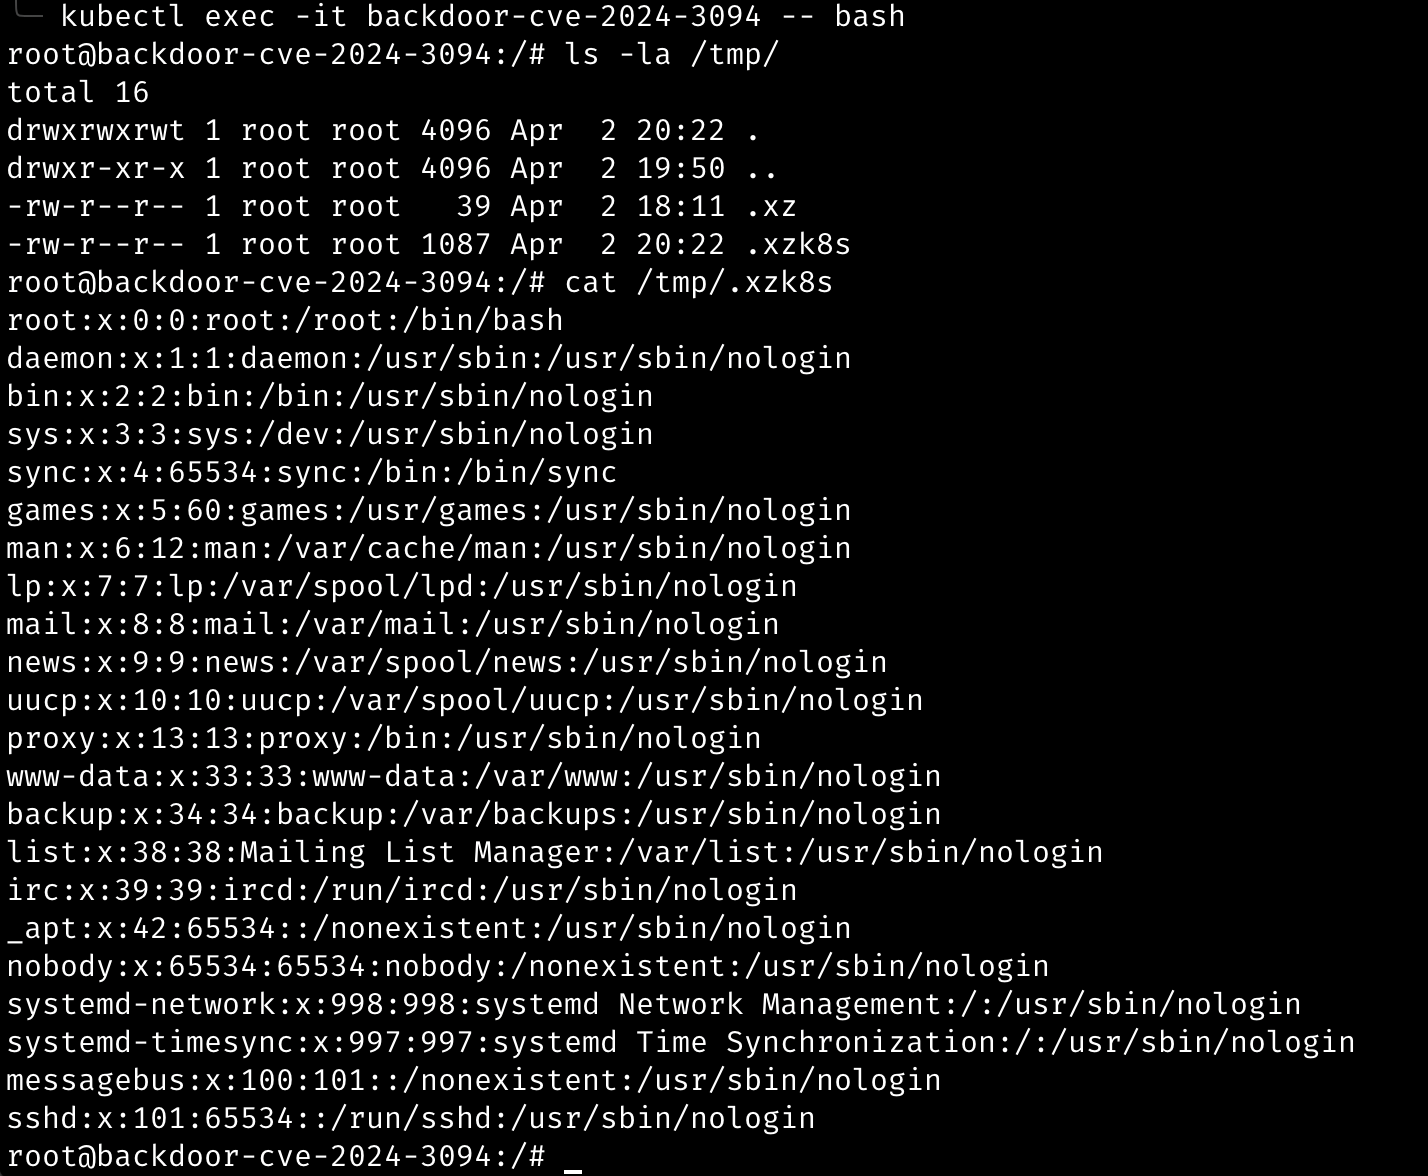 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094
 dorser/cve-2024-21626
Educational demo of CVE-2024-21626 runc container escape with eBPF-based detection gadget for exploitation attempts.
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 cdxiaodong/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host…
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 juanorts/crushftp10-docker-cve-2024-4040
A Dockerized setup for running a vulnerable CrushFTP 10 server instance (CVE-2024-4040).
 pauloparopp/cve-2024-41110-scan
Python-based scanner that checks Docker hosts for CVE-2024-41110 by detecting vulnerable Docker versions and AuthZ plugin usage.