
moltis
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
ai-securityapi-securityauthentication-authorization+7
2.8k
moltis-org/moltisA secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.
 zentinelproxy/zentinel
A security-first reverse proxy built to guard the free web.
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems
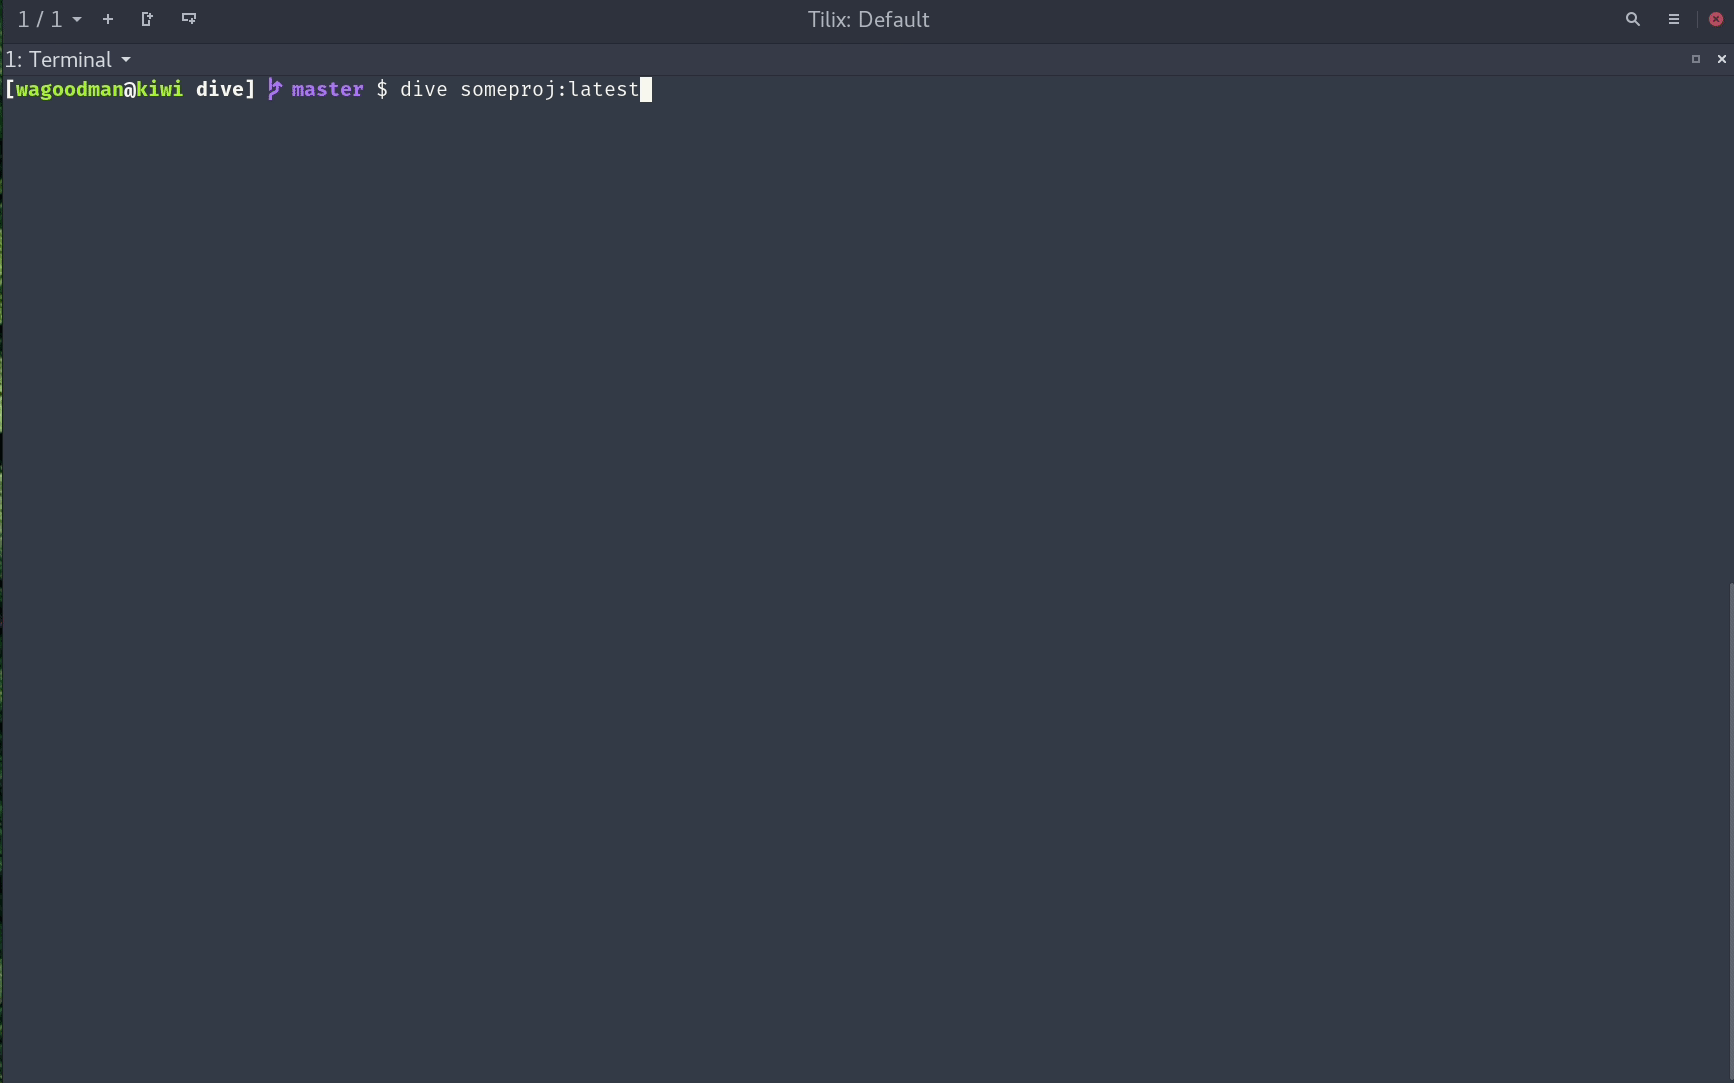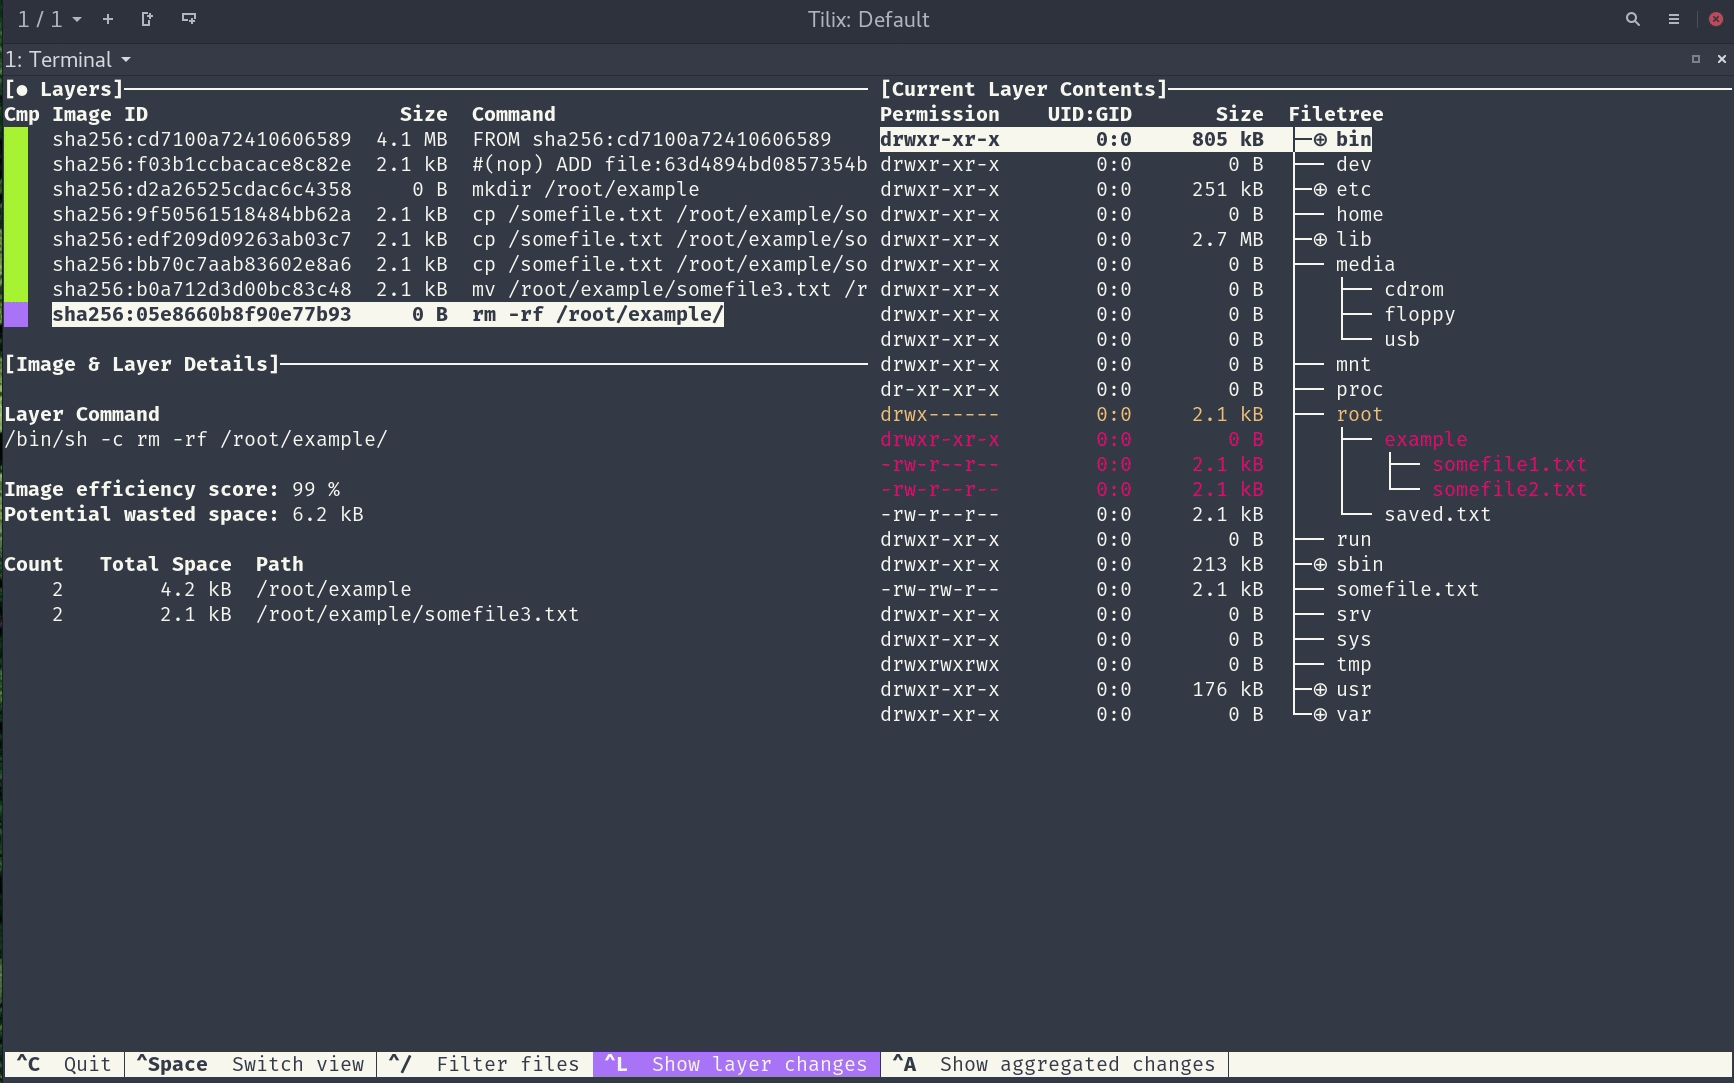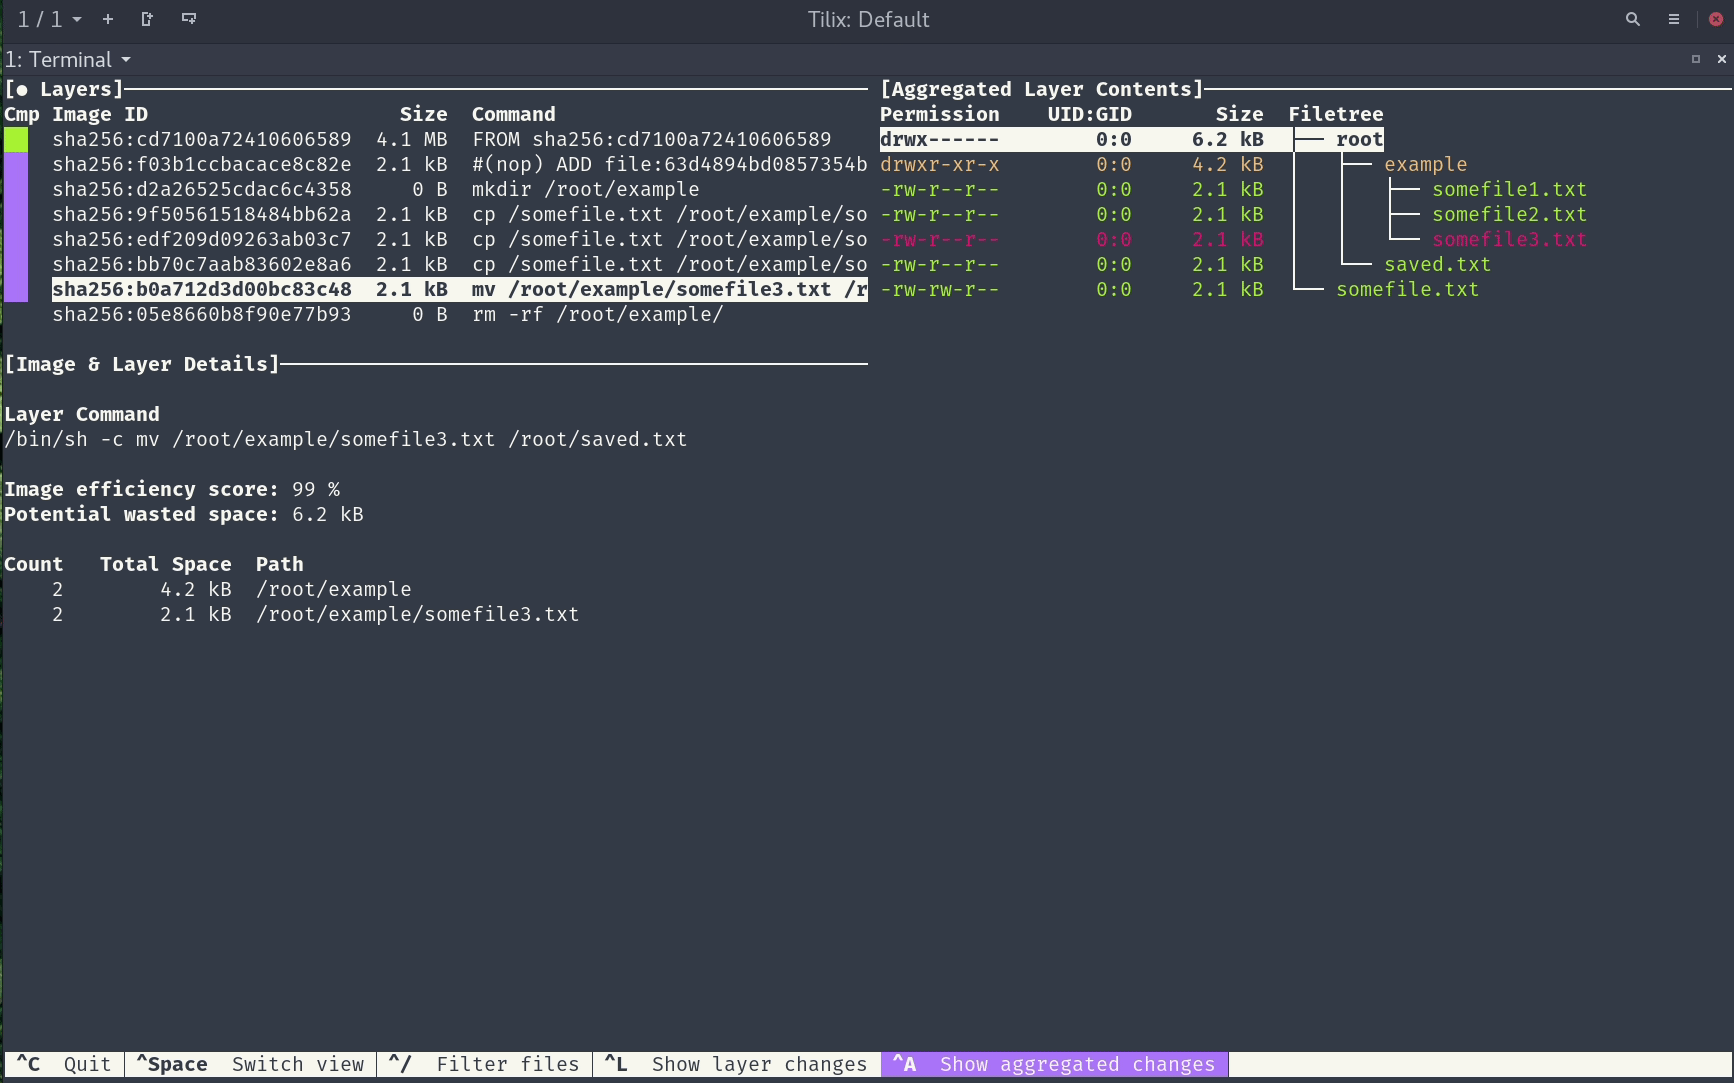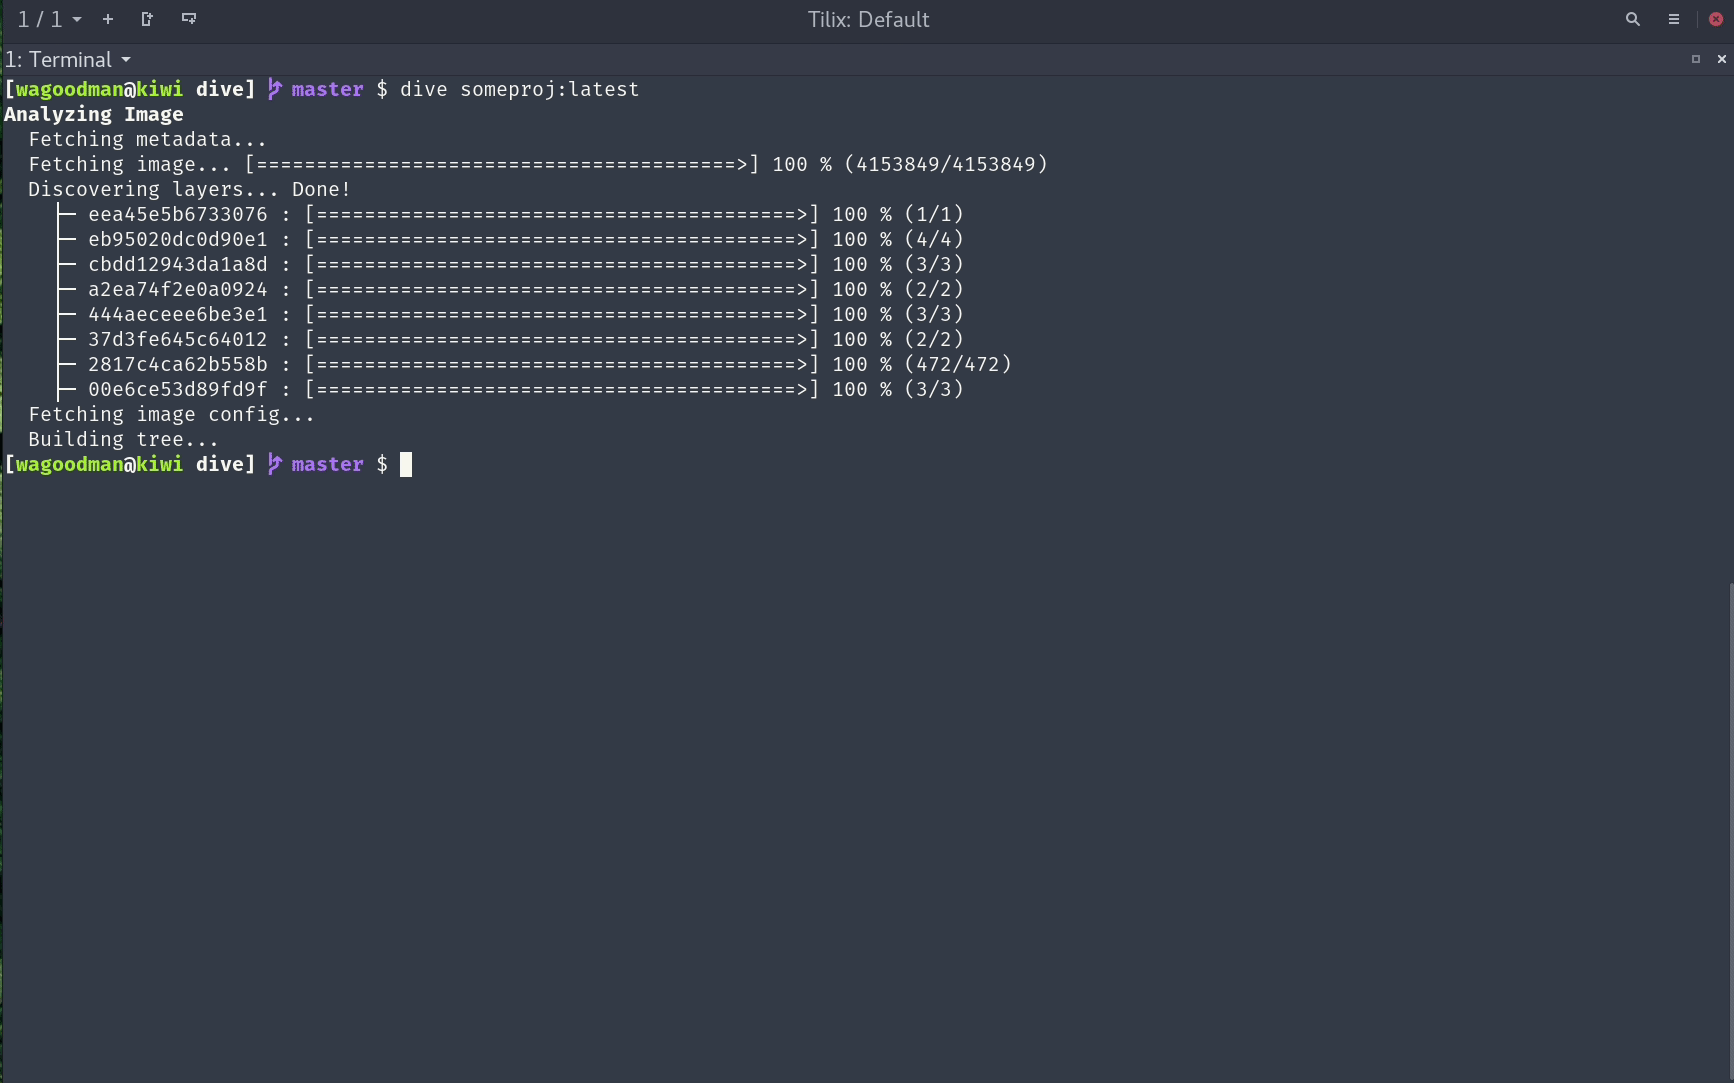 wagoodman/dive
A tool for exploring each layer in a docker image
 containers/bubblewrap
Low-level unprivileged sandboxing tool used by Flatpak and similar projects
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 kubesphere/kubeeye
Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…
 backbay-labs/clawdstrike
Policy engine and EDR for AI agent fleets and developer workstations. Monitors tool calls, file access, network flows, and process execution with…
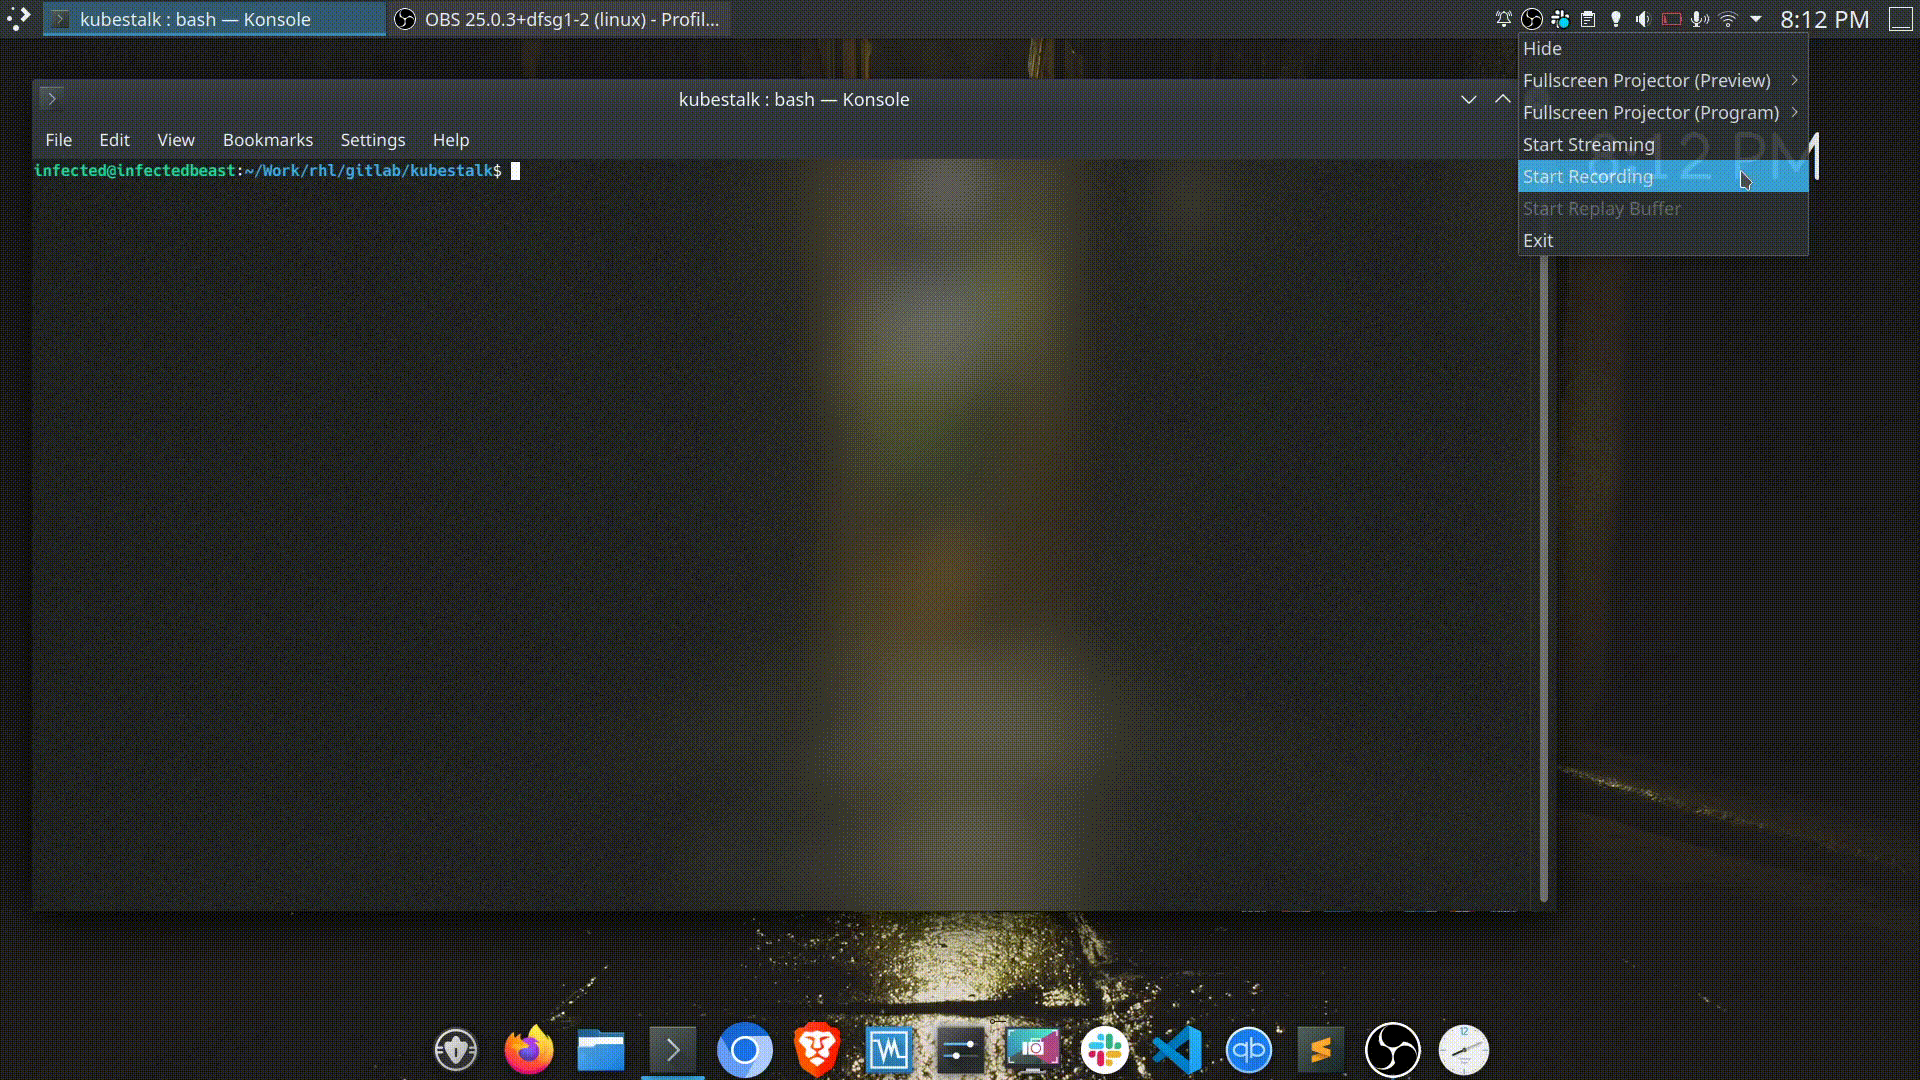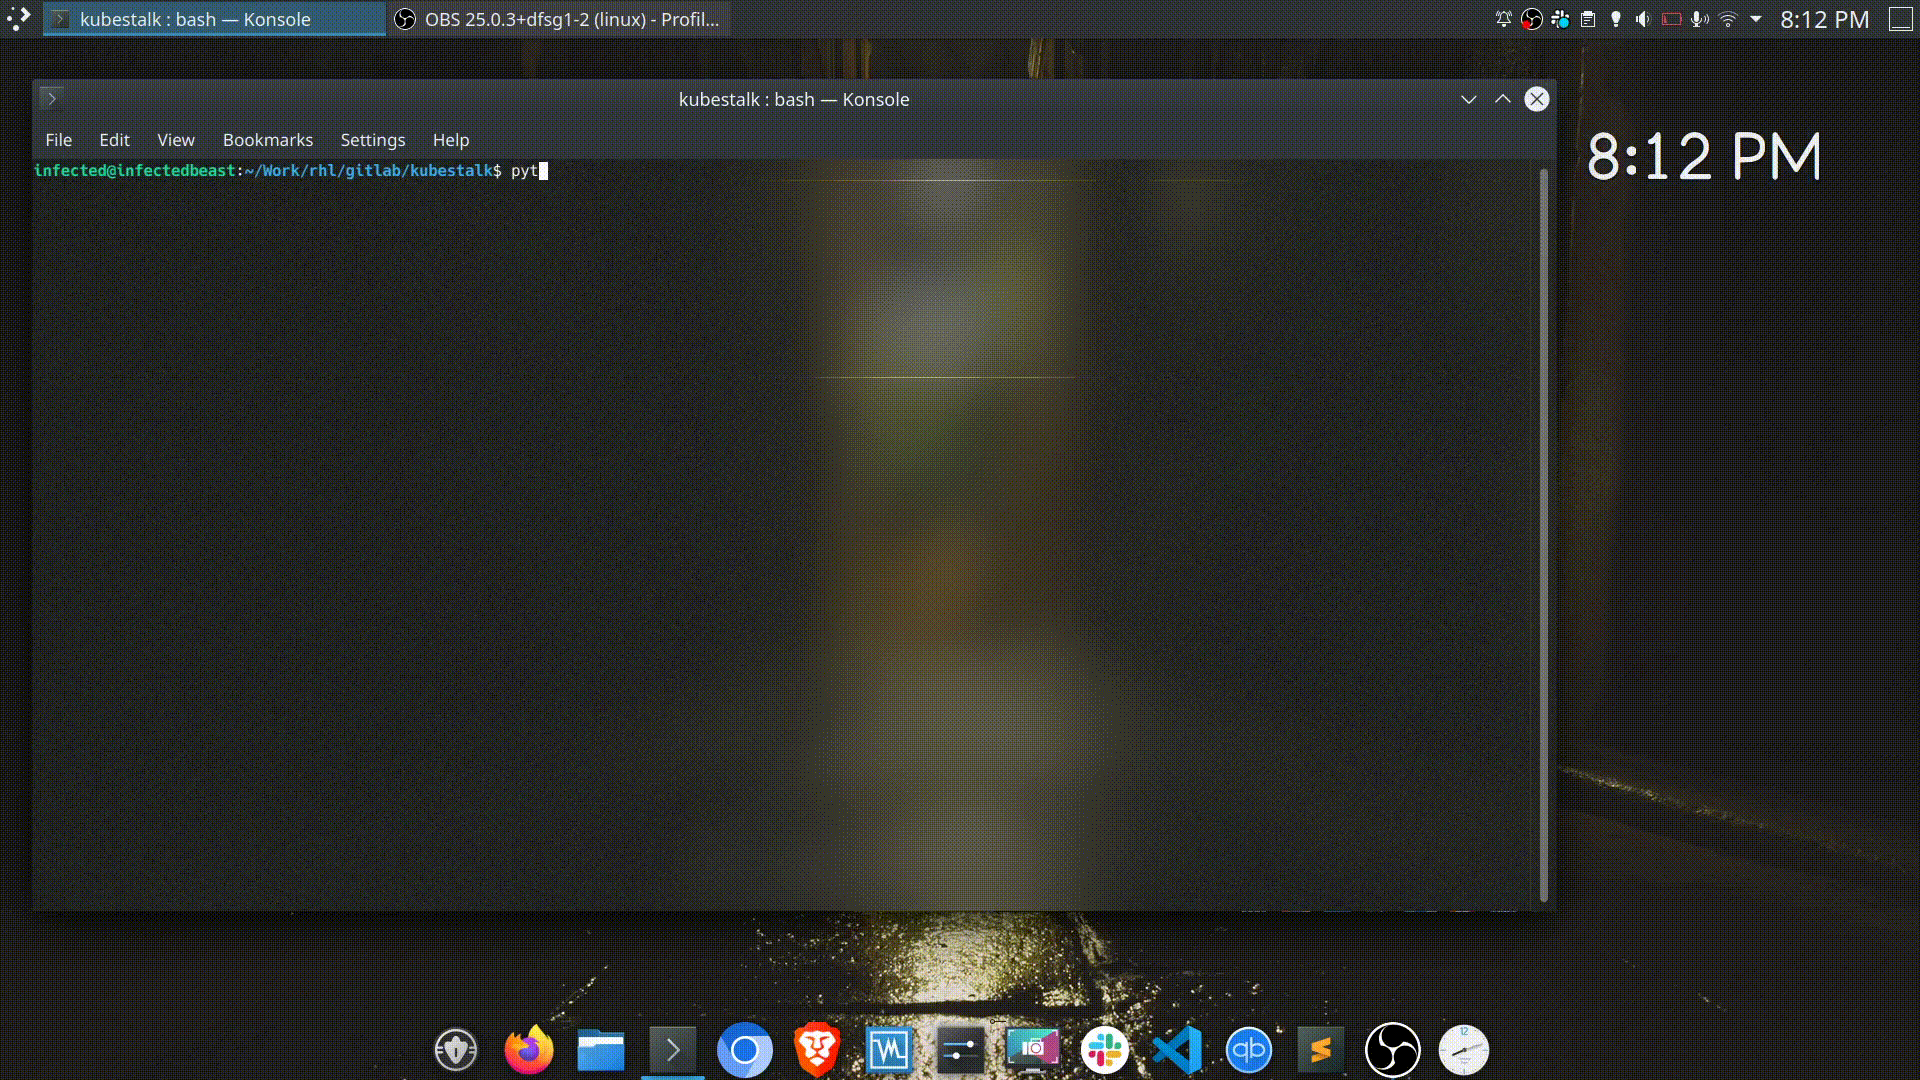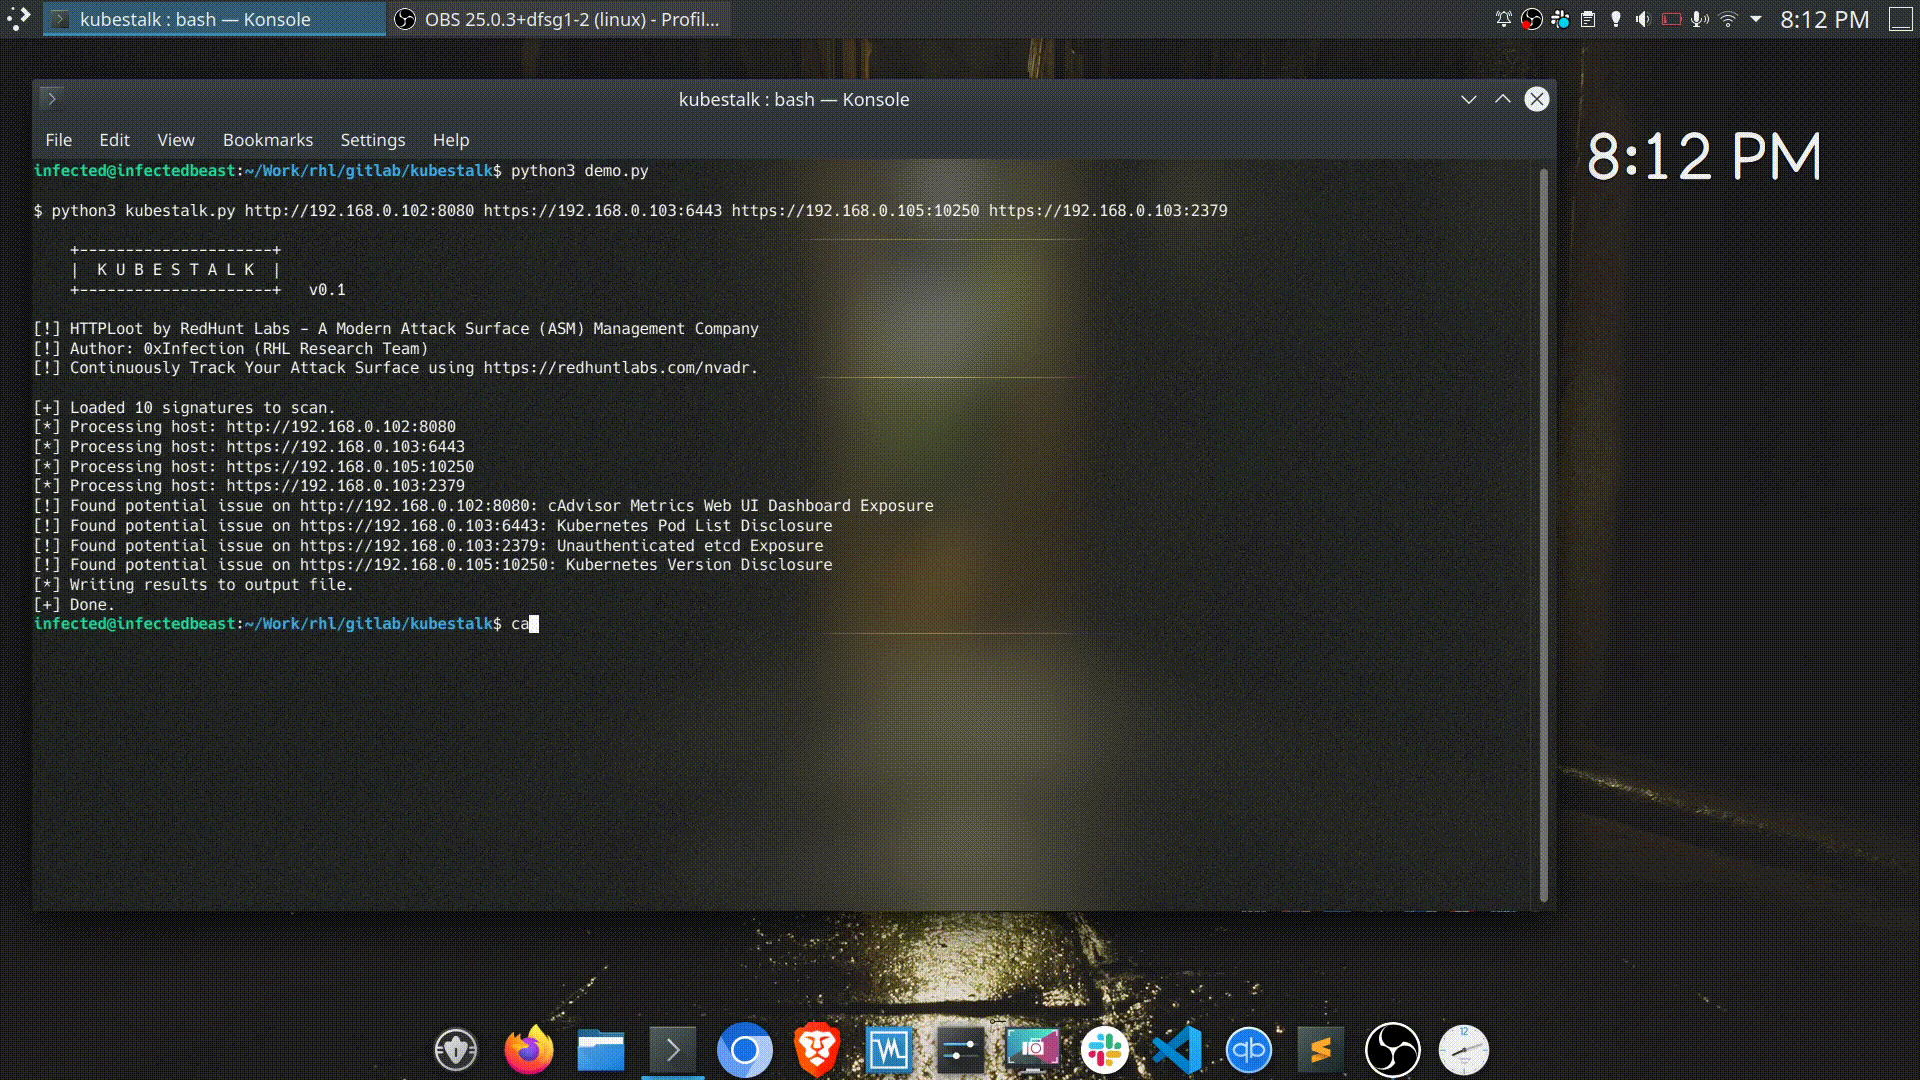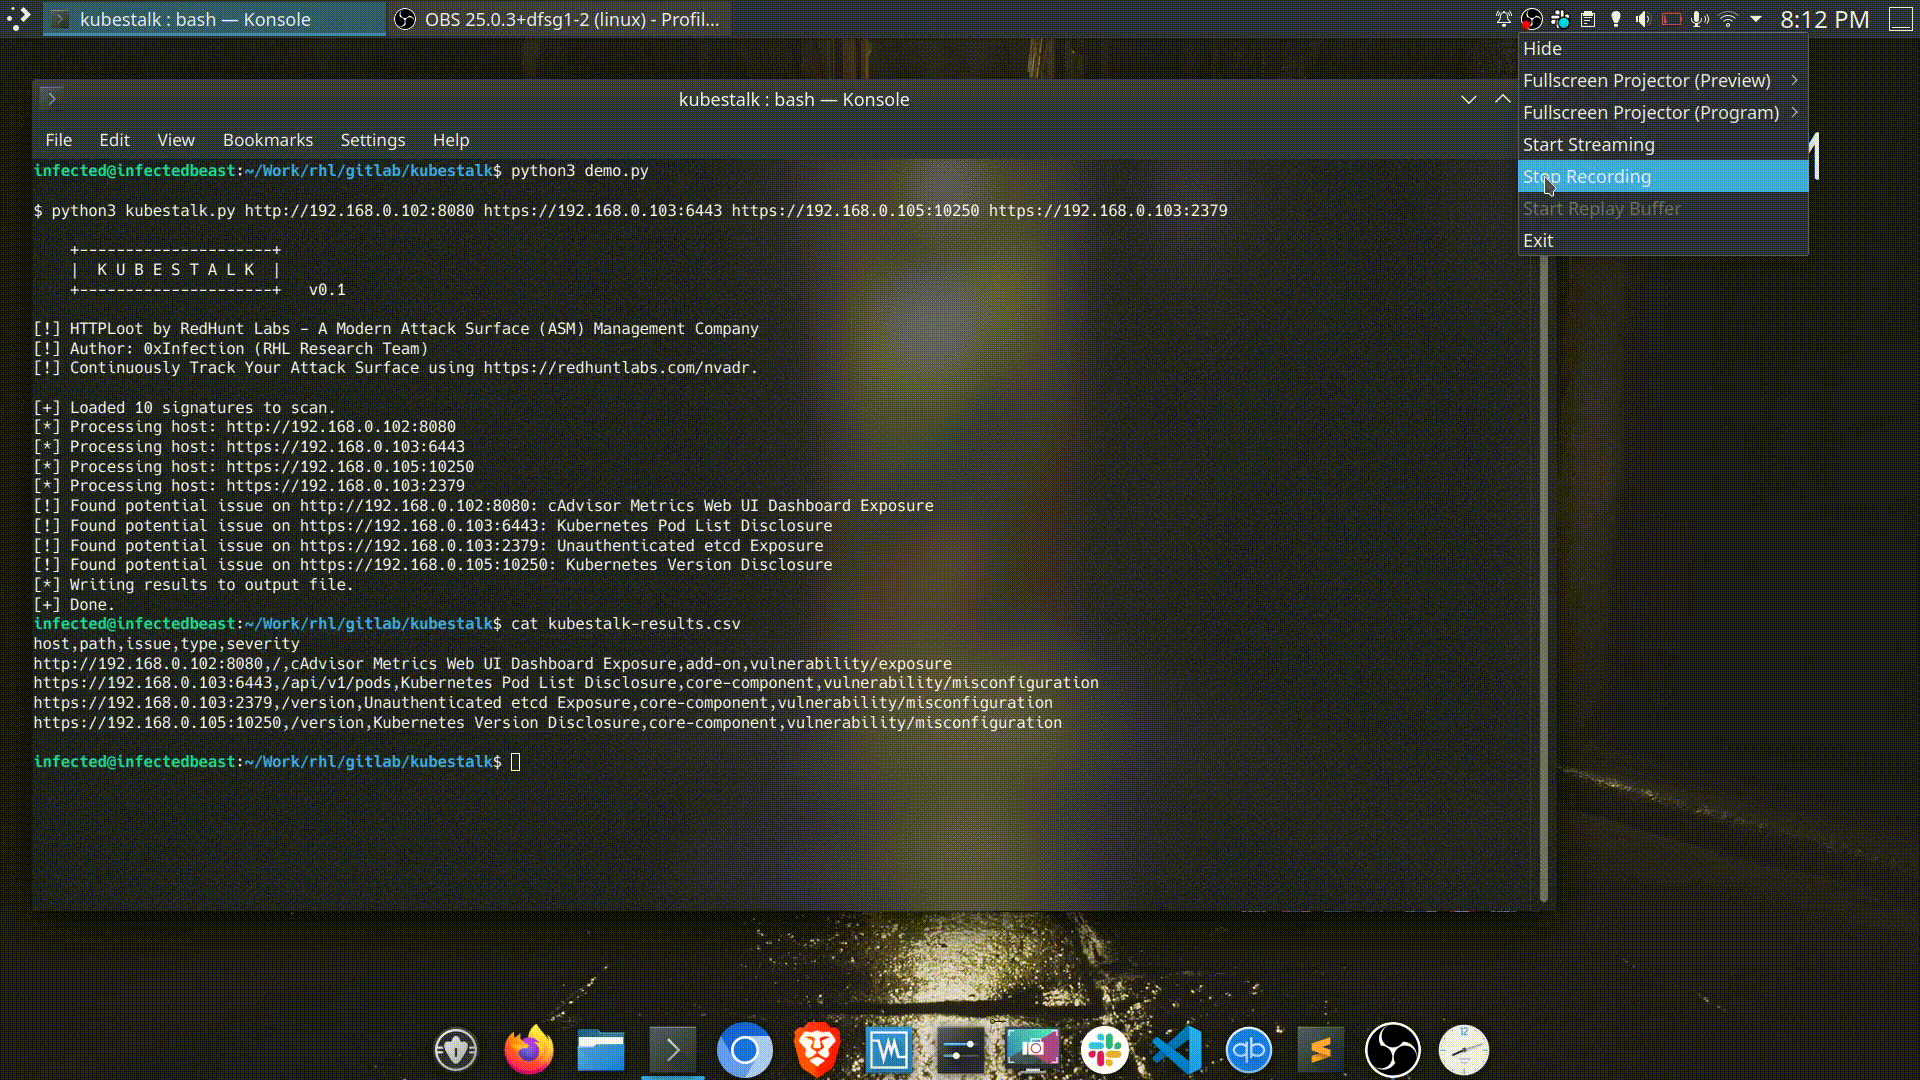 redhuntlabs/kubestalk
Black-box Kubernetes attack surface discovery tool that probes for unsecured clusters, exposed dashboards, and misconfigurations using…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 linux-lock/bpflock
eBPF-driven security tool for locking and auditing Linux machines. Restricts kernel features, blocks fileless execution, protects memory, and hardens…
 rosehgal/dockerent
The only open-source tool to analyze vulnerabilities and configuration issues with running docker container(s) and docker networks.
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 nccgroup/go-pillage-registries
Pentester-focused Docker registry tool to enumerate and pull images
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…