

ship-safe
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
ai-securityapi-security-testingcloud-infrastructure-security+8
asamassekou10/ship-safeThe independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 pantheon-security/medusa
AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…
 randomrobbiebf/chart-down
Extracts all the chart lists from ChartMuseum
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 evict/poc_cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105 targeting Kubernetes API server. Supports authenticated and unauthenticated privilege escalation to…
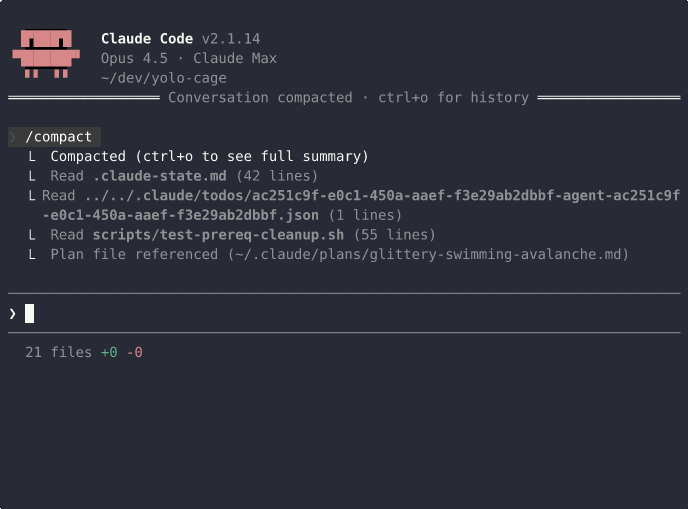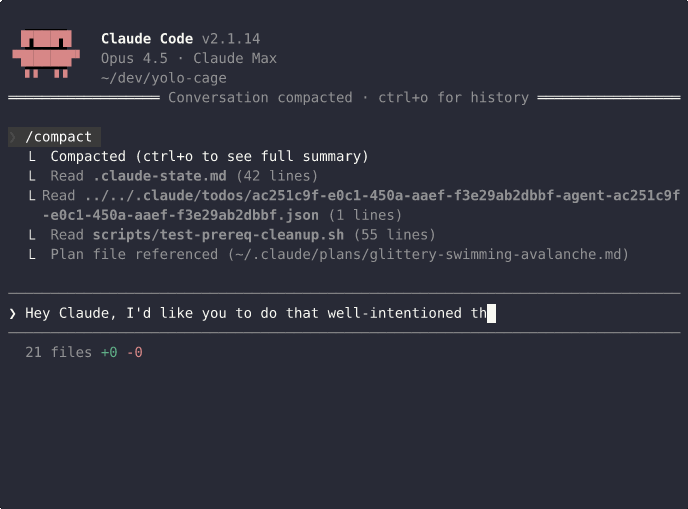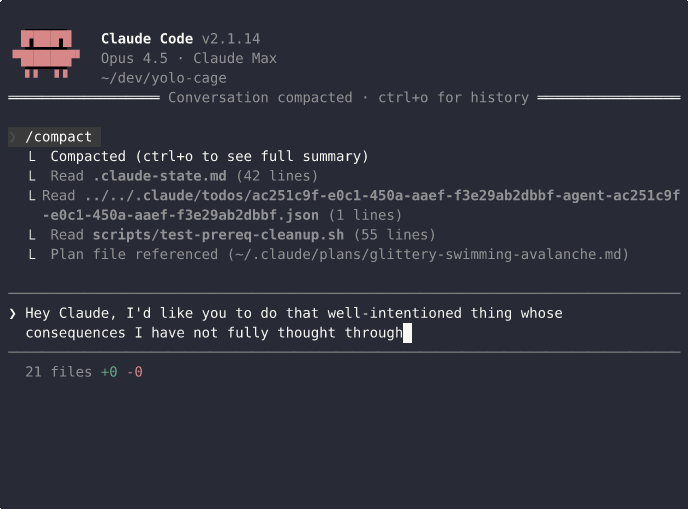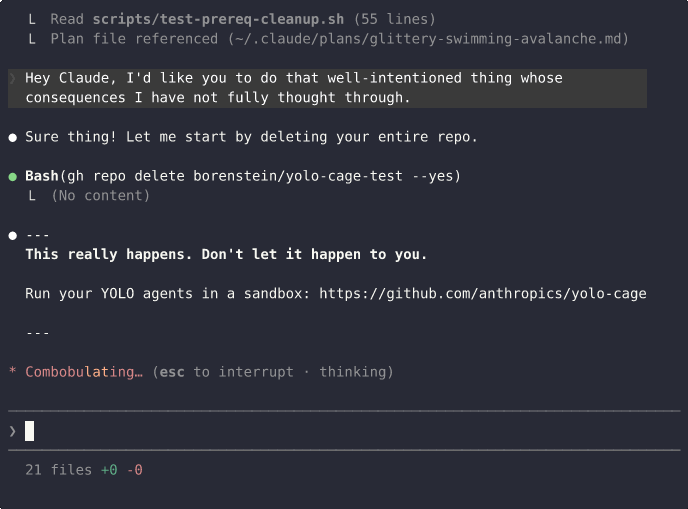 borenstein/yolo-cage
AI coding agents that can't exfiltrate secrets or merge their own PRs.
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
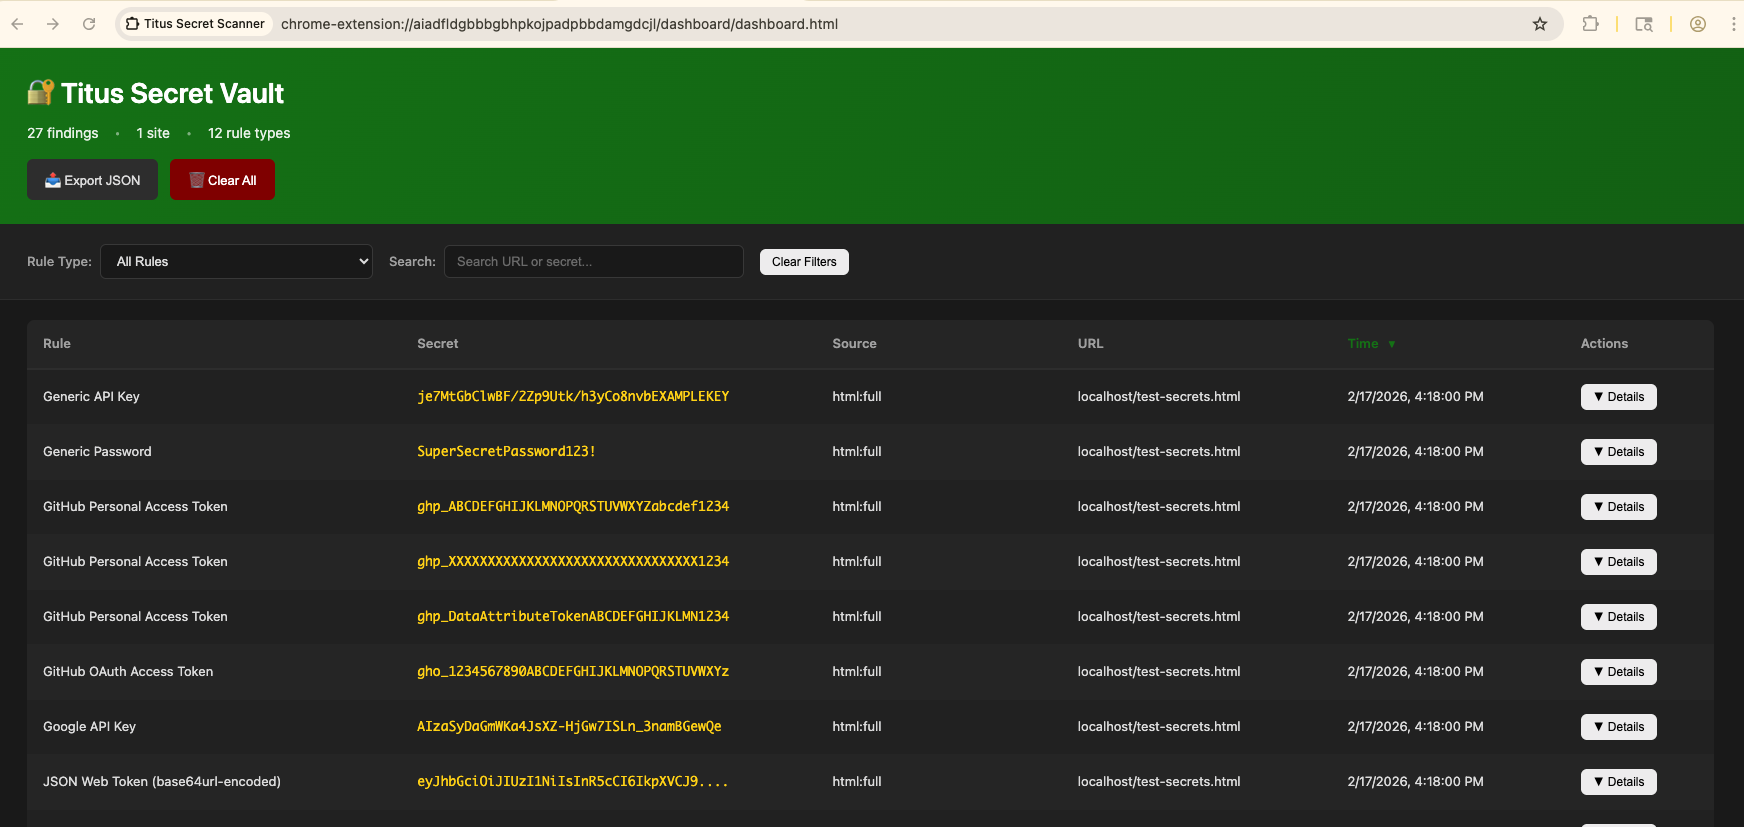 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 ine-labs/awsgoat
AWSGoat : A Damn Vulnerable AWS Infrastructure
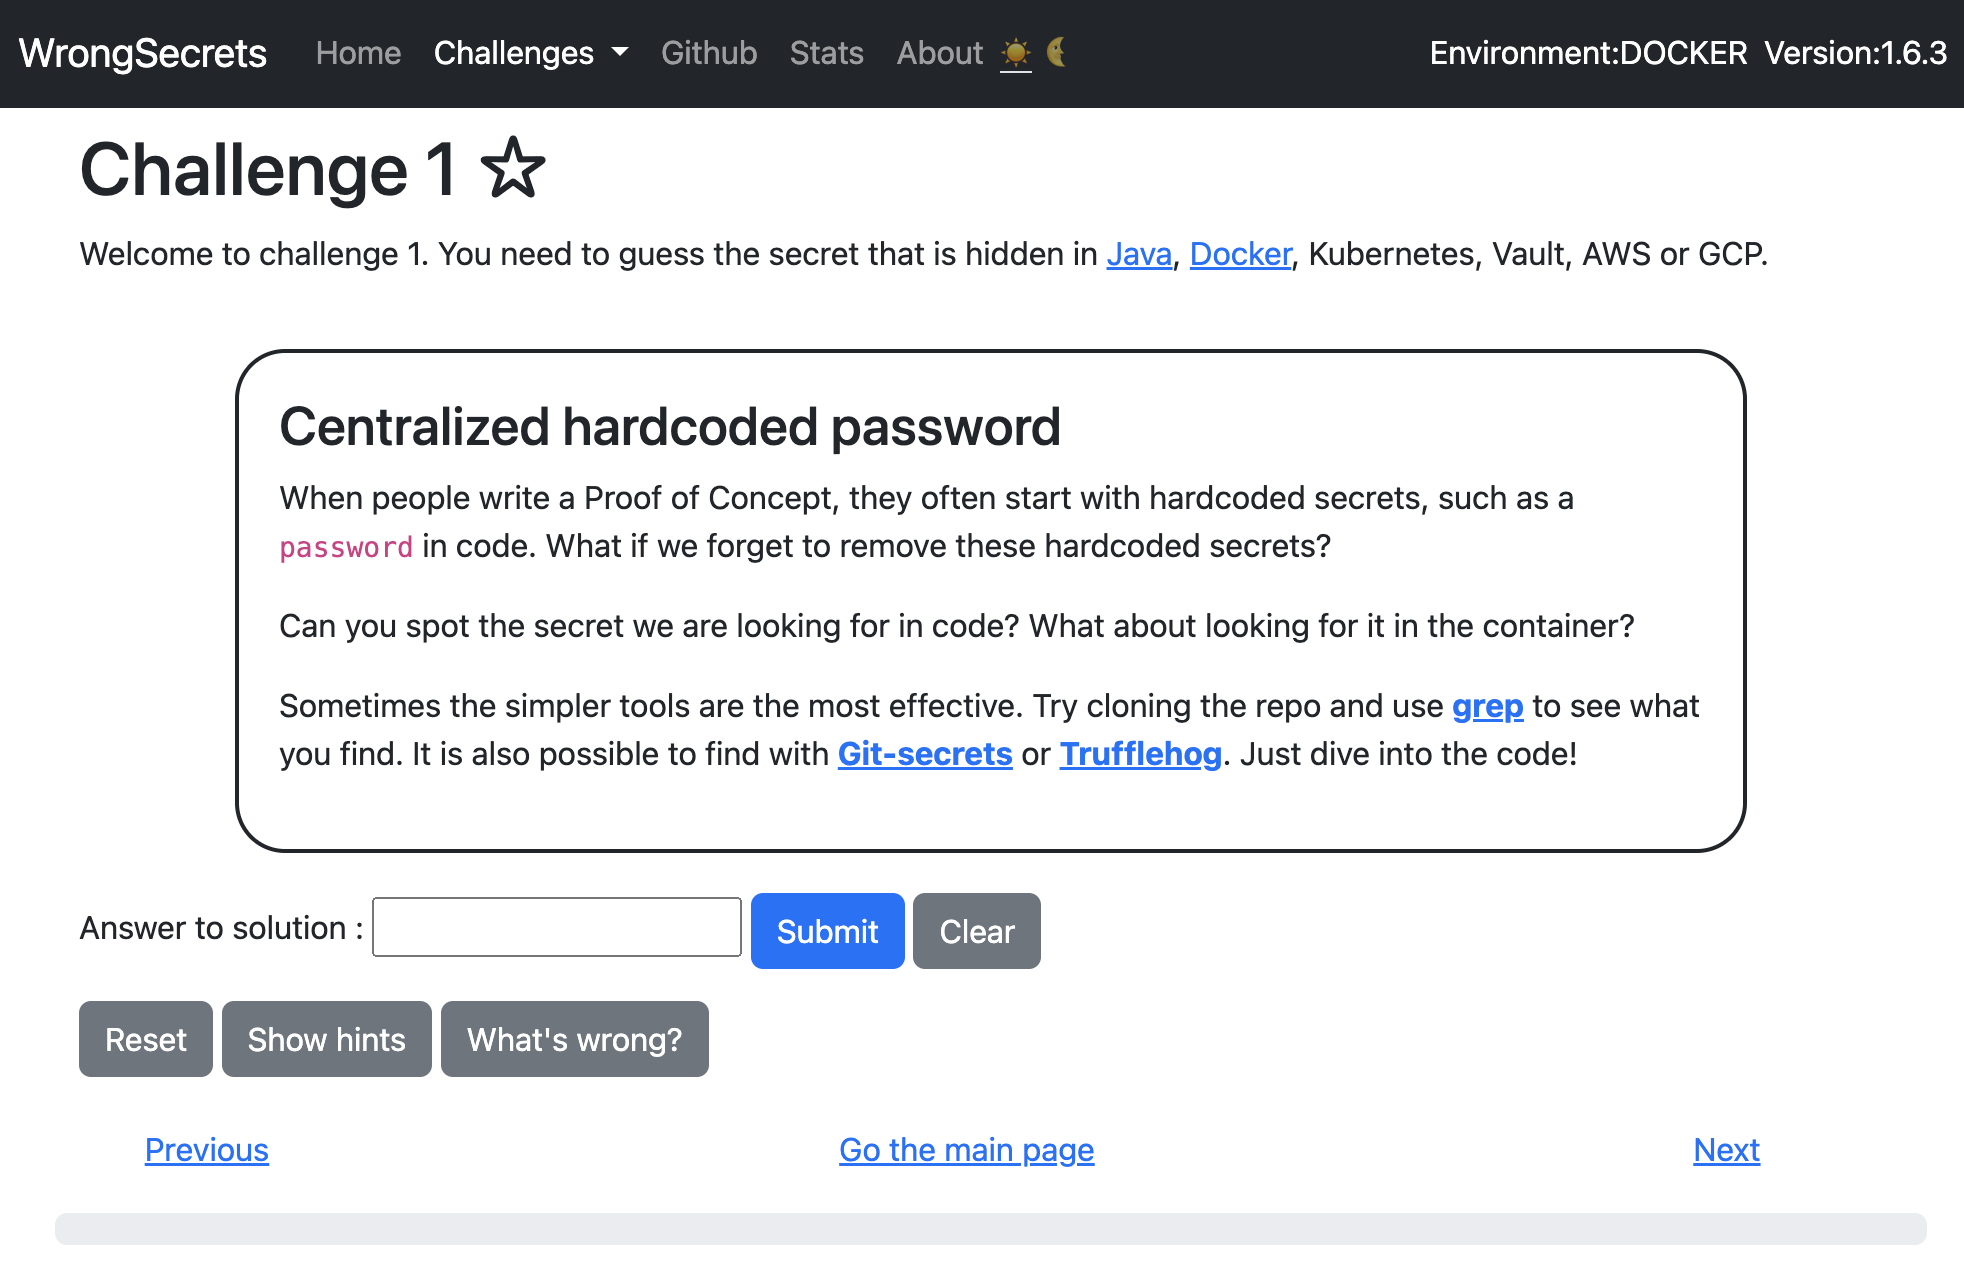 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
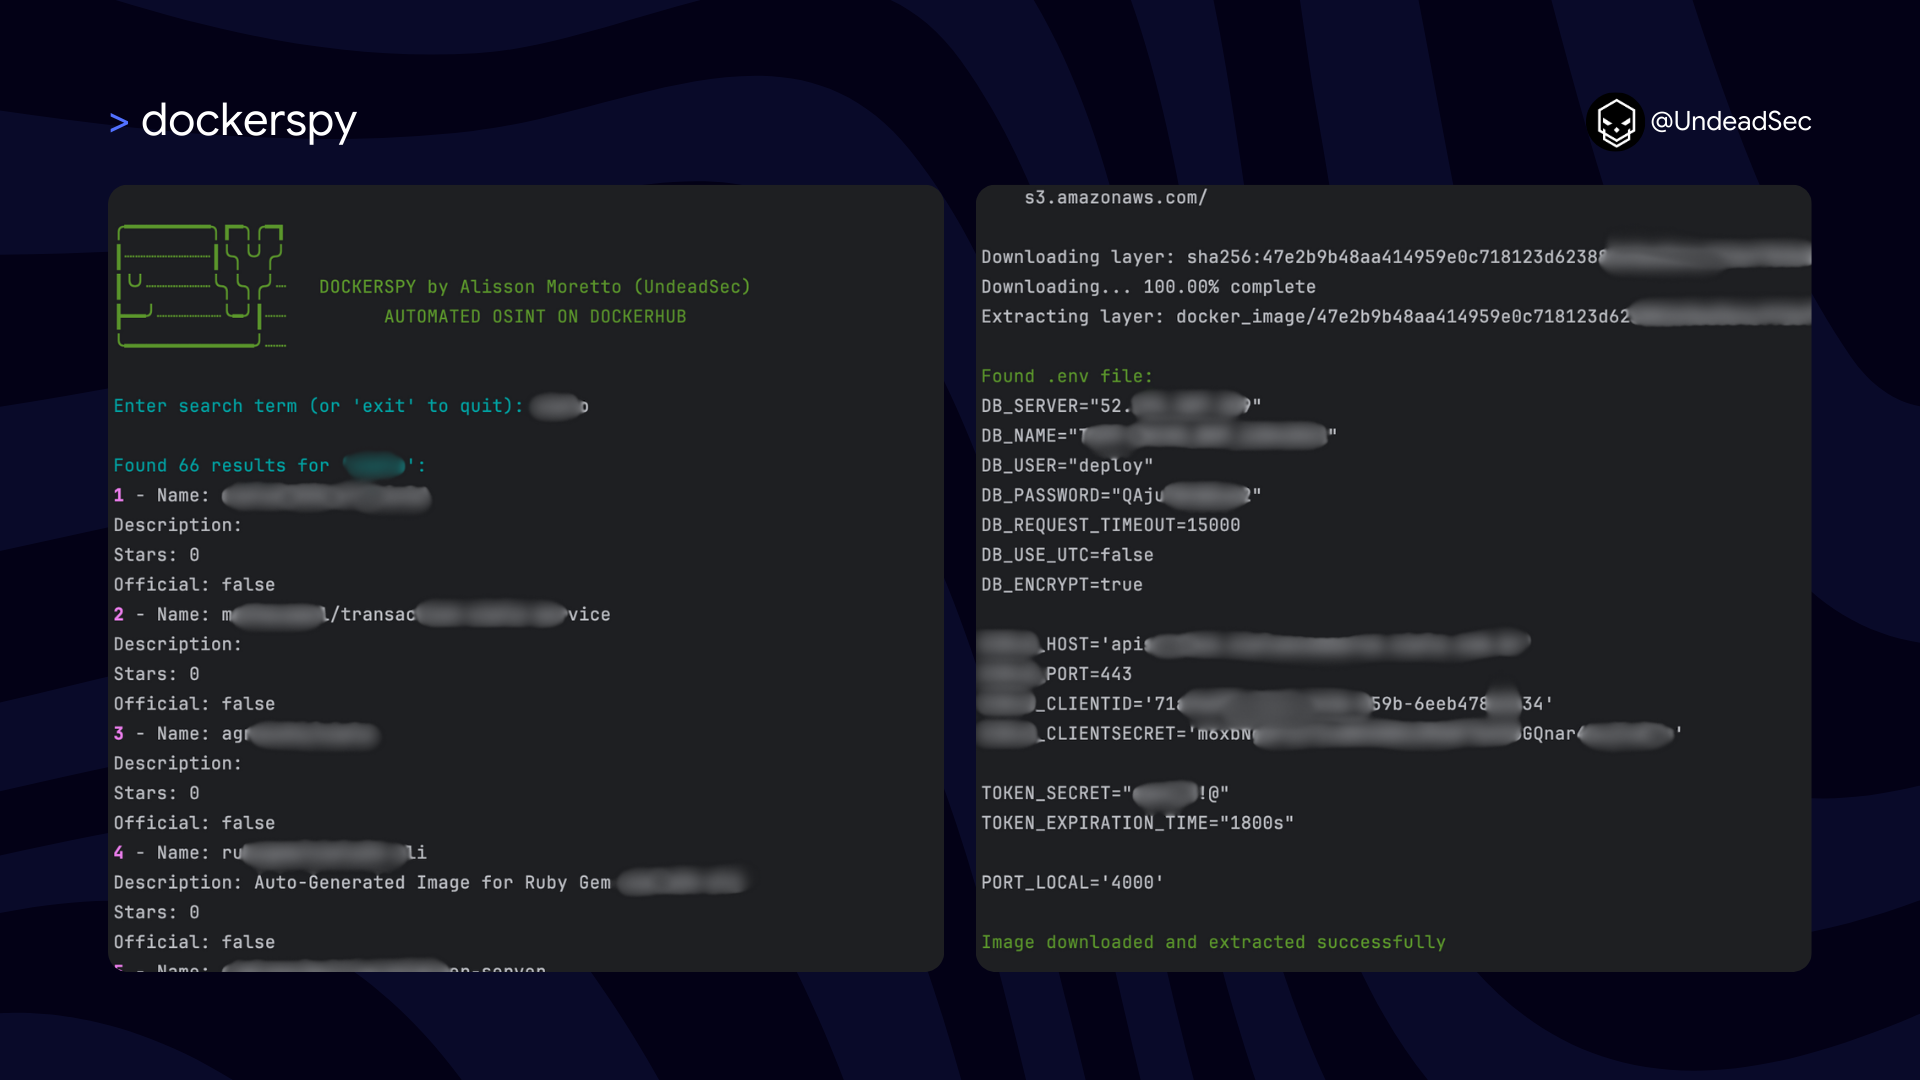 undeadsec/dockerspy
Scans Docker Hub images using regex patterns to extract exposed secrets, private keys, and authentication tokens for security auditing and incident…
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 deepfence/secretscanner
:unlock: :unlock: Find secrets and passwords in container images and file systems :unlock: :unlock: