
cli
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
cloud-infrastructure-securitycode-analysiscontainer-security+6
snyk/cliSnyk CLI scans and monitors your projects for security vulnerabilities.
 otsmane-ahmed/ci-supplychain-guard
Static analysis tool that detects malicious dependencies in CI/CD pipelines using pattern matching and AST analysis, with a traffic-light risk…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
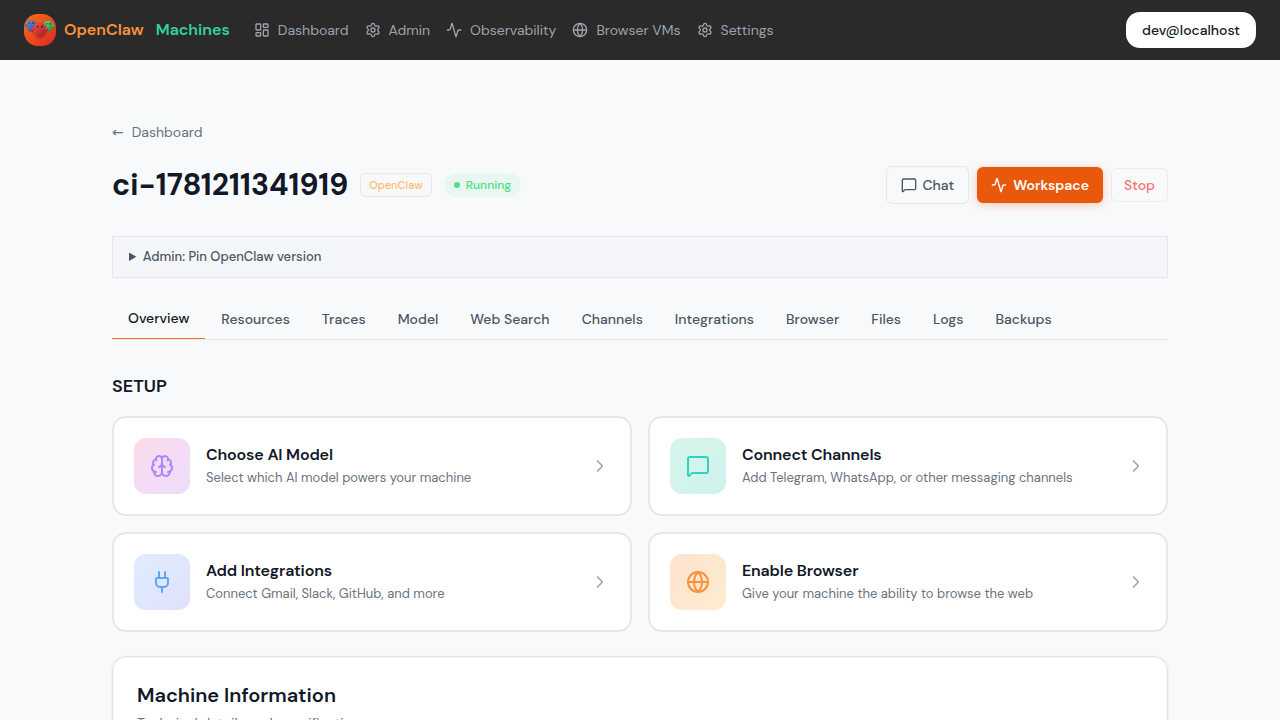 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
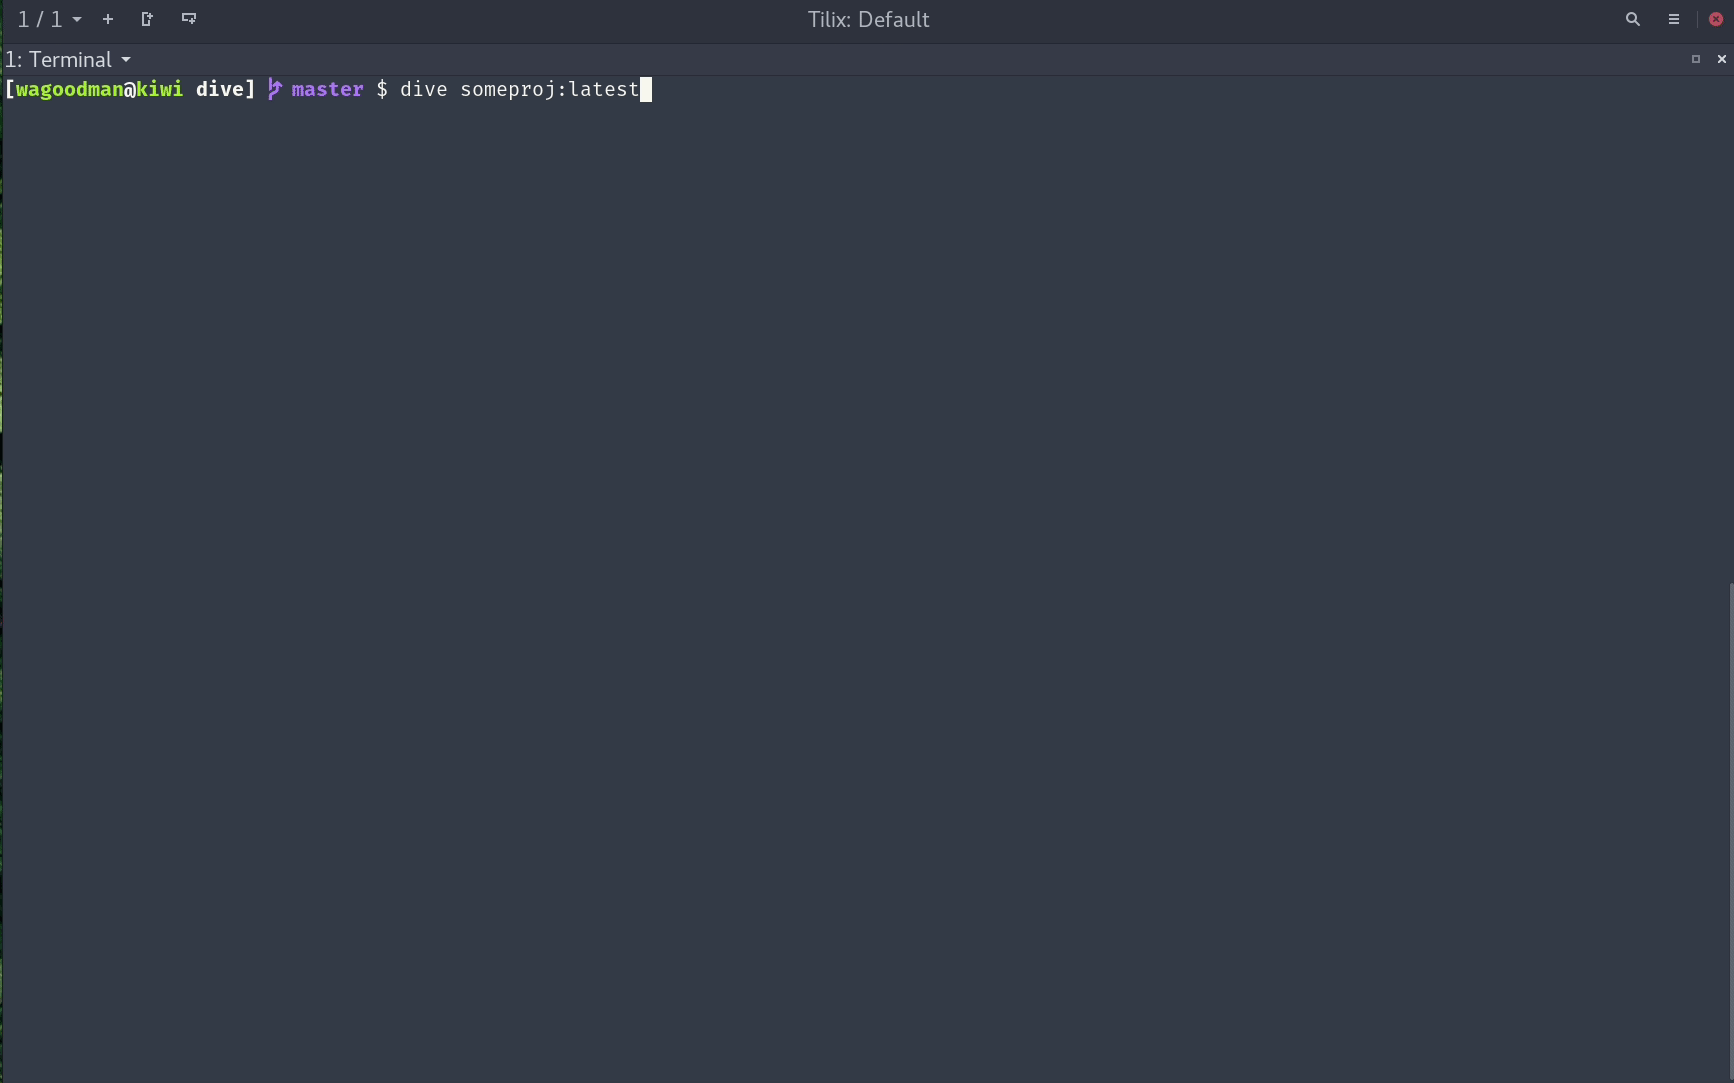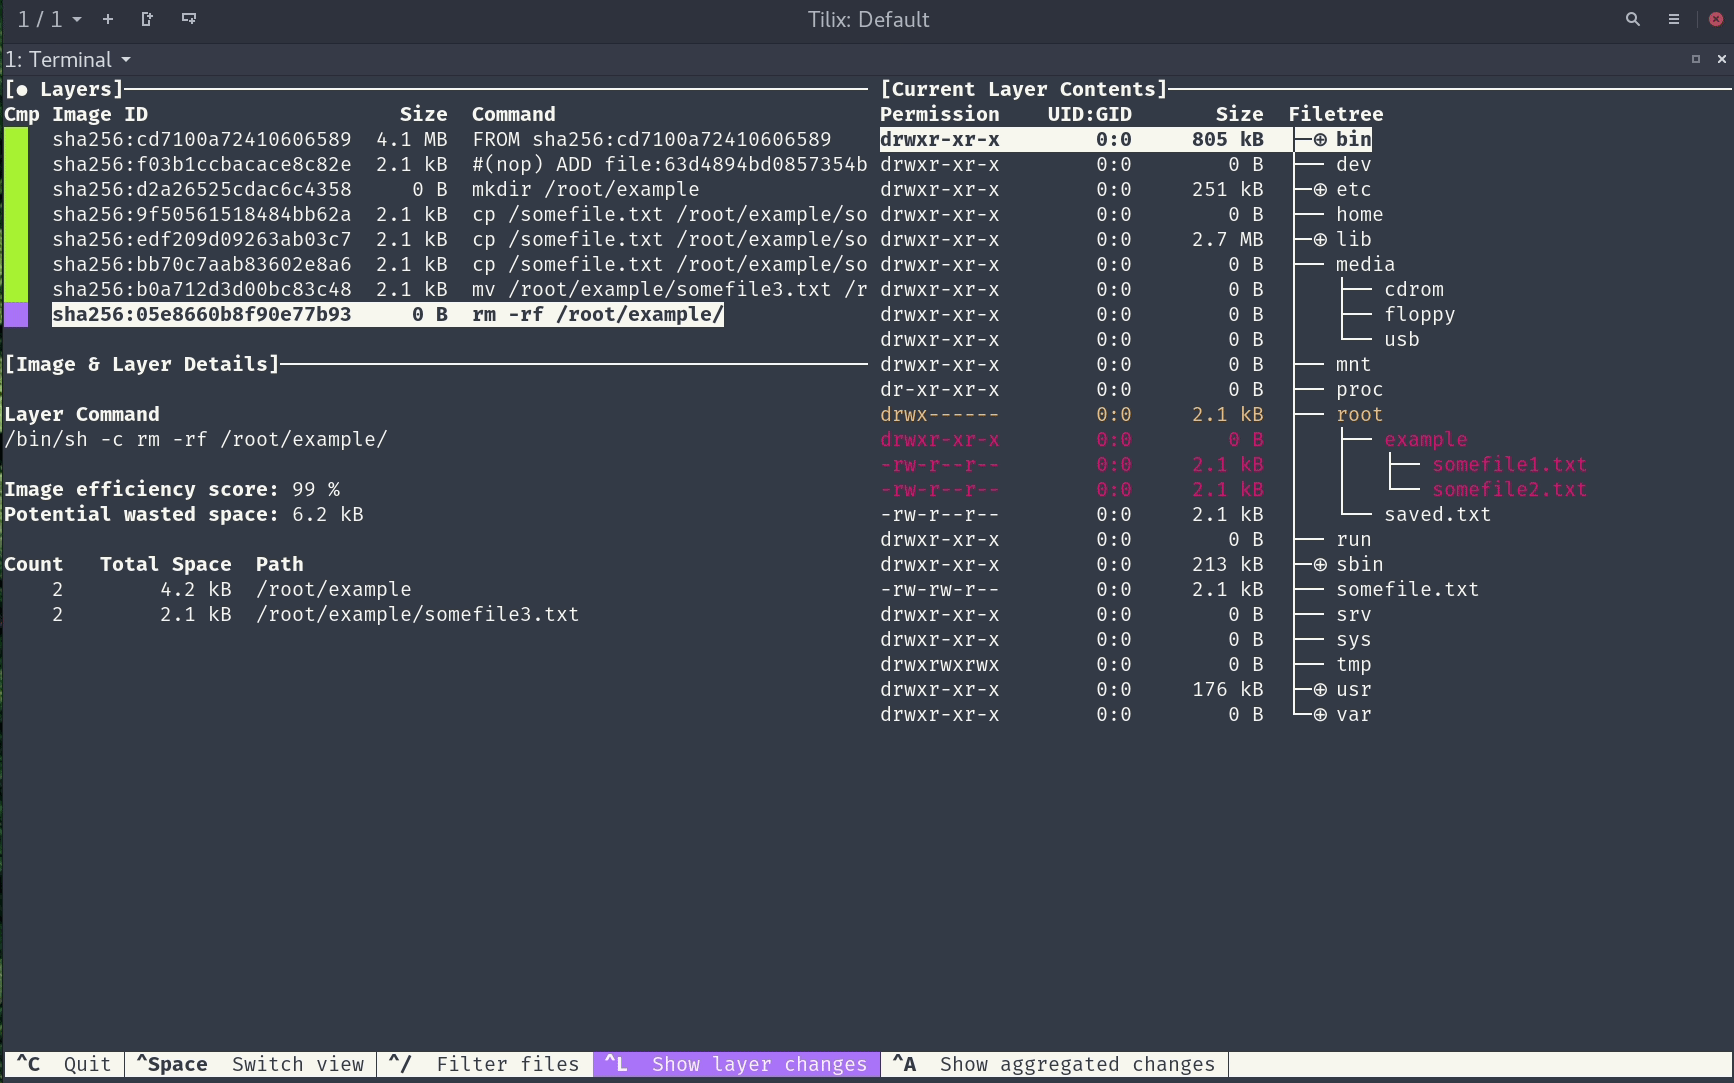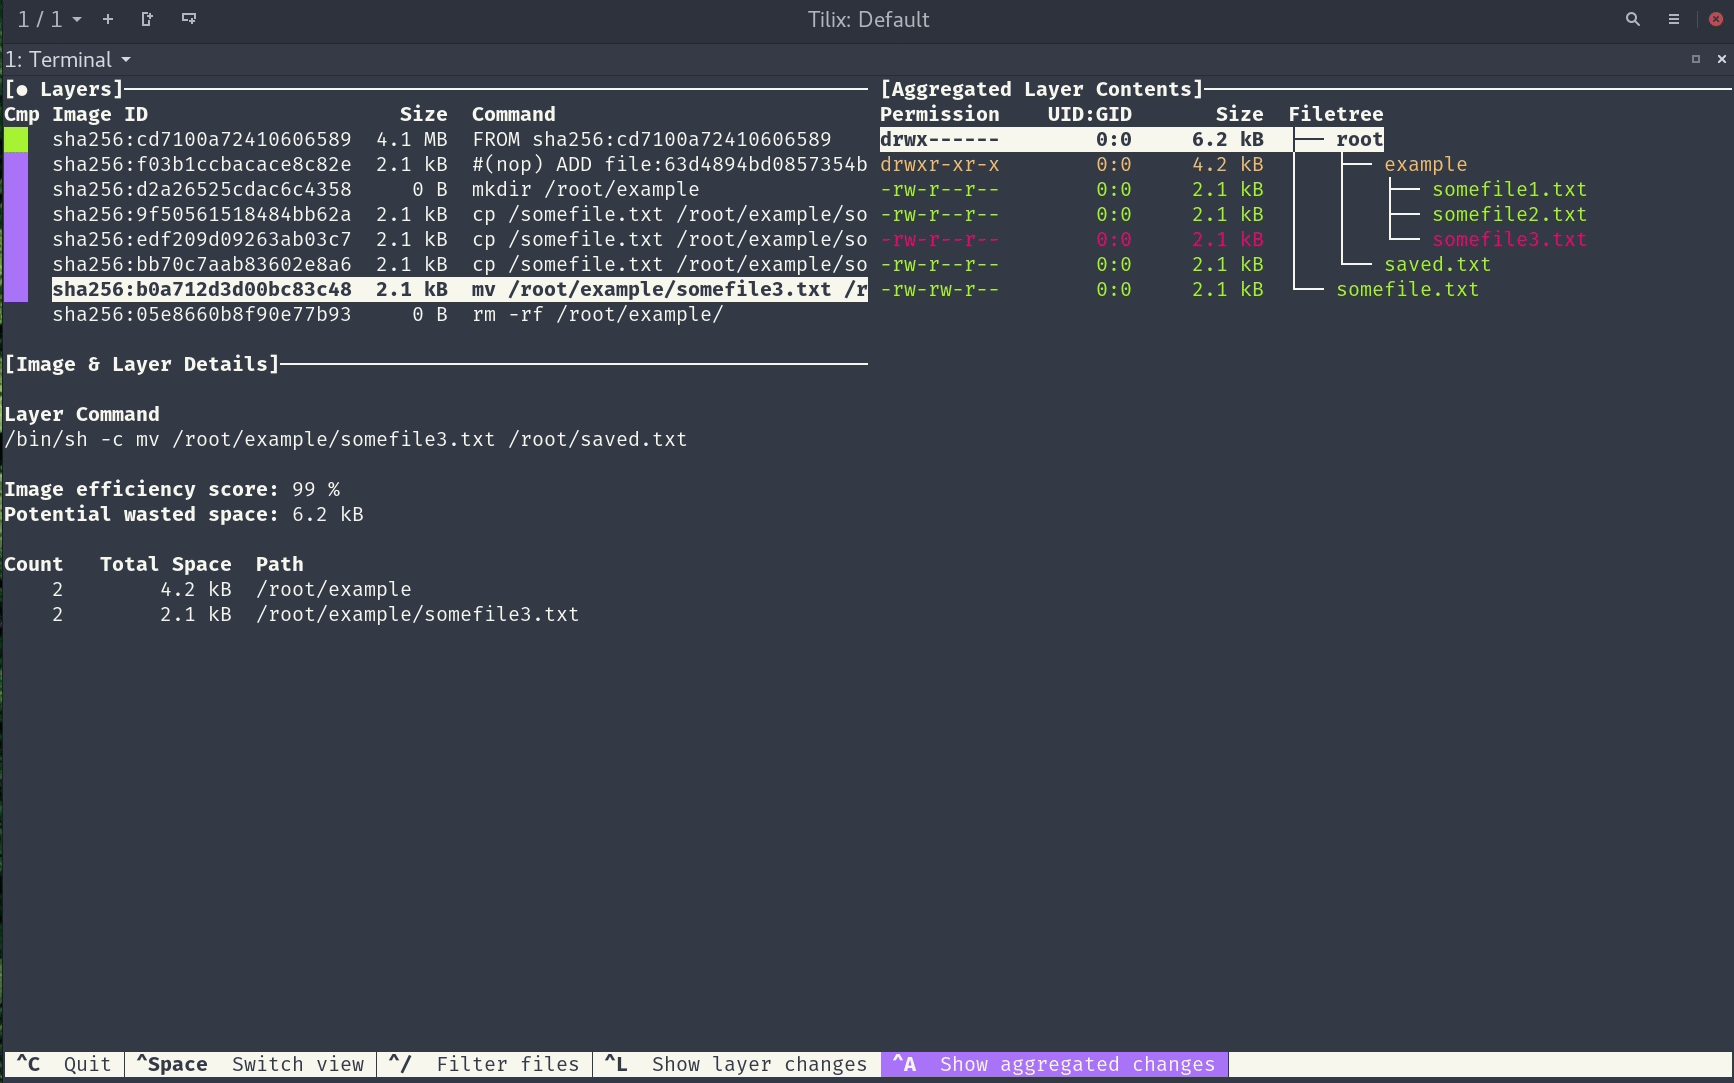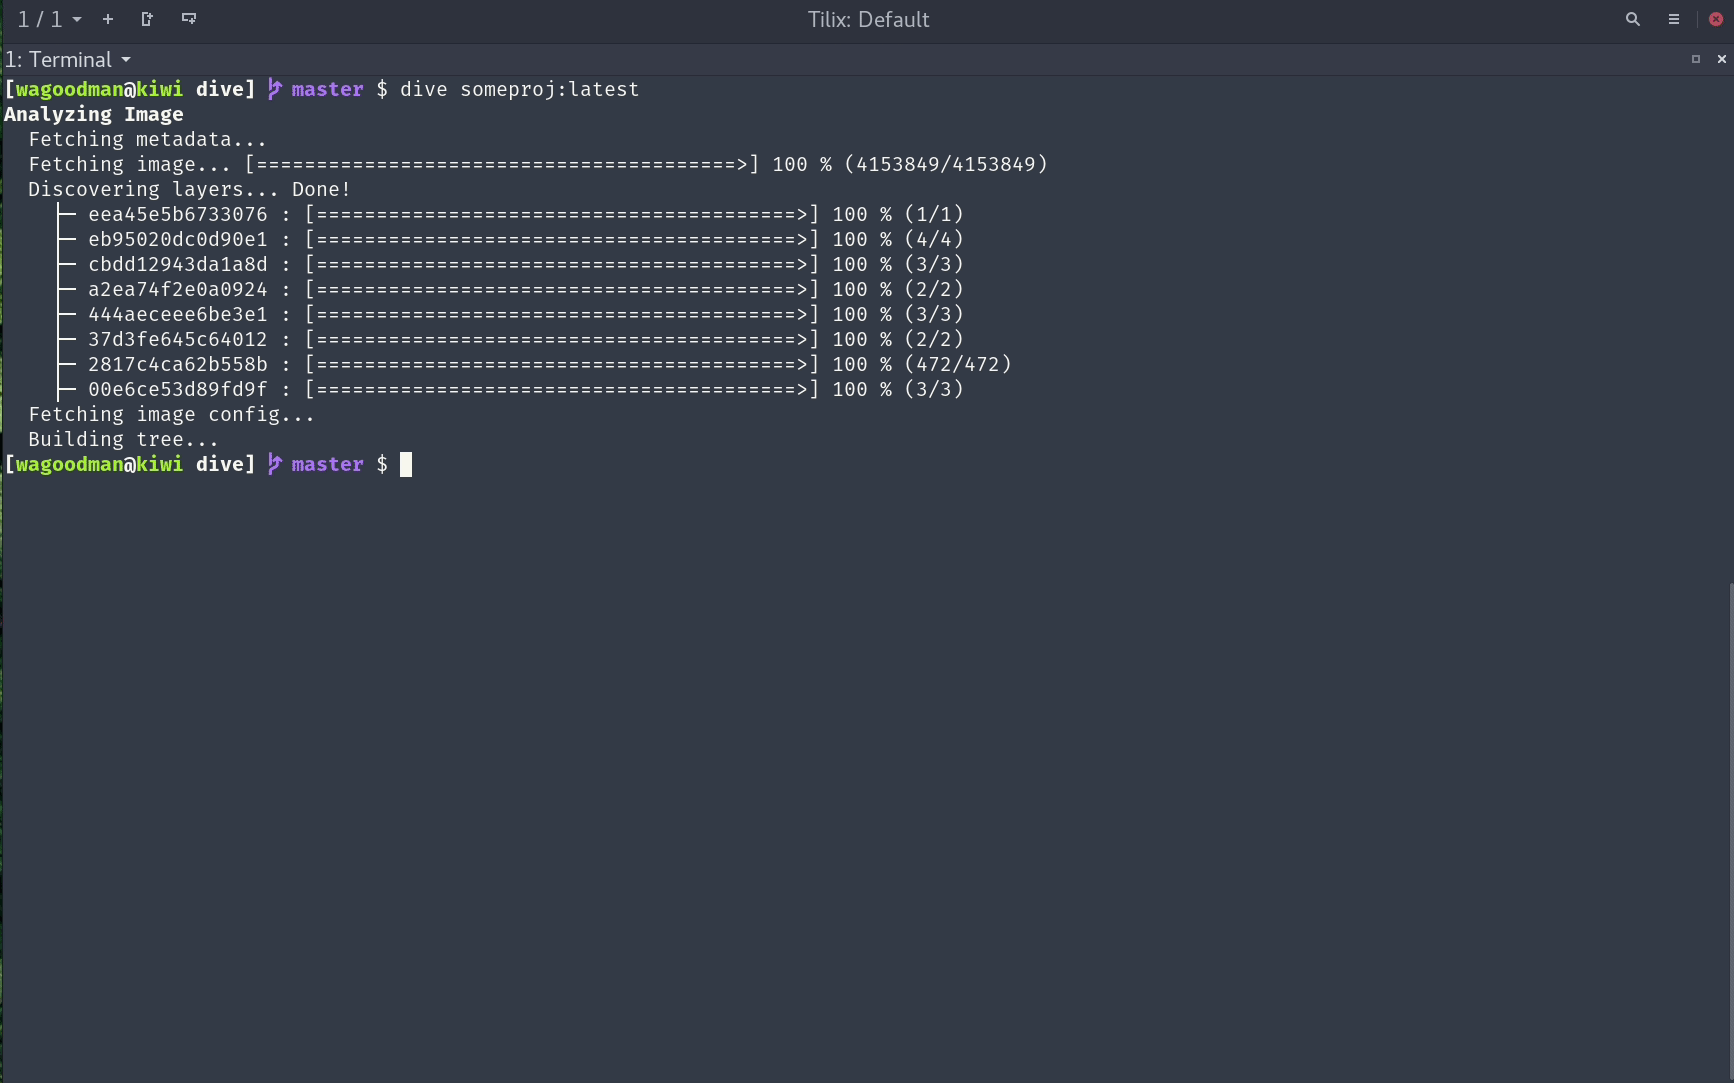 wagoodman/dive
A tool for exploring each layer in a docker image
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
 chaostoolkit/chaostoolkit-kubernetes
Kubernetes driver extension of the Chaos Toolkit probes and actions API
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 devopstoday11/tarian
Anti-Virus for K8s. Protect your Applications running on Kubernetes from malicious attacks with pre-registered source code, runtime processes…
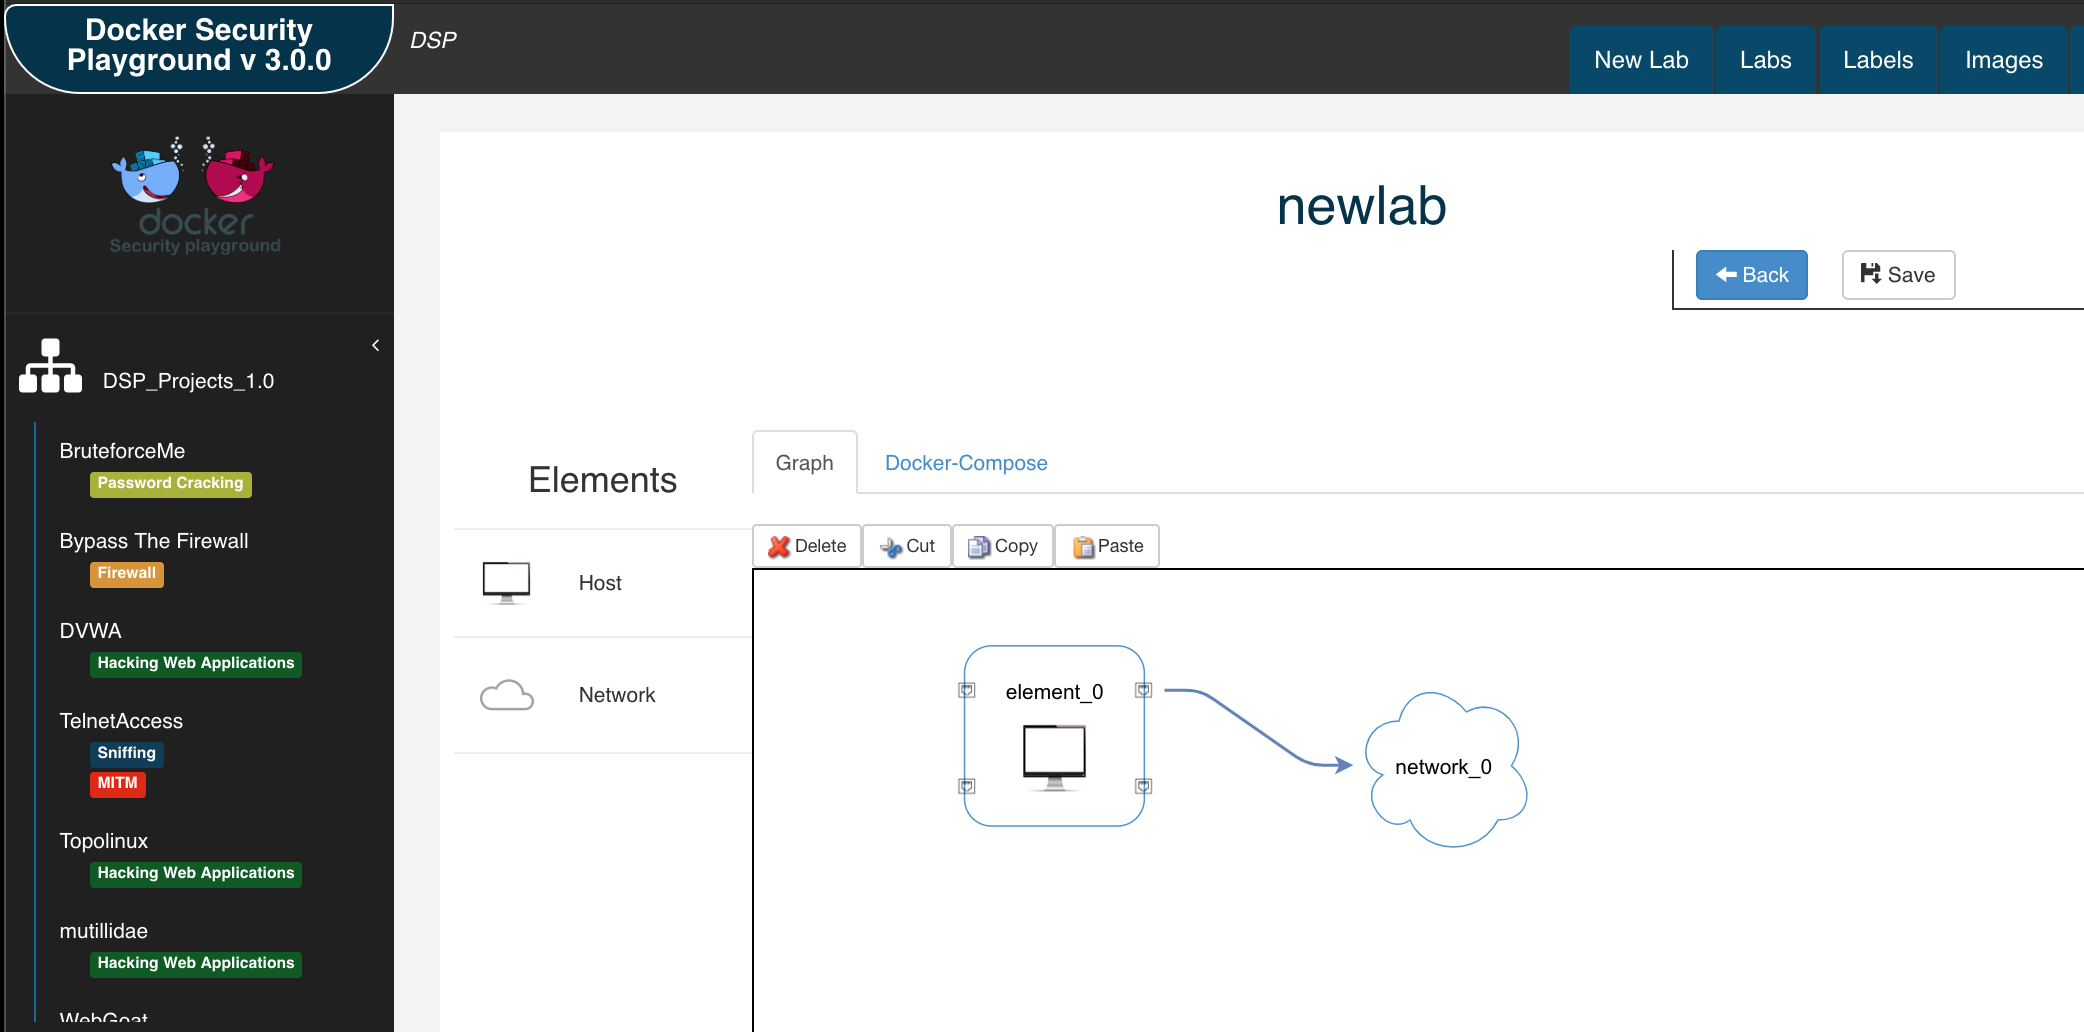 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
 chaosblade-io/chaosblade
An easy to use and powerful chaos engineering experiment toolkit.(阿里巴巴开源的一款简单易用、功能强大的混沌实验注入工具)
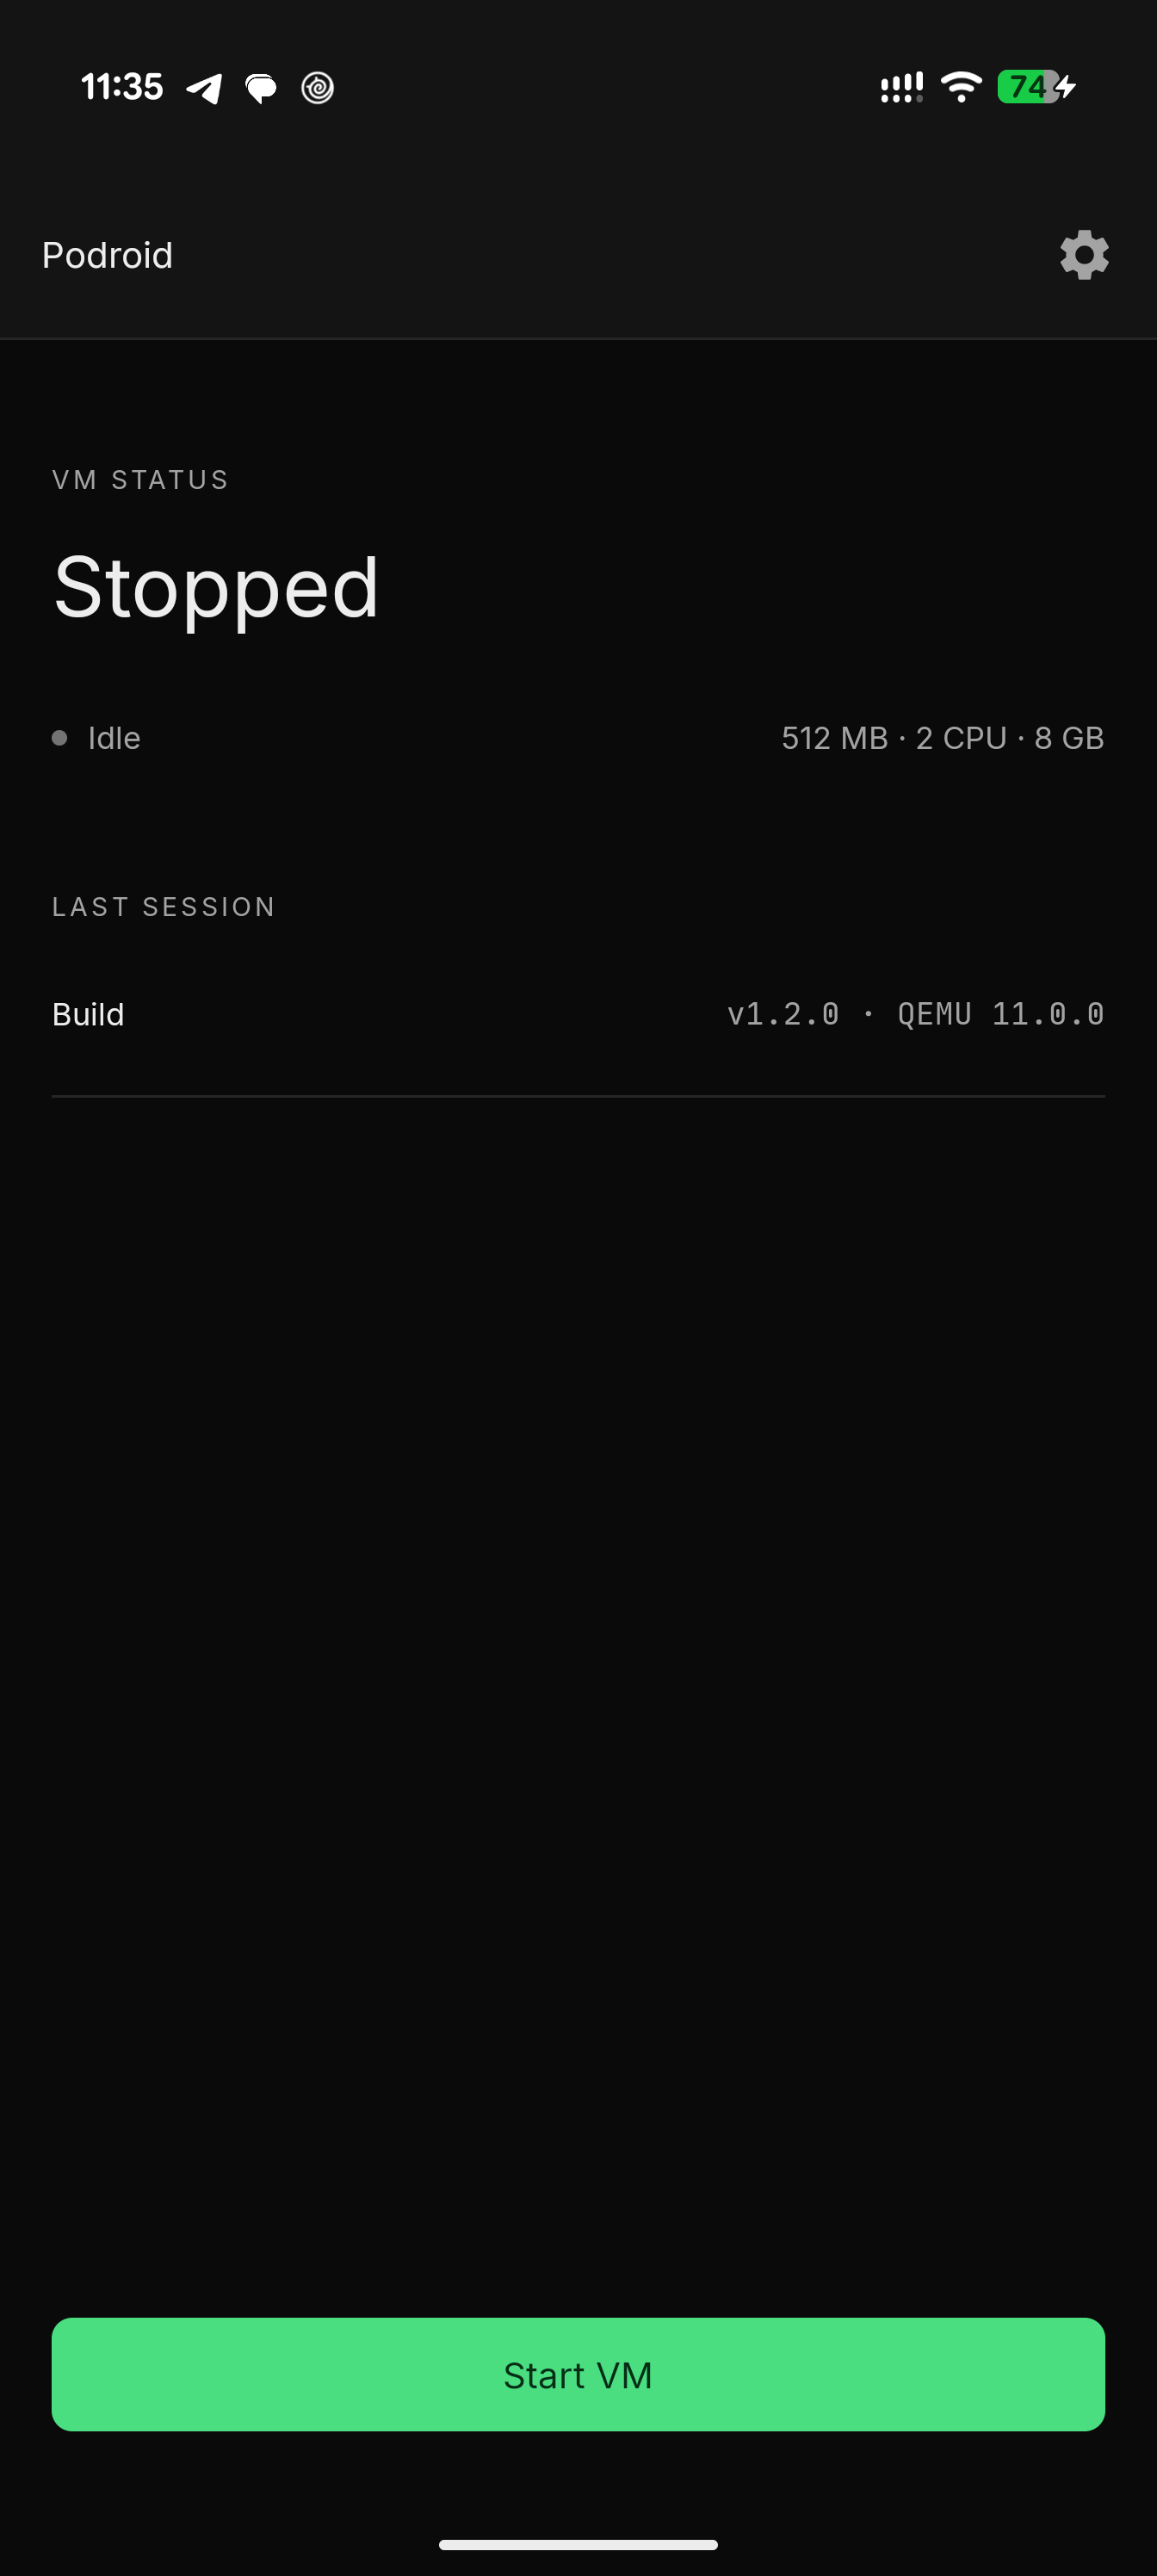 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
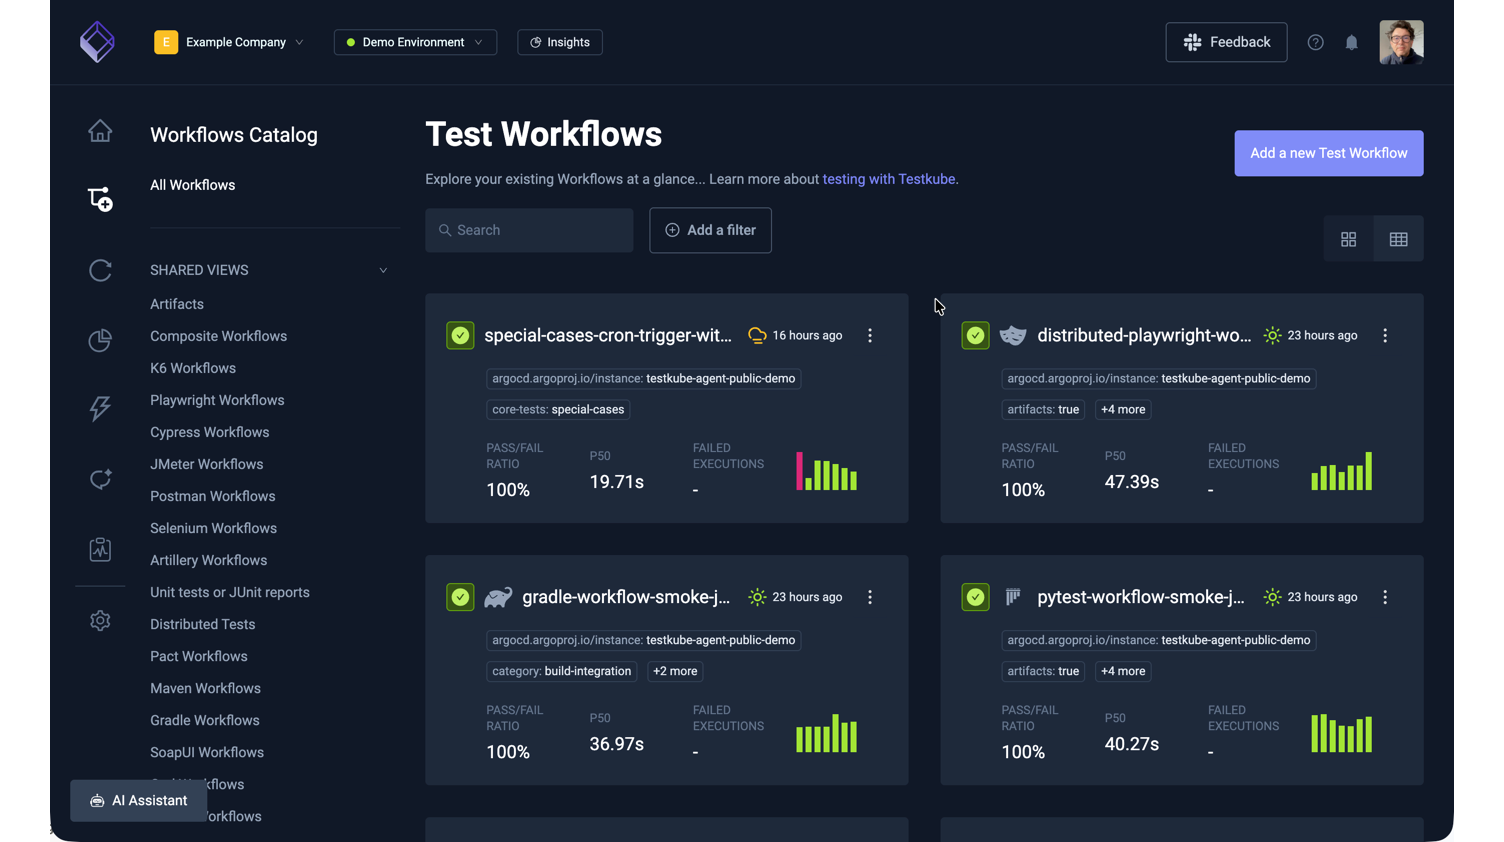 kubeshop/testkube
☸️ The Open Testing Platform for AI-Driven Engineering Teams
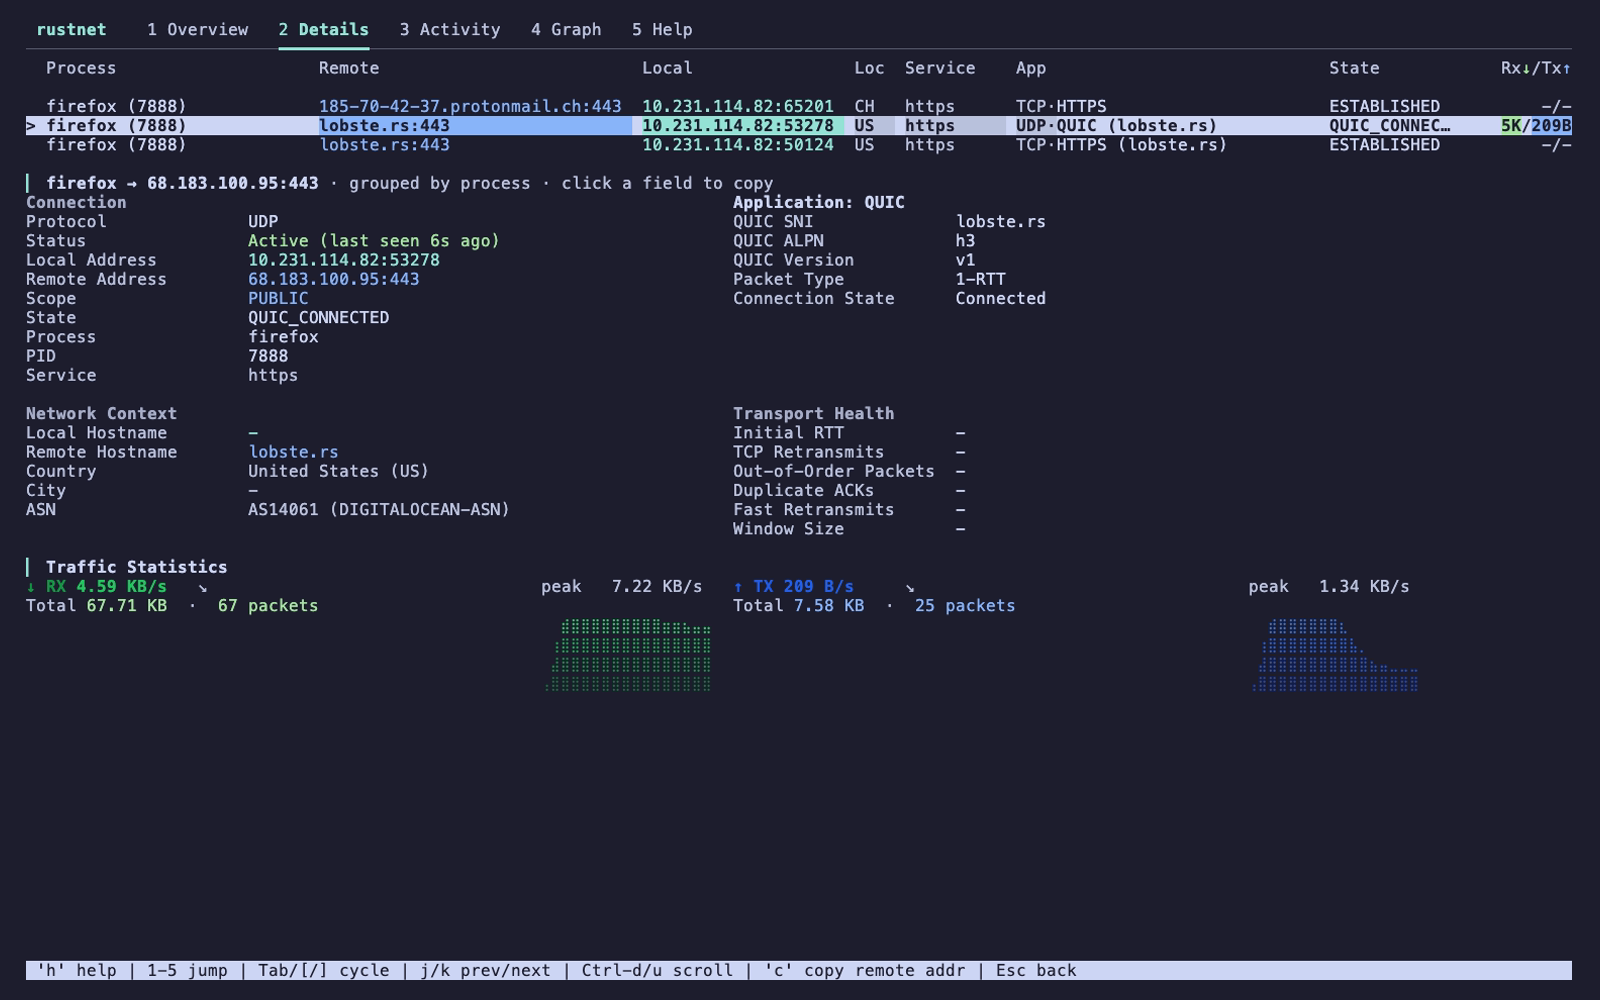 domcyrus/rustnet
Per-process network monitoring for your terminal with deep packet inspection. Cross-platform, sandboxed.
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…