
kubescape
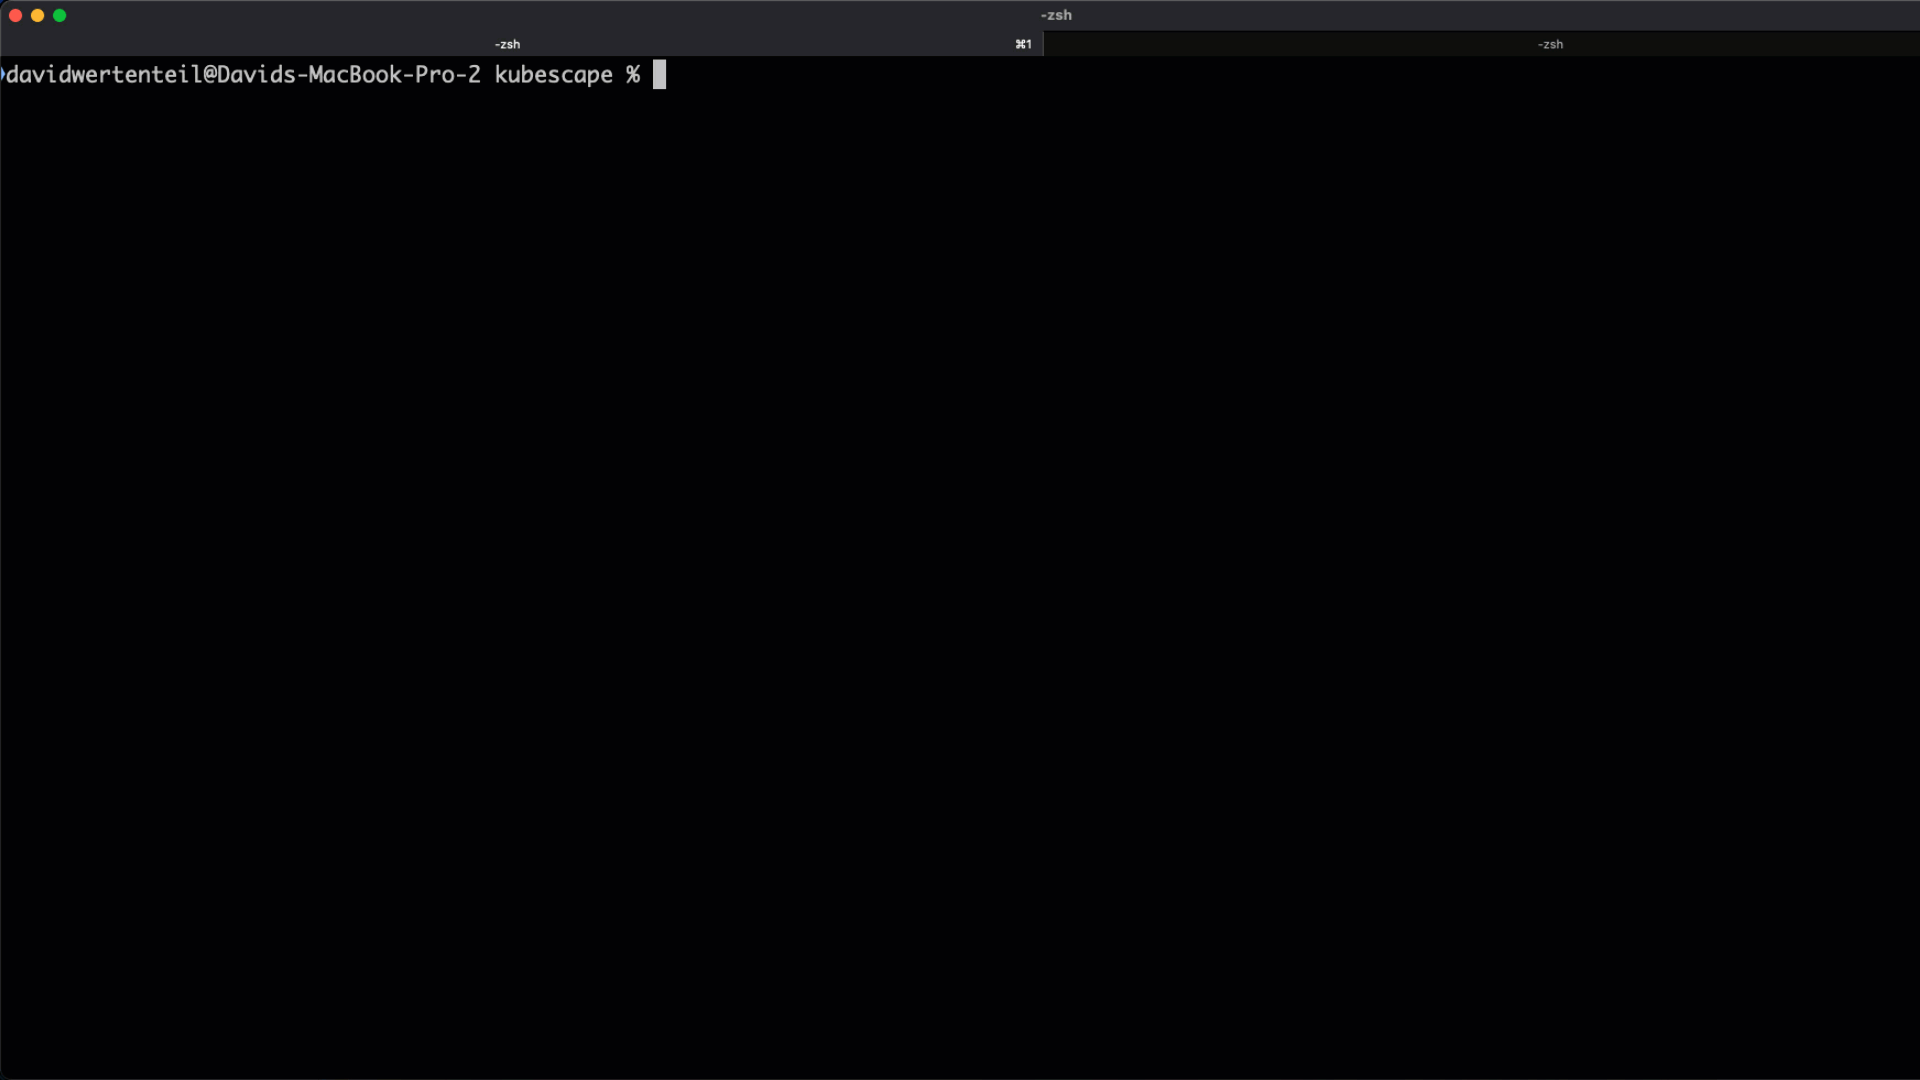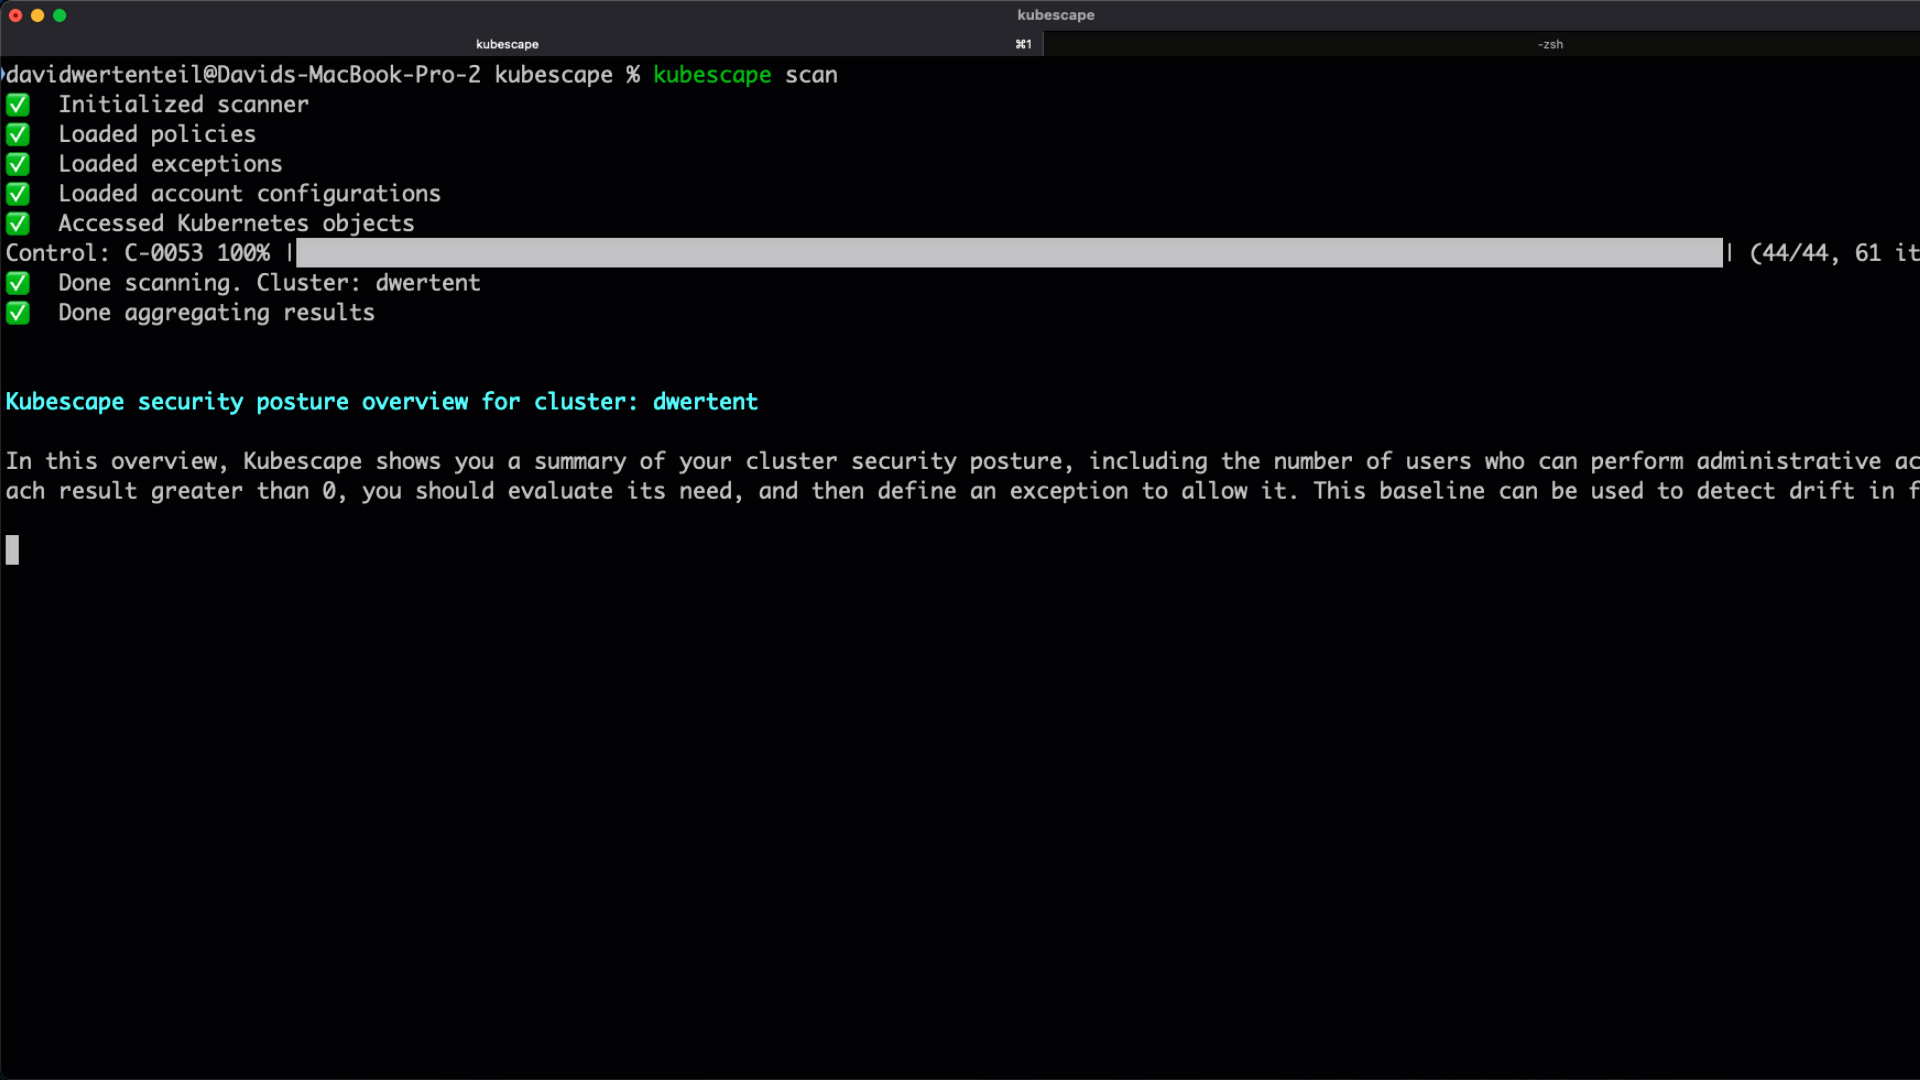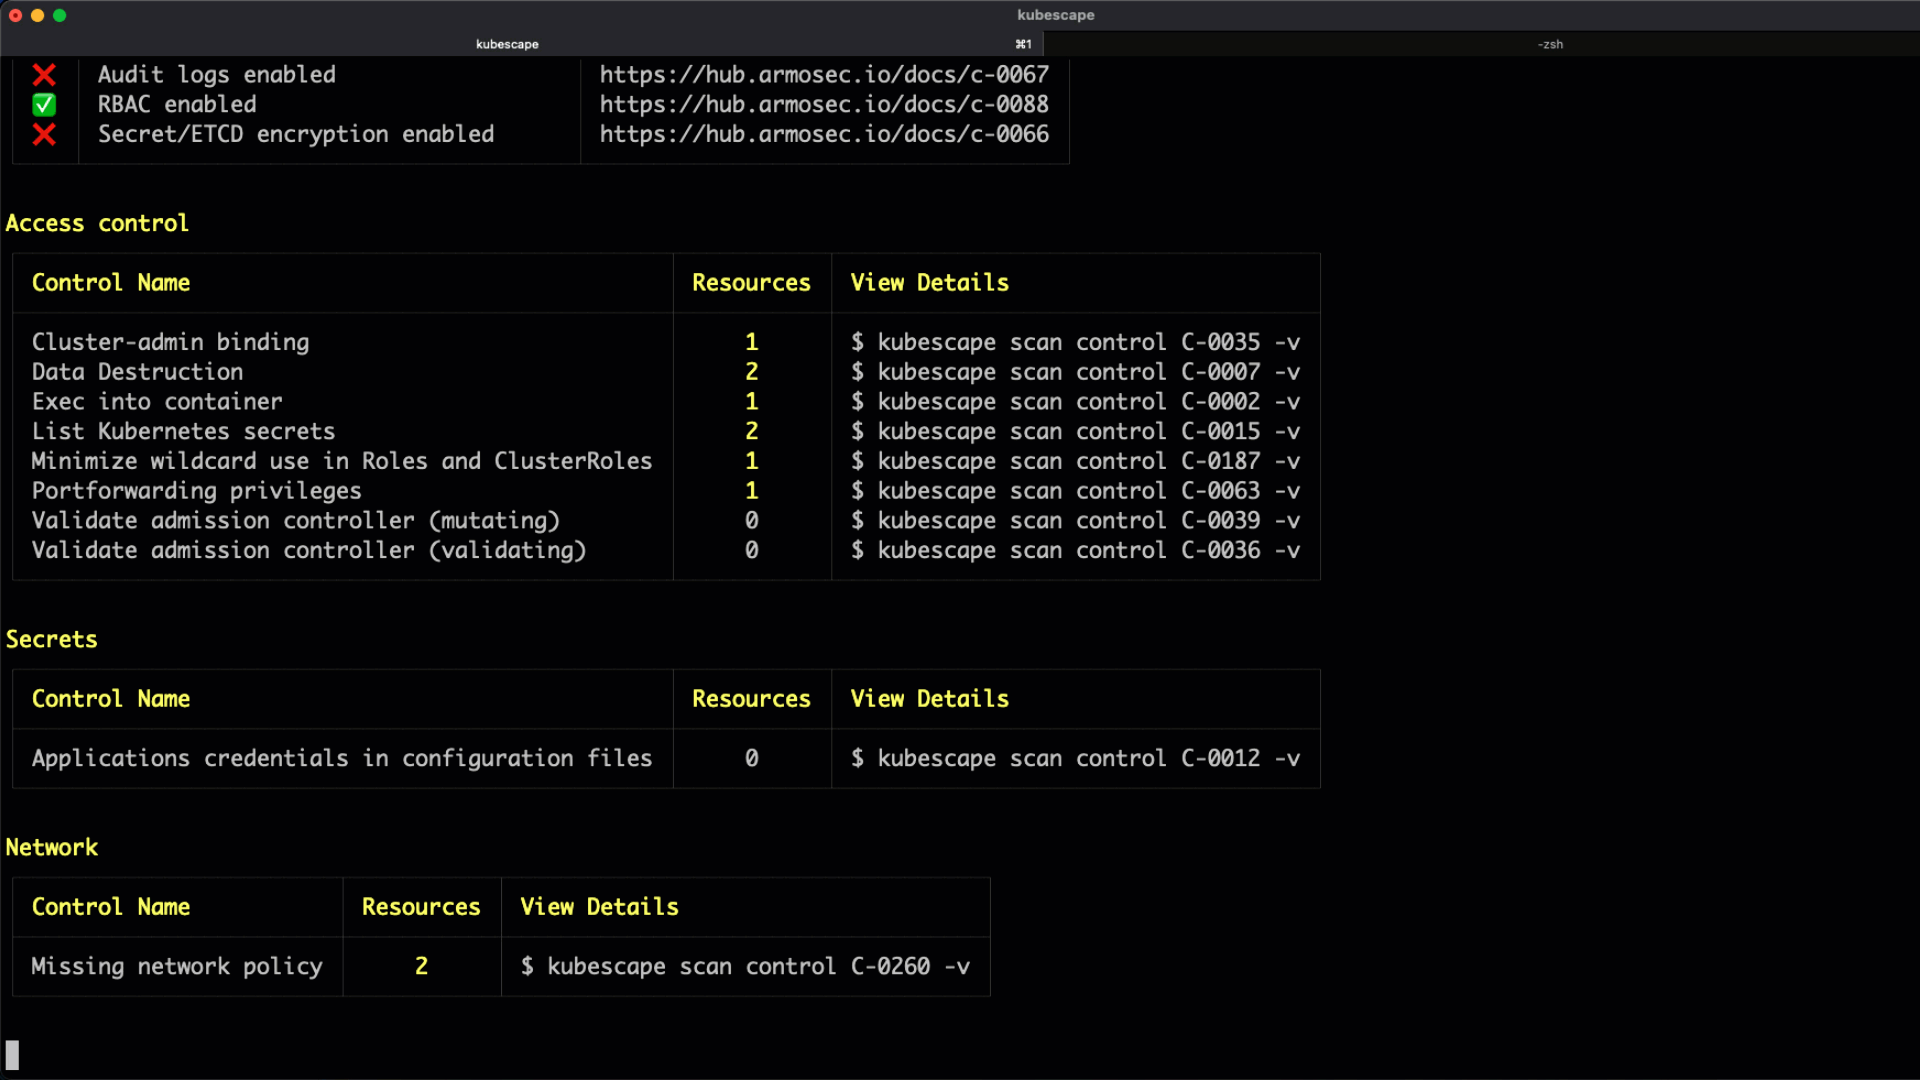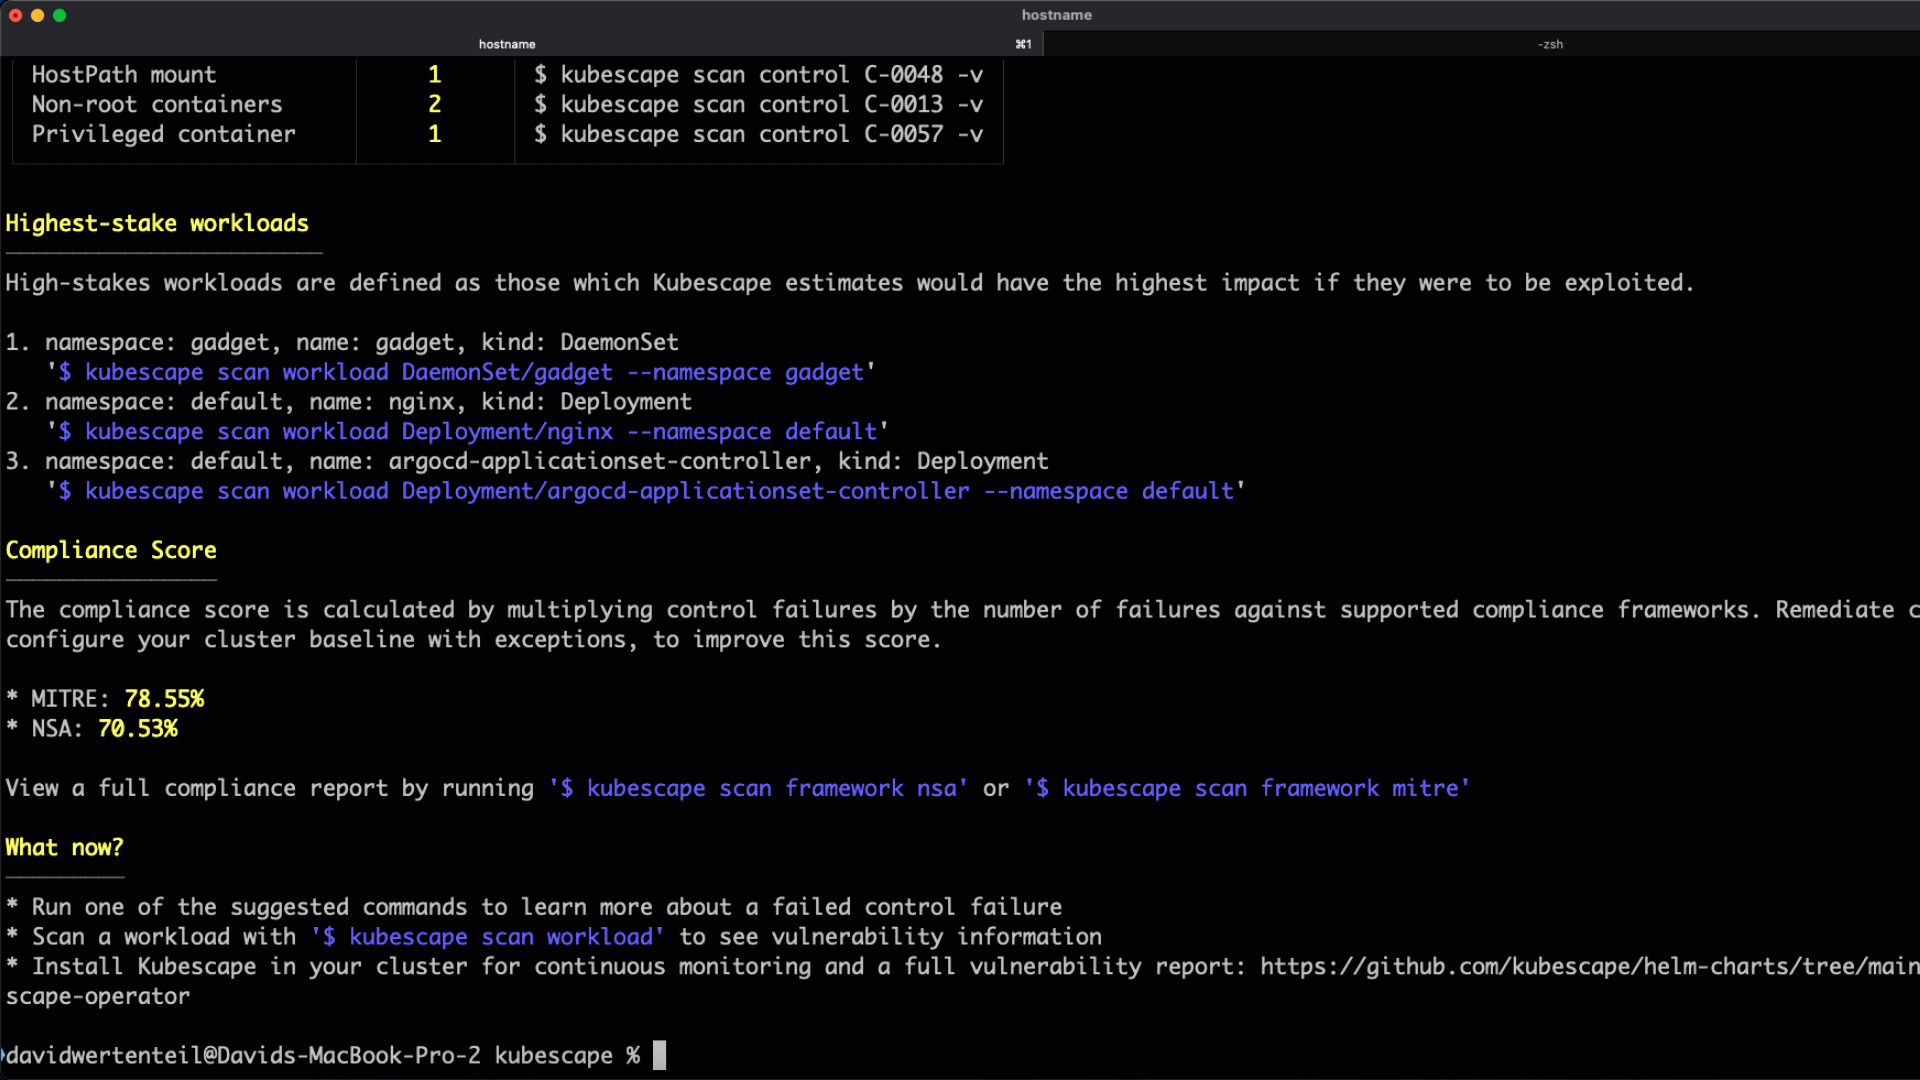
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…

Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…

Vulnerable Environment and Exploit for CVE-2024-53677

Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…

Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.

Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…

:unlock: :unlock: Find secrets and passwords in container images and file systems :unlock: :unlock:

SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!

Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…

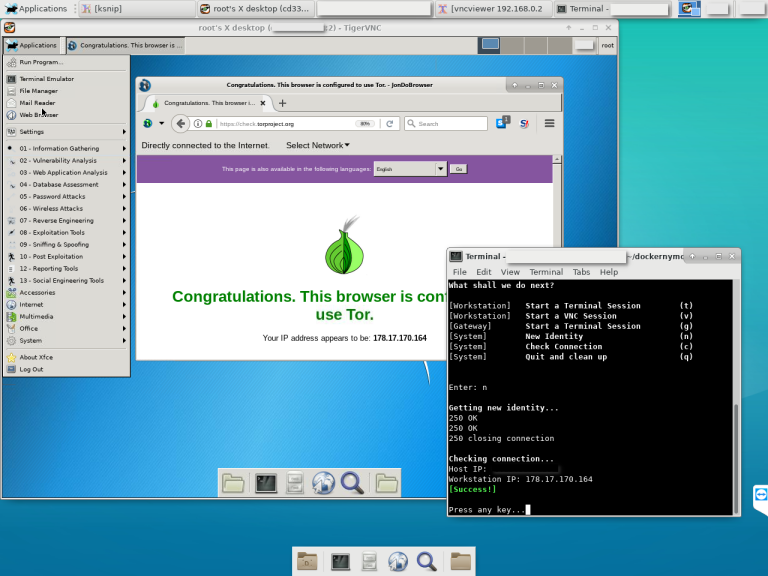
A script used to create a whonix like gateway/workstation environment with docker containers.

Real-time cloud-native runtime security agent for Linux that monitors syscalls and container/Kubernetes metadata to detect anomalous behavior and…

Shell script to detect TanStack npm supply chain attack indicators (CVE-2026-45321 / GHSA-g7cv-rxg3-hmpx)

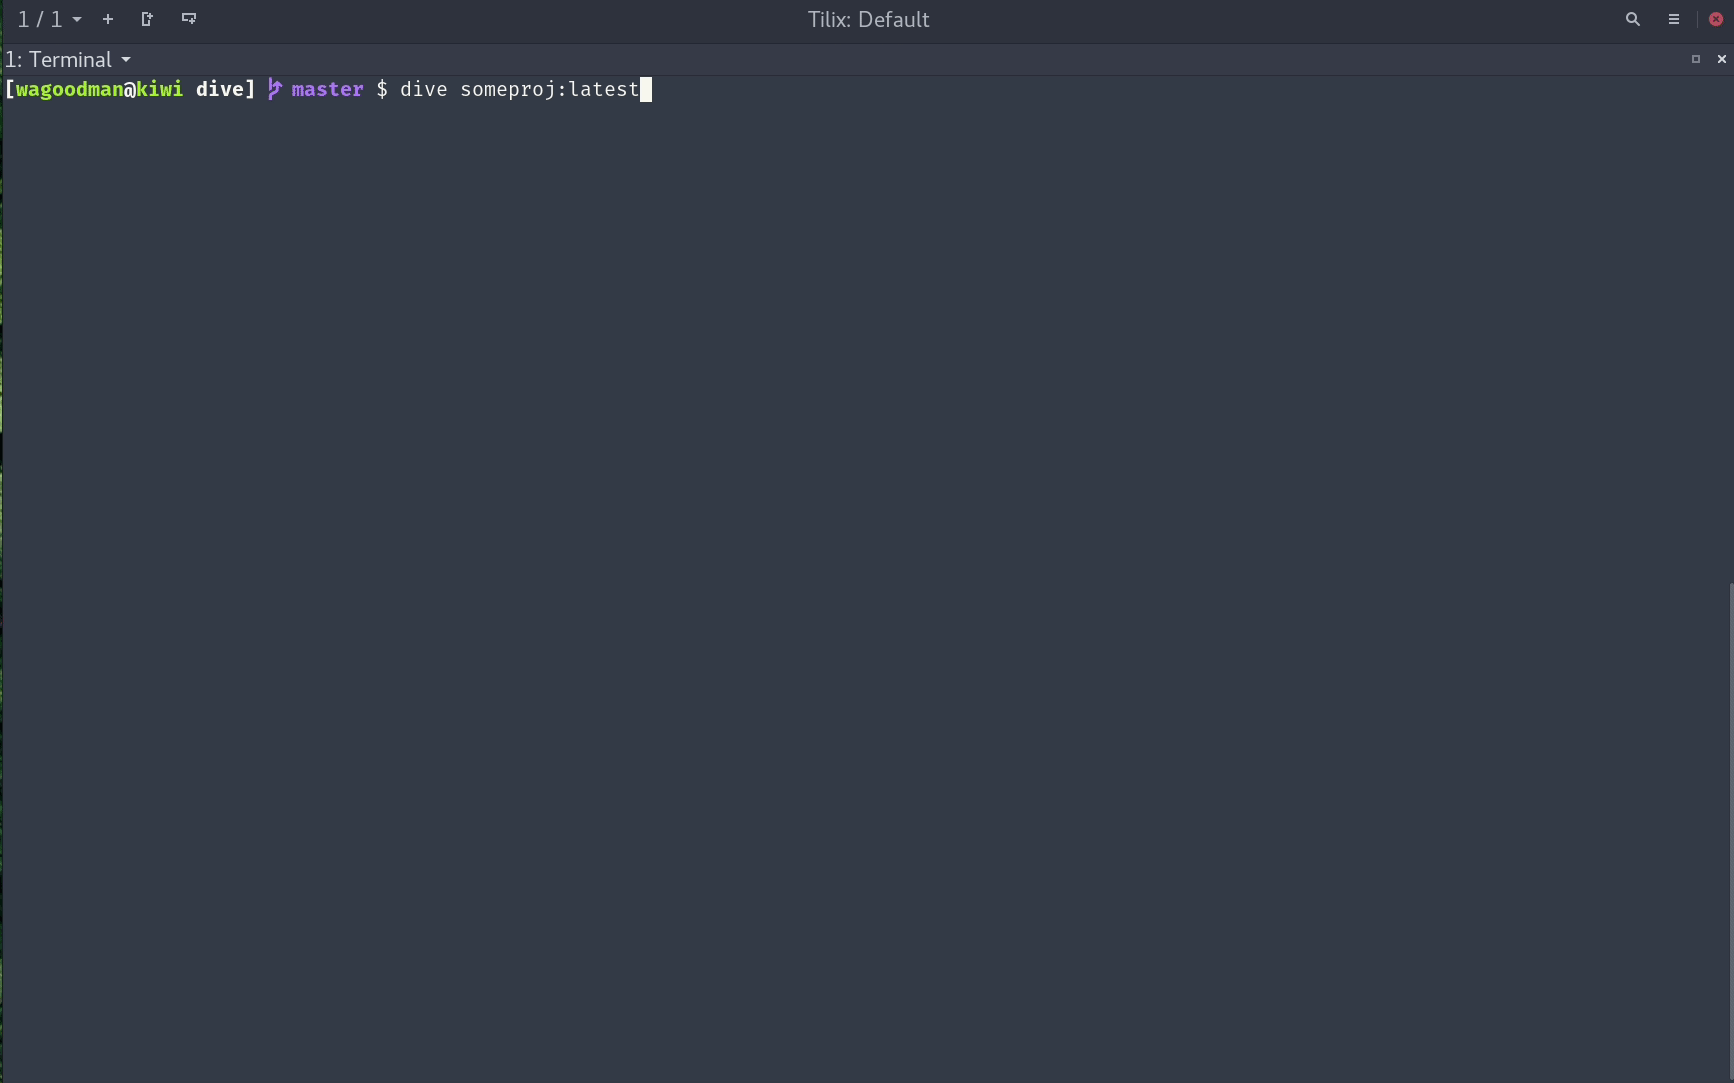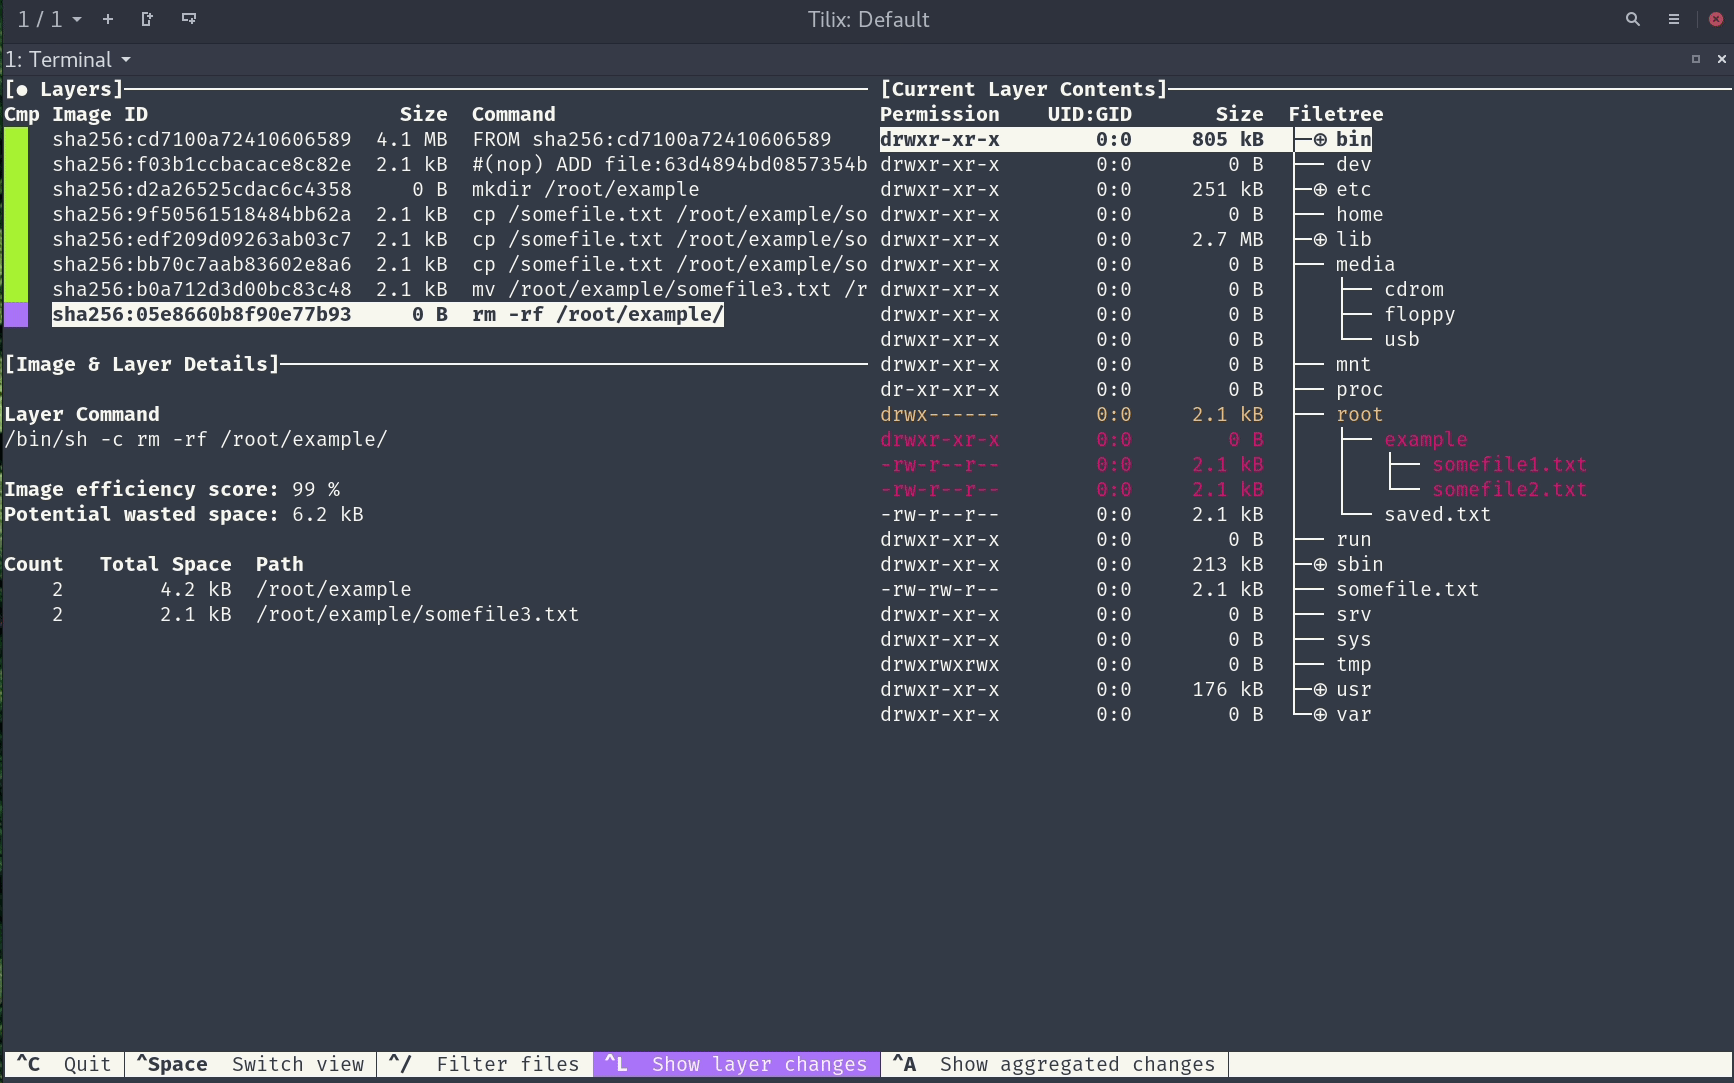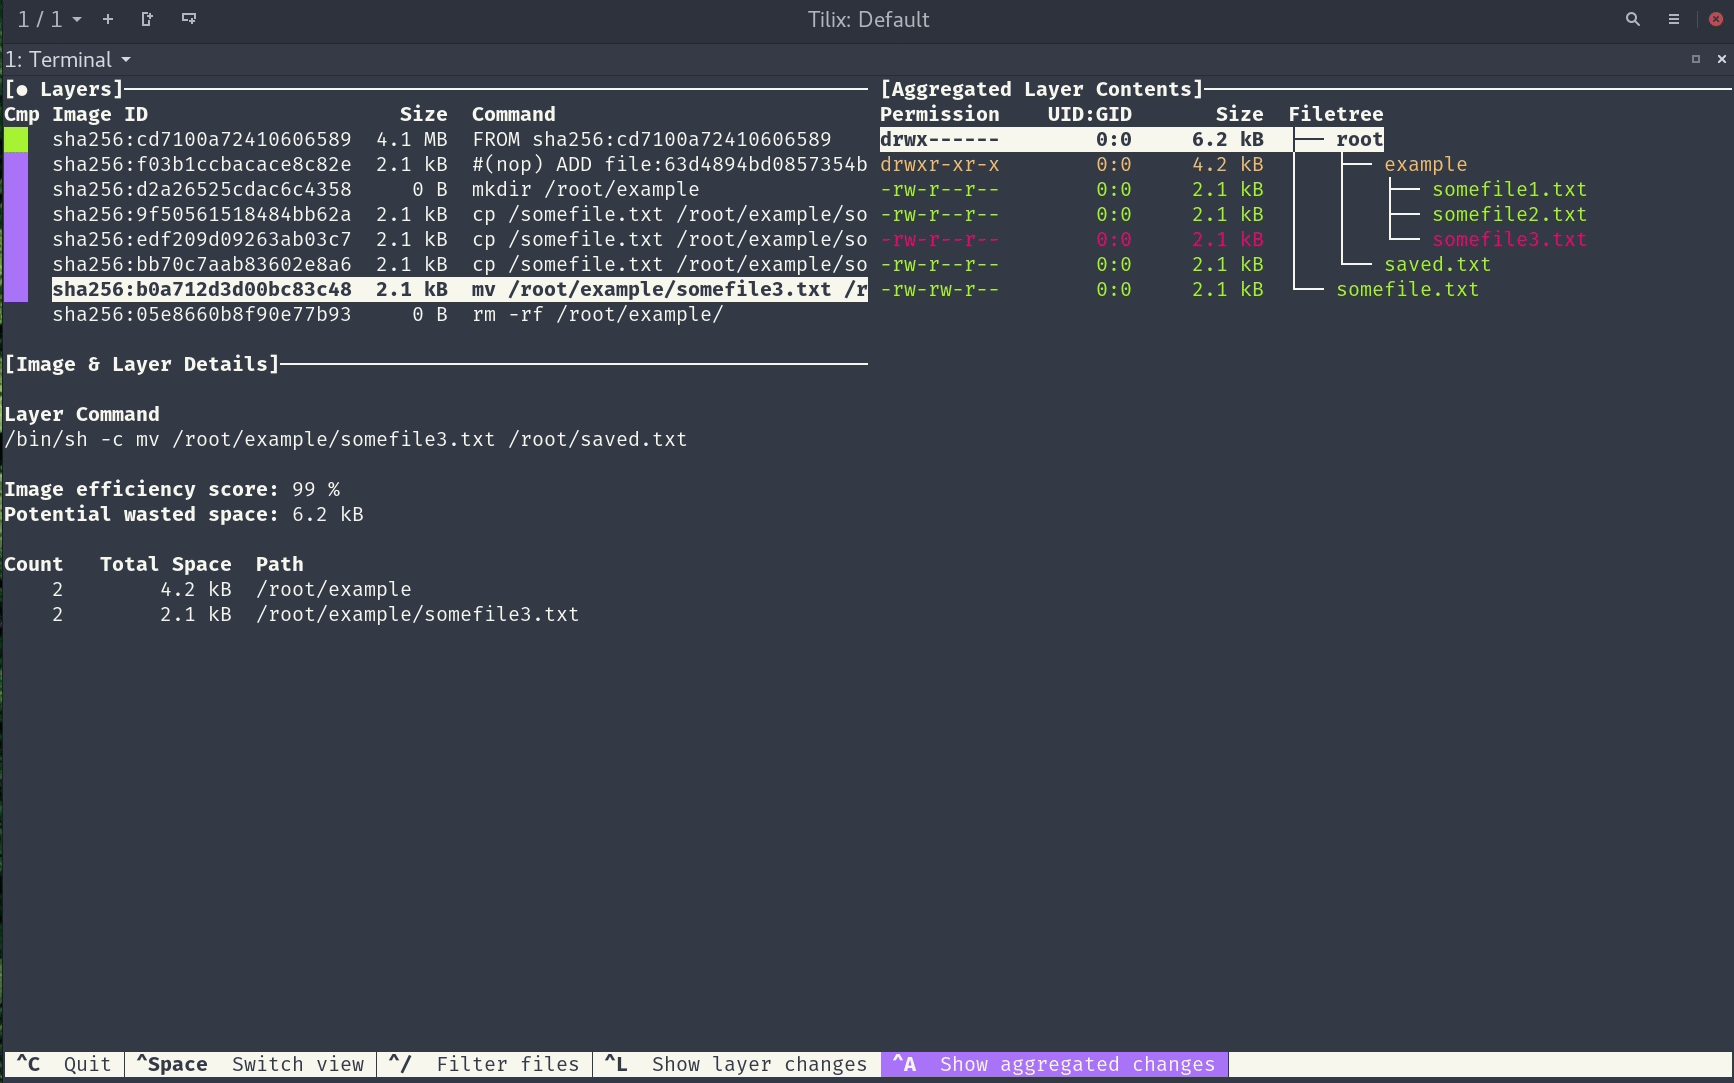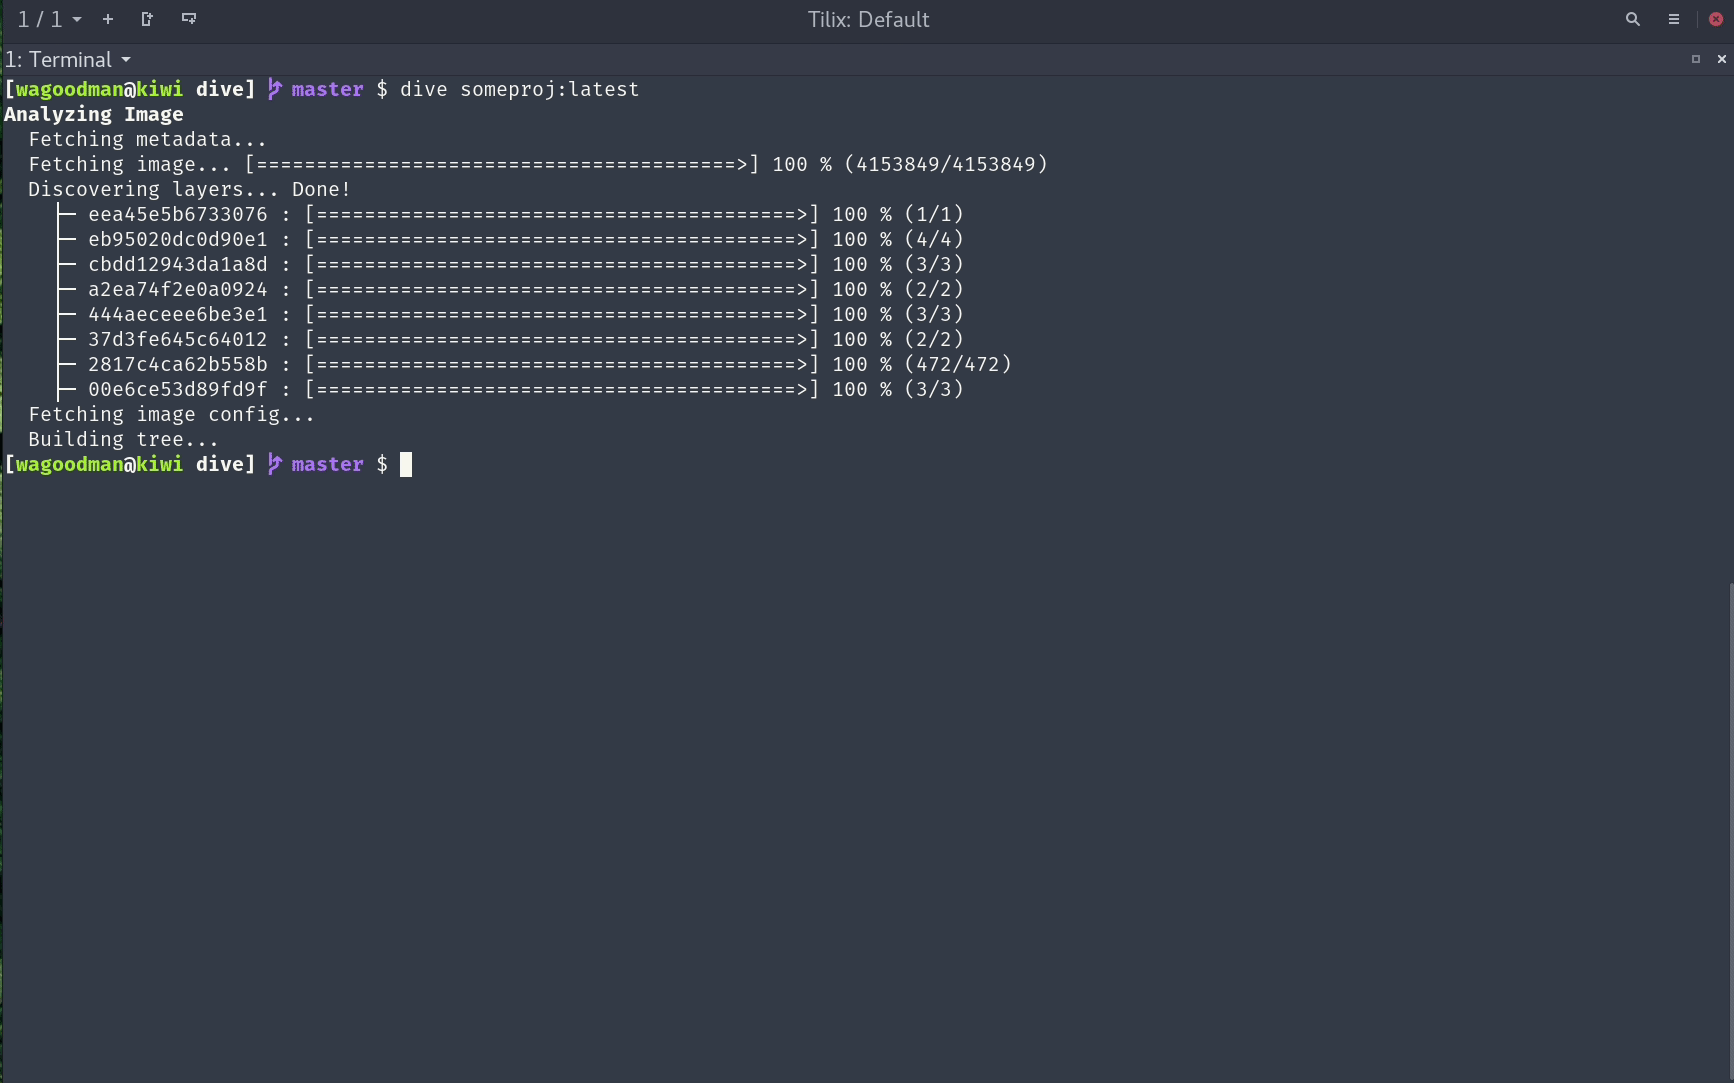
A tool for exploring each layer in a docker image

A repo to automatically generate and keep updated a series of Docker images through GitHub Actions.

This page is a result of the ongoing hands-on research around advanced Linux attacks, detection and forensics techniques and tools.

Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…

eBPF Security Monitoring and Sandboxing Agent Based on Aya

Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…