
CVE-2024-53677
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
container-securityeducationexploitation+3
31 year ago
seanrickerd/cve-2024-53677Vulnerable Environment and Exploit for CVE-2024-53677
 strikoder-premium/cve-2024-21626-runc-1.1.11-escape
PoC for CVE-2024-21626: runc leaks an internal fd referencing the host CWD before pivot_root, enabling container escape by setting process.cwd to…
 felipecosta09/cve-2024-3094
Step-by-step tutorial for detecting CVE-2024-3094 (XZ Backdoor) in container images using Trend Micro Vision One TMAS CLI, with automated scanning…
 cdxiaodong/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host…
 andrewd-cg/cve-2024-52005-poc
Proof-of-Concept for CVE-2024-52005: ANSI escape sequence injection in Git. Demonstrates incorrect 'not_affected' VEX claims in hardened container…
 cgv-dev/metasploit-module-tfm
Module written in Ruby with the objective of exploiting vulnerabilities CVE-2023-2728 and CVE-2024-3177, both related to the secret mount policy in a…
 felipecruz91/node-ip-vex
Sample project that uses VEX to supress CVE-2024-29415.
 pauloparopp/cve-2024-41110-scan
Python-based scanner that checks Docker hosts for CVE-2024-41110 by detecting vulnerable Docker versions and AuthZ plugin usage.
 been22426/cve-2024-3094
CVE-2024-3094 실습 환경 구축 및 보고
 neuralinhibitor/xzwhy
XZ Utils CVE-2024-3094 POC for Kubernetes
 extracoding-dozen/cve-2024-3094
Research of CVE-2024-3094 vulnerability.
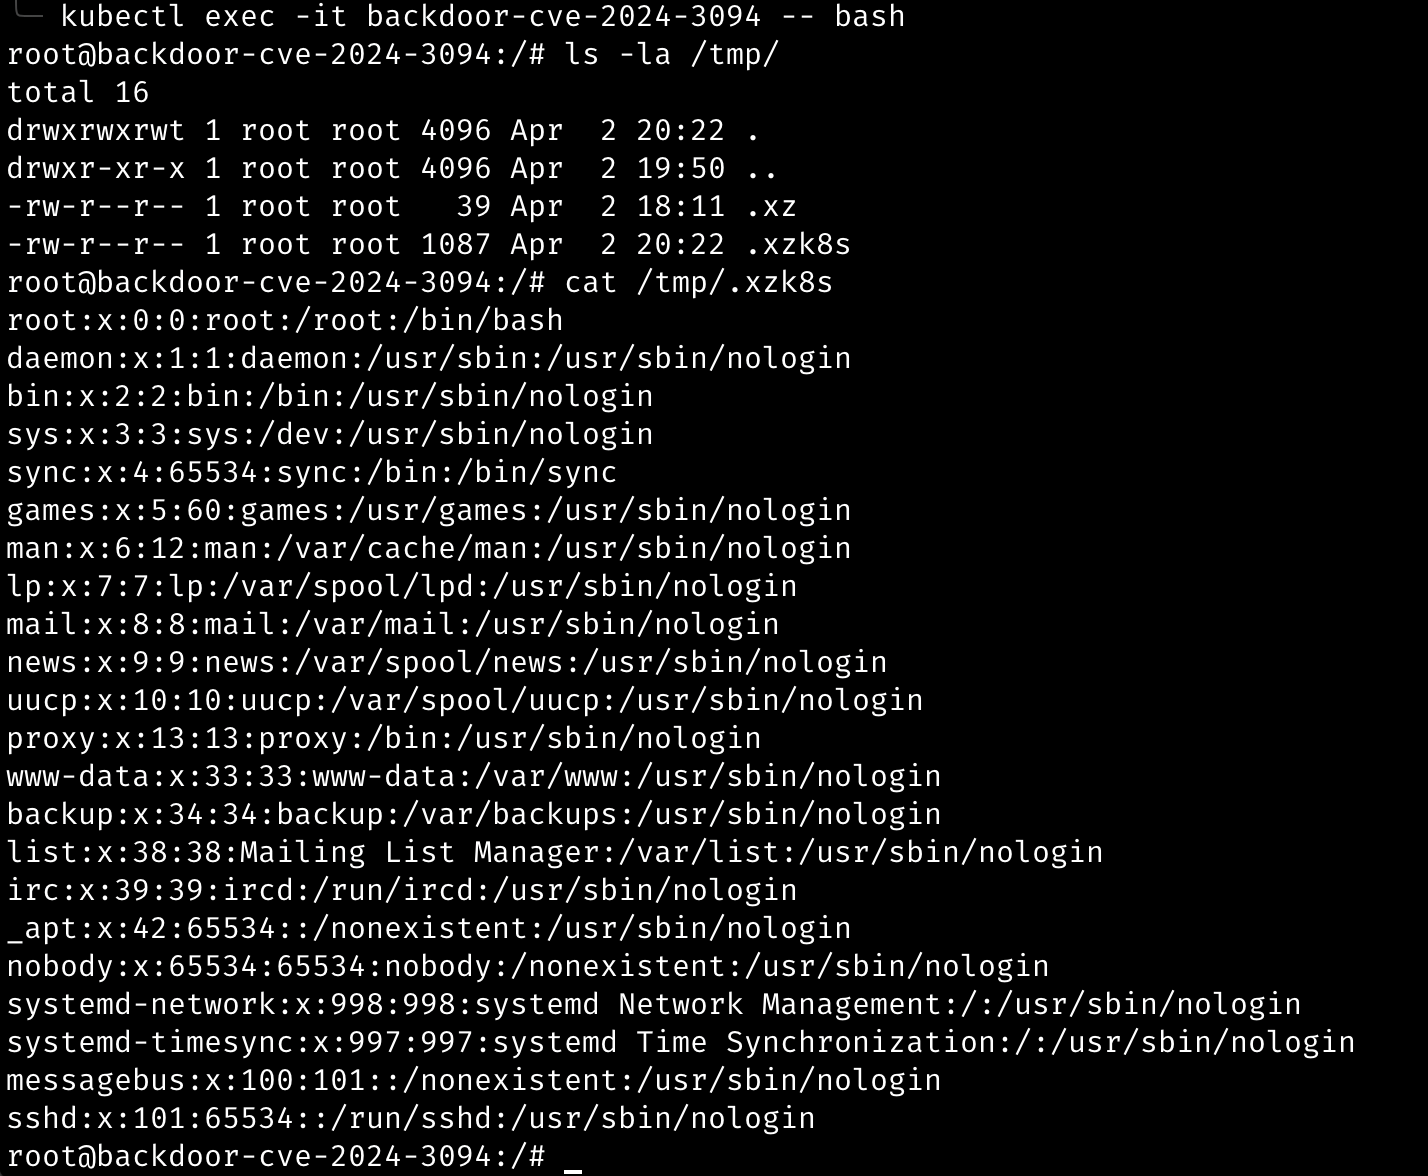 r0binak/xzk8s
Dockerfile and Kubernetes manifests for reproduce CVE-2024-3094
 vishalnoza/cve-2024-38819-poc2
Proof-of-concept exploit for CVE-2024-38819, demonstrating path traversal via symbolic links and percent-encoding in Spring Boot static file routing.
 sk3pper/cve-2024-21626-old-docker-versions
Analyzes and exploits a container escape vulnerability in legacy Docker/runc versions, demonstrating fd leakage to access the host filesystem, with…
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 laysakura/cve-2024-21626-demo
Demonstration of CVE-2024-21626 container escape exploit allowing host root access via malicious Docker image, with step-by-step attack scenario for…
 vt0x78/cve-2024-31989
Exploit for CVE-2024-31989.