

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.3k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 cdk-team/cdk
📦 Make security testing of K8s, Docker, and Containerd easier.
 datadog/security-labs-pocs
Proof of concept code for Datadog Security Labs referenced exploits.
 kmkz/exploits
Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 c-h4ck-0/learn-about-cve-2025-31133-poc
Educational proof-of-concept for CVE-2025-31133, a runc container escape via maskedPaths race condition. Includes lab setup, exploit script, and…
 0xrakan/coolify-cve-2025-66209-66213
Public security advisory for CVE-2025-66209, CVE-2025-66210, CVE-2025-66211, CVE-2025-66212, and CVE-2025-66213
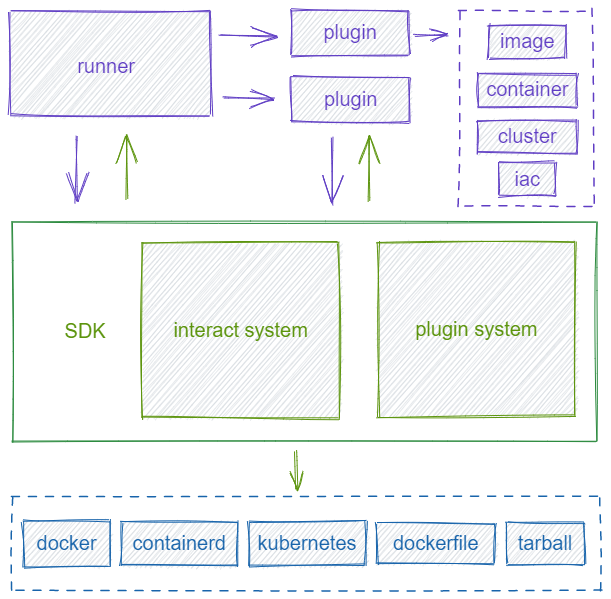 chaitin/veinmind-tools
veinmind-tools 是由长亭科技自研,基于 veinmind-sdk 打造的容器安全工具集
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 secure-system/insular
Isolate your big brother apps https://secure-system.gitlab.io/Insular/
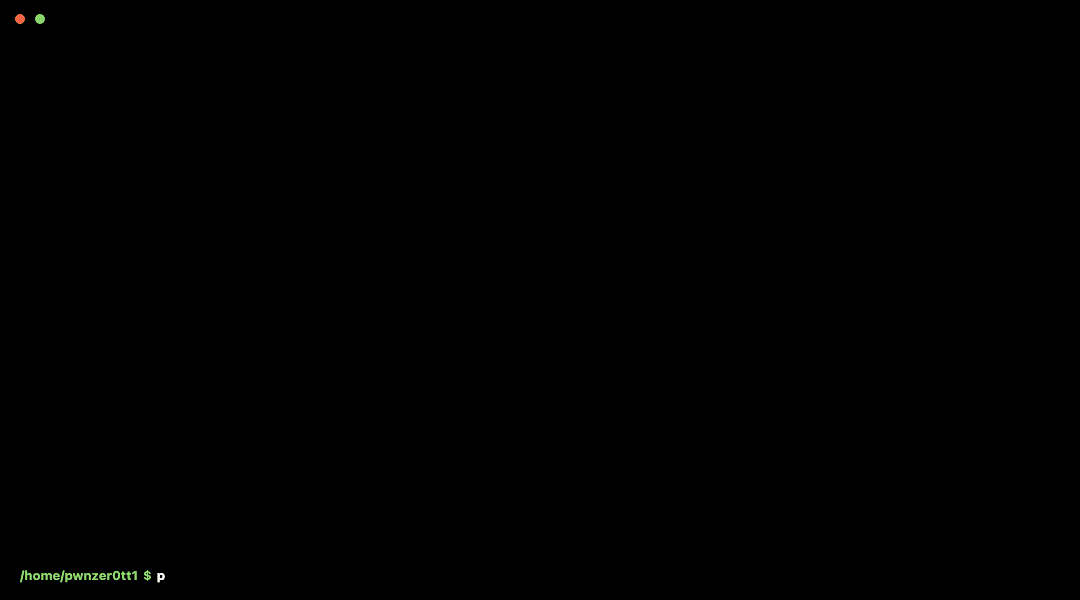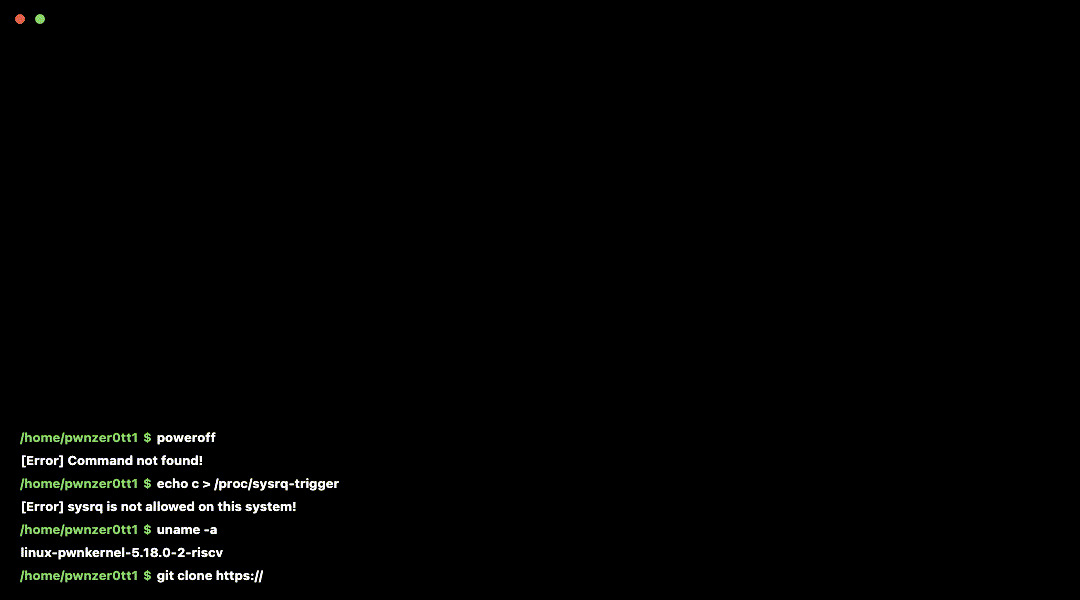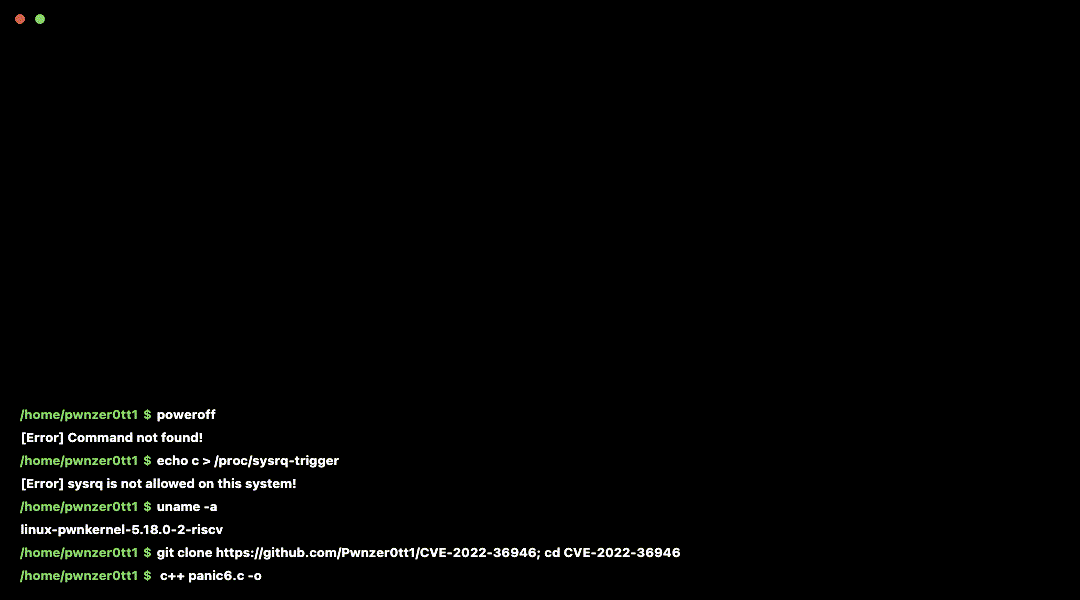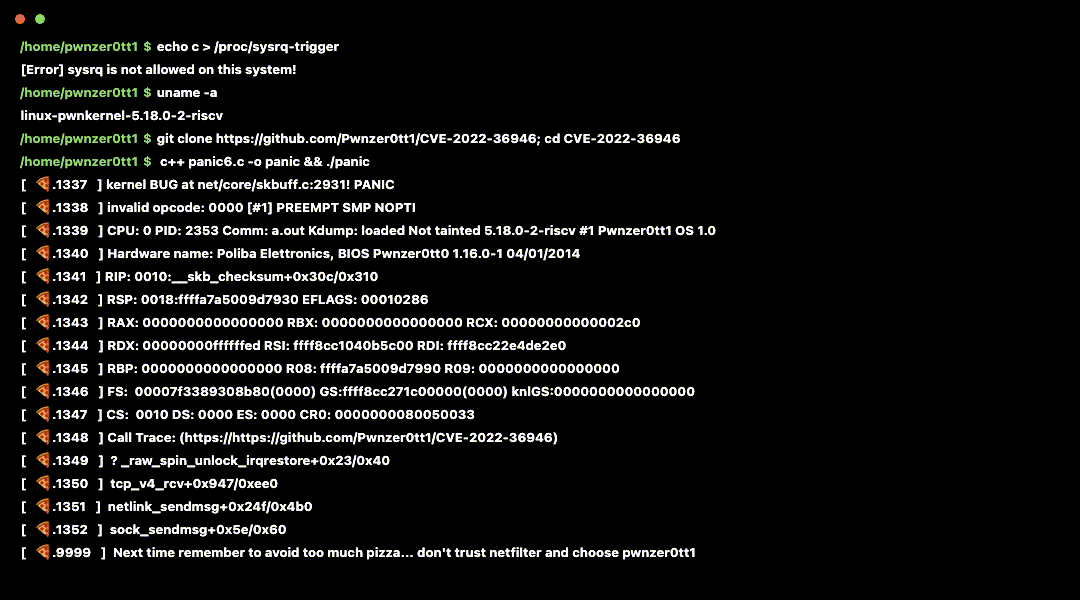 pwnzer0tt1/cve-2022-36946
CVE-2022-36946 linux kernel panic in netfilter_queue
 tamatahyt/cve-2026-53576
Kestra Unauthenticated RCE Exploit (CVE-2026-53576)
 wattocyber/offensive-one-liners
110 offensive-security one-liners for authorized testing and CTFs, grouped by category and kill-chain step.
 ihsansencan/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 chitoz1300/react2shell-cve-2025-55182
* React2Shell-CVE-2025-55182
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…